Ethics ransomware is claimed to have targeted BerlinerLuft. Technology GmbH in Germany, disrupting systems and components used for building complete ventilation and air conditioning systems. The impacted country is #Germany

Wanted in NL is reporting that ransomware attributed to the qilin threat actor encrypted or disrupted files and demanded a ransom. The impact is in #Netherlands
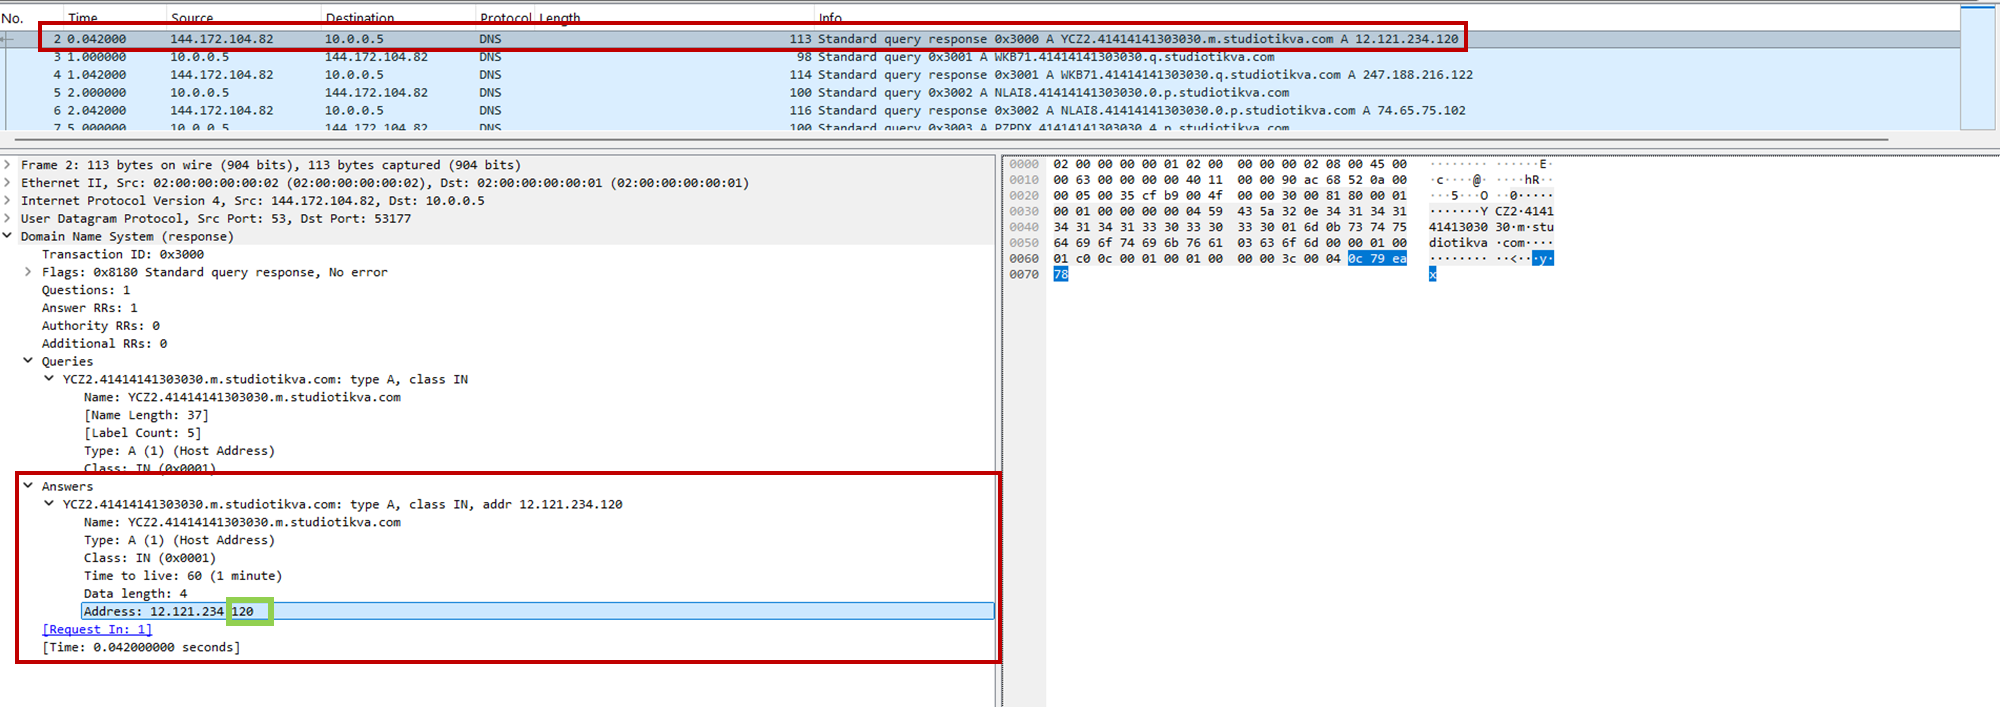
Project CAV3RN is a modular espionage framework targeting Israel that uses a DNS-based control plane to switch between direct HTTPS and a Google Apps Script relay. The newly documented components include GoogleService.dll and rnp.dll, which support tasking, module discovery, runtime upgrades, and brokered communication. #ProjectCAV3RN #GoogleService.dll #rnp.dll #studiotikva.com

Storm-2945, a sub-cluster of Midnight Blizzard, is running CaptiveCrunch to hijack hotel and conference Wi-Fi captive portals, redirecting travelers to attacker-controlled sites for Microsoft 365 credential theft, device code phishing, and malware delivery. The campaign uses CornFlake and ChocoShell, manipulates DNS/HTTP traffic, and extends to Android via malicious APKs. #Storm2945 #MidnightBlizzard #CaptiveCrunch #CornFlake #ChocoShell #Microsoft365 #MicrosoftEntraID #Android

There were 2 defacement incidents targeting Uruguay and Uganda, with attackers identified as Hunter Bajwa and chinafans. The incidents involved defacements of durazno.gub.uy in Uruguay and justicecentres.go.ug in Uganda. #Uruguay #Uganda…
A fake CCleaner installer is being used to deliver the GhostDesk Chrome extension, which steals credentials, cookies, screenshots, and keystrokes from Windows users. The campaign also uses lookalike fake apps such as 7-Zip and Adobe Acrobat, all connecting to the same command-and-control infrastructure to spread the spyware payload. #CCleaner #GhostDesk #Chrome…
B&B Hydraulik (DE) reported a ransomware incident allegedly carried out by the threat actor payload, impacting the company’s operations and access to its systems. The German hydraulics manufacturer is based in Hattingen and supplies hydraulic components and engineering solutions across industrial sectors. #Germany
Interlock ransomware group targeted AngMar Companies, a private organization operating home health care facilities, exposing 710 GB of confidential information, including patient medical records, medical histories, and sensitive personal data such as Social Security numbers, home addresses, and phone numbers. The leaked patient and organizational data has impacted #unitedstates
spacebears ransomware actors claim to have breached Basso Fedele & Figli S.r.l. (Olio Basso) / Villa Raiano and exfiltrated personal information of employees and clients, financial documents, and other files. The impacted organization is based in Italy, #Italy
A federal judge issued a second injunction blocking the U.S. Postal Service from implementing President Donald Trump’s executive order on mail-in voting, citing constitutional concerns. The ruling preserves the current election status quo while the administration seeks Supreme Court review. #USPS #DonaldTrump #IndiraTalwani

Palo Alto Networks’ Unit 42 says the Kimwolf, or Aisuru, botnet has added an HTTP/2-based flood method that uses Chrome-like browser fingerprints to make DDoS traffic look like normal web browsing. The latest version also shifts command-and-control lookups to Ethereum Name Service and Tor to resist takedowns after prior infrastructure seizures and arrests. #Kimwolf #Aisuru #Unit42 #EthereumNameService #Tor
A cyberattack on Ceva Logistics disrupted shipments for major European retailers and may have exposed customer data tied to Steam hardware orders in Europe. The incident affected eight warehouses, while the full scope, attacker identity, and whether ransomware or extortion were involved remain unclear. #CevaLogistics #Steam #Valve #Bol #DeBijenkorf #Ace&Tate #Ajax…
Cisco has patched CVE-2026-20349, a zero-day in Secure Firewall ASA and FTD software that can let a remote unauthenticated attacker trigger a reload and denial of service through a crafted HTTP request to the Remote Access SSL VPN service. Cisco said the flaw was actively exploited in August 2026, and CISA…
Hackers linked to Sandworm, also tracked as APT44 and UAC-0145, are luring system administrators and IT professionals with fake job offers to deliver malicious WireGuard-based tooling. The campaign uses recruiter impersonation, Telegram, Zoom interviews, and trojanized VPN software to run PowerShell payloads and steal access. #Sandworm #APT44 #UAC-0145 #WireGuard #SopraSteria #SourceForge
DeadLock ransomware uses a decentralized setup with the Polygon blockchain, Session, and Wasabi to hide communication, store leak-site data, and make takedowns harder. Microsoft says the operation, active since mid-2025, has hit 80 organizations across multiple sectors and relies on double extortion with a .dlock encryptor and ransom demands in Bitcoin or Monero. #DeadLock #Polygon #Session #Wasabi