Signal introduced Automatic Key Verification to help users confirm their encrypted chats have not been intercepted, using a key transparency system with Cloudflare and Trail of Bits as independent auditors. The feature complements manual safety number checks and arrives after phishing and social engineering campaigns against Signal users, including attacks linked to Russian state-sponsored hackers, UNC5792, and UNC4221. #Signal #Cloudflare #TrailofBits #UNC5792 #UNC4221
Rapid7 published a proof-of-concept exploit for CVE-2026-55040, a critical Microsoft SharePoint authentication bypass, and it is already being used in attacks against SharePoint honeypots. Microsoft and CISA have urged defenders to harden and restrict exposed SharePoint servers while noting that CVE-2026-45659 is also being abused by ransomware gangs. #Rapid7 #CVE-2026-55040 #MicrosoftSharePoint #CISA #CVE-2026-45659

SilentRansomGroup, identified in the claim as “R… D…,” allegedly deployed ransomware against the Redacted entry, with full company name pending disclosure (FULL DATA TIMER active). The claimed impact is limited to the affected country(ies) listed below: #countryname
SilentRansomGroup claimed ransomware activity impacting R…er (full company name pending disclosure). FULL DATA TIMER active; impacted country(s): #countryname
Ethics ransomware actor targeted Philadelphia Insurance Companies (phly.com) in the US, impacting the company’s insurance operations and designed services. The incident resulted in disruption and potential data compromise for the victim in #UnitedStates

Vanta’s third State of Trust report shows that AI is accelerating risk faster than most organizations can govern it, while budgets, staffing, and compliance time remain stuck. The report highlights rising vendor breaches, growing trust demands, and the rapid adoption of agentic AI—alongside major gaps in control, readiness, and oversight. #Vanta #agenticAI #AI

The Constitutional Court confirmed a network intrusion on August 10 that caused temporary disruptions to some IT services, even though security protocols were activated and full backups were available. The court has initiated legal proceedings to investigate the origin of the attack. #ConstitutionalCourt #cc.gob.gt
On August 11, 2026, CH Biotech experienced a cyberattack that affected part of its information systems, though early assessments indicate there was no significant impact on business operations. The company activated its defense measures, brought in external experts, and planned to notify the relevant authorities in line with regulations. #CHBiotech

A ransomware incident at Winnipeg’s Health Sciences Centre disrupted door access and facility maintenance systems, including heating, ventilation, and air conditioning, but did not affect patient care or clinical operations. Shared Health has launched an investigation, notified the provincial government, and is working with experts while increasing security at hospital entrances. #HealthSciencesCentre #SharedHealth #Manitoba

Q2 2026 saw 1,140 ransomware incidents targeting industrial organizations worldwide, with manufacturing, ICS-related organizations, and transportation most affected as attackers increasingly relied on enterprise IT disruption and data theft-only extortion. Qilin, Akira, The Gentlemen, and DragonForce drove much of the activity, while cases involving Chaos, MuddyWater, Stormous, and the Silent Ransom Group showed how ransomware branding, social engineering, and geopolitical motives are converging across industrial environments. #Qilin #Akira #TheGentlemen #DragonForce #Chaos #MuddyWater #Stormous #SilentRansomGroup

Siemens, Schneider Electric, Phoenix Contact, Honeywell, and CISA released August 2026 advisories for multiple ICS and building management product vulnerabilities, including code execution, privilege escalation, and denial-of-service flaws. The most severe issues affect Siemens Simatic IoT2050 Advanced and Siveillance Video Management Servers, while Phoenix Contact and Schneider Electric also patched critical…

Ivanti has released patches for four vulnerabilities affecting Endpoint Manager (EPM) and Neurons for MDM, including issues that could let remote attackers leak credentials, crash services, or control filenames. The company says it has seen no evidence of exploitation in the wild and that no other Ivanti products are impacted. #Ivanti…

North Korean hackers linked to the Lazarus Group are abusing the newly patched Windows zero-day CVE-2026-68820 in fake job application lures to compromise defense, aerospace, and aviation targets. The campaign uses Mistpen, ForestTiger, Troy, SecurityPDF, and RelayShell to gain SYSTEM privileges, persist, and steal data through compromised web infrastructure. #LazarusGroup #CVE-2026-68820…
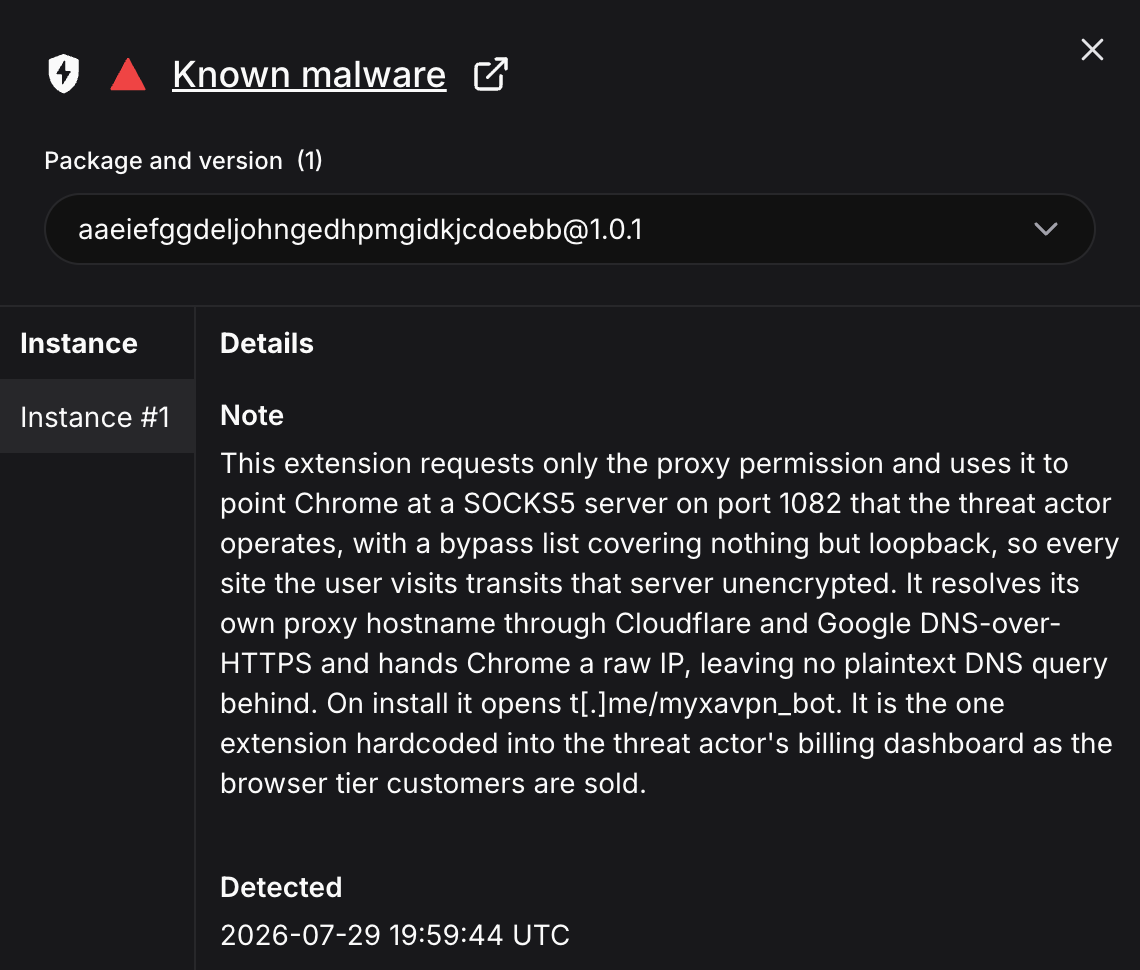
Socket’s Threat Research Team uncovered a campaign of 737 free VPN and proxy Chrome extensions spread across at least 40 developer accounts, many of which impersonate established brands and route browser traffic through a single operator’s SOCKS5 infrastructure. The operation also includes fake premium servers, DNS-over-HTTPS evasion, post-approval code substitution, and coordinated store-review deception tied to Myxa VPN and related domains. #MyxaVPN #ChromeWebStore #AmneziaVPN #AntiZapret
Holstrom, Block & Parke, a professional law firm in the US, claims it was targeted by the Ethics ransomware threat actor. Our attorneys have experience handling cases in family law, estate planning, appeals, and probate law, with impacts reported in #UnitedStates