Jack Rutherford Customs Brokers Ltd (The Rutherford Group) in Canada, serviced by an IT provider, reported a ransomware claim by the blacknevas threat actor affecting its cross-border customs brokerage and logistics operations. The Rutherford Group provides import/export clearance, compliance support, warehousing, and transportation services across borders, with impact in #Canada

The ransomware attack on gamaus.com (Greater Austin Merchants Cooperative Association) by the US-based threat actor incransom involved encryption of approximately 400GB of data. The incident is reported in the United States. #UnitedStates
Portable Intelligence Inc (www.portable-intelligence.com) in the US, serviced by an IT company, suffered a ransomware incident attributed to blacknevas. The attack targeted the company’s warehouse management/automation software operations used in North America, impacting United States #UnitedStates
Microsoft has released the Windows 10 KB5120249 ESU for versions 22H2 and 21H2 to address security vulnerabilities, fix bugs, and deliver the August 2026 Patch Tuesday updates. The update resolves a File History backup issue over SMB and expands the rollout of new Secure Boot certificates. #Microsoft #Windows10 #KB5120249 #SecureBoot
DeadLock ransomware uses a decentralized setup with the Polygon blockchain, the Session network, and Wasabi cloud storage to hide its communication and data-leak operations. Microsoft says the group, active since mid-2025, has already listed 80 victims and relies on double extortion to pressure organizations into paying. #DeadLock #Polygon #Session #Wasabi
Hackers are targeting social media accounts to steal explicit content and sell it on criminal marketplaces, according to a new FBI alert. The FBI says attackers use social engineering, password guessing, fake support scams, and cloned login pages, then often extort and harass victims with the stolen material. #FBI #Snapchat #UniversityofMichigan…

A newly disclosed flaw in OpenAI, Anthropic, and Google reasoning APIs let researchers replay encrypted reasoning objects across sessions and recover hidden content from public logs, including API keys and passwords. The paper also showed how opaque reasoning blocks could be used to hide prompt injections and extract proprietary traces, with…

Lazarus Group is exploiting a recently patched Windows zero-day, CVE-2026-68820, to deliver a new backdoor called Troy against defense and aerospace targets in France, Germany, Brazil, and India through Operation Dream Job. The campaign uses fake recruiter lures, trojanized PDF software, and compromised legitimate sites and servers to spread MISTPEN, ForestTiger,…
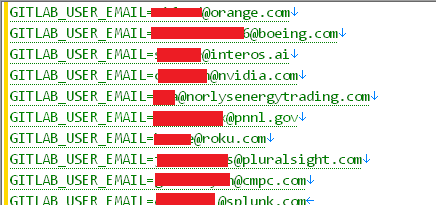
TeamPCP orchestrated a multi-ecosystem supply chain attack that began by compromising Trivy’s GitHub Actions pipeline and ended with malicious LiteLLM packages silently stealing secrets from CI/CD environments worldwide. The leak exposed 153GB of data from 118,829 pipeline runs tied to 2,488 domains, affecting organizations including AWS, Samsung, Cisco, Salesforce, ServiceNow, Siemens, and others. #TeamPCP #Trivy #LiteLLM #HudsonRock #Cavalier #Orange #Boeing #Roku #AdsWizz

A seller named exfilar is offering Branch deep link keys for $15,000, advertising access to public developer packages rather than a direct breach. The listing could enable phishing through a shared domain trusted by 2,553 apps, including 666 iOS apps and 1,887 Android apps. #Branch #exfilar…
ZeroBytes claims to have breached the French tax administration through internal VPN credentials and is offering a partial database containing 678,438 taxpayer records. The alleged data includes access to internal search tools for individual and business taxpayers, but the claim remains unverified and has not been publicly addressed by the French…
The UN FAO Climate Mapping Tool, ABC-Map, was allegedly left in a publicly writable open bucket, exposing 138,346 government boundary files totaling 11GB. The incident was observed on Aug. 12, 2026 and was reportedly caused by a misconfiguration. #UNFAO #ABCMap…
Attempts to exploit CVE-2026-71362 in Adobe Commerce and Magento are being blocked by Sansec’s Shield WAF, even though Adobe says it is not aware of active exploitation in the wild. The flaw can let attackers hijack customer sessions and access private account data without authentication, while Adobe has also patched six additional vulnerabilities in the same update. #AdobeCommerce #Magento #CVE-2026-71362 #Sansec
WindRelay, an Android NFC relay malware, is being used with the SpyNote RAT to steal payment card data and enable real-time fraudulent transactions. Group-IB says attackers impersonated bank staff, tricked victims into sideloading a malicious app, and completed the fraud in a 13-minute call. #WindRelay #SpyNote #GroupIB
Agentic AI has accelerated attacks by making long-standing technical, governance, skill, infrastructure, and AI-attack-surface debts easier for threat actors to collect on at scale. The article cites cases including JADEPUFFER, GTG-1002, PROMPTSTEAL, QUIETVAULT, PROMPTFLUX, FRUITSHELL, HONESTCUE, and the marimo intrusion to show that AI mostly changes speed, scale, and orchestration rather than introducing new attack techniques. #Anthropic #Claude #JADEPUFFER #HuggingFace #GTG-1002 #PROMPTSTEAL #QUIETVAULT #PROMPTFLUX #FRUITSHELL #HONESTCUE #marimo