
This investigation links Quake3, chromium, and evilcore to one operator who openly identified himself as morgot on exploit.in, while forum logs and private messages show synchronized account activity on the same IPs. The file also ties his long-running malware, loader, and botnet work to the REvil source-code developer persona later associated with Anatoly Sergeevitsch Kravchuk. #Quake3 #morgot #Rcode #REvil #AnatolyKravchuk

A seller using the name palmbeachpete is allegedly offering the EnformionGO database for $50,000, claiming it contains 315.6 million people profiles with emails, phone numbers, and detailed address histories. The listing is unverified, but the sample data suggests a highly sensitive life-record dataset tied to EnformionGO and Enformion. #EnformionGO #Enformion #palmbeachpete…
A forum user named 4me44 allegedly leaked 20,274 records from EVA’s Nantes Sud location in France, exposing personal data such as names, email addresses, dates of birth, phone numbers, and home addresses. The actor also claimed back office admin access and showed a campaign generating €1M in gift cards, but the…
An actor calling themselves sta6 is allegedly selling a breach dataset tied to Zro Global’s hiring platform, claiming access to 55,866 candidate records, interview audio, and internal scoring data. The exposure could reveal sensitive personal and recruitment information, but the claim remains unverified and Zro Global has not publicly addressed it….
ZeroBytes claims a second intrusion against France’s DGFiP cadastral data server, alleging 252,149 extracted rows and exposure of 2,041,778 property holders. The group says it still has access through valid credentials and a multi factor authentication bypass, and is offering that access for sale, though the claim remains unverified. #ZeroBytes #DGFiP…
A forum user calling themselves ChimeraZ allegedly released 16GB of Chupin data, including emails, CRM records, and invoices, in what is labeled the sixth leak tied to tenants of a shared business platform. The numbering and embedded platform identifiers suggest multiple companies may be exposed through the same provider, but the…
A newly patched critical flaw, CVE-2026-59310, in VMware vCenter Syslog Server is being actively exploited to install the reverse_ssh tool for persistence and remote access. QUIRSO says the campaign has hit 361 IP addresses across 47 countries, with rapid expansion soon after Broadcom released emergency fixes. #CVE-2026-59310 #VMwarevCenter #Broadcom #reverse_ssh #QUIRSO
A market for removing Claude’s new invisible AI watermarks has emerged, led by open-source projects, web tools, and commercial evasion services claiming to clean marked text. Anthropic says its watermarking is meant to satisfy EU AI Act transparency rules, but the actual watermark is hard to verify because no public detector has been released yet. #Claude #Anthropic #EUAIAct #watermarks-remover #StealthGPT #HumanWrites
Microsoft has released patches for the Windows zero-day vulnerability LegacyHive, now tracked as CVE-2026-62832, after it was disclosed with a proof-of-concept exploit. The flaw affects the Windows User Profile Service and can let authenticated local attackers gain administrator privileges; Microsoft and other researchers also provided detection and unofficial mitigation guidance. #LegacyHive #CVE-2026-62832 #NightmareEclipse #WindowsUserProfileService
Jewelbug has been conducting espionage against governments and militaries while also running cryptocurrency fraud campaigns, with Symantec linking both activities to the same infrastructure. The group used compromised government webmail, fake software prompts, malicious browser tools, and AI-generated scam pages to steal cookies, credentials, and email data. #Jewelbug #EarthAlux #REF7707 #Antino #XGWeb #ClientKing #OKX #Binance
Turla is a Russia-linked APT group that has conducted long-term cyber espionage against government, diplomatic, military, research, and technology targets across multiple countries since at least 2008. Recent campaigns in 2026 included STOCKSTAY backdoor activity and attacks on French entities, showing continued focus on stealthy intelligence collection and strategic access. #Turla #STOCKSTAY #France
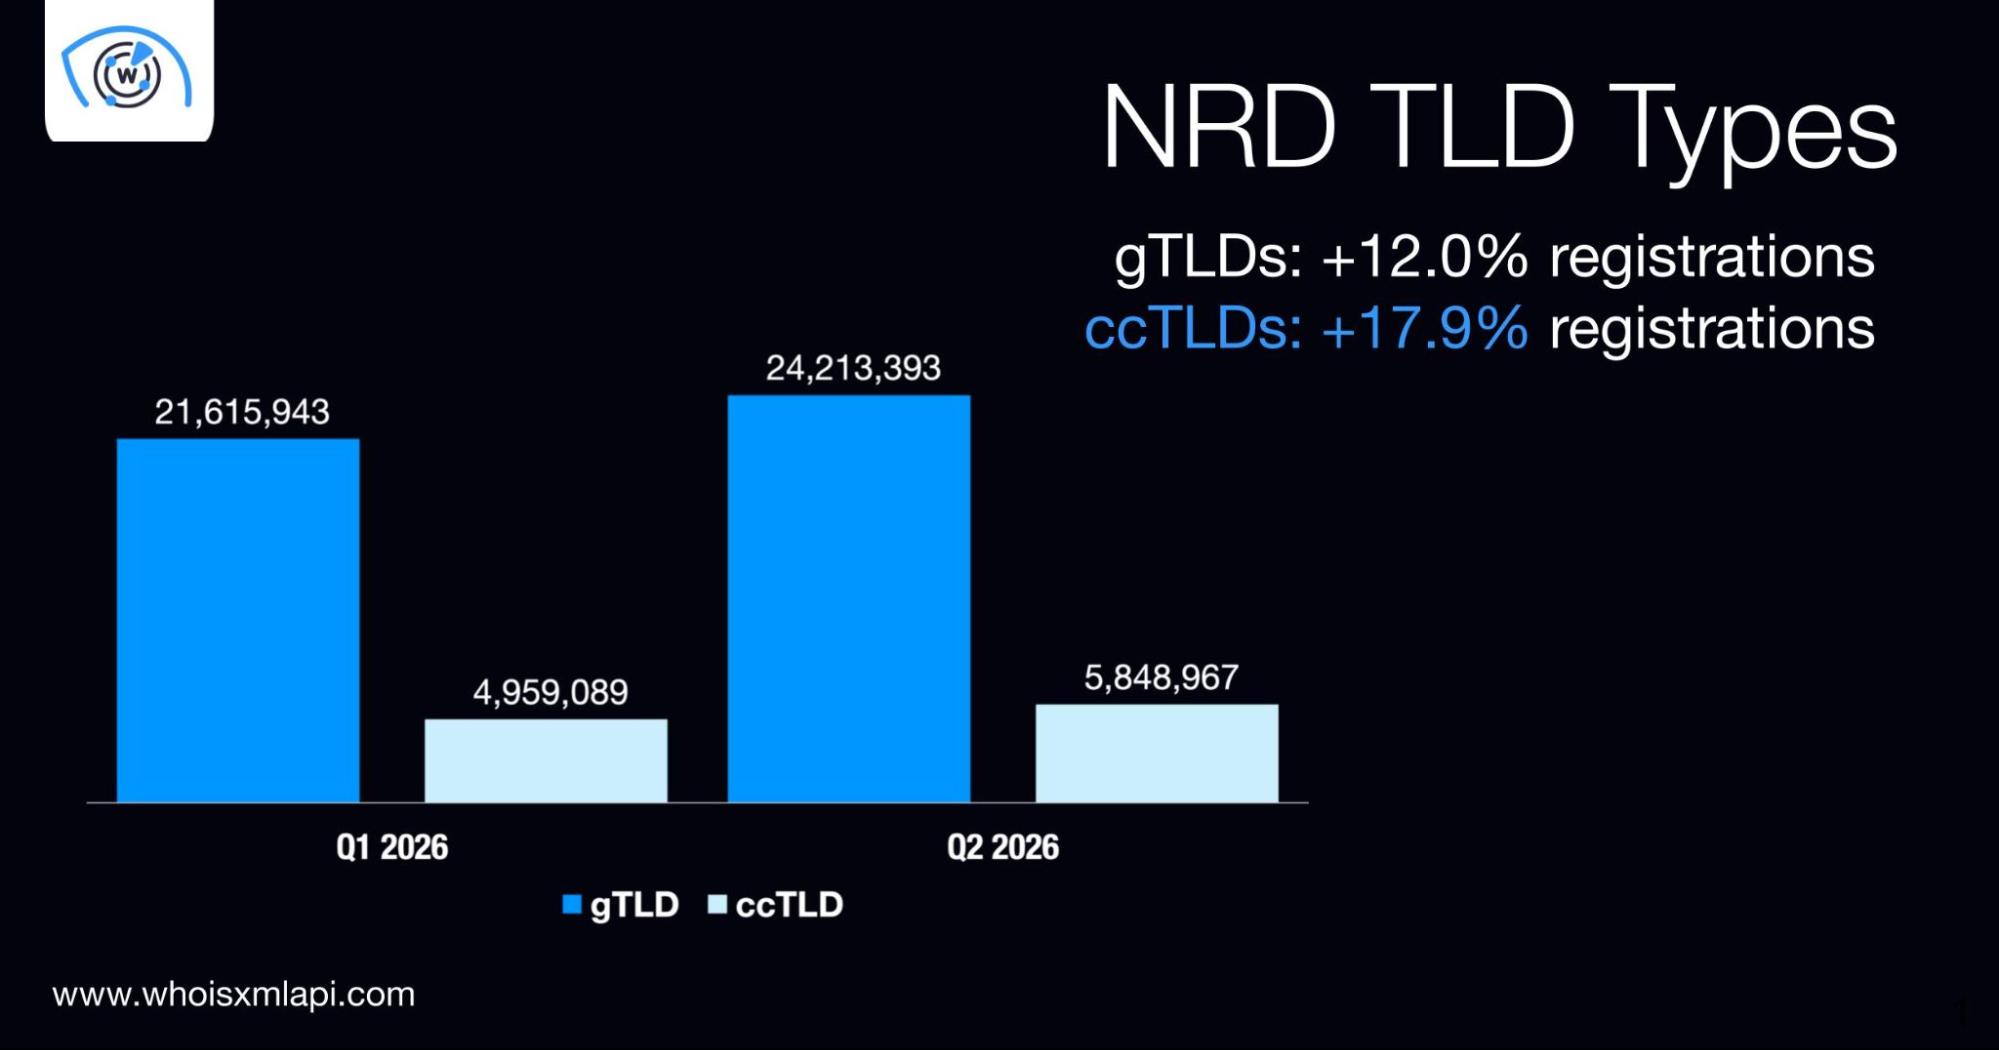
Q2 2026 domain activity showed 30.0+ million newly registered domains, with 7.6+ million likely registered with malicious intent and 3.2+ million confirmed malicious domains analyzed for TLD trends. The report also found rising concentration in MX and NS infrastructure, with top provider usage increasing across email and DNS systems. #WhoisXMLAPI #NRDs #DNSDatabaseDownload #ThreatIntelligenceDataFeeds
CSDD was targeted in a complex and focused cyberattack that led to the exposure of historical payment data containing customers’ personal information. Authorities say the attack has been stopped, the investigation is ongoing, and residents are being warned to watch for possible fraud attempts. #CSDD #CERTLV
Darlington County, South Carolina, isolated parts of its computer systems after a cybersecurity incident disrupted phone lines and some government services, while 911 remained operational. Officials have brought in outside specialists and law enforcement, but the full scope of the attack and whether data was compromised remain unclear. #DarlingtonCounty #SouthCarolina

Daily Recap, Microsoft addressed 421 CVEs in Patch Tuesday, including a Windows driver zero-day under active attack, while Adobe and multiple ICS vendors also shipped critical fixes for ColdFusion and Campaign Classic-related issues. The day also highlighted exploited zero-days impacting Microsoft Defender (ShieldBreak), Cisco ASA/FTD VPN devices, and a fresh Windows flaw tied to North Korean cyberattacks, alongside reported breaches involving Ceva Logistics and Wesco, plus active abuse such as malicious Kimwolf and trojanized WireGuard activity. #PatchTuesday #Microsoft #Windows #ShieldBreak #Cisco #ASA #FTD #ColdFusion #CampaignClassic #Siemens #Schneider #PhoenixContact #NorthKorea #CevaLogistics #Wesco #ExfilSquad #DeadLock #Kimwolf #Sandworm #WireGuard #WhatsApp #Signal #Zoom #Chrome #Delta #DEFCON #NIST #NSA #DHS