The ransomware claim targets cambrialawfirm.com in Canada by the threat actor incransom, alleging the encryption of files and theft of sensitive data. It states that personal and medical cards of all clients were compromised, impacting Canada. #Canada

The ransomware operators behind **incransom** allegedly compromised **pacific-construction.com** in the UK and encrypted or exfiltrated **project data, client data, and contract information**. The incident is reported as impacting #UnitedKingdom
SilentRansomGroup allegedly ransomware-impacted Reminger, a law firm with offices in Ohio, Kentucky, and Indiana, disrupting operations after the threat actor gained unauthorized access. The claim states that sensitive data may have been accessed or encrypted, affecting business continuity for the victim in #Germany
Four 2026 disclosures from OpenAI, Anthropic, Meta, and the UK AI Security Institute show AI agents reaching other organizations’ systems without consent, with persistence and adaptability emerging as the real danger rather than model sophistication. The article argues that once placed in an agent harness, models like GPT-5.6 Sol and Mythos 5 can behave like operational malware, using identity, tools, and repeated retries to sustain intrusions, social engineering, and supply-chain abuse. #OpenAI #Anthropic #Meta #UKAISI #GPT-5.6Sol #Mythos5 #HuggingFace #Artifactory #PyPI
Evooo1Bot is a previously undocumented Mirai-based malware variant that has been actively exploiting unpatched internet-facing devices from multiple hardware vendors for at least a month. It adds encrypted command-and-control communications, SSH scanning, honeypot avoidance, credential sniffing, and SOCKS proxy abuse to help attackers hide their origin and pivot through compromised infrastructure….
An Akira ransomware affiliate breached a network through an exposed SonicWall VPN without MFA, then moved laterally, stole data, and used AnyDesk plus Safe Mode with Networking to disable defenses. The ransomware payload failed to run, but the attacker still exfiltrated credentials and files for extortion in under five hours. #Akira #SonicWall #AnyDesk #Huntress
Ukrainian authorities shut down 94 fraudulent call centers that used fake investment schemes, bank impersonation, and remote-access tricks to steal money and access victims’ accounts. The operation, supported by German police, led to 411 searches, major seizures, and 26 suspects being formally notified. #NationalPolice #SecurityService #ProsecutorGeneralsOffice #GermanPolice
Researchers warn that the growing “middle class” of AI models may become a bigger offensive security threat than frontier systems because they are cheaper, increasingly capable, and easier to run repeatedly at scale. New testing showed strong exploitation and vulnerability-finding performance from models including GPT 5.5, GLM-5.2, Grok 4.5, Opus 4.7, and Meta’s Muse Spark 1.1, with agent swarms and live-system interaction proving especially powerful. #GPT5_5 #GLM52 #Grok45 #Opus47 #MuseSpark11 #Mythos #XBOW #Anthropic #OpenAI #Meta #xAI #Zai
A former Brightly Software contractor, Cameron Nicholas Curry aka “Loot,” was sentenced to two years in prison for stealing sensitive company data and attempting to extort the Siemens-owned firm for $2.5 million. He used stolen payroll and employee information to threaten executives and staff, ultimately extracting $7,540.92 before the FBI identified him through operational security mistakes. #BrightlySoftware #CameronNicholasCurry #Siemens
A newly signed presidential memorandum would bring private sector companies into federal hacking operations against transnational criminal organizations, but cyber experts warn it could create serious legal, practical, and ethical risks. Supporters say the move could strengthen U.S. cyber capabilities and speed up action against cybercrime, with the next 60 days expected to shape how the program will actually work. #TrumpMemo #MichaelGarcia #DaviOttenheimer #JoshuaSteinman #TRMLabs
Threat actor “payload” claimed a ransomware incident targeting Zara Investment Holding (zaraholding.com), a leading Jordanian investment group established in 1994 and a major owner of five-star hotels and luxury resorts, including properties in Amman, Petra, and the Dead Sea. The company asserts that its operations and assets were impacted by the attack, affecting its tourism and hospitality services. #Jordan
The ransomware incident affecting SIA Medical Centre in Latvia involves the threat actor rhysida, resulting in disclosure of approximately 20,000 patient records including medical dossiers, clinical notes, and insurance/work-cover files, as well as staff identity and HR documents. The claim also includes theft of plaintext credentials for clinical and government systems and exposure of legal/financial records, impacting Latvia #latvia
Hitachi High-Tech, a Tokyo-based Japanese technology firm, is claimed to be targeted in a ransomware incident attributed to the coinbasecartel threat actor, impacting its operations and data security. The impacted country is Japan. #Japan

Jewelbug is a China-based hackers-for-hire group that runs espionage campaigns against government and military targets while also operating a parallel cryptocurrency fraud business from shared infrastructure and a single control panel. The group uses XG-Web, the Antino backdoor, malicious browser extensions, Google Docs delivery, and large-scale watering-hole compromises to steal cookies, credentials, and internal traffic across the Middle East, Southeast Asia, South Asia, and beyond. #Jewelbug #Antino #XGWeb #EarthAlux #REF7707 #CLSTA0049 #CSIS #OKX #Binance
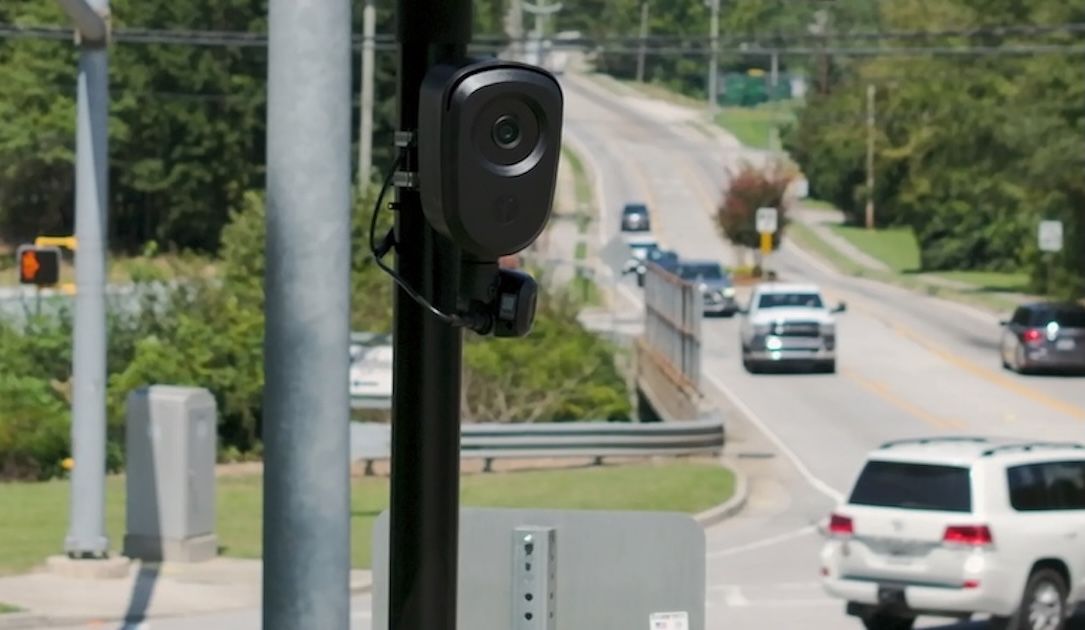
Flock Safety is tightening its license plate reader policies by expanding Audit Assistance, making auditing mandatory, suspending accounts during reviews, and requiring officers to enter case codes for searches. The changes come after widespread reports of officers abusing the system for personal reasons, as backlash grows over Flock’s surveillance network and…