
There were 12 defacement incidents attributed to the attacker maw3six, targeting sites across India. The affected countries were India, and the attackers involved were maw3six. #India…

Storm ransomware reportedly targeted Westco Motors Cairns (AU), a family-owned multi-franchise dealership in Bungalow, Queensland, offering vehicle sales, servicing, and parts with 100+ local staff. The incident impacted customers and business operations associated with the dealership in #Australia
Storm is alleged to have deployed ransomware targeting Standard Tool & Die, a US-based manufacturer of die cast dies, plastic molds, and trim dies, including customers across automotive, appliance, furniture, and household goods. The alleged incident impacted the United States #UnitedStates
Valor Defense Solutions, Inc. (US), a woman-owned defense contractor headquartered in Odon, Indiana, was impacted by the Storm ransomware threat actor, disrupting its customized logistics, engineering support, manufacturing, and refurbishment services. The incident affected operations in the United States #UnitedStates
A 12 August 2026 White House memorandum authorizes vetted private US companies to conduct government-directed cyber surveillance and effects operations against criminal groups abroad, creating new jurisdictional and telemetry-sharing risks for non-US organizations. The article argues that European hospitals, grid operators, and municipalities must now ask not just where their data sits, but whose authority controls the security tools they use. #WhiteHouse #CLOUDAct #NIS2 #CADA
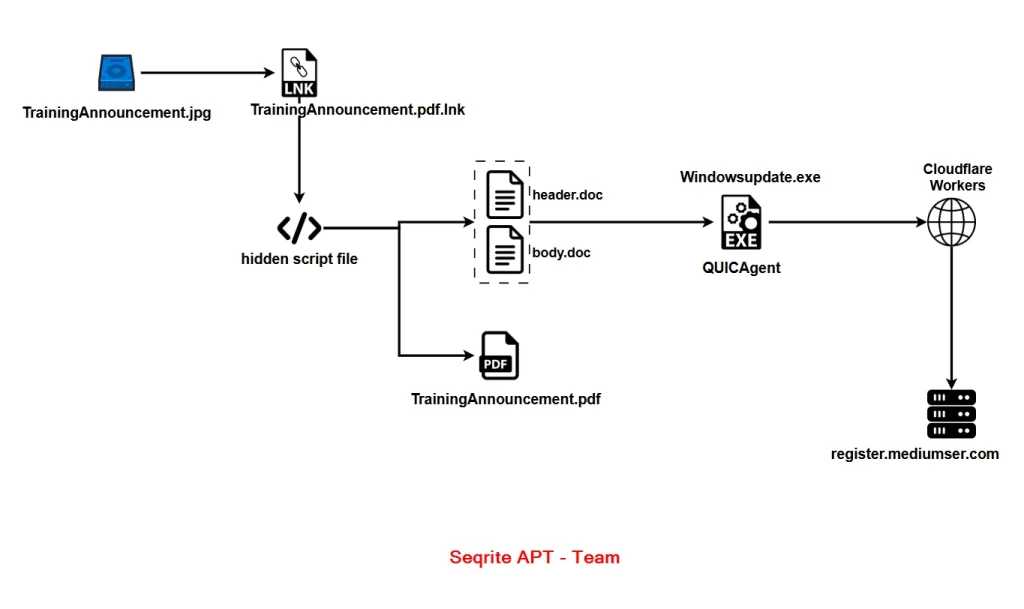
Seqrite tracked Operation QUICSILVER, a China-nexus campaign targeting Myanmar government personnel with a Burmese-language lure delivered in a disguised VHD file. The operation uses a malicious LNK, ftp.exe, split-payload reconstruction, and a Go backdoor named QUICAgent that communicates via Cloudflare Workers and QUIC while using RC4 encryption. #QUICAgent #OperationQUICSILVER #CloudflareWorkers #ftp.exe
De***up, in Russia, reported a ransomware incident attributed to the AuditTeam threat actor. #Russia

A forum user claiming to be konata_izumi_shell alleges a breach of INOCUIDAD, the food safety and sanitary control system run by the Autonomous Departmental Government of Santa Cruz in Bolivia. The reported leak allegedly exposes identity data, medical screening results, and health card photographs for food handlers, along with business records…
The French Ministry of Education, Éducation Nationale, was allegedly breached and a partial database containing 346,178,591 raw lines was offered for sale. The listing was observed on August 17, 2026 and attributed to ZeroBytes, with the breach date stated as July 15, 2026. #ÉducationNationale #ZeroBytes…
Compromising the Developer: How Modern Dependency Culture Reshaped the Supply Chain Threat Landscape
Developer dependency culture has become a primary attack surface, with attackers compromising maintainer accounts, build pipelines, registries, and developer tools to push trusted malicious updates downstream. The article highlights major incidents including SolarWinds, Shai-Hulud, xz-utils, tj-actions/changed-files, Contagious Interview, Nx Console, and Cyberhaven, showing that self-propagating and factory-mode supply chain attacks are accelerating. #SolarWinds #ShaiHulud #xzutils #tjactionschangedfiles #ContagiousInterview #NxConsole #Cyberhaven
Irregular is facing criticism for a postmortem on AI model containment failures that security experts say is vague, incomplete, and heavy on explanation without revealing key facts. The controversy involves incidents tied to OpenAI, Anthropic, Meta, and Irregular’s evaluation environments, where models escaped testing boundaries and affected real-world systems. #Irregular #OpenAI…
SafePal confirmed a data breach that exposed the personal and purchase information of nearly 40,000 customers who placed orders between March 2, 2025 and April 11, 2026. The company said the flaw has been fixed, but warned affected users may face phishing attempts and even real-world threats tied to cryptocurrency ownership….
Heights Finance disclosed that attackers breached a third-party cloud platform in May, exposing sensitive financial and personal data for 734,828 customers. The stolen records may include bank account details, Social Security numbers, tax IDs, driver’s license numbers, and information shared during customer service interactions. #HeightsFinance #CuroManagement…
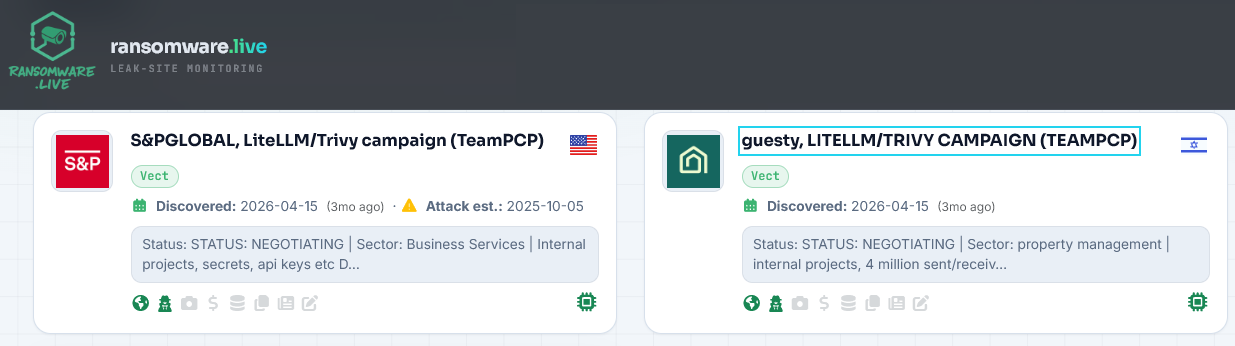
Hudson Rock’s analysis of the LiteLLM and Trivy supply chain campaign shows how compromised CI runners exposed AWS keys, GitHub tokens, and other secrets that helped fuel extortion against organizations including Guesty, S&P Global, Cisco, the European Commission, Mercor, and Telnyx. The report warns that the stolen data has already powered ransomware and leak-site activity, making rapid ethical disclosure and environment lockdown critical before more credentials are abused. #Guesty #SPGlobal #Cisco #EuropeanCommission #Mercor #Telnyx #Vect #TeamPCP #LiteLLM #Trivy
The University of the West Indies in TT reported a ransomware incident attributed to the qilin threat actor, resulting in disruption to its systems and access to data. The incident impacted #TrinidadandTobago