CISA confirmed that ransomware gangs are exploiting CVE-2025-60710, a high-severity Windows Task Host privilege escalation flaw affecting Windows 11 and Windows Server 2025. The agency added the vulnerability to its KEV catalog and urged federal agencies to patch it, while Microsoft has not yet publicly confirmed in-the-wild exploitation. #CVE-2025-60710 #CISA #WindowsTaskHost #Windows11 #WindowsServer2025
Microsoft is testing a faster File Explorer and a redesigned, more customizable context menu in Windows 11 preview builds to improve speed, reduce clutter, and address user feedback. The company is also removing the WMIC tool from newer Windows 11 releases, a LOLBIN that has been abused by cybercriminals. #Microsoft #Windows11 #FileExplorer #WMIC

A critical flaw in the Forminator Forms WordPress plugin, tracked as CVE-2026-15748, can let unauthenticated attackers upload executable files and achieve remote code execution. Defiant says the issue affects more than 300,000 websites running vulnerable versions, though there are no reports of active exploitation yet. #ForminatorForms #CVE-2026-15748 #Defiant…
Fortinet has acquired Virtue AI to strengthen its AI security capabilities for models, conversational applications, and autonomous agents. The Virtue AI platform adds automated red-teaming, real-time guardrails, and continuous validation to help protect enterprise AI systems throughout their lifecycle. #Fortinet #VirtueAI…
Xpander has raised $7.5 million in seed funding led by Pico Venture Partners, with participation from Emerge Ventures, Samsung Next, and Seedil. The startup is building a platform to help organizations adopt, secure, and manage AI agents across environments using a vendor-neutral harness and its Omni agentic engineer. #Xpander #PicoVenturePartners #SamsungNext…

ASEC identified a phishing campaign that impersonated a sales team member to deliver the malicious attachment 7200_Quantum_Enterprise_LLC_SSO-0661.GZ, which contained an injector that disables security software and deploys PhantomStealer. The attack used UAC bypass, BYOVD, and process hollowing to run with elevated privileges, terminate security products, and steal credentials, browser data, and…
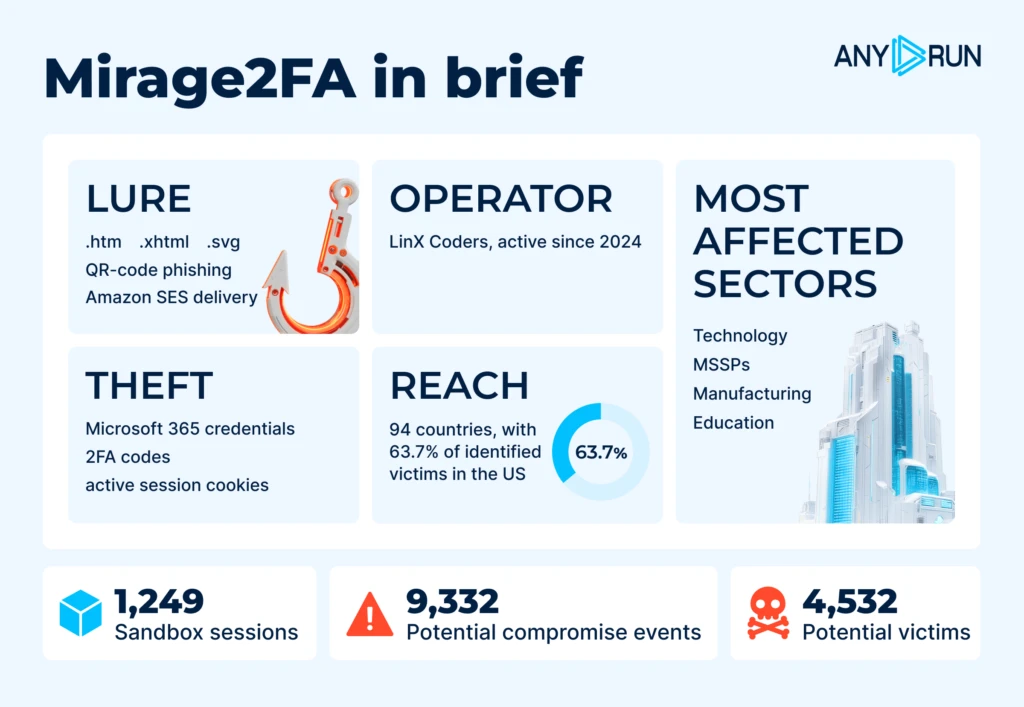
Mirage2FA is a phishing-as-a-service toolkit that steals Microsoft 365 credentials and authenticated sessions using Adversary-in-the-Middle attacks to bypass MFA. ANY.RUN found the campaign is heavily concentrated in the United States and targets industries such as Technologies, Manufacturing, and Education, with thousands of potential compromise events between 2024 and 2026. #Mirage2FA #Microsoft365…

Berlin’s state network was hit by a cyberattack that led to the isolation of two senatorial administrations after an intrusion was discovered. Authorities are investigating the incident, which may have resulted in the exfiltration of sensitive data, with the public prosecutor’s office and the BSI involved. #Berlin #BSI
UT San Antonio detected unauthorized activity on its technology systems over the weekend and suspended certain online and phone services to contain the threat before it reached core systems. The university said no evidence of data theft has been found so far, and payment and registration deadlines were extended while the investigation continues. #UTSanAntonio #utsaedu

WindRose Health Network (WHN), a US healthcare provider in Hope, Indiana, was targeted by the Storm ransomware threat actor. The attack impacted the US. #UnitedStates
The ransomware claim targets the Prefeitura Municipal de Arcos in Brazil (BR) by the threat actor emperador, alleging full access and exfiltration of internal servers, databases, emails, and admin credentials. It further claims critical systems were encrypted and threatens publication and permanent data loss if no response is made within 14 days, contacting the attackers directly with no recovery attempts. #Brazil
Foresee Pharmaceuticals Co., Ltd. (TW) reported a total leak of 1.2TB of confidential data allegedly stolen by incransom, including Drug Master Files (ASMF), FDA/EMA materials, R&D and clinical study reports, financial statements, and other proprietary information. The exposure involved multiple drug development projects and partner-related information impacting Taiwan #Taiwan

CISA has added CVE-2025-62593, a critical Ray flaw that can lead to remote code execution through DNS rebinding attacks in Firefox and Safari, to its Known Exploited Vulnerabilities catalog due to active exploitation. The issue affects Ray development environments and has been linked to abuse by the RondoDox botnet and attacks…
Apple released security updates for macOS Tahoe 26.6.2, iOS 26.6.1, and iPadOS 26.6.1 to fix dozens of flaws, most of them in WebKit, with risks including crashes, memory corruption, and data disclosure. The updates also address a Telephony authentication issue and more than 120 bugs in iOS 18.7.10 and iPadOS 18.7.10,…
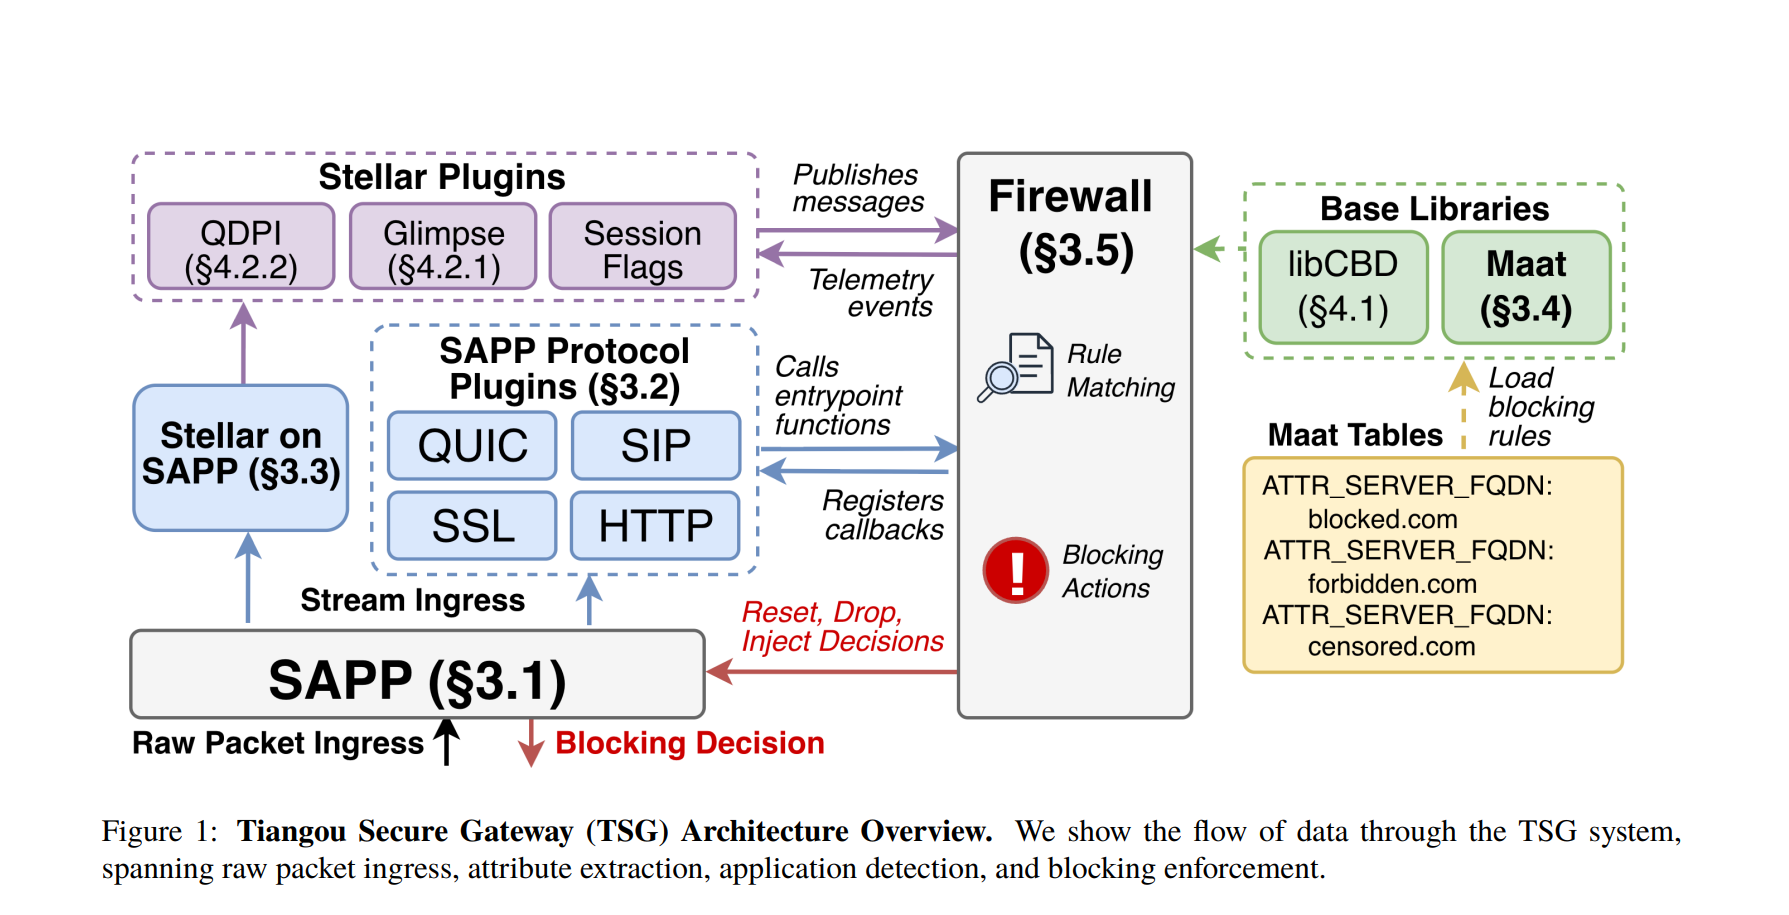
Researchers reconstructed and ran Tiangou Secure Gateway (TSG) in a lab using leaked Geedge Networks source code, revealing how the commercial censorship platform detects and blocks VPNs, Tor, Signal, and other circumvention tools. Their analysis also found strong technical evidence linking TSG to Great Firewall of China components, with deployments tied…