Cl0p has publicly named more than 40 organizations allegedly hit in a campaign that abused CVE-2026-12569 in PTC Windchill and FlexPLM, using web shells and a custom implant to steal data. The stolen information reportedly includes databases, engineering documents, backups, and other sensitive files, with victims ranging from Shell and Philips…
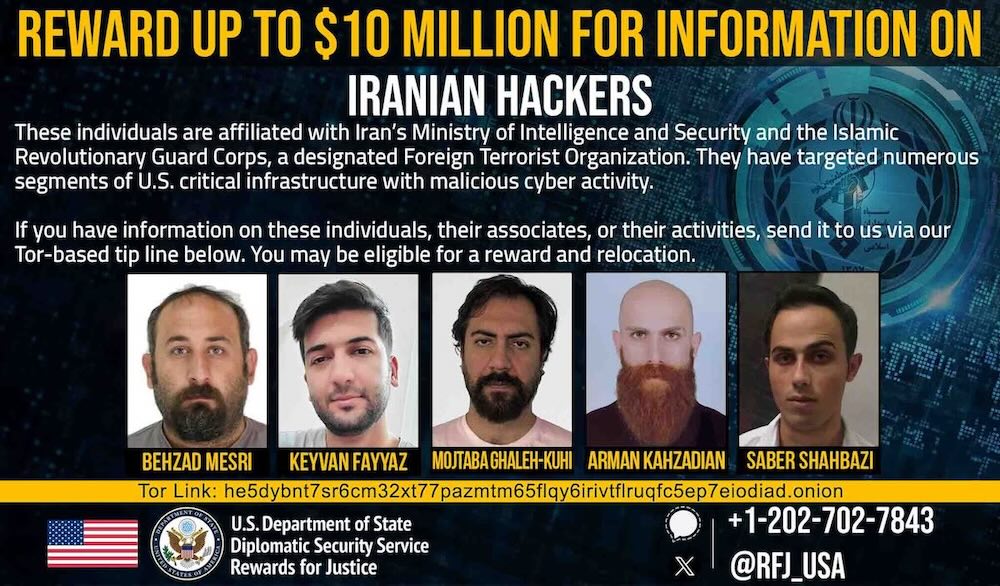
The US announced charges against 17 members of Iran-based Mabna Institute for hacking hundreds of organizations worldwide and stealing more than 31 terabytes of academic data and intellectual property. The group allegedly targeted universities, professors, government agencies, NGOs, and companies, including an extortion attempt against HBO. #MabnaInstitute #IRGC #HBO #Megapaper #Gigapaper…

Prevalent AI has raised $22 million in growth funding from Integrity Growth Partners to expand its data fabric platform and accelerate its US presence. The London-based company uses AI to turn fragmented enterprise security data into a knowledge graph that helps organizations identify gaps, reduce risk, and deploy AI agents securely….
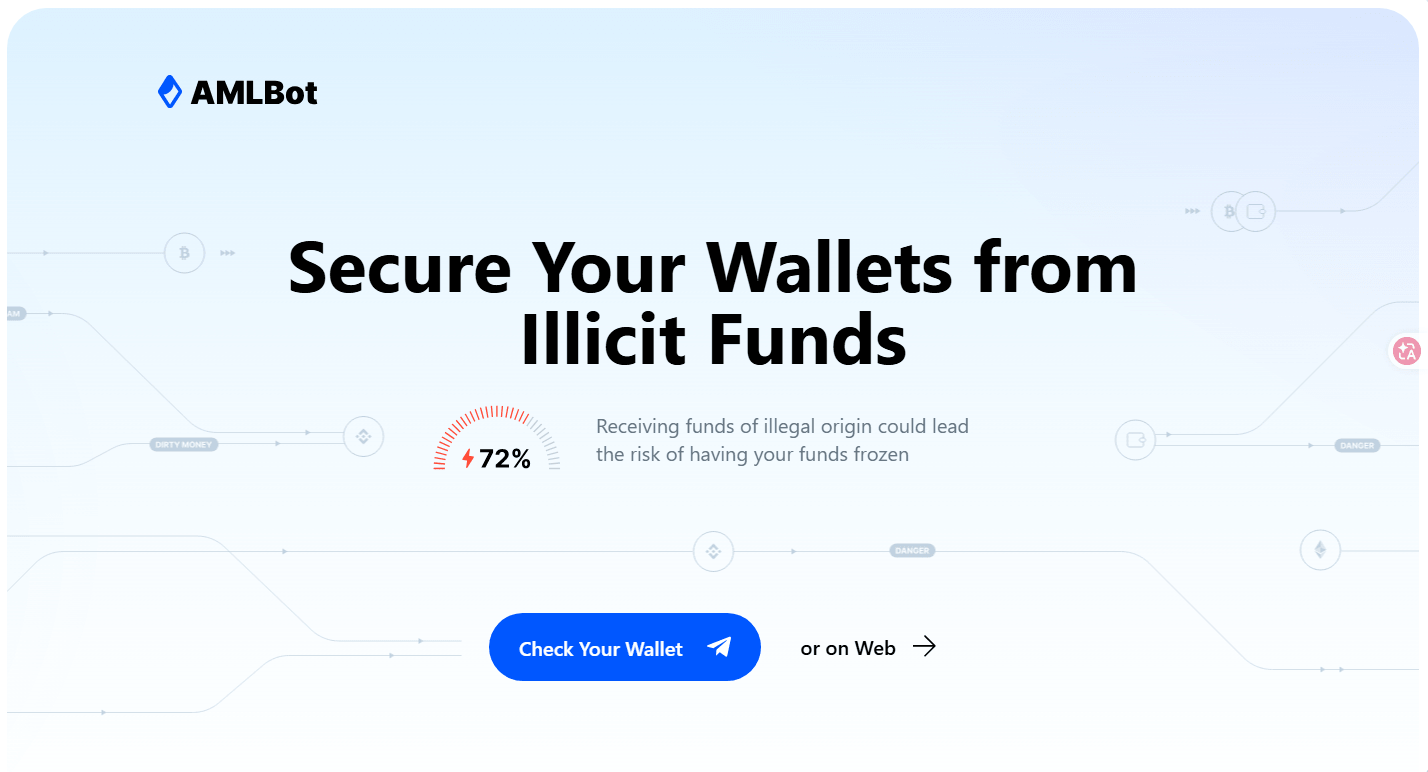
Scammers are using fake AML wallet-checking sites that mimic legitimate services like AMLBot to trick users into connecting wallets and approving malicious transactions. The scheme relies on fake progress screens, fabricated fees, and misleading “Clean, Low Risk” results to steal crypto or gain access to token permissions. #AMLBot #AML Check #Browser…
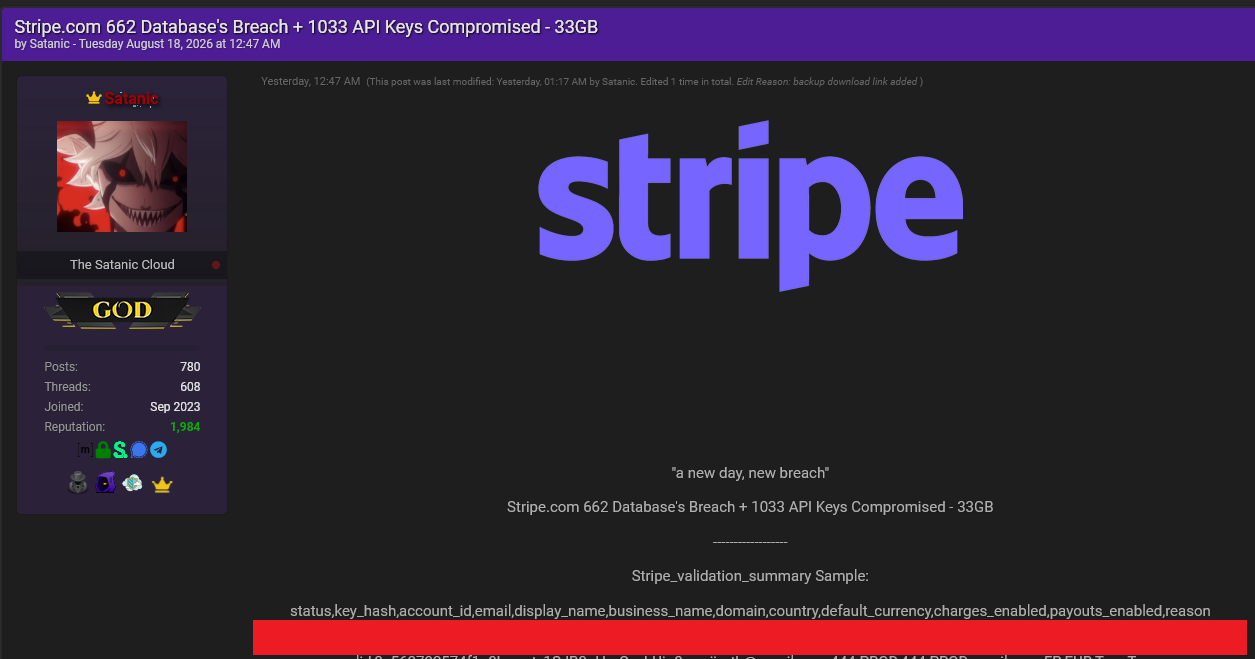
On August 18, 2026, the threat actor Satanic released data on pwnforums allegedly taken from hundreds of vendors using Stripe, including 1,033 API keys and extensive customer and transaction records. The leak suggests a broader compromise of payment infrastructure, with the actor claiming access to roughly 20,000 Stripe API keys and threatening staggered releases. #Satanic #Stripe #pwnforums

A forum user known as Satanic allegedly exported data from hundreds of Stripe merchant accounts using 1,033 compromised API keys, with the claim covering 662 datasets totaling 33GB. The post is unverified, and the evidence suggests merchant credential theft rather than a breach of Stripe itself. #Stripe #Satanic #APIKeys…
The ransomware claim targets CRASL (UK), with the threat actor thegentlemen allegedly aiming to disrupt operations at CRASL Accounting Services in Suffolk. The company offers personalized bookkeeping, tax planning, and strategic business advice to individuals, sole traders, and growing businesses. #UnitedKingdom

Euroscreen, an Italian digital printing and projection screen manufacturer, reported a ransomware claim attributed to thegentlemen, potentially disrupting operations tied to its worldwide audio-visual and printing solutions. The incident impacted IT #Italy
The ransomware claim targets mecasem.org in Mexico and is attributed to the threeam threat actor, emphasizing quality and reliability in its operations. Since 2012, MECASEM’s ISO 17025 (COFRAC) accredited and EN 9100/ISO 9001 certified services are referenced in connection with the alleged compromise. #Mexico

There were 2 defacement incidents reported, targeting Malaysia and India. The attackers involved were dr3n4k and Demon King. #Malaysia #India…
CISA, HHS, and the FBI warned that the Medusa ransomware gang has compromised more than 500 U.S. critical infrastructure organizations since June 2021, affecting sectors such as healthcare, defense, manufacturing, government, IT, and financial services. The agencies urged defenders to patch vulnerabilities, segment networks, and restrict untrusted access to internal remote services to reduce the risk of Medusa attacks. #Medusa #CISA #HHS #FBI
CareCloud has confirmed a much larger data breach than initially reported, with the number of affected individuals now reaching 3,756,469. The intrusion involved access to one of CareCloud’s AWS environments in March, exposing sensitive personal, health, and in some cases payment card information. #CareCloud #AWS…
Lifesum in Sweden was targeted by the direwolf ransomware threat actor, resulting in disruption to Hospitals & Physicians Clinics operations. The incident impacted Sweden #Sweden
Brazil has ordered Discord to suspend its Go Live livestreaming feature while regulators investigate whether the platform failed to protect children from content promoting self-harm and suicide. The case follows a fatal livestream involving a 13-year-old girl and has expanded into broader scrutiny of Discord and Telegram over harmful content, extremist…