
Hunt.io uncovered Operation CameraSwarm, a campaign that compromised more than 14,530 Dahua devices by combining credential attacks, CVE-2021-33044, CVE-2021-33045, and a P2P relay method. The recovered tooling and logs suggested concentrated activity in Ukraine and Russia, while defenders are urged to update firmware, disable unnecessary P2P access, and review Easy4IP exposure….

SilkParasite is a previously unreported espionage campaign targeting government bodies in Central Asia with a modular toolset built around seven RAT families, including five newly documented ones. The operation appears China-nexus and uses regional spear-phishing, DLL sideloading, and cloud-based C2 to stay stealthy and adapt quickly. #SilkParasite #BLOODALCHEMY #SpiceRAT #DriveSilkRAT #CookiETagRAT…
CodeSecCon brings together more than 1,500 attendees to explore how developers and security professionals can build, secure, and maintain applications more effectively. The event focuses on secure coding, reducing software vulnerabilities, DevSecOps collaboration, and safely integrating AI into applications while minimizing sensitive data exposure. #CodeSecCon #DevSecOps #Auth0 #Wiz #Datadog #WordPress #Schlumberger…

Insomnia ransomware targeted Aurora Health Management, a U.S. skilled nursing and rehab operator in Frederick, Maryland, seeking to disrupt operations and compromise systems. The claim describes an incident affecting Aurora’s services in the United States. #UnitedStates
Ransomware actor akira reportedly targeted Ericksen Krentel CPAs and Consultants, a New Orleans-based CPA firm, threatening to leak extensive corporate data including detailed client and employee personal information (passports, DLs, SSNs, addresses) along with confidential financials, documents, contracts, and NDAs. The impacted country(s): #UnitedStates
Advanced Engineering Consultants, associated with the coinbasecartel threat actor, allegedly suffered ransomware activity that disrupted access to their systems and data. The impacted country(s): #undefined
CISA has warned that attackers are actively exploiting CVE-2026-33824, a critical remote code execution flaw in the Windows IKE Extension that affects supported Windows 10, Windows 11, and Windows Server systems. Microsoft advises immediate patching, or temporary firewall restrictions on UDP ports 500 and 4500, as CISA orders U.S. federal agencies to remediate the issue within three days. #CVE-2026-33824 #WindowsIKEExtension #CISA #Microsoft #Windows10 #Windows11 #WindowsServer
Microsoft has fixed a bug in Windows Defender that caused access violation errors and service crashes after a recent security update on some Windows 10 and Windows 11 systems. The issue triggered “Threat service has stopped. Restart it now” messages, and Microsoft says the correction is included in Defender signature update version 1.457.236.0 or later. #WindowsDefender #MicrosoftDefender
Huntress reported a 155x surge in password spraying during the first half of 2026, driven in part by the LSHIY campaign targeting Microsoft Azure CLI and abusing legacy ROPC authentication. The attacks used IPv6 BYOIP infrastructure, exposed gaps in Conditional Access coverage, and succeeded where MFA did not apply to the specific sign-in flow. #LSHIY #AzureCLI #ROPC #MicrosoftAzure #Entra #LSHIYLLC

CG Power reported a suspected cybersecurity incident affecting its IT systems, while confirming that its core operational systems and manufacturing production remained unaffected. The company said the incident is under investigation by internal and external experts and has been notified to CERT-In. #CGPower #CERTIn
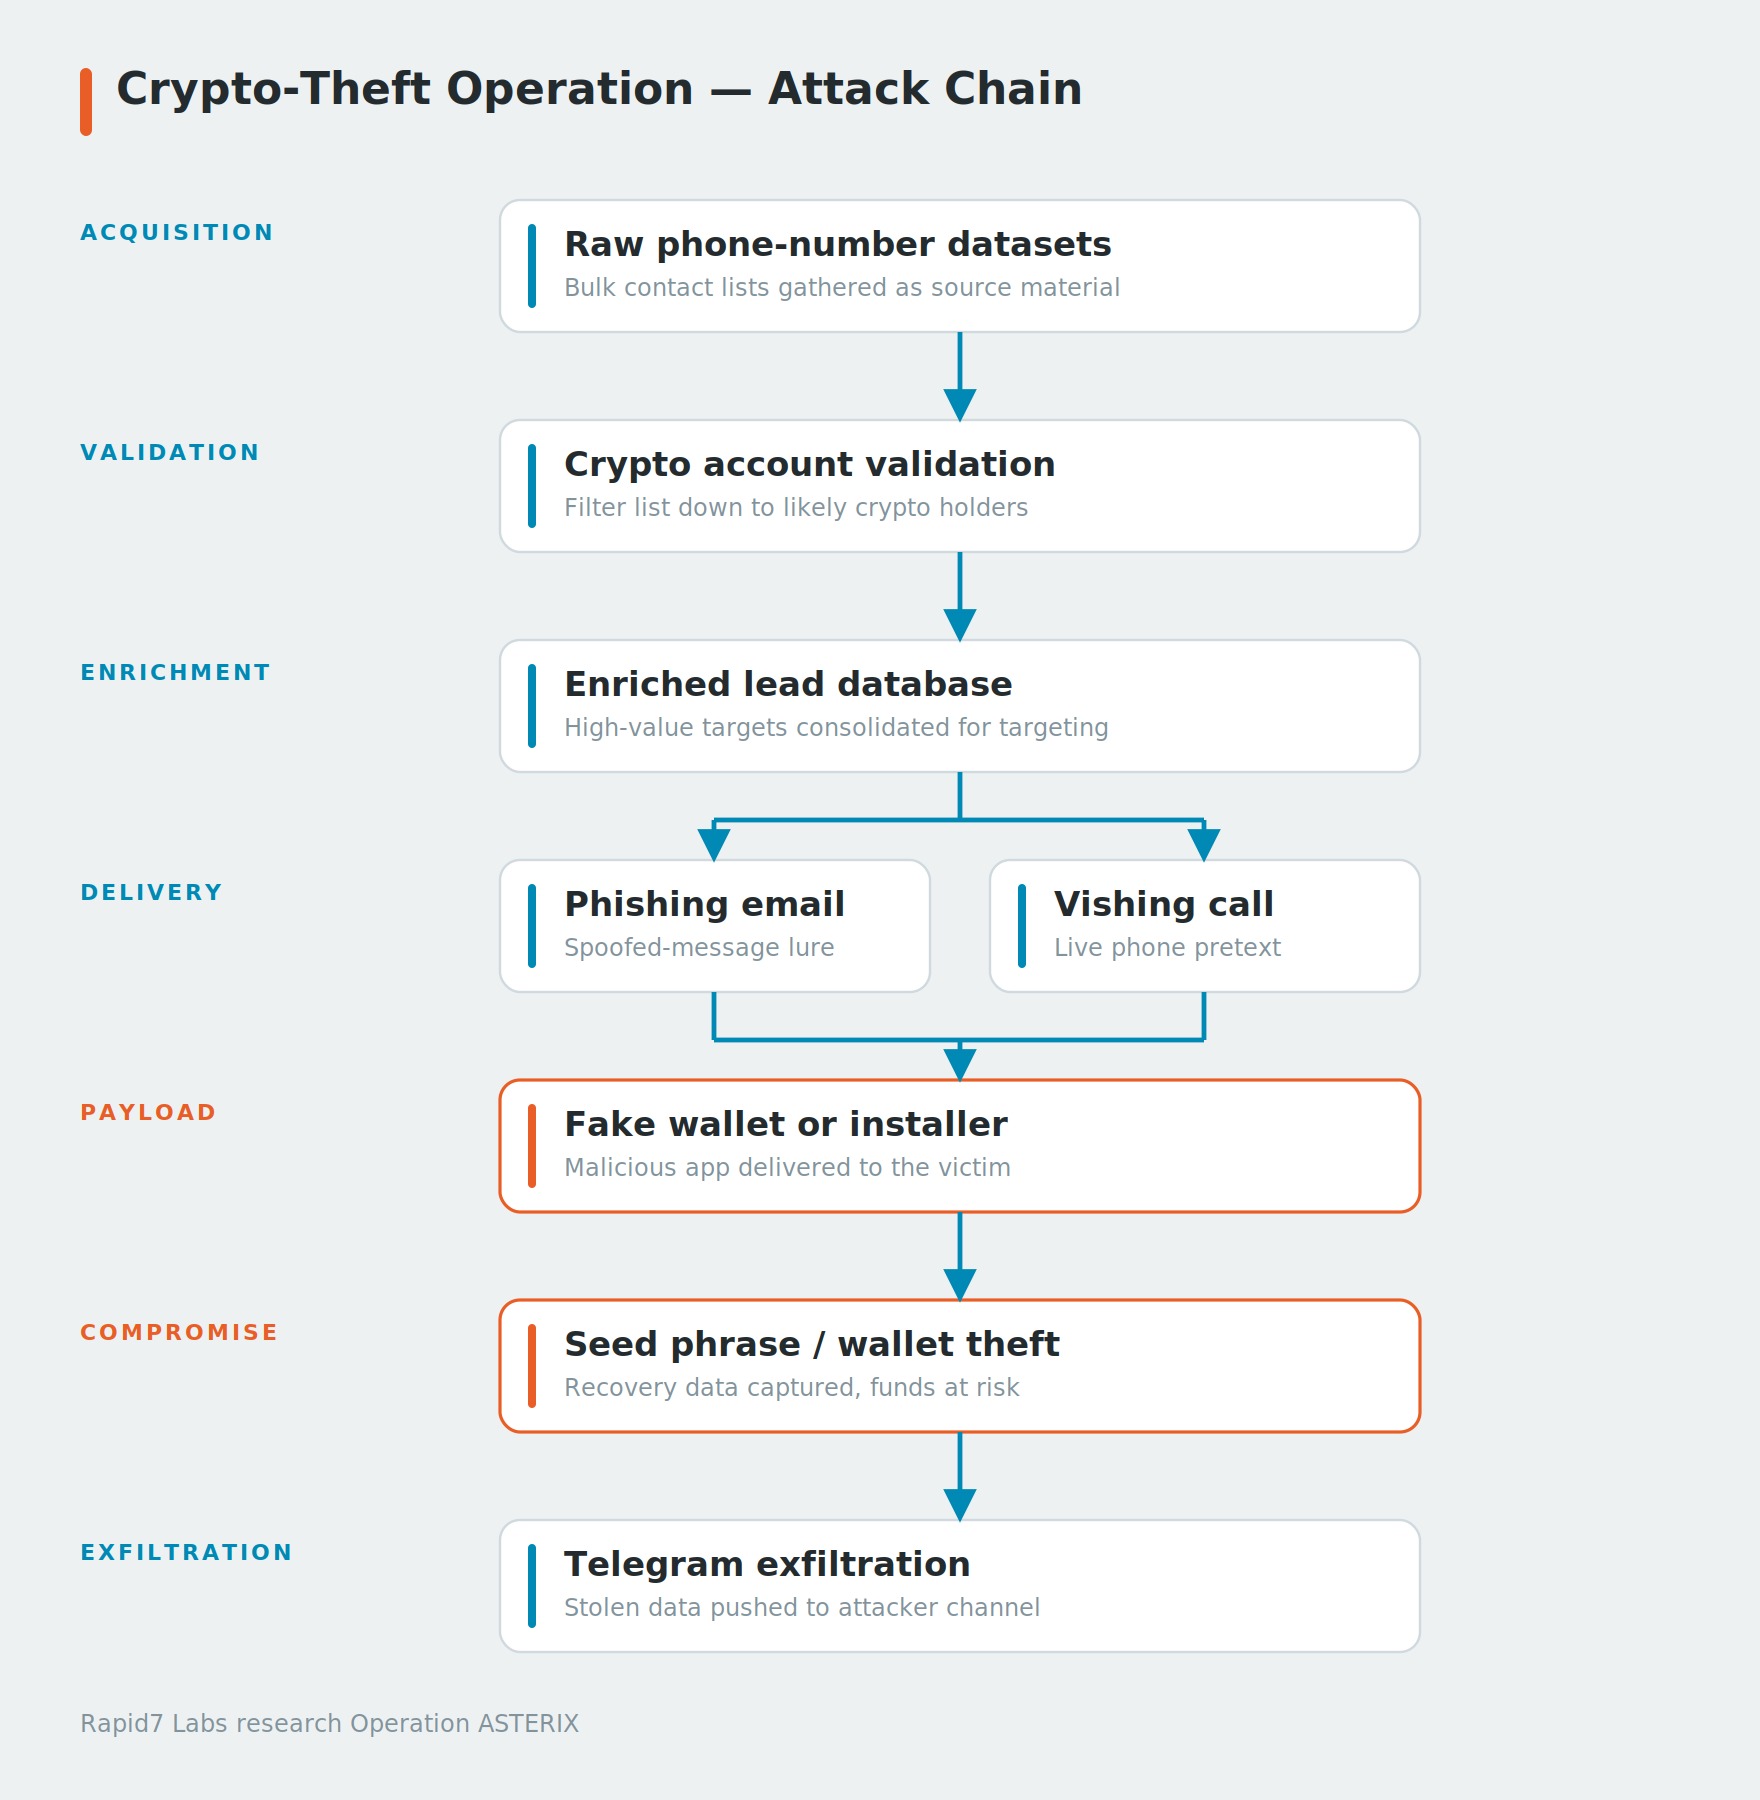
Rapid7 uncovered Operation ASTERIX, a cryptocurrency fraud campaign that used exposed infrastructure to stage phishing panels, vishing tools, fake wallet apps, and Telegram exfiltration while heavily relying on AI coding assistants during development. The operator also tried to bypass model safety controls with a custom jailbreak prompt after one AI model resisted parts of the workflow. #OperationASTERIX #TrezorSuite #LedgerLive #Exodus #Asterisk #Crypto.com #Kraken

Gen Threat Labs identified WordlistLoader, a new loader used in ClearFake campaigns to deliver Amatera Stealer through fake CAPTCHA and ClickFix-style infection chains. The report also details major Amatera changes through version 4.3.3-alpha1, including stronger obfuscation, WoW64/Heaven’s Gate syscall hardening, x64 syscall trampolines, and a redesigned Application-Bound Encryption bypass. #WordlistLoader #AmateraStealer #ClearFake #FakeCaptchas #ClickFix #HeavensGate #WoW64 #PoolParty
The ransomware claim targets sipresitalia.it in Italy, attributed to the krybit threat actor, affecting S.I.P.R.E.S. SRL (Società Italiana Progetti Ricerche e Sviluppo — Italian Research and Development Projects Company). The attacker’s operation resulted in data compromise and disruption for the organization in #Italy
Automotoresrosedal.com.ar, an Argentine organization (Rosedal Automotores S.R.L.), was targeted by ransomware activity attributed to krybit in Argentina. The attackers encrypted or disrupted victim systems, impacting operations and data access within #Argentina
The ransomware group krybit targeted the official website of the municipality of Jilemnice (www.mestojilemnice.cz), affecting local services in CZ. The incident impacted #Czechia