
Researchers disclosed a remote Spectre attack against Cloudflare Workers that leaked a JWT from a co-located Worker in production at up to 12 bits per second, far faster than the 2021 attack. Cloudflare said the issue has been mitigated with improved DyPrIs, the V8 Sandbox, and MPK-based in-process isolation, and reported…

GrecoSteel.com (GR) suffered a ransomware attack attributed to threat actor settra, leading to disrupted access to finance and payroll systems after the attackers accessed and encrypted/probed critical environments under a broad “PROLOGUE: 19 document categories” staging. The resulting operational shutdown and financial control loss impacted Greece #Greece
In a ransomware incident involving am-bition.jp in Japan, the threat actor settra reportedly targeted internal documents related to the AMBITION Group and its insurance partner Hope SSI PROLOGUE AMBITION Co., L…. The intrusion resulted in unauthorized access and encryption/exfiltration of sensitive corporate materials. #Japan
Target reports a ransomware incident allegedly carried out by the xpl0itrs threat actor, impacting its general merchandise retail operations in the US. The claim indicates unauthorized access and disruptive effects associated with the attack, with impacts attributed to #UnitedStates
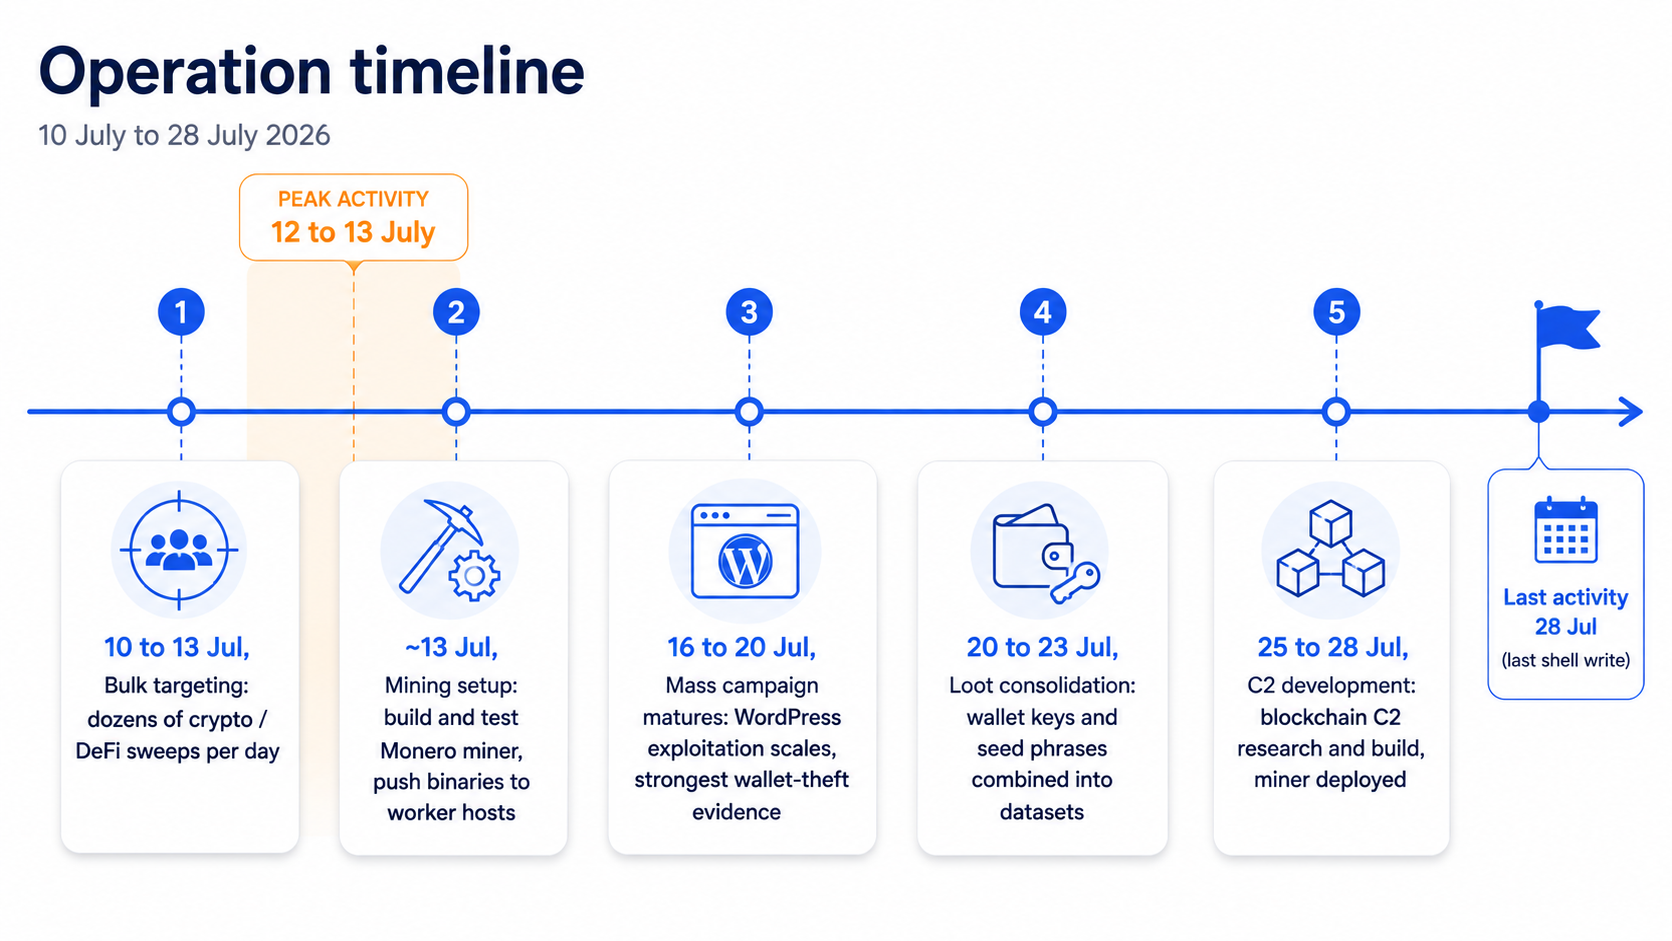
CloudSEK found an exposed directory belonging to a Chinese-speaking operator who used AI coding agents, Telegram, and a self-hosted LLM proxy to run autonomous intrusions against WordPress sites, crypto/DeFi targets, and wallet-bearing phishing databases. The operator also built a blockchain-based DeadDropC2 concept and deployed a disguised Monero miner, while leaving behind over 12,000 WordPress backdoors, harvested credentials, and large sets of wallet keys and seed phrases. #WordPress #DeadDropC2 #Monero #Telegram #ClaudeCode #Codex #Hermes #pi #ZhipuGLM
Latvia’s Road Traffic Safety Directorate (CSDD) suffered a large-scale cyberattack that exposed data tied to 1.2 million individuals and 200,000 companies, including names, payment details, licence plates, and registered addresses. Authorities warned the stolen information could be abused by fraudsters, while Prime Minister Andris Kulbergs ordered an investigation and said the incident may have national security implications. #CSDD #AndrisKulbergs #Leta
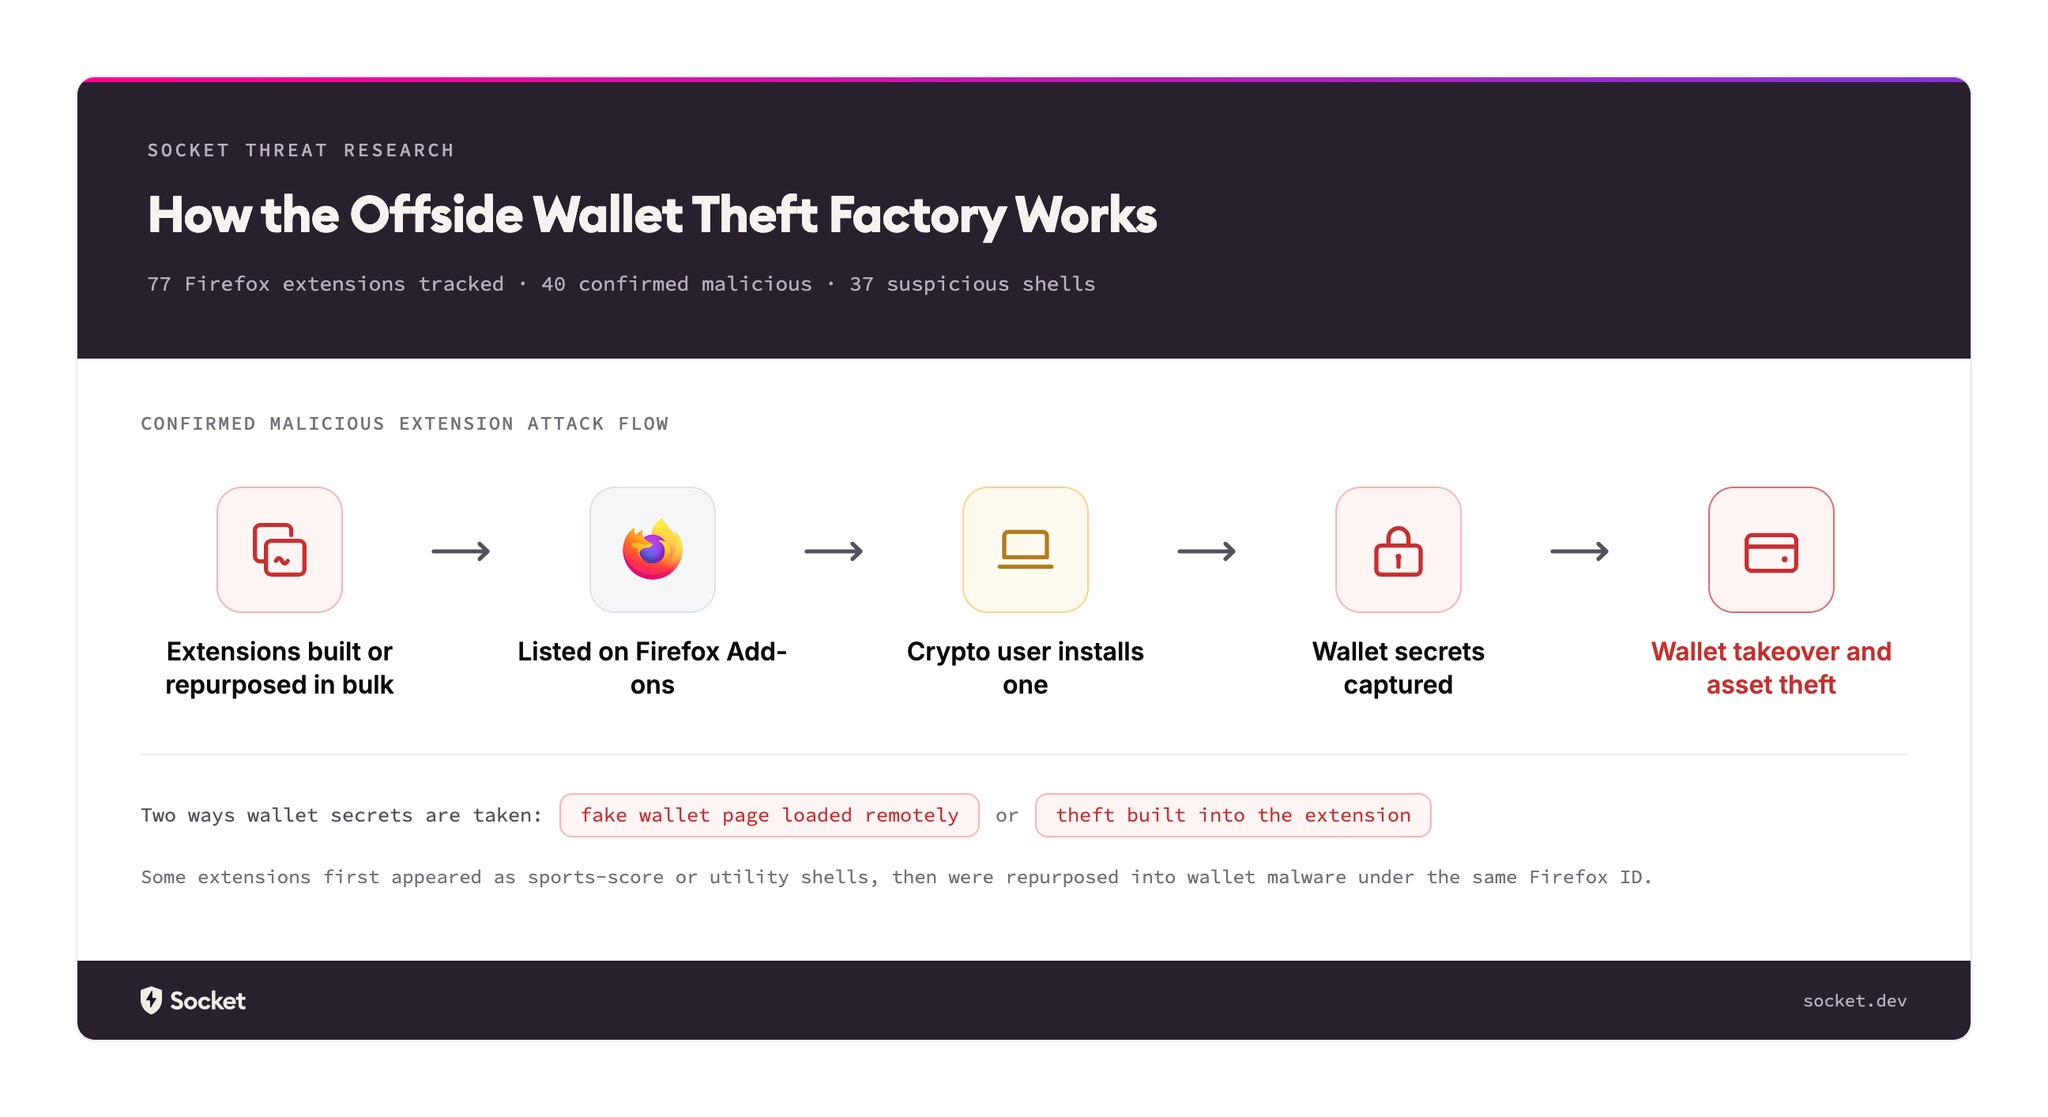
Socket Threat Research identified 77 Firefox extension identities linked to the “Offside Wallet Theft Factory,” with 40 confirmed malicious extensions that steal wallet secrets or credentials and 37 deceptive sports-score shells that appear to support the same publishing pipeline. The campaign impersonates OKX, Rabby Wallet, TronLink, and other Web3 products using Supabase-controlled loaders, Cloudflare Workers, hardcoded C2 infrastructure, and version repurposing across Firefox IDs. #Firefox #Supabase #CloudflareWorkers #RabbyWallet #OKX #TronLink
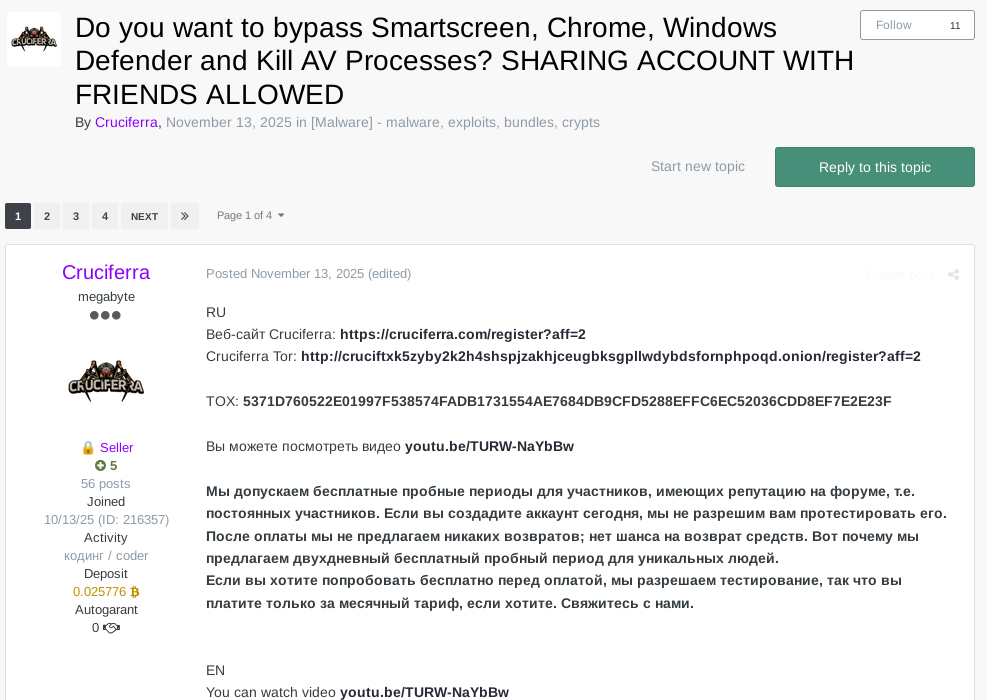
In late July 2026, eSentire TRU reported ErrTraffic-generated ClickFix campaigns that delivered the Cruciferra loader, which abused the signed vulnerable driver DCRCVDrv.sys to kill AV/EDR processes from the kernel. The campaigns used compromised WordPress sites, blockchain-based dead-drop C2 infrastructure, and fake CAPTCHA/BSOD lures to trick victims into running malicious PowerShell while deploying Remus through side-loading and process hollowing. #Cruciferra #ErrTraffic #DCRCVDrvsys #Remus #MocoMsys #ServiceModelRegexe
A network of 41 websites impersonated popular games and Windows software to funnel visitors toward installing Download Studio, using deceptive click handling, affiliate redirects, and convincing fake download pages. The campaign included genuine-looking links, valid signatures, and prior abuse history tied to Download Studio’s updater, including FakeMBAM distribution by Avast-reported attackers….
U.S. cybersecurity agencies warned that threat actors are using AI-generated Python scripts to exploit Siemens S7 Series PLCs in critical infrastructure, with activity also extending beyond Siemens devices. The ongoing attacks target sectors such as energy, water, manufacturing, and food, with the apparent goal of reconnaissance, disruption, data theft, and potential safety incidents. #SiemensS7 #CISA #NSA #FBI #DepartmentofEnergy #EnvironmentalProtectionAgency
CareCloud disclosed that a breach affecting its AWS environment impacted 3,756,469 people and may have exposed patient-related data from its databases. The company said the intrusion caused an 8-hour network disruption, and affected individuals are being offered identity protection services while investigators continue reviewing the incident. #CareCloud #AWS
Sakura Internet disclosed that attackers accessed its sales management system, potentially exposing customer contract and membership information from up to 1,360,563 member accounts. The company says passwords were hashed, no credit card data was stored in the affected system, and it has notified authorities and impacted customers. #SakuraInternet #JapanGovernmentCloud
A suspected ransomware affiliate is impersonating a recovery service called Ransom Busters, emailing victims before attacks are public and claiming it can provide decryption keys and erase stolen data for a fee. GRIT and Coveware believe the activity may be tied to the same affiliate behind attacks involving DragonForce, Settra, and Anubis, using overlapping tools and tactics to extort victims and siphon ransom payments. #RansomBusters #DragonForce #Settra #Anubis
Alphanumeric.com, an American IT company, reported ransomware activity attributed to the settra threat actor (ALPHANUMERIC SYSTEMS, INC.), involving access to and potential exfiltration of internal documents. The impacted country is #UnitedStates
The ransomware claim from threat actor settra targets wcmanagement.info, alleging encryption of documents related to West Coast Management and Realty PROLOGUE, including over 1,000 debt collection records with names. The statement was posted without a specified country of impact, so impacted country(s): #unknown