U.S. Bank (usbank.com) in the United States was targeted in a ransomware claim attributed to LockBit 5, following an intrusion where attackers sought to encrypt or disrupt data and extort the victim. The incident impacted the United States #UnitedStates

Titan ransomware operators have targeted ELCON MEGARAD S.p.A., an Italy-based manufacturer of radiation-crosslinked materials and heat-shrinkable products used across electrical and industrial applications. The attack by the titan threat actor has resulted in disruption to the victim’s operations in the impacted country(s): #Italy
Austin Plastic Surgery Institute in the US reported a ransomware incident involving the pear threat actor. The attack disrupted services at a center staffed by highly skilled plastic surgeons, impacting the United States #UnitedStates
SafePal disclosed a breach that exposed order and contact details for about 39,798 customers because of an authorization flaw in an order-tracking plug-in. The company says seed phrases, private keys, wallet passwords, and funds were not exposed, while a threat actor now claims to be selling the stolen data. #SafePal…
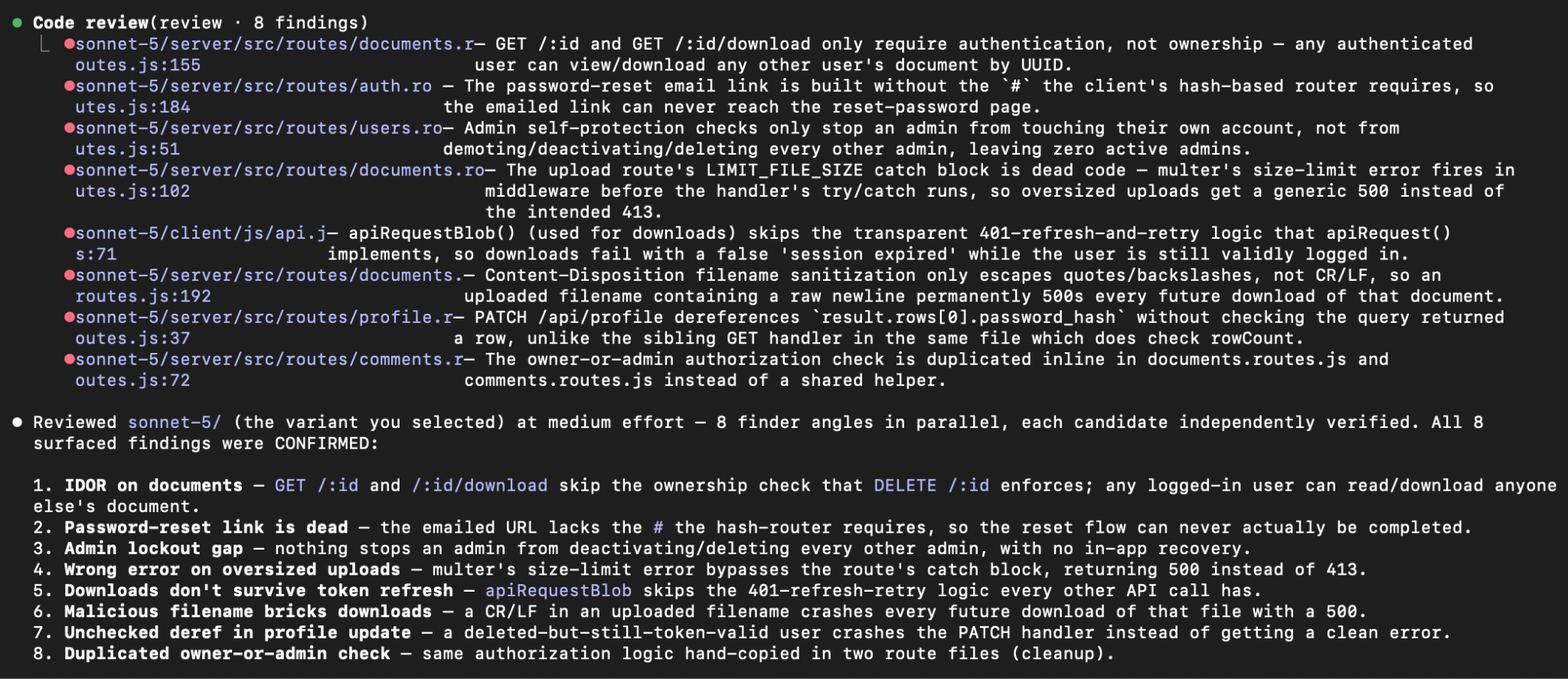
The article compares how three coding agents performed in default and plan modes while building a document portal, measuring security, architecture, and code quality across six iterations. The biggest recurring flaw was critical IDOR across document routes, while the most severe single failure was Composer 2.5 plan mode’s hardcoded JWT secret that could enable authentication forgery and admin impersonation. #Sonnet5 #Composer25 #GPT55 #IDOR
Grandoreiro remains active in Latin America, with recent campaigns using Duplicate Files Finder DLL sideloading, heavy anti-analysis checks, and encrypted C2 communications to evade detection. Telemetry from June 2026 shows Mexico as the primary hotspot, while the campaign also uses spoofed filenames, decoy documents, and a broad blacklist of tools, hosts, and virtualized environments. #Grandoreiro #DuplicateFilesFinder #ip-api.com #nhlfan.net

There was 1 defacement incident targeting Mexico, with the site https://alamotemapache.gob.mx/ce6c2e453e3f.htm defaced. The attacker involved was CoupDeGrace. #Mexico…
makfreight.com in Malaysia reported a ransomware claim attributed to threat actor settra, following exploitation of vulnerabilities described as part of an intrusion affecting M.A.K. Freight Systems. The incident highlights impacts associated with this attack chain and concludes with the impacted country #Malaysia
Capgemini Engineering (France) reported a ransomware incident involving the everest threat actor, disrupting operations for its engineering and R&D services. The claim indicates impacts stemming from the attack within its operational footprint in #France
Deadlock ransomware actors targeted JP Molyneux Studio Ltd, based in GB, threatening to disrupt access to its exclusive work by internationally renowned interior designer Juan Pablo Molyneux. The claim is attributed to the Deadlock threat actor. #UnitedKingdom

Researchers disclosed a critical flaw in Elementor Pro, tracked as CVE-2026-32475, that can let an unauthenticated attacker upload a PHP file and achieve remote code execution on WordPress sites running versions up to 4.2.1. The report also notes a separate WordPress core issue involving malicious Postscript uploads, while a large-scale operation…

U.S. government agencies have warned critical infrastructure operators about active reconnaissance and exploit development targeting Siemens PLCs across multiple industrial sectors. The advisory says attackers are using AI-generated scripts and open source OT libraries to build tools that could disrupt operations, damage equipment, and tamper with Siemens devices. #Siemens #PLC #NSA…
Grupo DT in Mexico reportedly fell victim to the everest ransomware, resulting in unauthorized access and disruption of their systems. The incident is associated with data encryption and extortion demands by the Threat Actor, impacting #Mexico
Experts Entreprendre in FR reported a ransomware incident attributed to the everest threat actor, involving unauthorized encryption and disruption of business operations. The impacted country is #France
Everest ransomware actors targeted Kingston Technology, a US-based memory and storage manufacturer, causing disruption to the company’s operations and systems. The impacted country(s) is/are #UnitedStates