A threat actor carried out Operation CameraSwarm, compromising more than 14,000 Dahua IP cameras across Ukraine and Russia by combining brute-force attacks with authentication bypasses and a persistent RPC backdoor. Hunt.io found exposed attacker infrastructure and evidence that the toolkit was prepared for reuse or handoff, but the operator’s final motive…
Surveillance is being expanded by companies, employers, criminals, law enforcement, and intelligence agencies, all of whom collect data for their own benefit rather than for users’ privacy. The article warns that AI is making these practices faster, broader, and more invasive, while regulations like GDPR, BIPA, and Daniel’s Law offer only…
CERT Polska says CVE-2026-73570, a recently patched Zimbra Collaboration flaw, is being actively exploited in the wild. The issue affects systems with the optional zimbra-snmp package and SNMP notifications enabled, allowing unauthenticated attackers to run arbitrary OS commands as the Zimbra user. #CVE-2026-73570 #ZimbraCollaboration #CERTPolska…
AI has transformed phishing into a faster, more personalized, and harder-to-detect threat that can bypass traditional email filters and lead to rapid account compromise. The article explains why MSPs must move beyond inbox-only defenses and use behavior monitoring, identity detection, and rapid response to stop attacks before they become costly breaches. #Kaseya #IBM #HarvardBusinessReview
A critical flaw in Elementor Pro, tracked as CVE-2026-32475, can let attackers upload a malicious PHP file and achieve remote code execution on vulnerable WordPress servers. The issue affects Elementor Pro versions before 4.2.2 and only sites using a published Elementor Form with a File Upload field and the multiple file upload option enabled, with no active exploitation seen yet. #CVE-2026-32475 #ElementorPro #Patchstack #WordPress

The ransomware attack attributed to DYSPHOR1A targeted an Indonesian Police Database (ID), claiming access to records of 52,000 Indonesian police officers, including email addresses, phone numbers, names, passwords, location details, and 4,000 facial photographs. The impacted country is #Indonesia
The DYSPHOR1A ransomware actors compromised GUSTO College’s GLMS (Global Learning Management System) in TH, accessing exposed user credentials from the Moodle platform at gusto-education.com. The impacted country is #Thailand.
DYSPHOR1A ransomware actors claimed to have leaked data from AYUDHYA TH Insurance (Allianz Thailand), targeting a financial/transaction batch-processing system behind Allianz’s customer-facing web platform. The attackers allegedly accessed internal batch-control systems and extracted admin credentials (TBH2CASH:AAbb1234). #Thailand

A new report from Americans for Responsible Innovation urges the federal government to treat key AI models, companies, and supporting industries as critical infrastructure and to name CISA as the lead agency for AI-related cyberthreats. The report argues that the AI stack is deeply interconnected with other critical sectors, making it vulnerable to disruptions that could cascade across the economy and national security. #AmericansforResponsibleInnovation #CISA #OpenAI #Anthropic #ANCHORCI
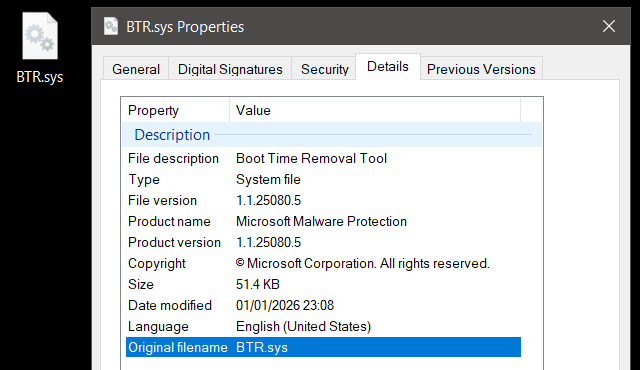
This research reverse engineers Windows Defender’s BTR.sys boot-time remediation driver and shows how its encrypted transaction format can be abused to perform arbitrary file and registry operations from Ring 0. The paper also introduces BTR_CLI, demonstrates EDR/AV bypass and boot-time neutralization against Microsoft Defender, and highlights the defensive implications of a signed built-in LOLDriver. #BTR.sys #BTR_CLI #MicrosoftDefender #MsMpEng.exe #WdFilter.sys #WdBoot.sys #WdNisDrv.sys #Mimikatz #mimidrv.sys #MSRC

ShieldBreak is a Windows proof of concept from Nightmare-Eclipse that chains Cloud Files, Object Manager manipulation, Defender APIs, and a timing race to achieve local privilege escalation on fully patched Windows systems. It ultimately writes an attacker-controlled DLL to C:WindowsSystem32phoneinfo.dll and triggers SYSTEM code execution through the Windows Error Reporting QueueReporting task. #NightmareEclipse #ShieldBreak #phoneinfo.dll #MpClient.dll #QueueReporting
CISA warned federal agencies that attackers are exploiting CVE-2026-64849, a critical MLflow DNS-rebinding SSRF bypass that can expose internal services and cloud metadata on unpatched systems. The flaw in MLflow’s webhook delivery can let unauthenticated attackers steal AWS IAM credentials, prompting CISA to add it to its exploited-in-the-wild catalog and order rapid patching. #CVE-2026-64849 #MLflow #CISA #AWSIMDS #IAM
OpenAI has introduced stricter containment, sandboxing, and token-level monitoring for AI research models with advanced cybersecurity capabilities, after internal testing suggested the upcoming Astra model may reach the company’s critical capability threshold. The changes, driven in part by a Hugging Face security incident, add continuous oversight and operational pauses to reduce…

Russia’s 2022 attack on Viasat showed how satellite communications can be disrupted at scale, and Atalanta’s new AI-assisted Argo platform is designed to help prove and improve resilience against similar threats. The technology is also being applied to critical infrastructure and government projects as concerns grow over Russian and Iranian activity…

Cisco released patches for 15 vulnerabilities across Crosswork, Secure Workload, BroadWorks, and other products, including several critical flaws that could enable remote code execution, authentication bypass, and sensitive file access. Cisco said it is not aware of any of the issues being exploited in the wild, and fixes are now available…