North Korean hackers conducted a supply chain attack against the Rust ecosystem by poisoning the popular arrayref crate and related packages on crates.io. Wiz linked the operation to Sapphire Sleet, noting infrastructure overlaps with earlier Axios and Mastra NPM campaigns and a malicious dependency impersonating proc-macro2. #SapphireSleet #arrayref #proc-macro2 #crates.io…
A critical type confusion flaw in the isolated-vm Node.js library could let attackers achieve remote code execution on the host by abusing the ExternalCopy transfer process across V8 isolates. The issue affects embedders running untrusted JavaScript with shared References and was fixed in isolated-vm versions 6.2.0 and 7.0.1. #isolated-vm #ExternalCopy #V8…

iAuthFlow V2 is a high-end phishing toolkit sold on a Russian-language cybercrime forum that can maintain access to a victim’s account even after a password reset. Abnormal’s analysis suggests the toolkit silently registers an attacker-controlled passkey during a phishing flow, making traditional recovery steps insufficient. #iAuthFlowV2 #Abnormal #Google #Gmail #passkeys…

Baylor Genetics disclosed a cybersecurity incident in which an unauthorized third party accessed parts of its network between June 11 and June 17, 2026, potentially exposing personal information for patients and some current or former employees. The company secured affected systems, completed a forensic review, notified impacted individuals, and confirmed that laboratory operations, patient care, and test result integrity were not affected. #BaylorGenetics
SickKids said a cybersecurity incident exposed personal information belonging to some current and former employees, as well as job applicants, due to a flaw in third-party software. The hospital says clinical systems and patient records were not affected, and it has restored the Careers website while continuing its investigation with outside experts. #SickKids #Boomerang #SickKidsFoundation #MOVEitTransfer #LockBit
Threat actors are abusing FTP server banners as dead-drop resolvers to deliver commands that install two previously undocumented remote access trojans, E4del and PINHOLE. The campaign likely begins with phishing-delivered ZIP and LNK files, while PINHOLE and E4del use unusual C2 and execution techniques to maintain access and evade detection. #E4del #PINHOLE #SOCRadar #MalwareHunterTeam
Microsoft has patched CVE-2026-69836, a maximum-severity flaw in Entra ID that allowed unauthenticated attackers to execute code over the network in low-complexity attacks. Microsoft says the issue has been fully mitigated and no user action is required, while also addressing several other critical flaws across Azure Arc, Exchange Online, and Azure Managed Instance for Apache Cassandra. #EntraID #CVE-2026-69836 #AzureArc #ExchangeOnline #AzureManagedInstanceforApacheCassandra

First Commerce LLC, a privately held real estate investment and development company in the US, was targeted by the pear ransomware threat actor, resulting in encrypted files and a disruption of operations. The incident is reported as affecting the United States #UnitedStates
Clifton Architectural Glass & Metal, a US-based company that installs double-pane windows, reported a ransomware incident attributed to the pear threat actor. The attack impacted their operations in the United States #UnitedStates
Battle Creek Public Schools in the US reported a ransomware incident attributed to threat actor rhysida, impacting student records including IEP/special-ed files, disability determinations, and discipline/suspension records, along with federal funds compliance and staff health-spending documentation. The exposed data also included ESSA/Title I application materials and payflex/EHA-related claims, with impacts affecting #UnitedStates.

There were 3 defacement incidents targeting Greece and the United States, with one incident against govpresidency.gov.gr in Greece and two incidents against elyon.edu and merkaz.edu in the United States. The attackers involved were AnsBix8 and maw3six. #Greece #UnitedStates…
zLabs identified ToxicPanda 2.0, an updated Android banking Trojan that greatly expands its command set, targeting scope, and fraud capabilities, including PIN theft, lock-screen credential harvesting, and abuse of Android Wireless Debugging for shell access. The campaign also shifts delivery to Amazon AWS-hosted buckets and targets 349 financial apps and 140+ banking and cryptocurrency apps across 16 countries. #ToxicPanda #AmazonAWS #AndroidAccessibilityService #ADB #SPAKE2
CareCloud reported that a March data breach affected 3,756,469 people after a hacker accessed one of its AWS electronic health record environments for eight hours and exfiltrated sensitive data. The exposed information included Social Security numbers, ID numbers, payment card details, medical records, and insurance data, prompting notifications to regulators and…
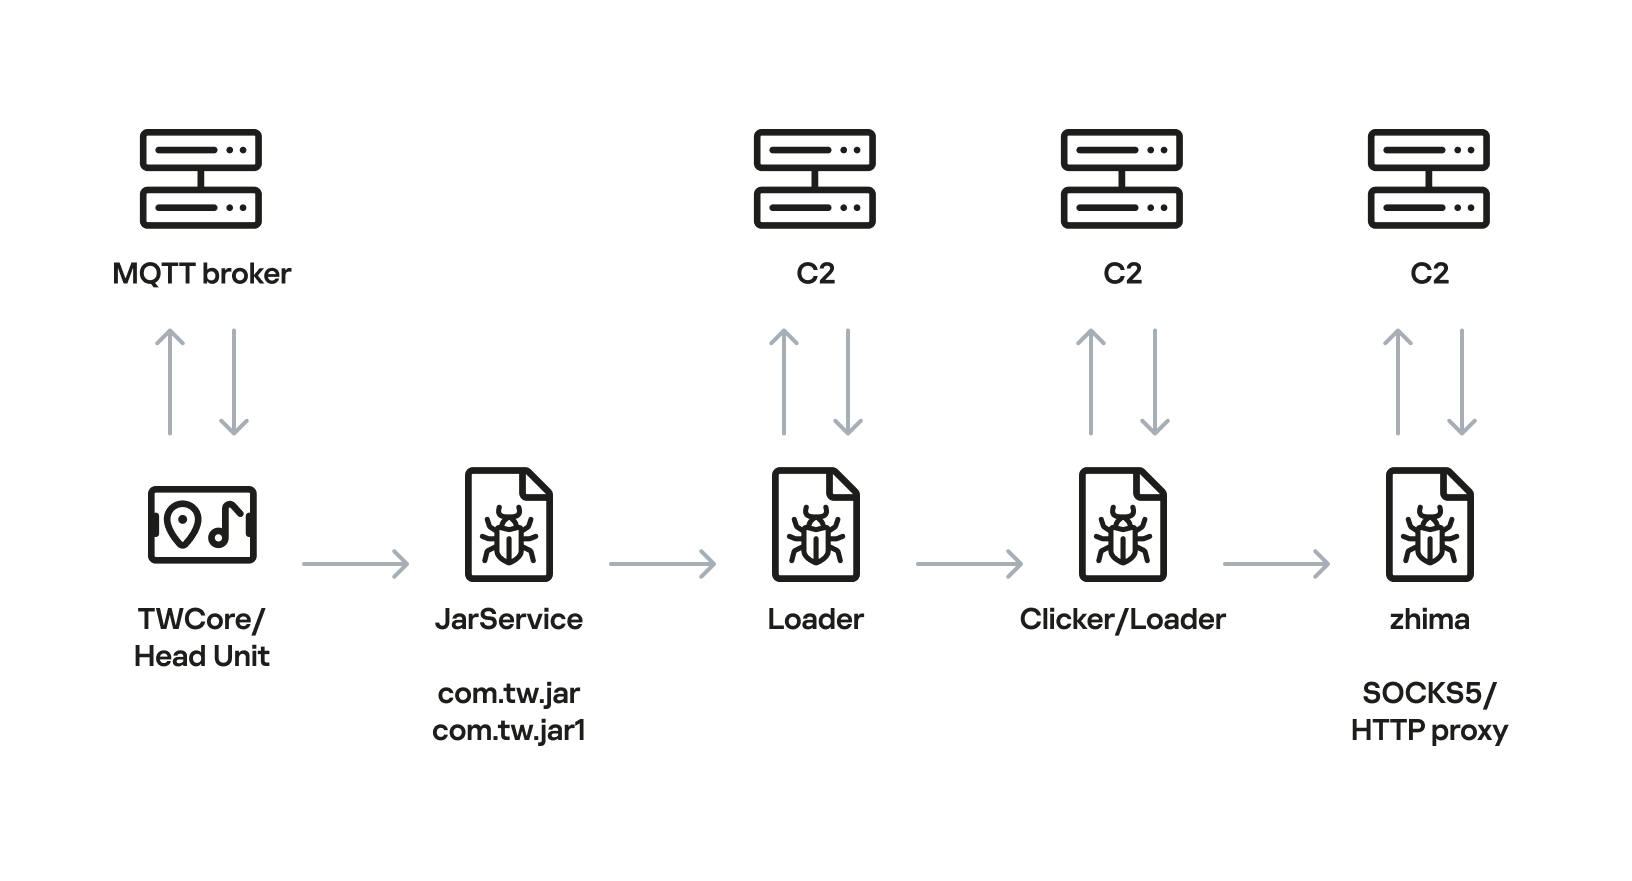
Researchers uncovered a new Android malware campaign targeting Android-based automotive head unit firmware through the legitimate TWCore updater, making this the first documented infection chain of its kind on a car head unit. The multi-stage payload ends in a clicker and the zhima reverse proxy module, and Kaspersky attributes the activity with high confidence to the MoYu Group, an actor linked to BADBOX. #TWCore #JarService #zhima #MoYuGroup #BADBOX #DoFun
Hogan Omidi P.C., a boutique US family law firm serving high-asset clients, was reportedly targeted by the dragonforce ransomware threat actor, disrupting legal operations and case management. The incident impacted #UnitedStates