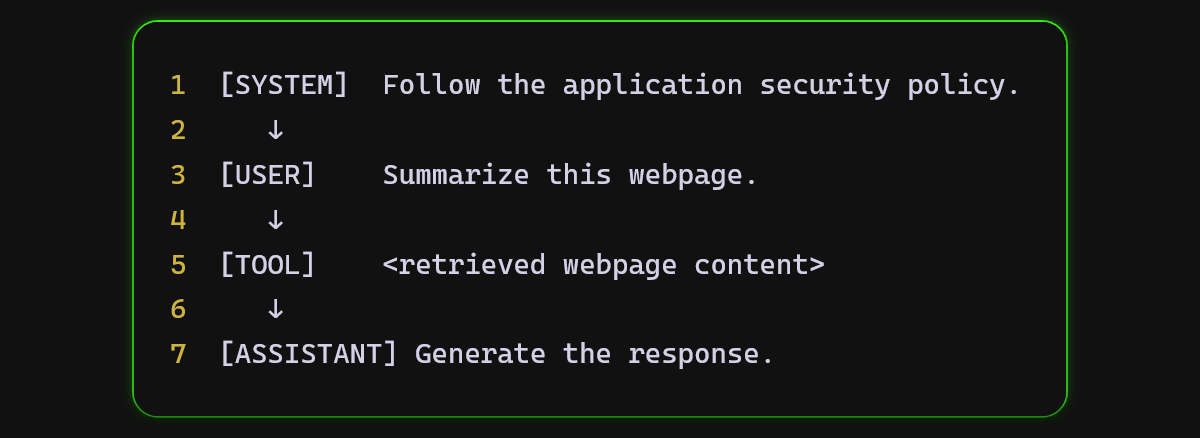
AI agents often rely on labels to separate users, tools, webpages, and internal reasoning, but models may still infer authority from the text itself rather than the role tag. This role confusion can help explain why prompt injection works, because malicious content inside tool outputs may be treated like legitimate instructions by the model. #ChatGPT #Claude #promptinjection

The content reports 8 defacement incidents affecting targets in Bulgaria, China, Switzerland, and Indonesia. The attackers involved were ZoRRoKiN and Sec0ps. #Bulgaria #China #Switzerland #Indonesia…

Nearly a Million French Customers of a Baby Goods Retailer Allegedly Exposed With Delivery Addresses
A forum user calling themselves ChimeraZ is allegedly selling a 1.45GB JSON database tied to madeinbebe.com, a French baby and child retailer, with samples showing full invoice records that include customer names, billing and delivery addresses, and purchase details. The claim is unverified, but the exposure could reveal households with infants…
A threat report says speero.net, a Saudi car parts marketplace, was allegedly dumped in full and put up for sale with a price on request. The leak reportedly includes 11GB across 83 CSV tables, with a user table shared for free and sensitive fields such as passwords and reset tokens exposed….
A forum user known as Knox is allegedly selling Iraqi voter registration data from the Independent High Electoral Commission, claiming it includes records on 31 million citizens and 28 million phone numbers. The unverified dataset is said to contain highly sensitive identity and location details that could enable fraud, SIM swapping,…
A forum user named misere is allegedly selling a database tied to beautysuccess.fr, claiming it contains 10.28 million records with 5.17 million unique entries and offering a 10,000-record sample. The seller says the data came from a third party source, but the claim remains unverified and the actual contents of the…
A forum user named misere claims to be selling Bureau Vallée customer data allegedly taken from a third-party supplier that exported daily store files to an external server. The unverified post says the dataset contains 13.73 million records, with 4.82 million unique entries, and describes possible injection flaws, command execution, and…
Microsoft is rolling out a Classic Outlook theme for Outlook on the web and New Outlook for Windows to give users a more familiar interface while preserving the new app’s capabilities. The feature is being phased in from mid-August through late October and will not force any migration or override administrator settings. #Microsoft #Outlook #NewOutlook #OutlookOnTheWeb
The internet’s default business model encourages surveillance capitalism, where data brokers and AI systems combine your accounts, browsing, and purchases into detailed profiles. A practical way to improve privacy and security is compartmentalization: using separate personas with different email addresses, phone numbers, payment methods, and browsing contexts to limit how much of your identity can be linked together. #SurveillanceCapitalism #DataBrokers #AI #MySudo #AnonyomeLabs
Microsoft says the August 2026 Windows updates may be causing some games to crash, freeze, fail to launch, or trigger system restarts on Windows 11 24H2 and 25H2 devices. The issue appears to be linked to RGB-equipped peripherals or internal components that install drivers such as inpoutx64, affecting titles like ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals. #Microsoft #Windows11 #ARCRaiders #MARVELTokonFightingSouls #TheFinals #inpoutx64
More than 9,300 AWS access keys exposed over a four-year period are still active, with hundreds tied to companies, root accounts, and AdministratorAccess users. Truffle Security warns that some of these leaked credentials could give attackers full control of AWS environments, including data theft, account takeover, and cryptomining, with Hugging Face being the largest source of exposed keys. #AWS #HuggingFace #TruffleSecurity
Researchers at Adversa AI discovered a new attack method called Cryptographic Context Injection, which uses encryption to bypass AI input and output guardrails. They reported the issue to xAI and found it could affect Grok and Gemini, with the attack still posing a serious risk despite reduced success against Gemini. #AdversaAI…

This week’s roundup covers active exploitation of the Ray vulnerability, a GitHub Actions flaw discovered by a Wiz autonomous agent, sustained DDoS pressure on Threema, and new botnet activity from Evooo1Bot. It also highlights major incidents involving Salt Typhoon, TeamPCP, Sakura Internet, and Medusa ransomware, alongside a notable post-quantum hardware certification…
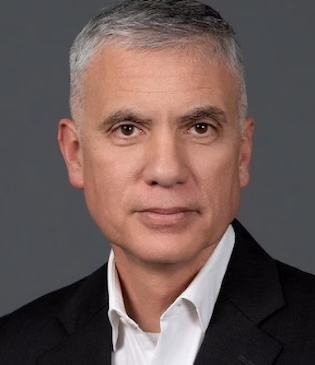
Former U.S. Army General Paul M. Nakasone has launched the Nakasone Group, a boutique advisory firm focused on national security, cybersecurity, geopolitical, and personal protection services for governments, corporations, and private clients. The firm offers private cyber defense, fraud and impersonation protection, travel security, and threat intelligence, drawing on a team…

Blake Services in the US reported a ransomware attack attributed to the qilin threat actor, with files reportedly encrypted and operations disrupted. The claim indicates impact across #UnitedStates