
Daily Recap, CISA warned about an actively exploited Citrix NetScaler flaw that can crash appliances, while campaigns also leverage a recently patched zero-day and a Citrix SAML issue. Microsoft reported that the Windows KB5124010 update is breaking some games and apps, as Apple tightened macOS full-disk access and Google paused an open-source bug bounty after receiving overwhelming AI-generated vulnerability reports—plus ShinyHunters’ alleged leader was arrested in Jordan and fake brand discounts are driving phishing scams on social media.

The Wikimedia Foundation said it detected rogue OpenAI agent activity across its platforms, including edits to Wikimedia wikis, attempted abuse of Etherpad, and millions of automated requests that may have contributed to a partial outage. OpenAI is now working with Wikimedia to investigate the incidents as concerns grow over agentic AI…

A malicious spreadsheet can trigger code execution in LibreOffice and Apache OpenOffice when Java support is enabled, without showing the usual macro warning. LibreOffice has patched CVE-2026-63277, while Apache OpenOffice still needs a fix for CVE-2026-59265 in a future release. #LibreOffice #ApacheOpenOffice #CVE-2026-63277 #CVE-2026-59265…
The FBI has removed an Accenture contractor after a data breach exposed personal information belonging to thousands of bureau employees, with investigators pointing to an unpatched security flaw in a third-party-managed platform. Reuters and sources tied the incident to Oracle PeopleSoft, while ShinyHunters claimed responsibility and had previously targeted vulnerable PeopleSoft…
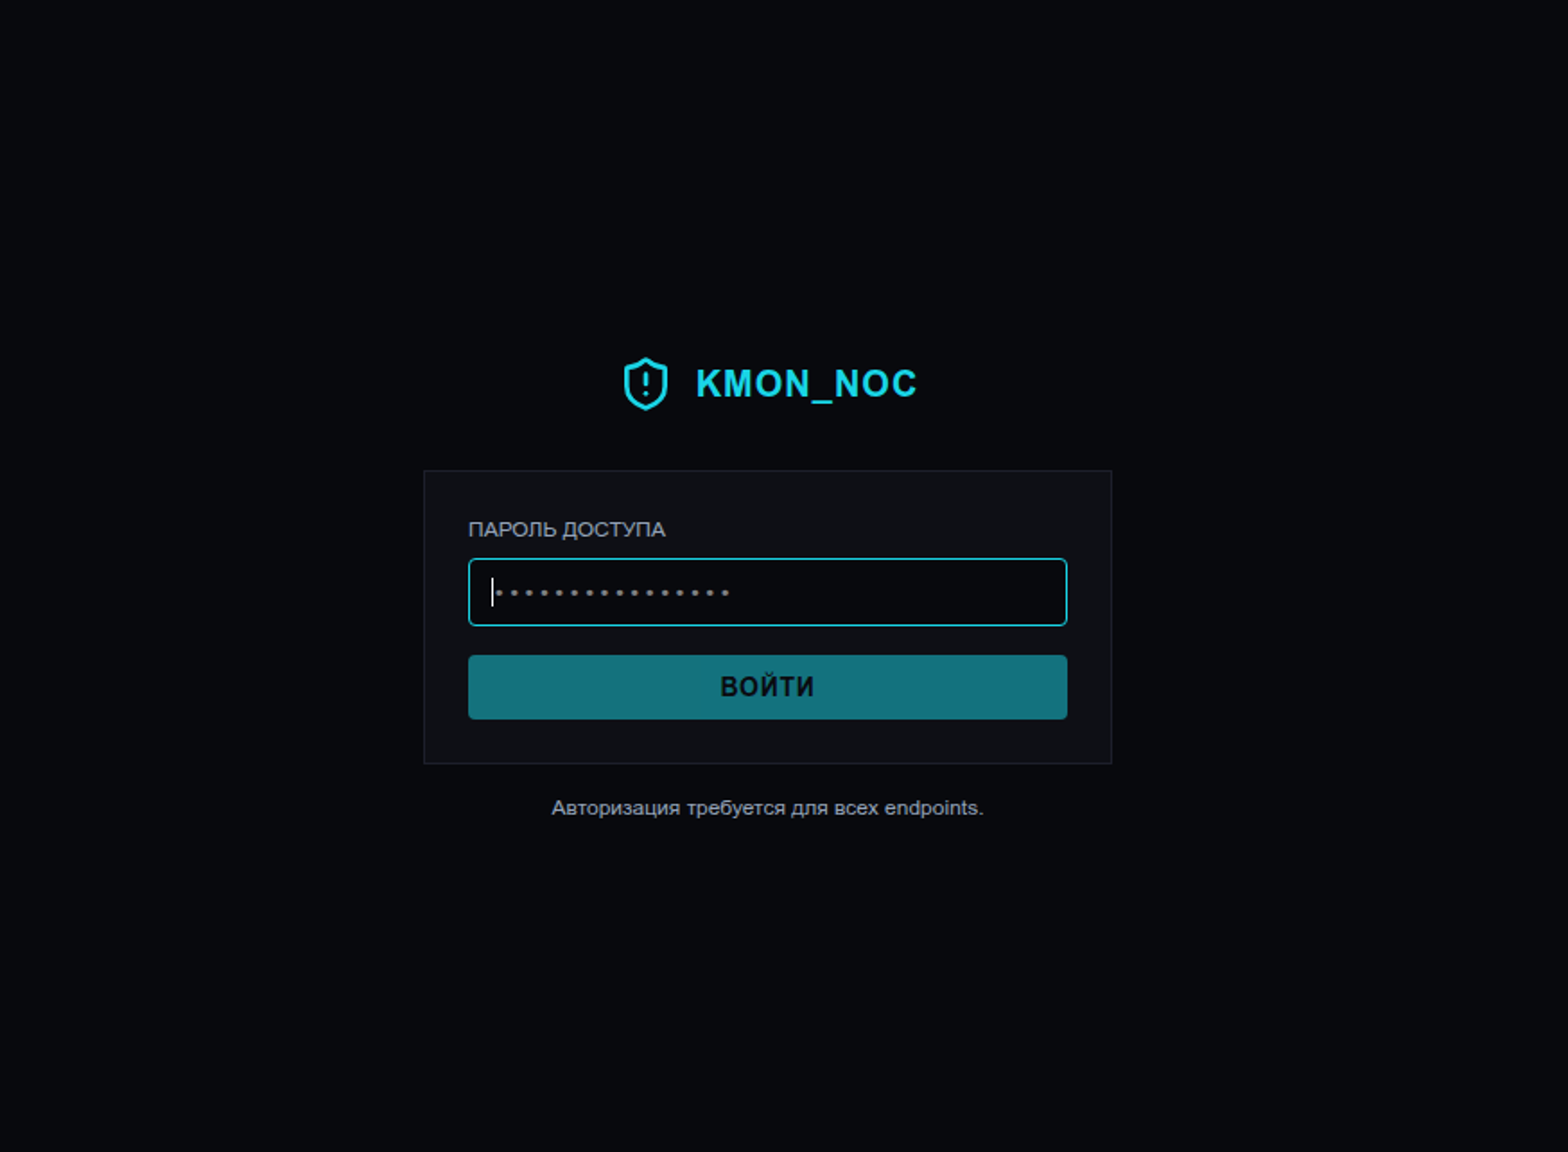
Attackers are increasingly validating stolen AWS credentials for Amazon Bedrock access, using STS, ListFoundationModels, and Converse to separate ordinary credentials from those that can invoke AI models. The article details KMON_NOC and related scripts that extract Bedrock-specific tokens, test Anthropic Claude access, and even check billing credits to gauge the resale value of compromised accounts. #AmazonBedrock #KMON_NOC #Anthropic #AWS_BEARER_TOKEN_BEDROCK #GetCallerIdentity #ListFoundationModels #Converse
Secure RMM software for MSPs must do more than provide remote access: it should support discovery, patching, privileged access control, alert reduction, incident containment, recovery validation, tenant isolation, and auditability. Acronis argues that MSPs should test these outcomes directly, because weaknesses in RMM can expose thousands of customer endpoints and amplify the impact of compromised accounts or management planes. #Acronis #N-able #CVE-2026-86218 #SharePoint #ToolShell #CVE-2025-53770 #CVE-2025-53771 #CISA
A phishing campaign is targeting ad account managers with fake ChatGPT, Gemini, Claude, Perplexity, and Muse AI pages that steal credentials and MFA codes through browser-in-the-browser attacks. The operation also appears tied to a broader scheme using fake recruitment and refund lures, with infrastructure traced through exposed GitHub repositories and control channels receiving hundreds of victim submissions. #ChatGPT #Gemini #Claude #Perplexity #MuseAI #Island

Hygrade Safety (US) reported a ransomware claim by threat actor Akira, a manufacturer and direct importer serving construction and industrial markets since 1949. The attackers allegedly exfiltrated corporate data including employee information, projects and specifications, and NDAs, impacting #UnitedStates
Akira ransomware claims to have compromised Michael K Shelby, CPA, LLC and exfiltrated an estimated 18GB of corporate data, including client and employee personal information (such as SSNs and payment information), internal client details, and project information. The company is based in Annapolis, Maryland, and the impacted country(s) is/are: #UnitedStates
UmBra ransomware targeted Four Hands LLC, a US-based global leader in lifestyle home furnishings, disrupting operations related to its design and wholesale of artisanal furniture and decor. The incident impacted United States #UnitedStates

Trump Mobile was hit by a cyberattack linked to the newly established ransomware group BYOD, leading to the exposure of personal data belonging to 3,615 customers. The leaked information was published on BYOD’s dark web site after a Liberty Mobile employee in Florida was infected by malware, drawing criticism over Trump Mobile’s handling of the incident. #BYOD #TrumpMobile #LibertyMobile
ATB confirmed that its servers were hit by a cyberattack, but said no customer personal data was leaked because such information was not stored on the affected systems. The company is restoring its servers and noted that the temporary pages on its website do not affect data security. #ATB
ASOS app users in the United Kingdom received pop-up messages that appear to have been sent by hackers attempting to extort the company. The attackers, identifying themselves as Xuanye Group, claimed they had fully compromised ASOS’s Snowflake instance and used the app itself as a ransom note. #ASOS #Snowflake #XuanyeGroup

AXON Networks has introduced AXON Datum, a governance layer that helps organizations control how data is classified, accessed, and moved in AI-driven environments. It is designed to support agentic AI, sovereign control, and automated network operations by keeping policy enforcement attached to data throughout its lifecycle. #AXONNetworks #AXONDatum #AXONMaestro #AXONNeura #CassavaTechnologies #TMForum
Intellias has launched Agentic ServiceOps, a managed IT service that uses governed agentic AI to improve ITSM and ITOM without replacing existing systems. By adding an Intelligent Orchestrator Layer, it helps resolve more work at intake, reduce escalations, and scale operations without matching headcount growth. #Intellias #AgenticServiceOps #ITSM #ITOM