In Argentina, Instituto Ferrero de Neurolog,ía y Sueño (IFN) reported a ransomware attack attributed to the threat actor kazu, impacting its operations and access to critical medical and administrative systems. The intrusion disrupted its ability to deliver neurological and sleep disorder services and diagnostics in #Argentina.

PappyJoe, a US-based cloud practice management platform used by clinics, hospitals, and healthcare professionals, was targeted by the kazu ransomware threat actor, impacting operations related to appointments, EMRs, billing, prescriptions, and patient communications. The incident disrupted the organization’s healthcare technology services in #UnitedStates
Storm ransomware reportedly targeted Ruggles Sign Company, a US-based, family-owned signage provider with 75+ years of experience offering design, manufacturing, installation, and maintenance services for major brands like Nike, J. Crew, and Under Armour. The incident impacted United States. #UnitedStates
PCA ***** reports a ransomware incident involving the threat actor majinahanashi, with a public leak publication scheduled for [LEAK] affecting 1844 files. The impacted country(s) information was not provided, so no country could be identified.
Kessler Creative in the United States reported a ransomware incident attributed to the coinbasecartel threat actor. The attack resulted in disruption to systems and access to files, with the impacted country being #UnitedStates.
Longhorn Investments was allegedly hit by ransomware attributed to the coinbasecartel, resulting in unauthorized disruption of their systems and potential encryption of files. The claim identifies the impacted country(s) as #unknown.
ReliaQuest, LLC in the US was targeted in a ransomware claim attributed to shinyhunters, with the post directing attention to its alleged victim and urging Mandiant to report and advise accurately. #UnitedStates

One defacement incident was reported, targeting Bangladesh via the site https://pabnapourashava.gov.bd/systemadminbd.txt. The attacker involved was systemadminbd. #Bangladesh…
OTEIS Conseil & Ingénierie in France reported a ransomware incident attributed to coinbasecartel, impacting its engineering and consulting operations. The company’s services across structural, fluids, electrical engineering, and project management were disrupted in the affected environment, #France
coinbasecartel ransomware activity targeted Flecha Bus, an Argentine intercity bus operator providing long-distance passenger coach services across Argentina, disrupting its operations in the passenger transportation sector. The impacted country is #Argentina
Incransom ransomware, with unauthorized access gained to el-group’s confidential files in Switzerland, stole client data, proprietary R&D, and financial documentation. The impacted country(s): #Switzerland
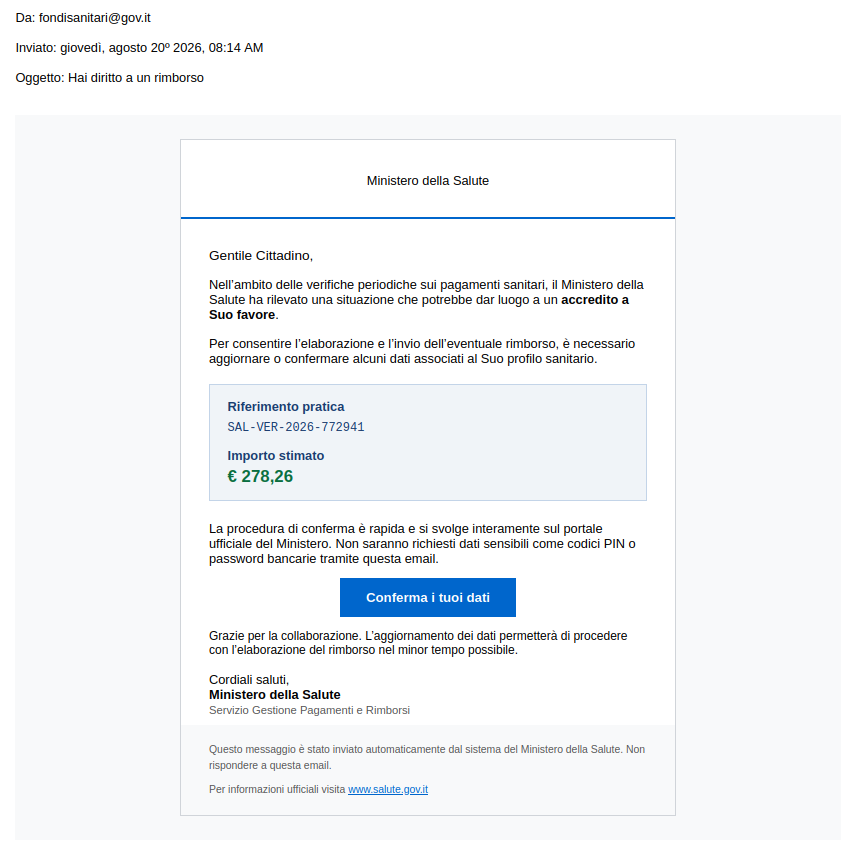
CERT-AGID identified a phishing campaign using the Ministry of Health’s name and branding to trick victims into revealing personal data and payment card details through a fake €278.26 refund notice. The fraudulent emails spoof the sender [email protected] and direct users to malicious pages that collect identity, contact, and card information for further abuse. #CERT-AGID #MinisteroDellaSalute #fondisanitari.gov.it

Daily Recap, North Korean-linked actors and a separate malicious-crate campaign were tied to a Rust supply-chain wave that injected build-time malware into crates with 245 million downloads, including poisoning the arrayref pathway to deliver an infostealer. Elsewhere, Microsoft warned of a max-severity Microsoft Entra ID flaw already exploited in attacks, while attackers abused Google OAuth and WhatsApp account linking and a passkey-enabled phishing toolkit to maintain access. #NorthKoreanHackers #Rust #arrayref #MicrosoftEntraID #GoogleOAuth #WhatsApp #Passkeys #EntraFlaw
Coinbasecartel ransomware targeted Tower Insurance, a New Zealand-based insurer, disrupting its digital-first policy and claims operations. The incident impacted New Zealand. #NewZealand
coinbasecartel ransomware activity claimed to have targeted RXPE Group in China by encrypting or threatening access to files to extort payment. The incident is reported as affecting #China