Microsoft has issued a temporary workaround for Windows 11 gaming problems caused by the August 2026 Patch Tuesday updates, which can crash or freeze games and trigger errors on affected PCs. The issue is tied to RGB device drivers or components such as inpoutx64.sys, impacting titles including ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals. #Microsoft #Windows11 #inpoutx64.sys #ARCRaiders #MARVELTōkonFightingSouls #TheFinals

L Group is claiming to have deployed ransomware against compendiumusa.net in the United States, threatening to disrupt access to the organization’s data and systems. The impacted country(s) is/are: #UnitedStates
Qilin ransomware claimed an attack on Aurore Development S.p.A. in Italy, deploying malware and encrypting files to extort the victim. The incident impacted IT #Italy
The Storm ransomware actor targeted the City of Mitchell in the United States, encrypting data and disrupting services after compromising the organization. The attack impacted the city’s local government operations in #UnitedStates
Storm ransomware reportedly targeted Sharp Motor Group, a privately owned automotive dealership group in Tweed Heads, New South Wales, Australia, providing vehicle sales, servicing, spare parts, finance, insurance, and trade-in services. The company serves customers across the Northern Rivers region and the Gold Coast from its headquarters at 153 Wharf Street, Tweed Heads, NSW 2485, Australia. #Australia
The FTC proposed a policy targeting personalized pricing practices that use consumers’ personal data without clear disclosure, while Washington’s Attorney General urged stronger statewide privacy protections and a new data broker regime. In Europe and Canada, Germany’s BfDI pushed for EU-wide cookie manager rules, the Dutch DPA fined Uber €824.99 million over automated driver deactivations, and Ontario issued updated guidance on police drone surveillance. #FTC #NickBrown #BfDI #Uber #AutoriteitPersoonsgegevens #OntarioIPC

A forum user named misere is allegedly selling Bureau Vallée customer records, claiming 13.73 million total records and 4.82 million unique records taken through a third-party exporter. The post says the data came from daily store exports on an unprotected external server, with claimed injection flaws, persistent access, and a downloadable…
A forum user named DumpSecNew is allegedly selling query results taken from France’s Portail Calypsso, an access portal used by French national police systems. The claimed data includes records from TAJ, FPR, SIV, SNPC, and other files, with the post describing the incident as unverified and pricing the access data at…
A forum user named xpl0itrs claims to be selling 6.1 TB of documents allegedly taken from Gruppo Spaggiari Parma, including identity cards, tax records, school reports, medical files, and vaccination records. Spaggiari says the incident was limited to a forms component and denies that its register and school management systems were…

Cybersecurity Threat Research ‘Weekly’ Recap. This week covered government/health phishing schemes for refund and reimbursement theft, plus Microsoft 365 session hijacking via AiTM tooling and broader crypto fraud using fake AML checkers, wallet apps, and stealer pipelines. Across malware delivery, supply chain, and cloud/identity abuse, researchers tracked campaigns involving ToxicPanda 2.0, ClearFake-to-Amatera chains, StopAndProtect WordPress intrusions, and covert infrastructure using BOFScale and Cloudflare Workers, alongside defensive guidance and emerging AI security benchmarking (EchoBench, AVDH).
#Mirage2FA #OperationASTERIX #ToxicPanda #ClearFake #Amatera #StopAndProtect #BRIDGEHEAD #BOFScale #CloudflareWorkers #EchoBench #BTRsys #Cruciferra
Studio BOLDRIN PAOLO in Italy reported a ransomware incident attributed to the qilin threat actor. The attackers encrypted critical files and disrupted operations, impacting #Italy
Tecnici Associati STP in Italy was targeted by the Qilin ransomware group, resulting in the encryption of files and disruption of operations. The incident impacted Italy #Italy
Resi.com, a UK-based online architectural and home renovation platform, reportedly suffered a ransomware attack in Germany attributed to the threat actor krybit, compromising access to its systems. #Germany
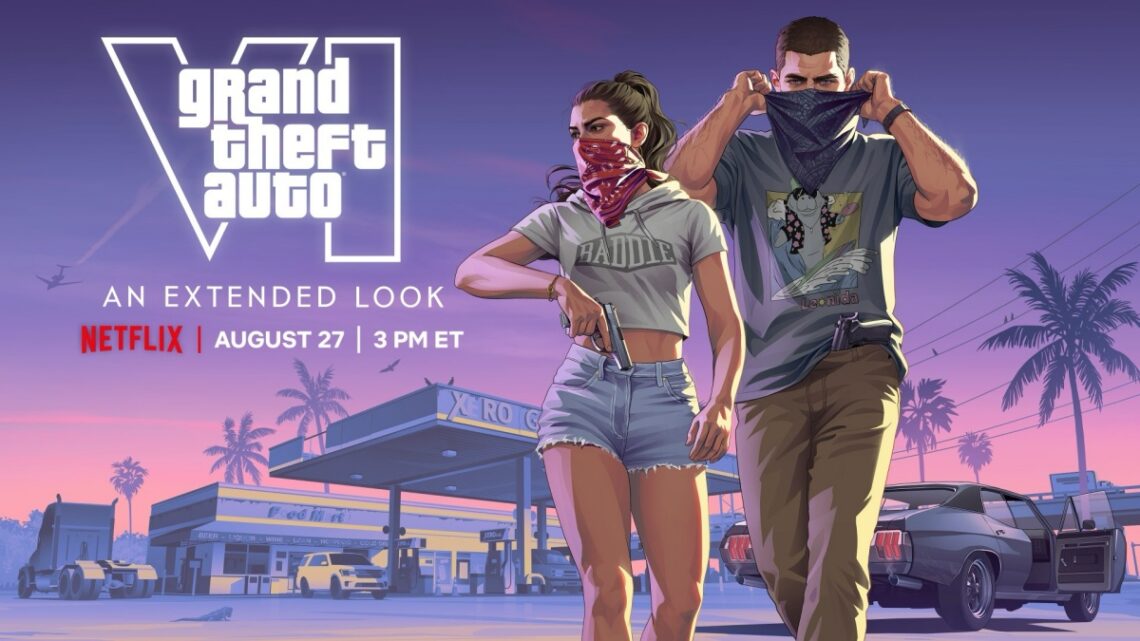
Take-Two Interactive has issued DMCA subpoenas to Microsoft and Discord to identify the source behind leaked Grand Theft Auto VI footage, focusing on the alias “Cyberleek” and related accounts and servers. The company says the leak disrupted Rockstar’s marketing plans ahead of the game’s November release and is seeking detailed user…

There was 1 defacement incident targeting France, with the attacker identified as CoupDeGrace. The defacement details list only one country targeted, France, and one attacker involved, CoupDeGrace. #France…