SecurityWeek and MTSI will host the Cyber Attack Methods course at the 25th Anniversary ICS Cybersecurity Conference in Nashville from October 6–8, giving participants hands-on experience in how attackers compromise cyber-physical systems. The training is designed for engineers, developers, testers, and security professionals to better understand attack paths, reduce risk, and…
WhatsApp has introduced new security features for passkeys, two-step verification, and caller context to help users better protect their accounts and identify suspicious calls. More than 1 billion people now use passkeys on WhatsApp, and Android users will soon see additional details about unknown callers before answering. #WhatsApp #Meta…
Law enforcement agencies from 22 countries identified 263 suspects and arrested 58 people tied to cybercrime networks run by African crime groups during Operation Jackal IV. The operation targeted the Black Axe syndicate and related fraud rings involved in romance scams, crypto investment scams, business email compromise, and money laundering. #BlackAxe #OperationJackalIV #INTERPOL
Threat actors have compromised more than 270 Zimbra Collaboration Suite instances by exploiting CVE-2026-73570, a high-severity remote code execution flaw in the SNMP monitoring component. Synacor patched the issue in ZCS 10.1.20, while CERT Polska, CISA, and Shadowserver warned of active exploitation and widespread unpatched systems. #Zimbra #CVE-2026-73570 #Synacor #CERTPolska #CISA #Shadowserver

This ATIS report explains how zero trust architecture can secure 5G cloud and operational environments as networks shift from operator-owned infrastructure to complex multi-vendor and hyperscale cloud deployments. It emphasizes continuous monitoring, micro-segmentation, IAM, SIEM/SOAR, eBPF, AI/ML, and shared standards work across 3GPP, ETSI, O-RAN, CISA, NIST, MITRE FiGHT, and GSMA MoTIF to address threats such as Salt Typhoon and cloud-native attack paths. #SaltTyphoon #3GPP #O-RAN #MITREFiGHT #GSMAMoTIF

Dark Project ransomware reportedly impacted a dentist in New Britain, Connecticut, US, compromising the entire customer database of just over 8,000 files along with a small number of records containing Social Security numbers. The impacted country is #UnitedStates.
PCA Group Sdn. Bhd., Malaysia, was targeted in a ransomware leak attributed to the majinahanashi threat actor, with 1,844 files reportedly exposed as part of the scheduled publication. The impacted country(s) is Malaysia #Malaysia
Pump Engineering Company, based in the US, was targeted by Dark Project in a ransomware attack involving theft of 120,000 files totaling 115 GB, including customer and insurance records, confidential financial documents, and extensive project drawings. The incident impacted the United States #UnitedStates
Australia’s Annual Cyber Threat Report 2024–25 shows a sharper threat environment, with more hotline calls, more incidents, rising financial losses, and a growing focus on state-sponsored activity against critical infrastructure, telecommunications, and logistics. The report also highlights escalating ransomware, credential theft, phishing, DDoS, and edge-device exploitation, while urging stronger resilience measures such as MFA, logging, legacy IT replacement, and preparation for post-quantum cryptography. #APT28 #FancyBear #ForestBlizzard #BlueDelta #GRU #BADBAZAAR #MOONSHINE #REDSPICE #ASDsACSC #CIFortify #ReportCyber
Research on Browser-in-the-Browser recruitment scams shows threat actors impersonating real HR staff from major companies to run highly convincing interview-themed phishing campaigns. The attacks adapt to mobile by swapping the fake browser popup for a full-screen login page, while infrastructure and lookalike domains tied to brands like Amazon, Apple, and FIFA remain active for long periods. #BrowserintheBrowser #Amazon #Apple #FIFA #Zimperium
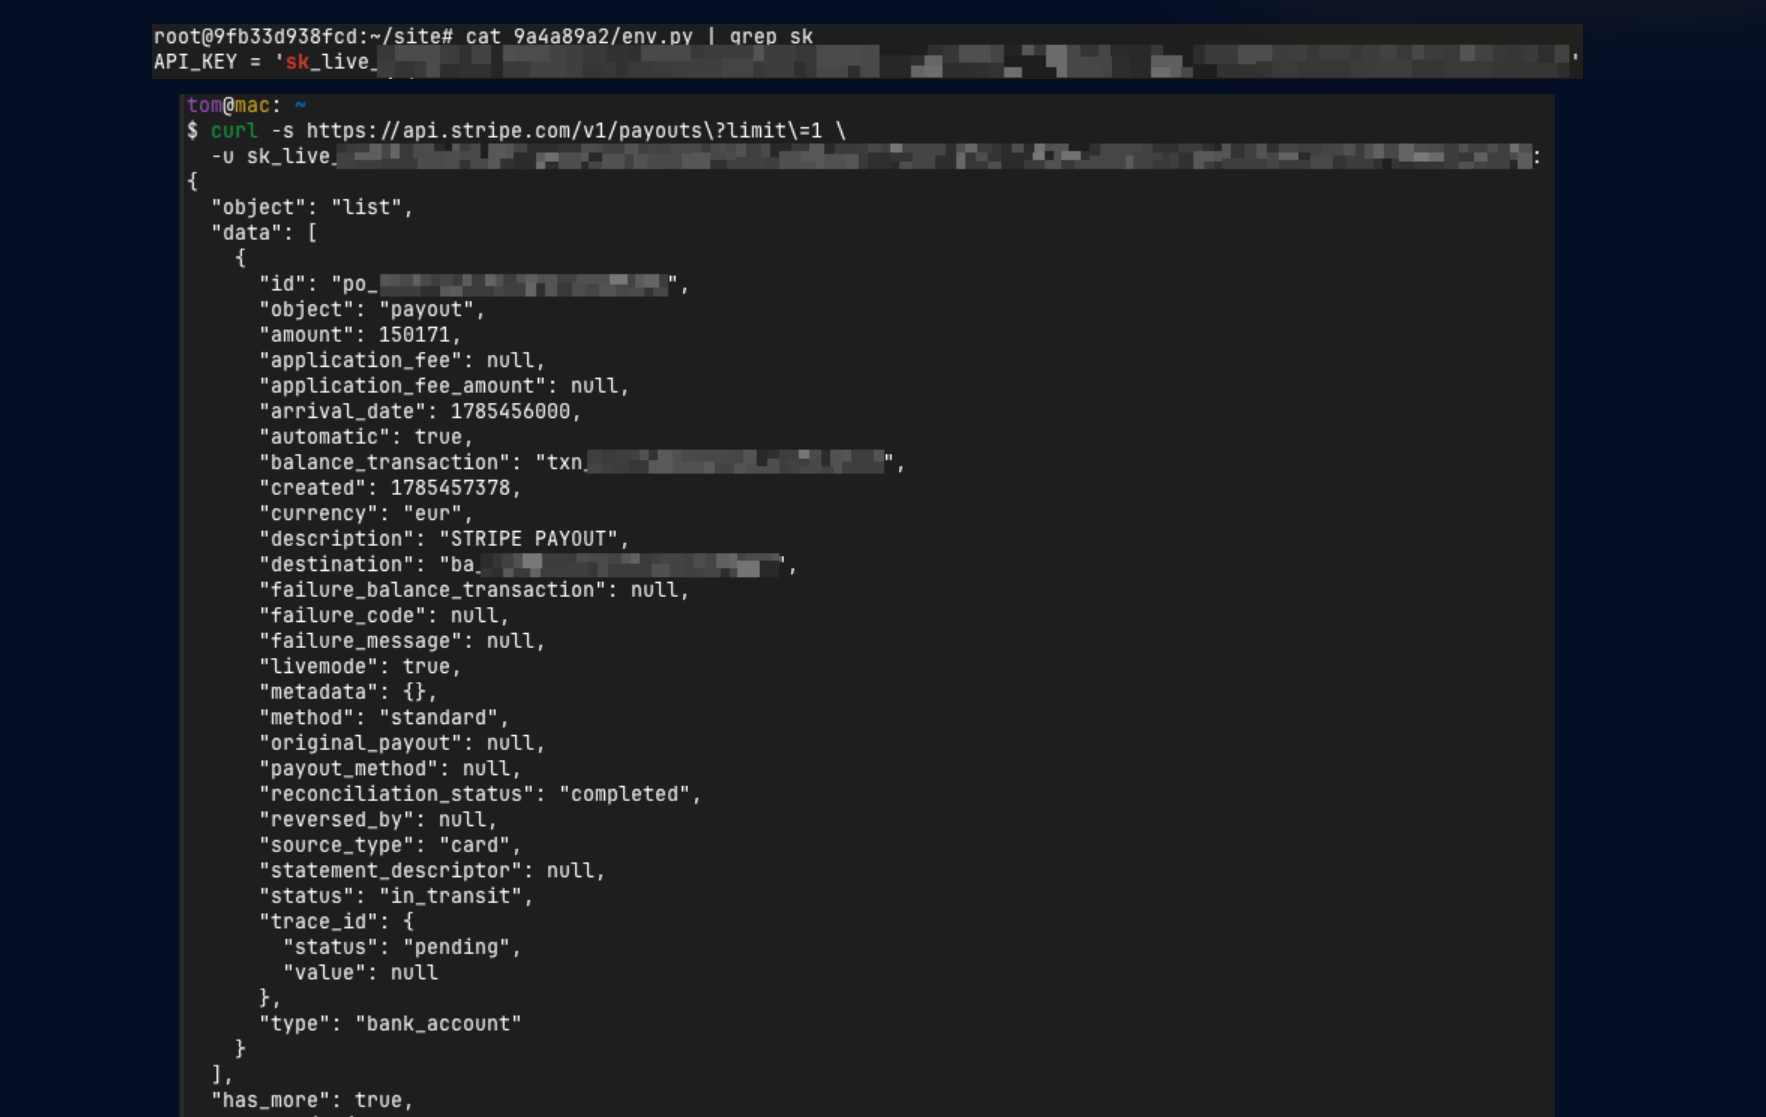
Researchers found over 28,000 publicly exposed Git repositories across 3.5 million active web servers, revealing live AWS keys, Stripe secrets, GitHub tokens, and sensitive internal records. The exposure was caused by misconfigured public .git directories, putting organizations at risk of cloud takeover, financial data theft, and access to internal systems. #IntruderResearch…
CISA has ordered government organizations to urgently patch CVE-2026-21962, a critical unauthenticated remote code execution flaw affecting Oracle HTTP Server and the WebLogic Server Proxy plugin. The vulnerability has been actively exploited since January in attacks against Oracle WebLogic servers, with reporting tied to CloudSEK, FalconFeeds, SOCRadar, and a China-linked threat…

Taiwanese prosecutors charged nine people, including employees connected to Nvidia and Super Micro, over the illegal export of high-end AI servers to mainland China. The case highlights escalating U.S.-China competition over AI infrastructure and export controls on banned B300 GPUs and Nvidia H20 chips. #Nvidia #SuperMicro #B300 #H20…
Silent patches do not truly hide vulnerabilities because attackers can still diff binaries and uncover what changed, while defenders are left without the context they need to prioritize response. The article argues that Broadcom’s private Spring Enterprise Repository may give paying customers early exploit intelligence for Spring Framework issues, creating a…
The CIS CTI team identified KrustyLoader staged in AWS S3 buckets and used by threat actors to deliver an encrypted Sliver payload that injects into Windows Explorer and deletes itself from disk. Investigation linked the activity to multiple compromised or attacker-created cloud storage buckets, with open-source reporting connecting the campaign to…