
A July 2026 cyber incident disrupted a small UK gas-fired electricity generator for several days, prompting a government and NCSC response while posing no wider grid threat or customer outage. Public reporting linked the event to Iran, but no technical evidence has confirmed attribution, and the exact intrusion path, affected systems, and responsible actor remain unknown. #NCSC #Iran #UK #ElectricityGenerator

AuditTeam ransomware activity targeting ma***up in RU led to unauthorized disruption and data compromise, consistent with extortion and encryption-style attacks. The incident resulted in operational and security impacts for organizations in #Russia
Brazosport College in the US was impacted by the Qilin ransomware group, which deployed malicious encryption to disrupt access to files and systems. The attack resulted in operational disruption and data compromise attempts, with the impacted country being #UnitedStates.

There were 2 defacement incidents targeting Thailand, with both incidents linked to the attacker EbRaHiM-VaKeR. The affected targets were https://amssplus.mhs2.go.th/V.html and https://bigdata2.mhs2.go.th/V.html, and the attackers involved was EbRaHiM-VaKeR. #Thailand…
The Orova ransomware group targeted Bai-chi CPA Firm, a registered Taiwanese CPA practice, in Taiwan. The attack impacted data and operations of the Taiwanese organization in the wake of the ransomware incident. #Taiwan
Arich Enterprise Co., Ltd. in Taiwan reported a ransomware incident attributed to Orova, impacting its pharmaceutical marketing service operations and customer network. The affected environment spans medical centers, regional and area hospitals, clinics, chain and standalone pharmacies, and hypermarket channels. #Taiwan
Central Florida Civil LLC (US) reportedly suffered a ransomware attack claimed by the Orova threat actor, with attackers targeting Central Florida Civil, a Belleview, Florida-based underground utilities and site development company. The impacted country(s): #UnitedStates
AnonyMousKIT is a phishing-as-a-service platform that automates stealing Apple device unlock codes, bypassing Activation Lock, and harvesting Apple IDs, iCloud backups, and Keychain credentials. SOCRadar linked the operation to 506 domains and 168 reseller storefronts, with campaigns focused heavily on Brazil and reaching victims in multiple countries. #AnonyMousKIT #SOCRadar #Apple #ActivationLock
Threat actors are abusing npm packages and mirrors like UNPKG and npmmirror to host malicious HTML pages that impersonate Cloudflare CAPTCHAs and redirect users to attacker-controlled destinations. The campaign uses legitimate infrastructure as free hosting for phishing pages, with some redirects pointing to Microsoft login themes, ChatGPT, or dynamically controlled URLs. #Cloudflare #npm #UNPKG #npmmirror #Turnstile
LACMA disclosed a breach that exposed customer and employee information after suspicious activity was detected on its systems in July 2025. The museum later determined that attackers may have accessed highly sensitive data, including Social Security numbers, government IDs, financial details, and health information. #LACMA
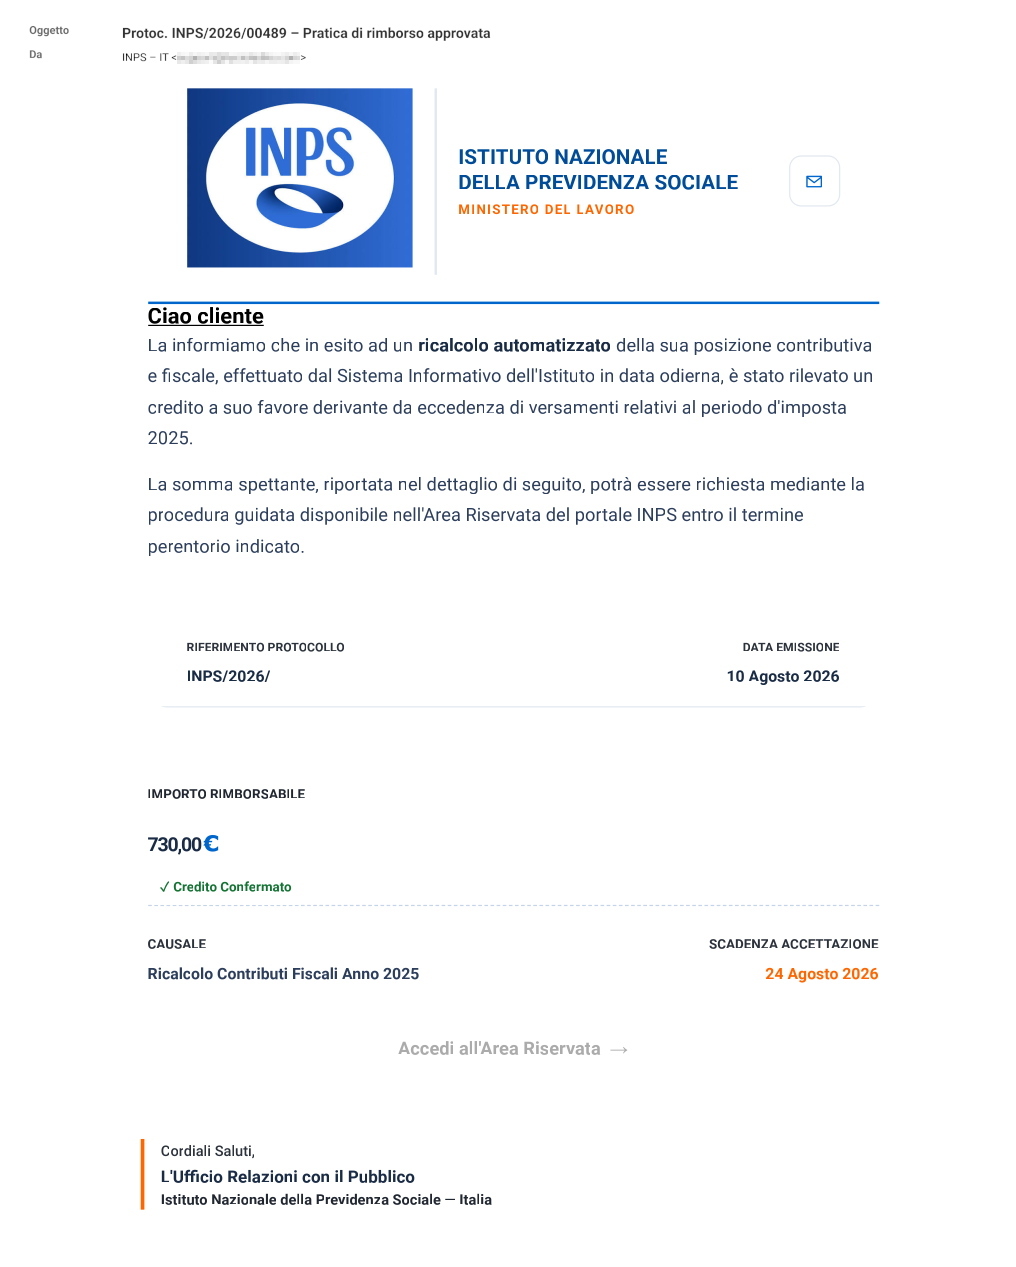
CERT-AGID identified a phishing campaign using INPS branding to steal personal data, payment card details, and push victims into approving unauthorized banking transactions. The attack lures users with a supposed €730 refund tied to a “tax and contribution recalculation” and directs them to a fake site on feedsafepro[.]com that imitates the INPS portal. #INPS #CERT-AGID #feedsafepro

Colorado police arrested Joshua Culver, also known as “Maverick Young,” for allegedly impersonating Supreme Court Chief Justice John Roberts and an NSA TAO leader. The indictment says he used forged court documents and false federal authority to try to influence cases in Indiana, including demands to dismiss charges and quash warrants. #JohnRoberts #NSA #TailoredAccessOperations #JoshuaCulver
Grand Theft Auto VI faced a major leak after the persona CyberLeek released gameplay footage early, triggering a high-profile investigation that may involve insider access or stolen proprietary data. Take-Two Interactive and Rockstar Games responded with DMCA subpoenas and copyright notices while the leaks continued to spread, turning the incident into both a legal fight and an unwanted marketing campaign. #GrandTheftAutoVI #CyberLeek #RockstarGames #TakeTwoInteractive #Discord #Google #Microsoft #X

A forum user named sh444d0w claims to have shared Agence Vauban database data for free, including 5,430 user accounts and detailed property-related records. The post is unverified, but it appears structurally convincing and could expose sensitive client, financial, and property information. #AgenceVauban #sh444d0w…
A forum user calling themselves GordonFreeman claims to have breached the Junta Central Electoral and advertised 7,141,313 Dominican citizen records with 5,758,124 identity card photographs. The alleged dump includes cédula numbers, personal details, and JPEG portraits, but the claim remains unverified and no price was stated. #JuntaCentralElectoral #GordonFreeman #DominicanRepublic…