Manchester Airports Group (MAG) said hackers breached its systems and stole customer data tied to Wi‑Fi sign-ups, car park, lounge, and Fast Track bookings across Manchester, Stansted, and East Midlands airports. The company said airport operations were unaffected, temporarily suspended its “Manage My Booking” service, and is warning customers to watch for suspicious messages. #ManchesterAirportsGroup #MAG #ManchesterAirport #StanstedAirport #EastMidlandsAirport

PaperCut is warning that hackers are actively exploiting a vulnerability in all versions of PaperCut NG and PaperCut MF in zero-day attacks, with confirmed incidents affecting customers. The company has released emergency patches and is urging organizations to restrict Internet-exposed PaperCut Application Servers to trusted IP addresses. #PaperCutNG #PaperCutMF
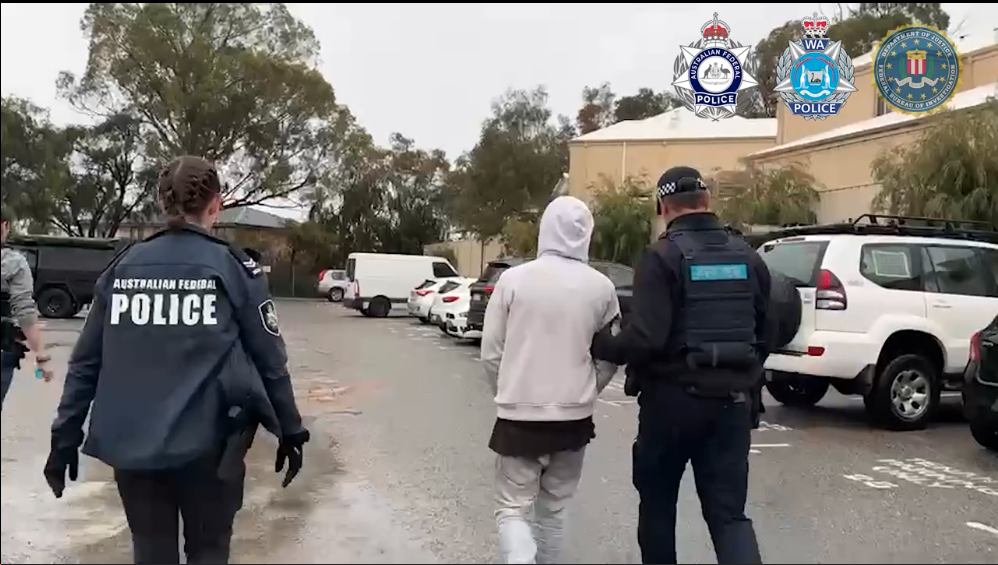
Two men from Western Australia were arrested and charged for their alleged roles in TeamPCP, a cybercrime group tied to malicious code inserted into widely used open-source software and attacks that affected more than 1,000 organizations worldwide. Investigators say the campaign involved Trivy, mini Shai-Hulud, and stolen credentials, while law enforcement and researchers continue to trace the group’s infrastructure and online identities. #TeamPCP #Trivy #miniShaiHulud #AquaSecurity #GitHub #EuropeanCommission

Manchester Airports Group said an unauthorized third party accessed customer data tied to car park, lounge, Fast Track bookings, and in-airport Wi‑Fi sign-ups at Manchester, Stansted, and East Midlands airports. MAG contained the incident, notified authorities, and confirmed that no bank or payment details were exposed and airport operations were not affected. #ManchesterAirportsGroup #ManchesterAirport #StanstedAirport #EastMidlandsAirport
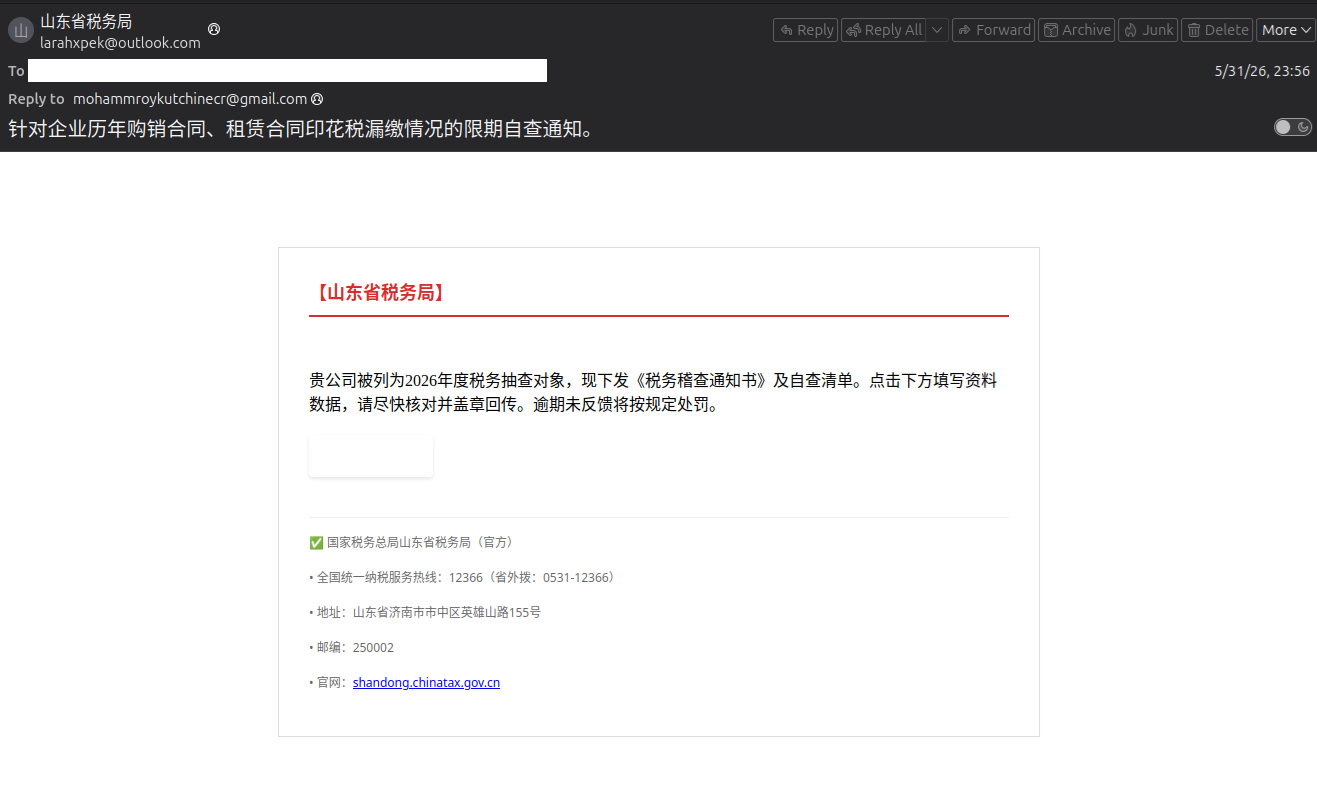
Proofpoint identified PackClient, a modular C2 framework and RAT sold on Telegram that is being used by TA4922 in tax-themed campaigns targeting organizations in mainland China and India. The malware supports data theft, surveillance, payload delivery, and multiple plugins, and its infrastructure and infection chain include distinct registry paths, process trees,…

In an incransom ransomware attack targeting the Rohloff Group franchise partner in ZA, KFC became associated with the incident and threatened data exposure. The 536 GB leak comprised 103,196 files across 30,805 folders, including employees’ personal and banking details, IDs, loan applications, debt acknowledgement, disciplinary hearing results, and financial documentation related to royalties and food cost reconciliation, placing confidential data at risk, with full publication forthcoming. #SouthAfrica
Google Workspace is a critical business platform, but breaches can spread quickly when attackers gain access through social engineering or forgotten third-party integrations. A September 23, 2026 webinar by BleepingComputer and Material Security will examine real Google Workspace breaches and the practical controls that matter most for fast-growing companies. #GoogleWorkspace #MaterialSecurity #BleepingComputer #RajanKapoor #RickFitzgerald
Microsoft has started rolling out a permanent fix for Windows 11 crashes and game launch failures linked to the inpoutx64.sys driver. The issue affected titles like ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals, and Microsoft is also offering a registry-based workaround for enterprise-managed devices. #Microsoft #Windows11 #inpoutx64sys #ARCRaiders #MARVELTōkonFightingSouls #TheFinals
Australian authorities have arrested and charged two men accused of being linked to TeamPCP, a hacking collective tied to major supply-chain attacks against open-source software and developer platforms. The campaign allegedly affected organizations worldwide, including Trivy, LiteLLM, Telnyx, SAP, TanStack, the European Commission, Mistral AI, OpenAI, and GitHub, with huge financial and data-theft impact. #TeamPCP #Trivy #LiteLLM #Telnyx #SAP #TanStack #EuropeanCommission #MistralAI #OpenAI #GitHub
Google is adding new network security protections in Android 17 to improve connection privacy, including support for Encrypted Client Hello (ECH), stronger local network controls, and default Certificate Transparency. The update also helps reduce exposure to 2G-based attacks and makes it harder for ISPs and Wi-Fi operators to profile users’ browsing activity. #Android17 #EncryptedClientHello #ECH #CertificateTransparency #Jigsaw
Managed Detection and Response (MDR) gives organizations proactive threat monitoring, expert analysis, and faster response without the cost of building a full in-house SOC. ESET Threat Research and MDR combine global threat intelligence, customer telemetry, and direct analyst relationships to detect actors like FamousSparrow, infostealers, ransomware, and supply chain activity more effectively. #ESET #MDR #ThreatResearch #FamousSparrow #JaguarLandRover #MarksandSpencer
The Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) is responding to a cybersecurity incident affecting a standalone system. ATF immediately disconnected the impacted environment and began incident response and forensic investigation, with no indication that its network or other systems were affected. #ATF
Merrimack County in New Hampshire experienced a network security incident that temporarily blocked access to the state’s criminal information systems used by county dispatch operators. While other county systems remained offline, 911 call handling and police response were not disrupted, and no data breach has been confirmed. #MerrimackCounty #NewHampshire
Manchester Airports Group (MAG), which operates Manchester, Stansted, and East Midlands airports, suffered a cyberattack that exposed customer data linked to parking, lounges, Fast Track bookings, and Wi-Fi registrations. The compromised information includes email addresses, phone numbers, vehicle registration numbers, and postcodes, while bank and payment details were not exposed. #ManchesterAirportsGroup #MAG #ManchesterAirport #StanstedAirport #EastMidlandsAirport

There was 1 defacement incident targeting Mali, involving the attacker TeaM_CC. The affected site was https://apimali.gov.ml/ghost.html, and the summary includes the country hashtag #Mali….