
Daily Recap, Browser and privacy updates highlighted Brave adding email aliases to reduce tracking and Android 17 rolling out OS-wide ECH to better conceal browsing activity from network providers. In other headlines, Hasbro and McKesson disclosed separate data breaches, Berlin refused a ransomware demand, and PaperCut released additional emergency patches after printer-management exploitation reports involving chained flaws. #Brave #EmailAliases #Android17 #OSWideECH #Hasbro #McKesson #ShinyHunters #Berlin #Qilin #PaperCut #CosmosEVM #CosmosLabs #GiveWP #Log4j #Minimus #ATF #WhiteHouse
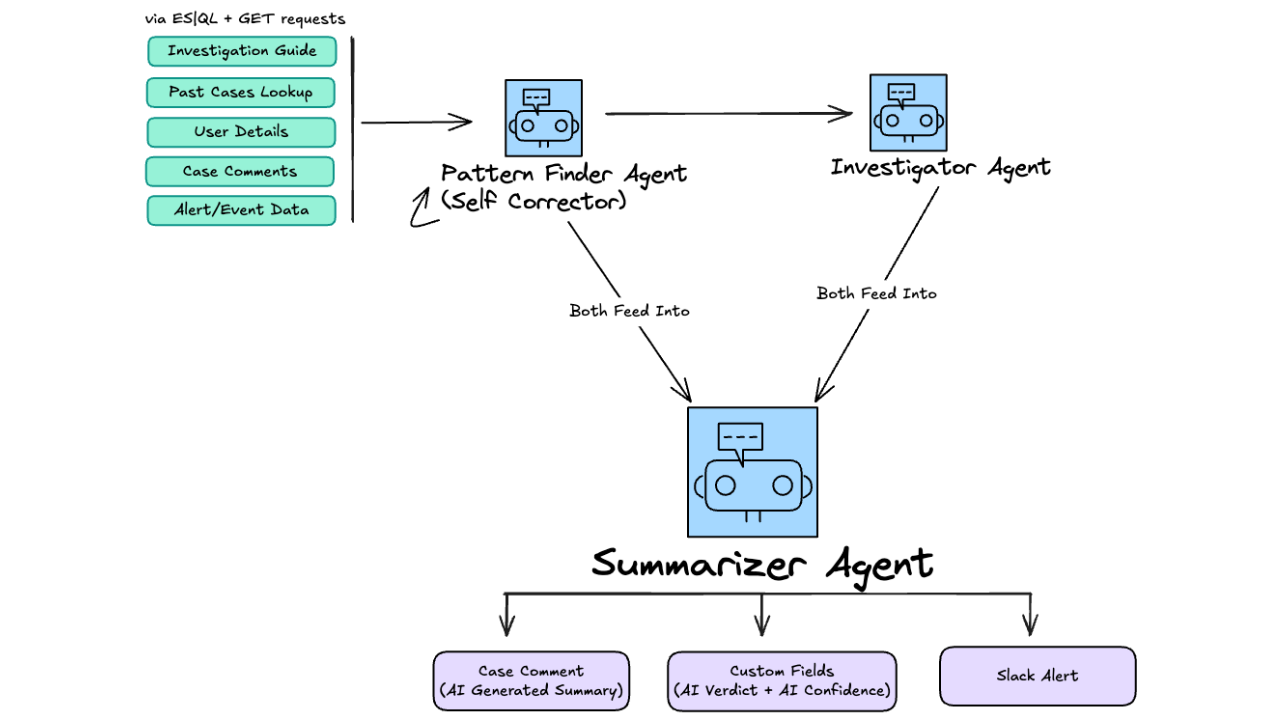
Elastic improved AI verdict correctness in its SOC from 60% to 92% by enriching agent context with investigation guides, Workday user risk data, and 30 days of past case outcomes for the same detection rule. The post explains how the Agent Brainstorm workflow in Elastic Workflows and Agent Builder uses Pattern Finder, L1 Investigation, and Summarizer agents to generate faster, more trustworthy triage results. #Elastic #AgentBuilder #Workday #Kibana #ESQL

LAPoco Architects in the US reported a ransomware incident attributed to the qilin threat actor, resulting in disruption of their systems. The attack impacted operations in #UnitedStates
Neogen Corporation in the US received a final ransomware warning from the threat actor shinyhunters, demanding contact by 1 Sep 2026 or facing data leakage and accompanying operational disruptions. The ultimatum was issued as of 30 Aug 2026 and ends with the impacted country: #UnitedStates

Multiple critical flaws in WordPress plugins and themes including WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP can enable authentication bypass, administrator account takeover, arbitrary file write, and remote code execution. Patchstack and Wordfence say the GiveWP issue chains unsafe unserialization with attacker-controlled data and a gadget chain to achieve command…
Bandit Industries in the US reported a ransomware incident attributed to the qilin threat actor, resulting in disruption of systems and potential data compromise. The attack affected operations across #UnitedStates
Brave browser 1.94 adds Email Aliases, letting users create disposable addresses that hide their real email while still forwarding messages to their inbox. The feature is designed to reduce spam, limit cross-site identity matching, and lower the risk of phishing after service breaches. #Brave #EmailAliases #OPAQUE
CareClinics in Malaysia was targeted by the qilin ransomware group, resulting in encrypted files and business disruption. The attack impacted all affected systems in #Malaysia
Neumaticos Corral S.A. in AR reported a ransomware incident attributed to the qilin threat actor, resulting in disruption and encrypted data. The impact was limited to Argentina #Argentina
The ransomware threat against Uniguacu, attributed to the emperador group, alleges full network commitment with privileged access to critical infrastructure to obtain the database containing confidential and financial information. The attacker claims to have compromised images targeting the financial sector and issues a 13-day deadline to trade, ending with #Uniguacu.
BLISS 1041, located in MT, was reportedly targeted by the qilin ransomware threat actor. The attack encrypted data and disrupted operations in #malta
La Maison Des Travaux in France reported a ransomware attack involving the Qilin threat actor. The attackers encrypted data and demanded a ransom, impacting operations in France #France
The Frame Group in Australia reported a ransomware attack attributed to the qilin threat actor, resulting in service disruption and potential data exposure. The impacted country is: #Australia
Hasbro is notifying employees and former employees that their personal information may have been exposed in a security incident involving its network earlier this year. The compromised data may include names, contact details, national ID numbers, and financial information, and Hasbro is offering identity protection services while its investigation continues. #Hasbro…
MONTCAU, impacted by the majinahanashi ransomware group, reported a leak involving 6341 files under a publication scheduled release. The exposed data is associated with the impacted country(s): #countryname