Ransomware claim: Fu Sheng Industrial Co., Ltd in HK was targeted by threat actor Orova after the company established itself in Taiwan and specialized in overhauling air compressors from Europe, the United States of America, and Japan. The incident impacted HK #HongKong

Orova ransomware targeted ASYS Corporation in Taiwan, disrupting its instrument agency services for semiconductor technology factories and related facility system integration engineering, along with its proprietary yield improvement equipment and industrial IoT sensors. #Taiwan
R L Fine Chem Pvt. Ltd. (Bangalore, Karnataka, India) in the pharmaceutical manufacturing sector, reported a ransomware incident attributed to the Global Secret Group after attackers encrypted 18.6 GB across 14,155 files and 2,840 folders on rlfinechem.com. The impact was felt across India, with operations disrupted and recovery efforts ongoing in #India
Spring Ring was a coordinated social engineering operation that used external Microsoft Teams accounts to impersonate IT help desk staff and lure more than 150 employees across at least 10 companies into vishing calls. The campaign led to attempts to deploy RMM tools, an obfuscated PowerShell RAT from san-sid[.]com, and in…
Microsoft has confirmed that the Windows 11 KB5120998 August 2026 preview update can revert mouse cursor personalization settings, with some users seeing larger white cursors or reset animations after installation. The company is investigating the issue and is asking affected users to report it through the Feedback Hub. #Microsoft #Windows11 #KB5120998
Berlin’s city administration says cybercriminals are trying to extort the city after Rhysida added it to its data leak site, claiming to have stolen 5.79 TB of files. Officials say Berlin will not pay, while investigators continue to assess the breach and protect sensitive government systems. #Rhysida #Berlin
Organizations still rely on on-premises file servers for cost control, sovereignty, and compatibility, but secure access governance is critical to protect data across hybrid environments. The article outlines five file server best practices, including using groups instead of direct user permissions, following the AGDLP model, relying on NTFS for granular control, preserving inheritance, and enforcing least privilege. #AGDLP #NTFS #tenfold
Sygnia found that Fire Ant shifted from VMware hypervisors to Cisco routers, TACACS servers, and Linux management hosts, using a hidden GRE tunnel and custom malware to maintain persistence and spy on traffic. The group also deployed a disguised backdoor called BridgeAgent, abused trusted infrastructure to reach high-value networks, and overlaps with the Chinese espionage group UNC3886. #FireAnt #BridgeAgent #UNC3886 #CiscoIOSXR
PaperCut says a threat actor is exploiting two zero-day vulnerabilities in PaperCut NG and MF to gain access to internet-facing Application Servers and covertly install legitimate remote access tools such as SimpleHelp and AnyDesk. The vendor has released emergency patches and urged customers to restrict access, preserve forensic evidence, and rebuild affected servers if compromise is suspected. #PaperCut #CVE-2026-81578 #CVE-2026-82078 #SimpleHelp #AnyDesk
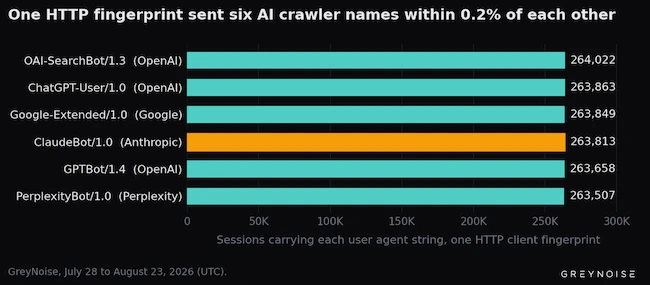
Attackers are forging AI crawler identities from OpenAI, Anthropic, Google, Perplexity, and Amazon to hide automated scans that search websites for exposed credentials and configuration files. GreyNoise found the activity came from 824 IP addresses targeting paths like /.env and /.aws/credentials, but did not confirm whether any secrets were actually stolen. #OpenAI #Anthropic #Google #Perplexity #Amazon #ClaudeBot

T&K TOKA confirmed a ransomware attack and unauthorized access to parts of its systems, causing the suspension of some business operations. The company is working with police to investigate the intrusion and potential data exposure, while the attacker identity and full impact remain unknown. #T&KTOKA
Compucase detected a cybersecurity incident on August 30, 2026, affecting a limited part of its computer network, and immediately isolated the impacted systems while bringing in external experts. Current assessments indicate that no personal or confidential data was leaked and the company’s operations remain unaffected. #Compucase
The University of Barcelona (UB) is investigating a recently detected cyberattack affecting some of its systems and is working with Catalonia’s cybersecurity authorities and CSUC to determine the scope of the incident. The university says no data has been affected so far, while it has implemented containment, monitoring, credential renewal, and temporary service interruptions. #UniversityofBarcelona #CSUC #CataloniaCybersecurityAgency
New Century Ophthalmology Group in the US, a leading ophthalmology practice in North Carolina, reported a ransomware incident involving the incransom threat actor after an alleged compromise of its systems. The attack impacted patient-facing operations and services in the US, highlighting disruptions to advanced eye care and treatment delivery. #UnitedStates
Allied Recycling in Ireland was targeted by ransomware attributed to the Qilin threat actor, resulting in disruption to systems and operations. The incident impacted Ireland #Ireland