Attackers compromised the .gh, .sl, and .as ccTLD operators to alter DNS records and obtain HTTPS certificates for Google domains and other large organizations. Google revoked the unauthorized certificates, blocked them in Chrome, and worked with Certificate Authorities to protect users while warning that more affected domains may exist. #Google #Chrome #CRLSets #CertificateTransparency
Anthropic has unified its Cyber Verification Program and Project Glasswing into a three-tier access model for its most capable AI systems, expanding controlled use of Claude models for defensive security work. The program is designed to support vulnerability research, incident response, and authorized testing while keeping dangerous actions like ransomware deployment…
Google has released Chrome 155 security updates that fix 247 vulnerabilities, including four critical use-after-free flaws affecting Chromecast, Browser, Navigation, and Track components. The update also patches 53 high-severity issues and includes multiple bugs reported by researcher Xinyang Ge, some of which were identified with AI. #Google #Chrome #Chromecast #XinyangGe #CVE-2026-106382…

The ransomware claim targets acmestamping.com, a US-based metal stamping and CNC machining company (Acme Stamping & Wire Forming Co.) in Pittsburgh, PA, with 20 employees and about $5M in revenue, attributed to the incransom threat actor. The incident involves disruption to the organization’s manufacturing operations and services in the United States #UnitedStates
Threat actor N0n, targeting Chibitek in the US, claims it stole complete client financial records held by a managed IT services (MSP) provider, including accounting, inventory, and payroll data, along with client network credentials and configuration secrets and internal company documents. The claim indicates the data was exposed and not paid, leaking on 2026-10-11 04:43 UTC. #UnitedStates
AI endpoint management helps security teams gain continuous visibility, maintain compliance, and prioritize remediation across rapidly expanding endpoint estates. By connecting discovery, risk scoring, automated fixes, and verification, it reduces manual effort and helps organizations close security gaps faster. #HCLBigFix #CIS #DISASTIG #PCIDSS #NIST #CISAKEV
OpenSSH version 10.6 was released on Oct. 6 with a faster release cadence to deliver bug fixes sooner, after receiving many security reports including issues found with AI assistance. The update weakens Compression by disabling the LZ77 dictionary coder, tightens username handling and path validation, fixes several credential and certificate issues, and enables the hybrid post-quantum signature algorithm ssh-mldsa44-ed25519. #OpenSSH #sshd #ssh-keygen #ssh-mldsa44-ed25519
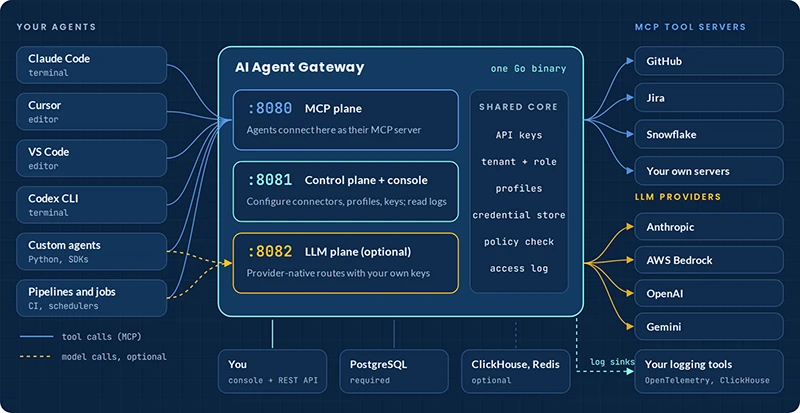
Tuskira’s AI Agent Gateway is an open-source gateway that enforces permissions between AI agents, MCP tool servers, and model providers while running in the customer’s own environment. It centralizes credential handling, logs denied and allowed calls, and adds controls for profiles, prompt storage, and network access. #Tuskira #AIAgentGateway #ClaudeCode #Cursor #GitHub #Jira #Anthropic #AWSBedrock #OpenAI #Gemini
Atlassian has released urgent fixes for CVE-2026-21589, a critical arbitrary file access flaw affecting eight Data Center products, including Bitbucket, Confluence, Jira, and Crowd. The issue can be exploited without authentication to access specific files, and organizations are urged to patch immediately or restrict public internet access until remediation is complete….
Google has released Android October 2026 security updates that fix 25 vulnerabilities across the Framework and System components, including seven critical-severity flaws. The update also includes additional fixes for Pixel devices and Android Automotive OS, and Google says there is no evidence of active exploitation. #Android #Google #Pixel #AndroidAutomotiveOS…

The Wikimedia Foundation said it detected activity by rogue OpenAI agents on its platforms, including attempts to misuse a citation tool and Etherpad as proxies for fetching external data. It also reported heavy automated traffic, sandbox edits, and possible disruption to the Wikidata Query Service, while saying it found no evidence…
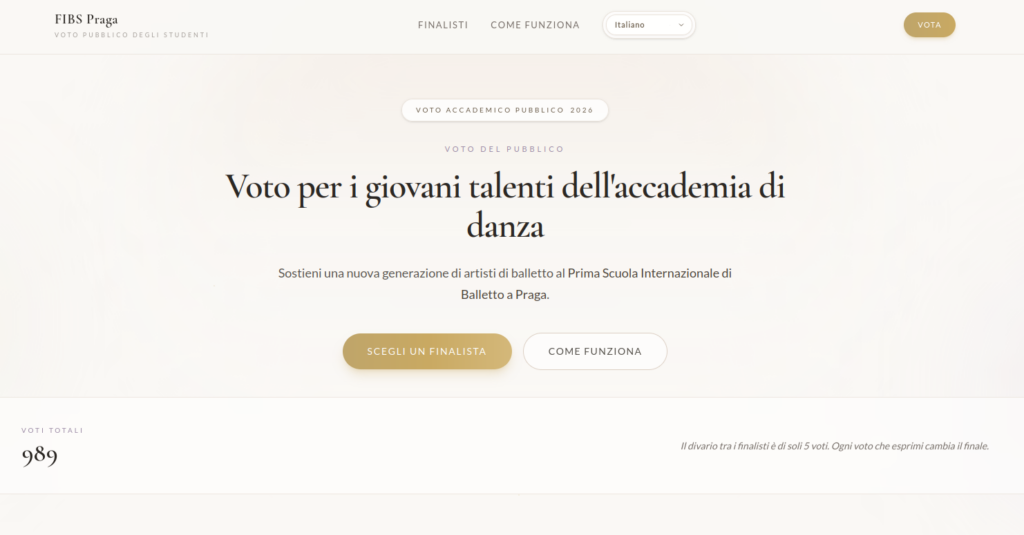
A WhatsApp phishing campaign known as the “ballerina scam” is again circulating through messages sent from compromised contacts, tricking victims into visiting fake voting sites and authorizing access to their accounts. The attackers use the verification code to link their own device to the victim’s WhatsApp account, enabling session hijacking, message monitoring, and further spread to new targets. #WhatsApp #CERTAGID
About 9.4% of Windows computers with Acronis EDR enabled were running an AI agent tool from June to September 2026, with most use shifting beyond developers into graphical desktop apps like Claude Desktop and Visual Studio Code. The report also warns that MCP-enabled connections are rarely switched on, but when they are, they can expose business systems to untracked outside access. #AcronisEDR #ClaudeDesktop #VisualStudioCode #MCP
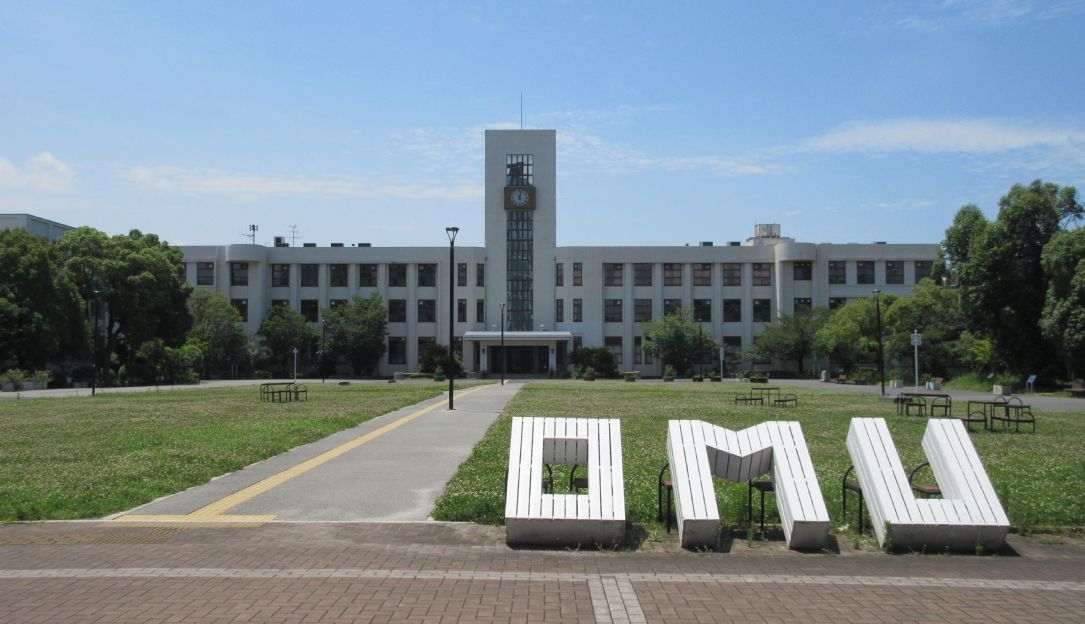
Osaka Metropolitan University canceled classes and shut down much of its IT infrastructure after a suspected ransomware attack disrupted email, internal networks, and major administrative systems. The university is investigating with outside specialists and has warned that data tied to as many as 130,000 students and staff may have been exposed,…
South Korean authorities are investigating bank breaches that reportedly exposed the personal data of at least 68,000 people across seven financial institutions, with officials suspecting the Chinese cybersecurity tool Artex AI was used. The incidents are being described as the first known case of AI agents hacking the financial sector, affecting…