Researchers uncovered the first confirmed Pegasus spyware infection of 2026 and a new NoviSpy variant targeting Serbian student activists, lawmakers, and local officials. The cases, linked to political unrest and upcoming elections, suggest a broader surveillance campaign in Serbia, with Apple notifications helping expose the victims. #Pegasus #NoviSpy #CitizenLab #SHAREFoundation #Apple #NSOGroup
Sality, a Russia-based peer-to-peer botnet that infected more than 11 million devices over 23 years, has been dismantled by law enforcement, CrowdStrike, and the Shadowserver Foundation. The takedown used infrastructure seizure and network disruption to cut off the botnet’s control, ending its use in cryptocurrency theft, cyberattacks, and DDoS activity. #Sality #CrowdStrike #ShadowserverFoundation #Europol #FBI

The FCC is proposing a public scorecard to rate telecom providers on how effectively they prevent and deter illegal robocalls, using broad performance metrics rather than a simple checklist. On the same day, the agency removed 14 providers from the Robocall Mitigation Database for failing to fix compliance issues, cutting them off from U.S. telecom networks. #FCC #RobocallMitigationDatabase #STIRSHAKEN #BrendanCarr
A critical authentication bypass in JFrog Artifactory (CVE-2026-82329) is being actively exploited to mint administrative tokens on self-managed instances. Because Artifactory artifacts are trusted by downstream build and deployment systems, attackers could poison packages and potentially trigger malicious code execution across connected environments. #CVE-2026-82329 #JFrogArtifactory #watchTowr #GuillermoRauch

A forum user named weykofa posted 16.2 MB across 450 files tied to science.co.il, the Israel Science and Technology Directory. Most of the material appears to be public directory content, with only a few visitor log entries and legal documents suggesting anything beyond what was already publicly available. #sciencecoil #weykofa…
Andrew Richards introduces The Cybersecurity Pulse with insights on AI security, governance, and emerging threats, while highlighting how agentic AI is increasingly shaping both attacker tradecraft and defender priorities. The newsletter also covers infrastructure takedowns, emergency patching, verifiable AI logging, and new funding for companies building security and identity controls for autonomous systems. #CursorAgent #ClaudeSonnet4_5 #Aurora #Minimus #Echo #QScan #QTRouter #TRACE #PaperCutMF #PaperCutNG #Citrix #Alice #ActiveFence #Socure #Fravity #Kazimi

Manifold Security disclosed eight flaws across seven command-line AI coding agents where repository-controlled Git settings could trigger code execution on a developer’s machine, with four issues still unpatched at publication. OpenAI also issued three CVEs for the same attack class in Codex, while affected tools and versions included goose, Claude Code,…

Rockwell Automation has issued patches and workarounds for more than a dozen vulnerabilities across its industrial automation products, including critical and high-severity flaws in RSLinx Classic, ControlLogix, CompactLogix, and other tools. The advisories cover denial-of-service, remote code execution, privilege escalation, and cross-site scripting issues, with CISA also publishing guidance for CVE-2026-9637….
The UK Cyber Security and Resilience Bill has been amended to give ministers new powers to block critical-sector organizations from using high-risk technology suppliers. The move was triggered by a reported Iran-linked attack on a UK energy generator and highlights growing concern over supply chain security across UK critical infrastructure. #CyberSecurityandResilienceBill…

In MX, the ransomware claim targeting Trucka was attributed to the incransom threat actor, a transportation and logistics company providing local and long-distance freight shipping across major routes. The attackers’ actions disrupted Trucka’s logistics operations, affecting businesses relying on timely cargo movement and delivery across Mexico. #Mexico
The ransomware claim targets Westfield Public School District in the United States, attributed to the threat actor incransom. Westfield Public Schools serves students, families, and the broader community in Westfield, NJ, and the district’s operations may be impacted as a result of the attack. #UnitedStates
Asfaltos y Pavimentos S.A. (Asfalpasa) in Spain was targeted by the ransomware threat actor incransom, with their operations related to the fabrication, transport, and laying of asphalt mixtures and road construction and maintenance services. The attack resulted in disruption and data impact affecting organizations in #Spain
Several government websites linked to France’s Ministry of Ecological Transition were rendered inaccessible after a cyberattack claimed by an anonymous user on a criminal forum. ANSSI is investigating suspected user account compromise, while the incident caused service disruptions and a temporary outage of some digital services, including in the Creuse prefecture. #ANSSI #MinistryofEcologicalTransition #CreusePrefecture
Dropbox warned users that an unauthorized party accessed some accounts by abusing a flaw in Lenovo’s email verification process to create fraudulent Lenovo IDs tied to victims’ email addresses. The attacker then used Lenovo ID-based authentication to log into Dropbox without needing the account password, prompting Dropbox to expire affected sessions and require passwords for Lenovo ID sign-ins. #Dropbox #Lenovo
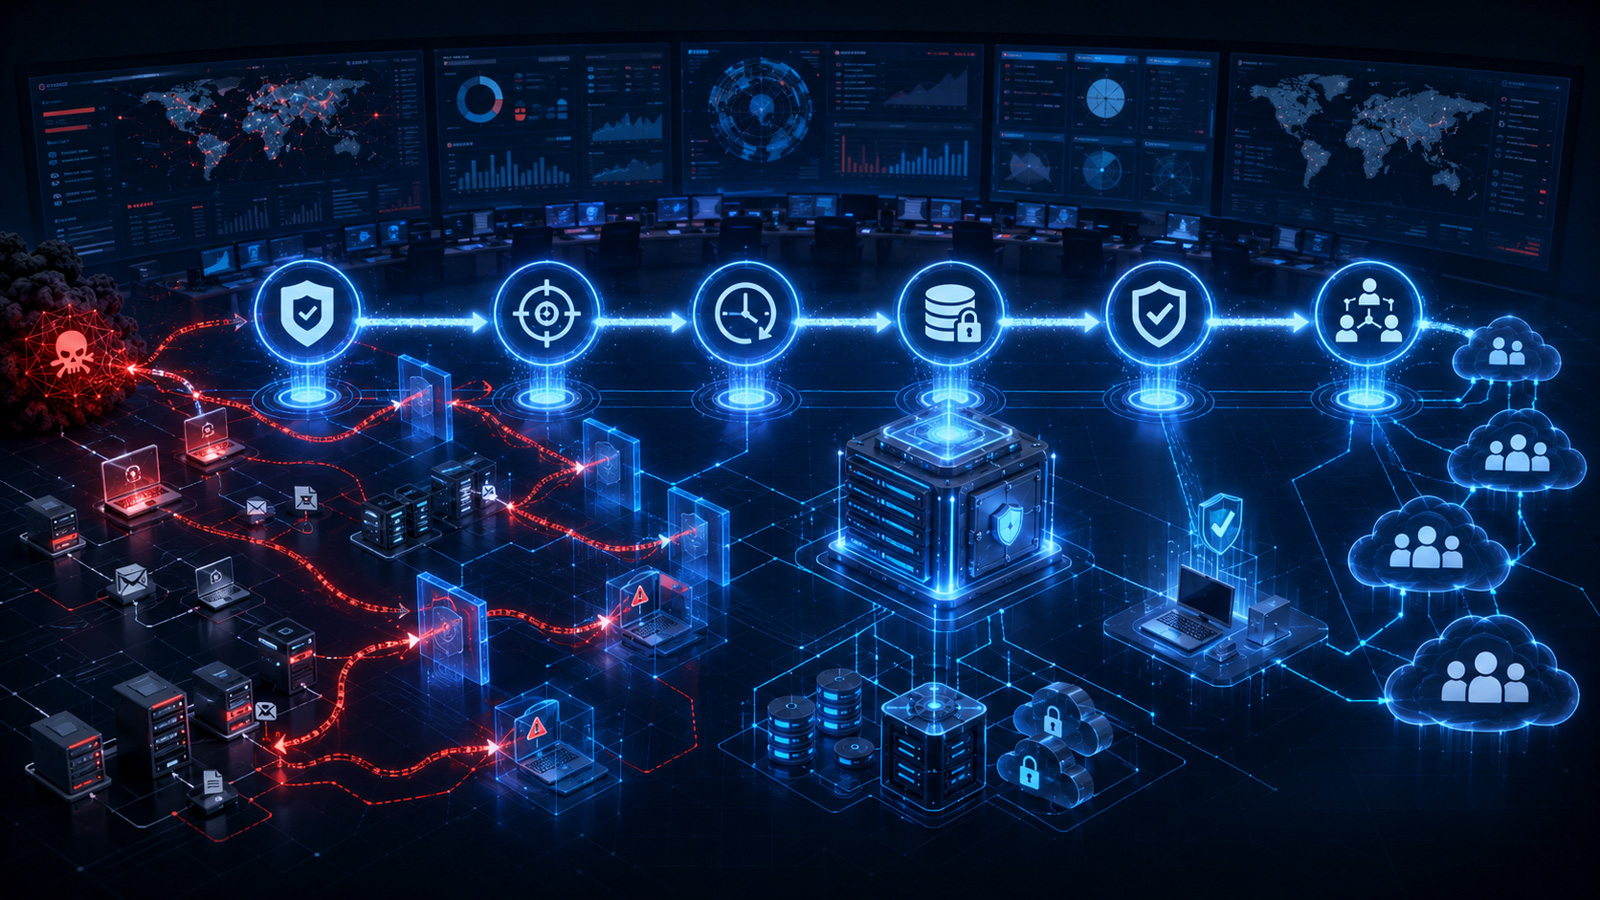
Ransomware protection for MSPs must go beyond backups by proving six outcomes: reducing exposure, detecting attacks before encryption, delivering 24/7 response, preserving recovery points, recovering cleanly, and operating consistently across tenants. The Acronis Cyberthreats Report highlighted 143 MSP, IT-service provider, and telecom victims in 2025, with phishing and unpatched vulnerabilities driving most initial access cases. #AcronisCyberProtectCloud #AcronisMDR #AcronisEDR #AcronisXDR