Searzhudin Tamirlanovich Aktulaev was indicted for running a 2016 malware campaign that used TVRAT, also known as TVSPY or TeamSpy, to infect more than 80,000 users through fake messages and malicious Excel attachments. Prosecutors say he also used DarkVNC, stole credentials and personal data, and maintained access to victims’ devices through…

A malicious LNK file disguised as a seafood ingredient purchase request was used to deliver a decoy HWP document while PowerShell, scheduled tasks, and external communications ran in the background. The attack exfiltrated system information, fetched additional commands from Backblaze B2, and was linked by AhnLab to Kimsuky. #Kimsuky #BackblazeB2 #AhnLab…

Netskope Threat Labs reports that Python-based NodeStealer has evolved from a Facebook credential stealer into a spyware-capable tool with keylogging, clipboard monitoring, screenshot capture, and a split Telegram C2 design. The new variant also expands Facebook Graph API collection to more than 20 endpoints, suggesting AI-assisted development and broader abuse of Facebook and Ads Manager data. #NodeStealer #NetskopeThreatLabs #Facebook #AdsManager #Telegram

SilentRansomGroup ransomware targeted S… M…, with the full company name redacted pending disclosure. Full Data Timer was active for the incident, impacting #countryname
SilentRansomGroup allegedly deployed ransomware against G… …g, with a full company name currently withheld pending disclosure, and a full-data timer indicating ongoing activity. The claim involves an undisclosed impacted region, ending with: #countryname
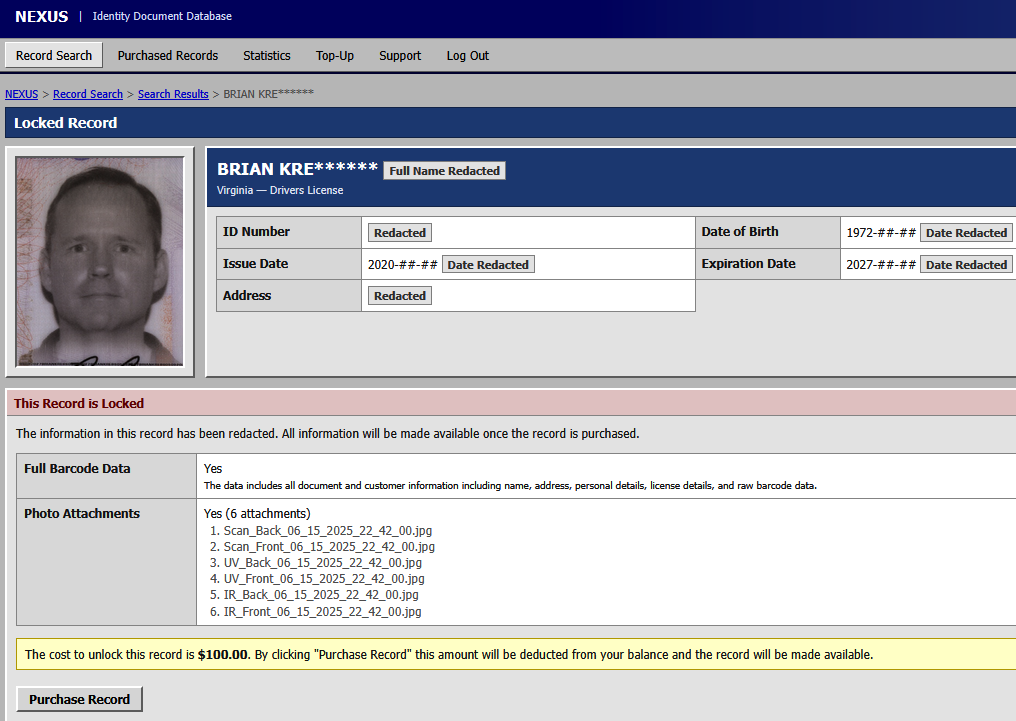
IDScan appears to have suffered a massive breach in which hacker NEXUS is selling 153 million scanned identity documents, including driver’s licenses, ID cards, passports, and medical cards, on the EXPLOIT forum. KrebsOnSecurity verified the leak, while IDScan has launched an investigation and the FBI has opened a formal probe. #IDScan…
A high-severity SQL injection flaw in the All-in-One WP Migration and Backup plugin can let unauthenticated attackers achieve remote code execution and take over WordPress sites. The issue, tracked as CVE-2026-19949, affects versions through 7.109 and was fixed by ServMask in version 7.110 after disclosure by Wordfence and researcher Jack Taylor. #CVE-2026-19949 #All-in-OneWPMigrationandBackup #Wordfence #ServMask #JackTaylor
Attackers are actively exploiting CVE-2026-9586, an unauthenticated SQL injection flaw in Sangoma Switchvox that can lead to remote code execution. Horizon3 reported rapid attack attempts from a single source IP and warned that most internet-exposed Switchvox systems may already have been targeted. #CVE-2026-9586 #Switchvox #Sangoma #Horizon3

Microsoft reported an active malware campaign that uses fake software-download sites to impersonate trusted vendors and deliver malicious installers, with victims across multiple industries and China-based operations. The activity is linked with moderate confidence to Silver Fox (Yinhu), and related reporting also ties ValleyRAT delivery to malicious installers and DLL sideloading…

Google has launched Gemini 3.8 Flash Cyber through the Fairwind Program to give trusted defenders early access to advanced cybersecurity capabilities for protecting critical infrastructure. Anthropic and OpenAI also introduced new frontier models and safeguards as they race to improve vulnerability discovery, reduce misuse, and control model behavior in real-world cyber…

OpenLeash is a new product from Max Brin designed to place a control layer around autonomous AI agents so their real-world actions stay aligned with user intent. It monitors, blocks, or escalates risky actions like database deletion or unauthorized payments, and is already being used by hundreds of users and multiple…

The National League Against Cancer reported a cybersecurity incident that temporarily affected services in its Radiotherapy Department. The institution said the incident is under investigation by the competent authorities and that its team is working to restore services quickly.
Ormond Beach, Florida, in the US, was targeted by the Wallstreet ransomware group, disrupting services and encrypting local systems. The city’s businesses and residents faced downtime and potential data exposure as a result of the attack, impacting the United States. #UnitedStates
PTT Oil and a retail business in Thailand were targeted by the direwolf ransomware operation, with attackers using malware to encrypt systems and disrupt operations. The incident highlights potential risks to chemical-related business processes and critical infrastructure in Thailand and beyond. #Thailand
Cartrack Holdings in South Africa was targeted by the direwolf ransomware, which encrypted company data and disrupted operations. The incident occurred using ransomware software associated with direwolf, impacting South Africa. #southafrica