Ransomware operators linked to krybit impacted ligacancerguate.org, targeting INCAN,— Instituto de Cancerología y Hospital Dr. Bernardo del Valle S., in Guatemala (GT). The incident involved disruption of access to healthcare services and pressure to pay a ransom, impacting Guatemala. #Guatemala

Luminis Health has engaged legal counsel amid an ongoing cybersecurity incident affecting the hospital system’s web platforms. The investigation remains active as the organization works to assess the scope and impact of the disruption. #LuminisHealth
The radiation data collection system used around nuclear facilities such as Shimane was hit by a cyberattack. Authorities confirmed that backup servers were not affected, so data monitoring remains uninterrupted. #Shimane #TottoriPrefecture
A Russian national, Searzhudin Tamirlanovich Aktulaev, has been indicted in California for allegedly using hundreds of fake freelance-platform accounts to send malicious Excel files that infected about 80,000 users. The campaign deployed TVRAT and DarkVNC to steal data from victims, including many in the US, and used the stolen information for fraud and other crimes. #SearzhudinTamirlanovichAktulaev #TVRAT #DarkVNC #TeamViewer #VNCViewer
Microsoft is working on a fix for a known issue that causes Microsoft Teams and new Outlook to crash or fail to launch on ARM-based Windows 11 24H2 devices after August 2026 updates. A temporary workaround is to update the Auto Super Resolution Package from the Microsoft Store until a permanent Windows fix is released. #MicrosoftTeams #Outlook #SurfaceLaptop7 #SurfacePro11 #AutoSuperResolutionPackage
Plex urged users to update Plex Media Server and Plex Desktop immediately after discovering multiple security vulnerabilities affecting Plex Media Server v1.43.2 and earlier. The company has released patches and emailed affected users, warning that attackers could reverse-engineer the fixes before CVEs are published. #Plex #PlexMediaServer #PlexDesktop

A high-severity flaw in the All-in-One WP Migration and Backup WordPress plugin, tracked as CVE-2026-19949, can let attackers trigger remote code execution by abusing a second-order SQL injection during archive restore operations. The issue affects versions up to 7.109, and with only 35% of installations updated to 7.110, about 3.2 million…
A threat actor on the dark web began selling scans of more than 153 million US and Canadian driver’s licenses through an identity theft service called Nexus, which was later shut down. Investigators linked the cache to a likely breach at IDScan.net, prompting an FBI investigation after some exposed licenses were…

Star Aviation, Inc (US) reported a ransomware incident involving the Storm threat actor, impacting its operations as a Commercial Aerospace EWIS solution center providing engine wire harness repair services including DER repairs and PMA. The claim indicates the disruption occurred in the United States. #UnitedStates
Petrocare Construction (CA) reported a ransomware incident attributed to Storm, disrupting construction management operations in Canada. The attack impacted the company’s activities across its Western Canada facilities, with effects noted in #Canada
Engefitas, a Brazilian manufacturer of adhesive tapes and adhesives for packaging, automotive, construction, electronics, and manufacturing sectors, is reported to have been hit by the Vexy Ransomware threat actor, indicating a disruption involving encrypted or stolen data. The incident is associated with impacts to operations and data security within Brazil. #Brazil
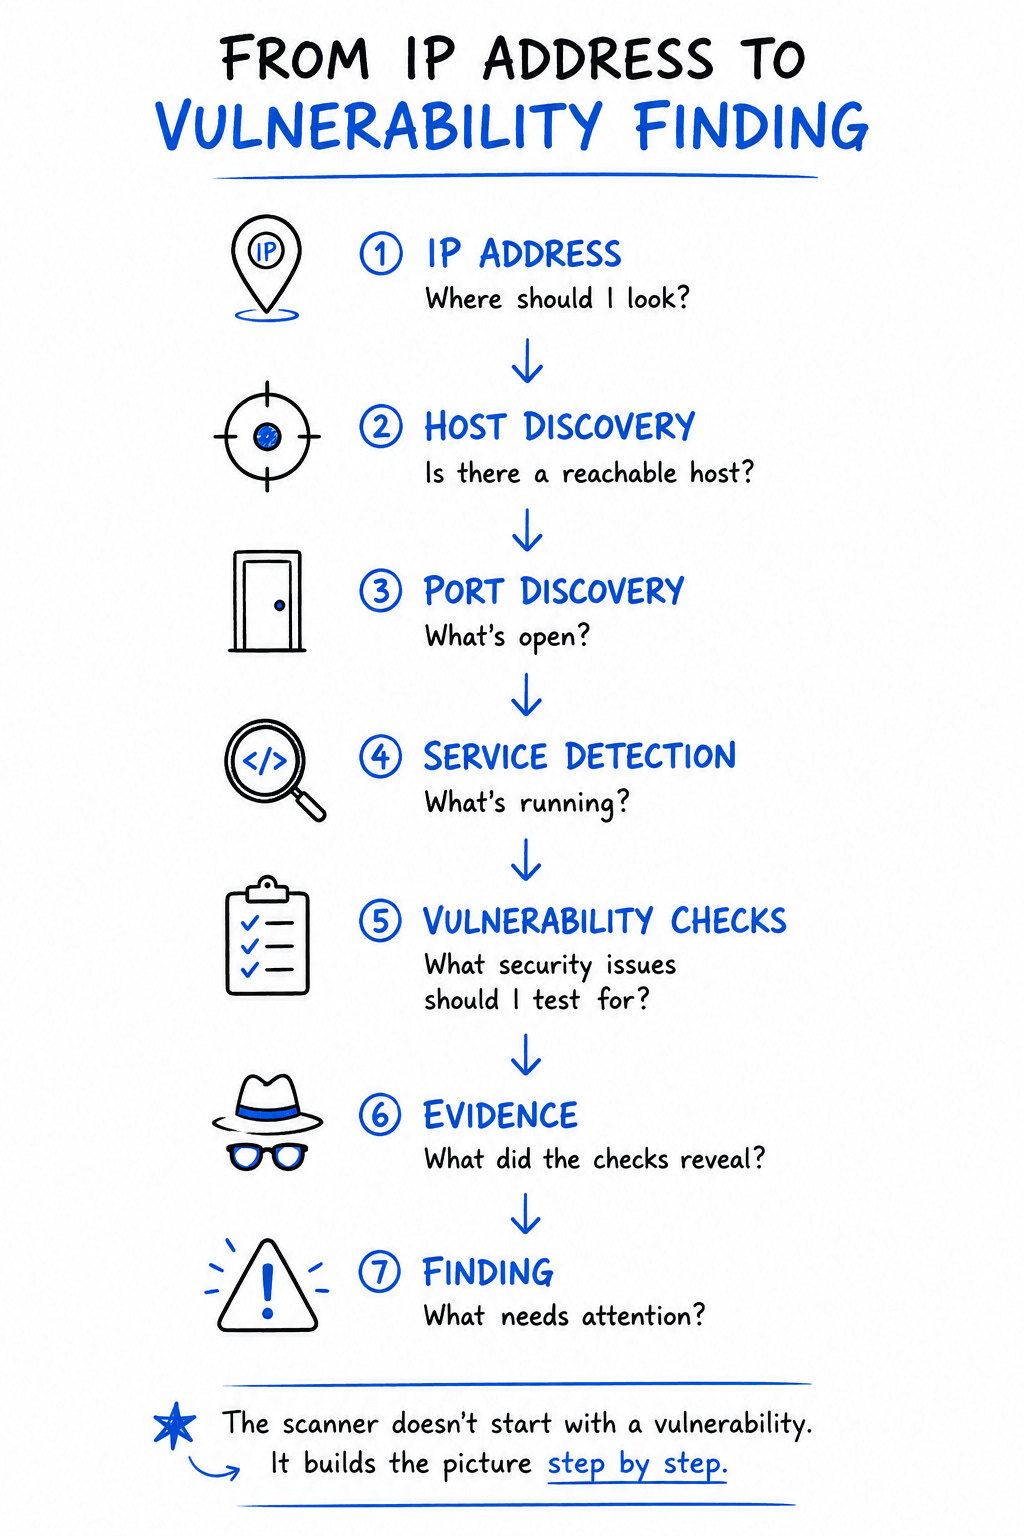
This article follows a single IP address through a vulnerability scan to show how a scanner moves from host discovery and port detection to service identification, vulnerability checks, and evidence collection before creating a finding. It also explains why networking knowledge and authenticated access matter when interpreting scan results and deciding what to remediate. #DrawnToCyber #DecodedSecurity
Incransom ransomware allegedly targeted Metales Panamericanos (previously known as ACERO PANAMA), a leading construction and steel supplier in Panama, demanding data or ransom following an attack on their systems. Metales Panamericanos, based in Panama, provides steel materials and expanded construction solutions including electrical solutions, equipment & devices, zing ceilings, strollers, metal wires, window structures, gypsum, and more. #Panama
VantaCore is a ransomware group believed to be a rebrand of Thor, targeting Russian organizations with custom-built malware and multimillion-dollar ransom demands. F6 says the group has attacked at least seven victims, uses a ransomware-as-a-service model, and reflects a broader shift among pro-Ukrainian hackers toward in-house tooling instead of LockBit 3…

CISA has added seven actively exploited vulnerabilities to its KEV catalog, affecting SonicWall SMA 1000, Sangoma Switchvox, JFrog Artifactory, Kludex Starlette, Kestra OSS, and Berri LiteLLM. Threat actors are abusing these flaws to gain admin access, execute commands, deploy reverse shells and miners, steal credentials, and target AI infrastructure for follow-on…