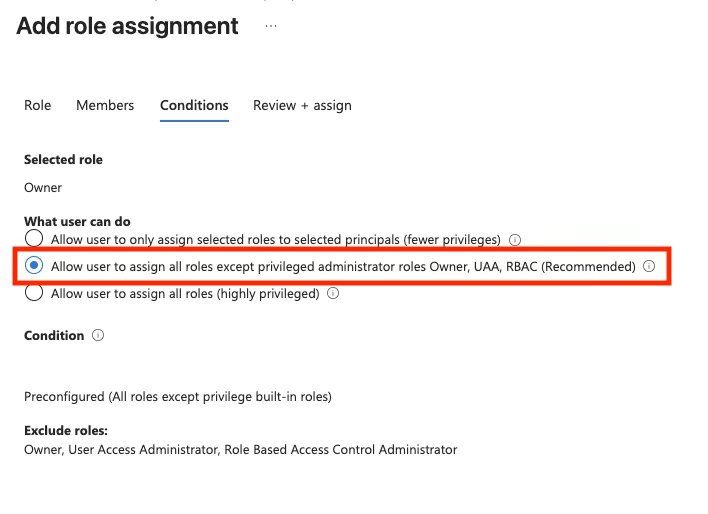
The article explains how Azure RBAC and ABAC can be analyzed at the permission level to uncover privilege escalation paths, including a built-in role that once allowed arbitrary escalation to Owner. It also describes an undocumented ARM API for mapping permissions to roles, the discovery and remediation of the Anyscale Platform Administrator Role issue, and recommendations for reducing attack surface in Azure. #AzureRBAC #ABAC #AnyscalePlatformAdministratorRole

Dustin, a Swedish IT retailer operating in the Benelux region through Centralpoint, took part of its IT environment offline after an unauthorized access incident. The company is investigating with external experts and authorities while assessing whether any customer data was compromised. #Dustin #Centralpoint

Ransomware from threat actor settra encrypted and stole documents from verveportraits.com.au (Verve Portraits Pty Ltd), demanding a ransom for their release. The victim’s operations in Australia were impacted. #Australia
Insomnia ransomware impacted Maglin, Miskiv & Associates in Parsippany, NJ in the United States, disrupting their personalized accounting, tax planning, bookkeeping, payroll, financial consulting, tax preparation, and audit support services. The affected systems and operations were impacted in #UnitedStates.
settra ransomware targeted ialegre.com in Brazil, encrypting Documents Industrias Alegre S.A. as part of the “Complete Data Breach PROLOGUE Industrias Alegre S.A.” incident. The impacted country is #Brazil
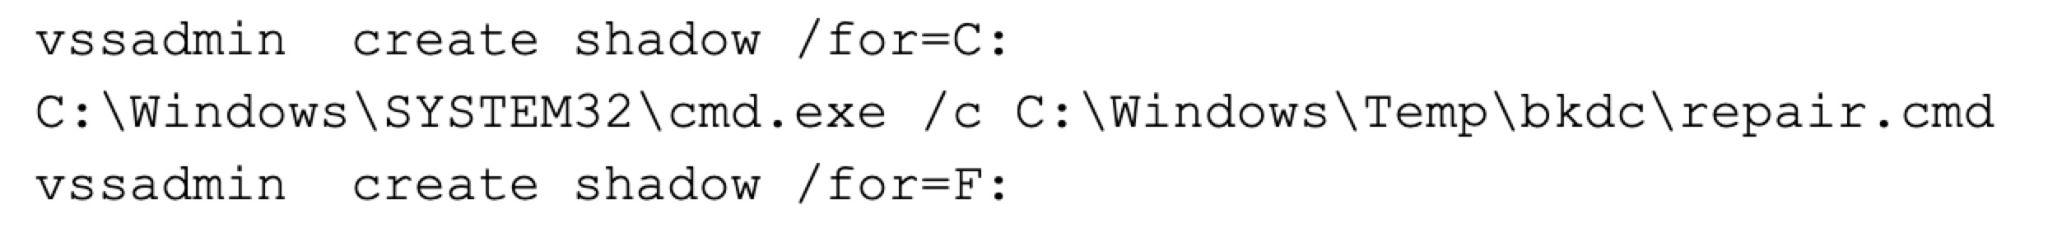
This report details two AI-assisted intrusion campaigns in Latin America: CL-CRI-1131 against Mexican transportation and government-related targets, and CL-CRI-1163 against Brazil’s financial sector. Attackers used living-off-the-land techniques, custom RATs, SOCKS5 tunneling tools, and exposed NextChat/LLM infrastructure to troubleshoot failures, stage scripts, and exfiltrate data. #CL-CRI-1131 #CL-CRI-1163 #NextChat #SockTz #Claude #GPT-4.1…
Google has launched Gemini 3.8 Flash with stronger performance in software engineering, agentic tasks, and multi-step reasoning, while keeping the more permissive Gemini 3.8 Flash Cyber limited to vetted security teams through the Fairwind program. The Cyber version is focused on vulnerability research and patching, with Google and its security partners reporting major gains in correct fixes, faster discovery, and improved prompt-injection robustness. #Gemini #Fairwind #ChromeSecurity #GraySwan

Thomson Reuters disclosed a breach affecting its C-Track court case management platform, exposing court records and sensitive personal information across multiple jurisdictions in the U.S., Canada, and the U.S. Virgin Islands. The company said the incident began in March 2026, was discovered on June 30, 2026, and has prompted free credit monitoring and identity theft protection for affected individuals. #ThomsonReuters #C-Track #OntarioSuperiorCourtOfJustice #WyomingJudicialBranch
A forum actor calling themselves Intelligence claims to be selling 3,134,269 DZI Insurance records that include national ID numbers, passport numbers, addresses, and contact details. The post says the data came from a poorly secured customer portal API and is being offered to only two buyers, but the breach claim remains…
A forum user named GoreTerminal claimed to leak a HopCharge analytics export containing 19,323 accounts, including full names, phone numbers, email addresses, IP addresses, and precise coordinates. The report says the data was shared free behind a reply wall, but the claim remains unverified and may reflect an exposed or misconfigured…
Microsoft confirmed that the KB5120998 August 2026 preview update resets mouse personalization settings on Windows 11, but only on non-English installations. The issue affects cursor and cursor animation settings, and Microsoft says impacted locales load default values instead of the user’s saved preferences. #KB5120998 #Windows11

AIR Security has emerged from stealth with $50 million in funding to launch AIR, a firewall designed to protect AI agents and their add-ons. The company says its research found thousands of public AI add-ons and AI Skills with untrusted instruction sources, impersonation tactics, and hidden behaviors that could expose enterprises…
HiddenLayer raised $100 million in a Series B round, bringing its total funding to more than $155 million, to expand security for agentic, generative, and predictive AI applications. The company plans to strengthen runtime protection for AI coding agents and help enterprises detect anomalous behavior, misuse, and unauthorized actions in production….
Capsule Security has launched an “AI circuit breaker” that detects, evaluates, and blocks autonomous agent actions in real time before they can cause harm. The system uses specialized models trained with NVIDIA Nemotron 3 Ultra and claims high accuracy and fast response times to stop rogue behavior inside agentic workflows. #CapsuleSecurity…
McDonald’s Ecuador, the local franchise operation of the global McDonald’s brand in EC, reported a ransomware incident attributed to Vexy Ransomware impacting its fast-food restaurant operations nationwide. The affected business includes restaurants operated under the franchise model through Arcos Dorados, including product lines such as burgers, fries, beverages, breakfast items, and children’s meals. #Ecuador