This article turns telemetry from over 1.8 million endpoints into a practical hardening guide for remote access tools most often abused by attackers, including RDP, ScreenConnect, MeshAgent, and VNC. It recommends a tiered defense strategy of blocking, monitoring, and tightly auditing remote tools to reduce attack surface and detect attacker-deployed access quickly. #RDP #ScreenConnect #MeshAgent #VNC #AmmyyAdmin #UltraVNC #RDPWrap

Katten Muchin Rosenman, a U.S.-headquartered law firm, was targeted by SilentRansomGroup in a ransomware claim affecting its systems and potentially disrupting legal operations. The incident involves the United States. #UnitedStates
Studio Oculistico Ciraci, an ophthalmology clinic in Bari, Italy, reported a ransomware incident attributed to the threat actor spacebears, potentially disrupting patient care and diagnostic services. The clinic has served the Italian National Health Service (SSN) since opening in 1989, and the attack could impact its ongoing operations across healthcare workflows in #Italy
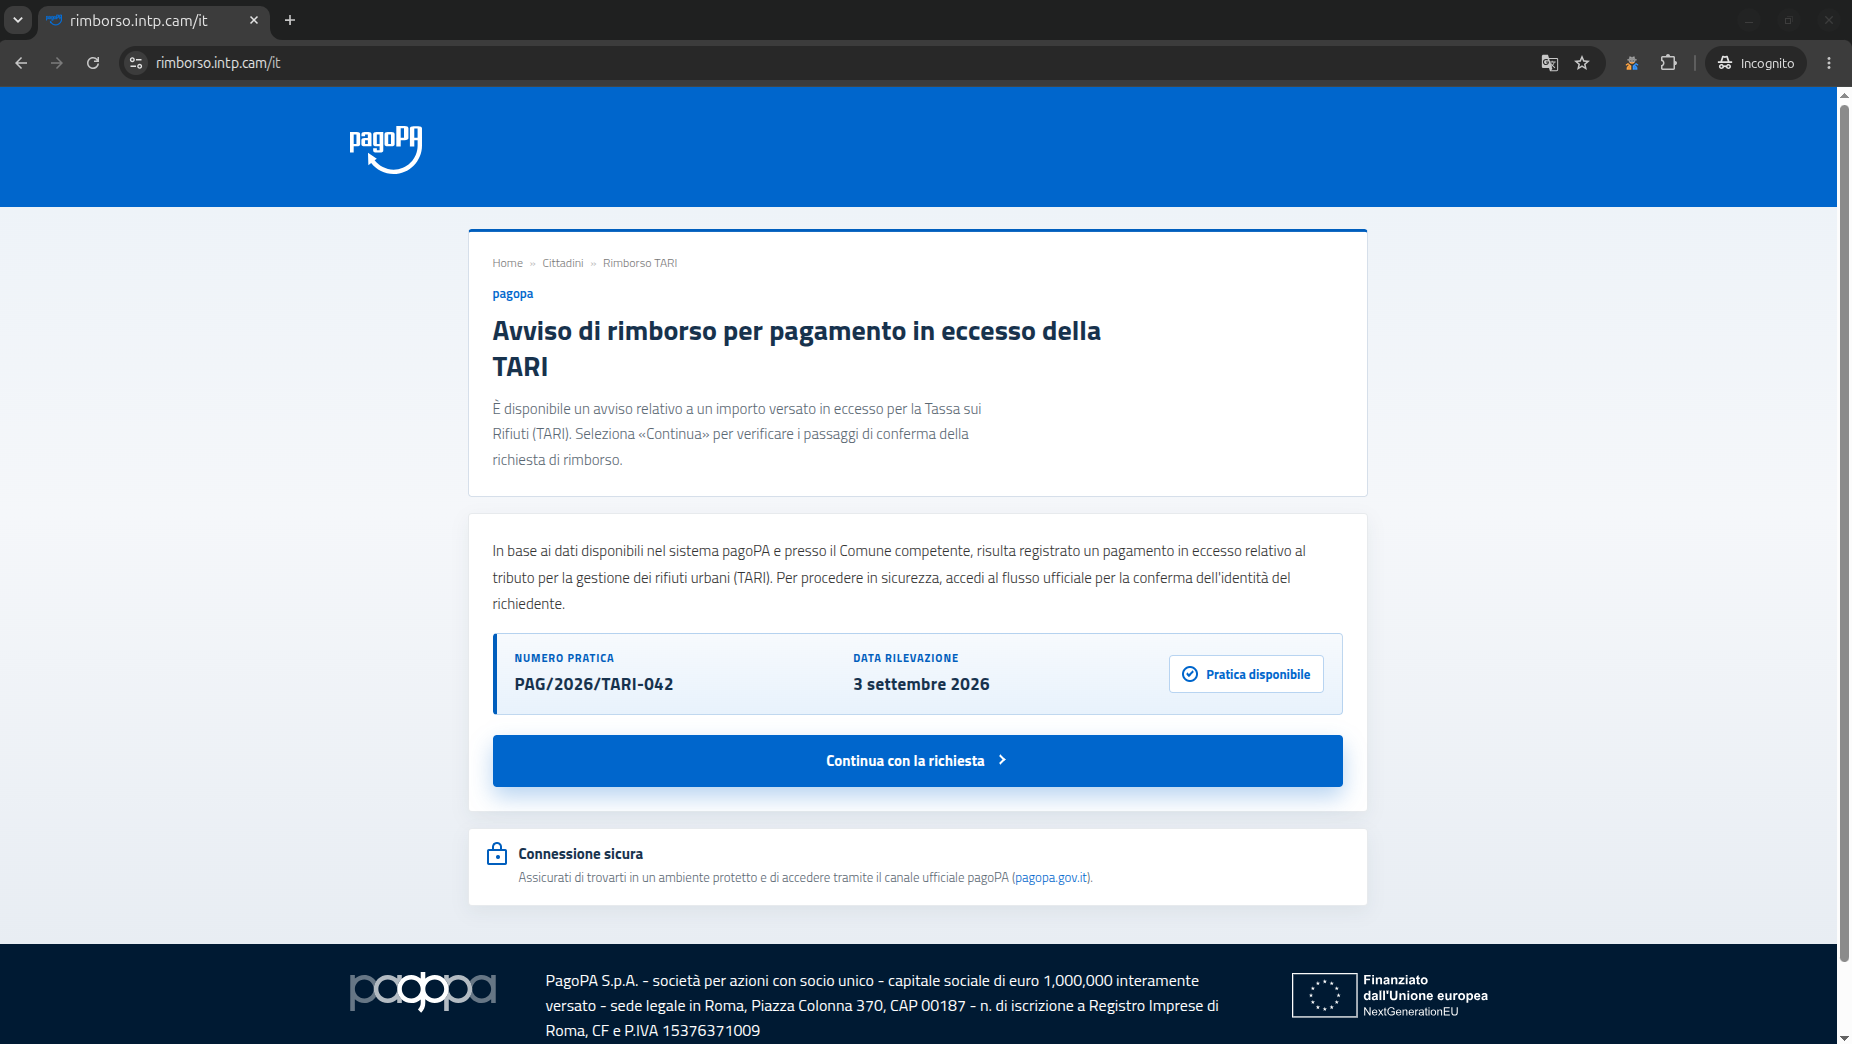
CERT-AGID identified fraudulent sites impersonating PagoPA to steal personal data and payment card information by offering a fake TARI overpayment refund. The campaign used a staged online form to collect identity details, contact information, and card data for potential fraud and future phishing operations. #PagoPA #CERT-AGID #TARI
Attackers compromised Coder’s Cloudflare infrastructure and redirected some registry traffic to unauthorized servers that served malicious Terraform modules. The malicious code stole credentials and secrets from affected environments and exfiltrated them to coder-infra[.]com. #Coder #Cloudflare #Terraform #coder-infra
France’s CNIL fined Hôpital privé de la Loire €500,000 after a 2025 data breach exposed sensitive information belonging to more than 727,000 people linked to the hospital. The investigation found major GDPR security failures, including weak access controls, lack of VPN and multi-factor authentication, and insufficient monitoring; the teen hacker “Marak” later claimed responsibility. #HôpitalPrivéDeLaLoire #CNIL #Marak #GDPR

The G7 cybersecurity working group is urging governments and organizations to accelerate migration to post-quantum cryptography before quantum computers can undermine today’s public key encryption. The report warns that quantum risk is already a business and economic issue, and calls for coordinated planning to protect sensitive data, authentication systems, and secure communications. #G7 #PQC #CISA #NCSC #ANSSI #BSI #CSE #NCO #ACN
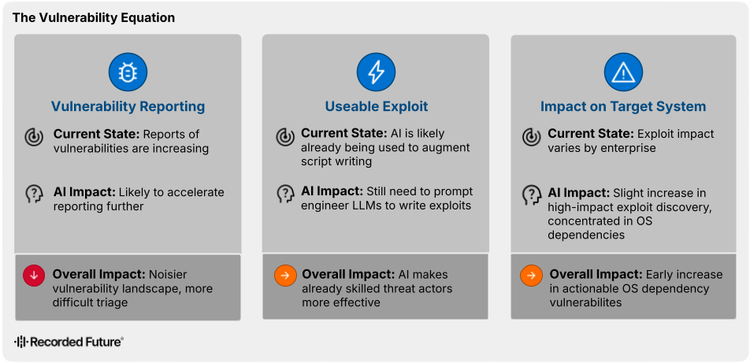
H1 2026 threat activity was dominated by abuse of legitimate tools, trusted platforms, and routine workflows, while AI mainly augmented existing intrusion tradecraft rather than replacing it. The report also highlights widespread exploitation of exposed CVEs, persistent RAT and stealware activity, evolving supply-chain compromises, NFC-based mobile fraud, and Magecart campaigns that leveraged trusted third-party services. #AsyncRAT #CobaltStrike #XWorm #Stealc #REMCOSRAT #PromptSpy #NGate #NFCShare #Magecart #ShaiHulud #TeamPCP

EtherHiding has been used on more than 5,400 compromised small-business websites to fetch payloads from BNB Smart Chain testnet smart contracts, enabling takedown-resistant delivery of ClickFix lures or a covert WebRTC command channel. Netskope says the campaign spans over 2,200 organizations worldwide and continues to grow as operators rewrite a single on-chain contract to change what victims receive. #EtherHiding #BNBSmartChain #ClickFix #WebRTC

Cisco has issued urgent fixes for a critical Nexus 9000 flaw, CVE-2026-20212, that could let a remote unauthenticated attacker run code as root on affected Silicon One-based switches. The company also released an IOS XR hardening update covering seven umbrella CVEs, while separate advisories address Secure Email S/MIME decryption issues, a…

This roundup shows how attackers are using normal-looking actions like Teams chats, file-sharing prompts, trusted software, and OAuth consent to gain access without obvious alarms. It also highlights active threats including The Gentlemen ransomware, Outsider phishing-as-a-service, Nexus ID theft, RevStealer, BlueKit, CRPx0, and abuse tied to Lenovo ID, Dropbox, Faronics Deploy,…
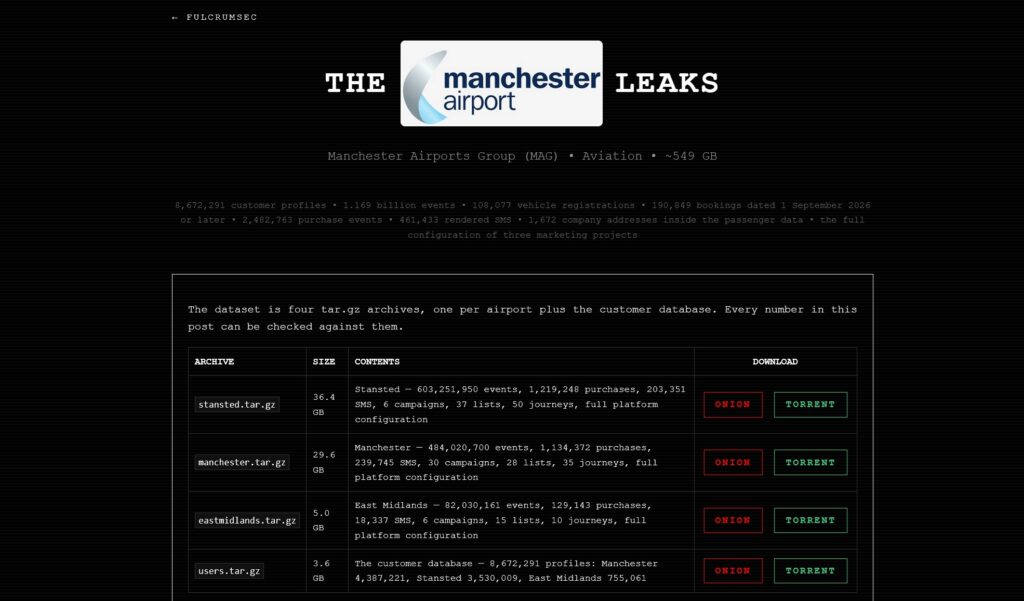
A breach involving the Manchester Airports Group (MAG) allegedly exposed the personal data of about 8.8 million people, including email addresses, phone numbers, vehicle registrations, and postcodes. FulcrumSec claimed responsibility, said it stole 550 GB of data, and stated that MAG refused to pay the ransom. #ManchesterAirportsGroup #MAG #FulcrumSec…
A critical vulnerability in Elementor Pro, tracked as CVE-2026-32475, is being actively exploited to upload webshells and run arbitrary commands on WordPress servers. Defiant’s Wordfence has blocked nearly 200,000 attempts since the patch on August 19, and administrators should upgrade to Elementor Pro 4.2.2 or later and inspect the uploads directory for rogue PHP files. #CVE-2026-32475 #ElementorPro #Wordfence
Hewlett Packard Enterprise has patched CVE-2026-73749, a critical buffer overflow in ArubaOS-CX that could let unauthenticated remote attackers achieve code execution with elevated privileges. The bulletin also addresses 23 additional ArubaOS-CX flaws affecting enterprise network switches used by organizations such as large businesses, government agencies, universities, healthcare organizations, data centers, and service providers. #HPE #ArubaOSCX #CVE-2026-73749

Daily Recap, Attackers are exploiting AI and application flaws—such as Langflow CVE-2026-0768 for unauthenticated RCE and credential theft, along with malicious .git configurations that can make agents like Claude, Codex, and Cursor execute attacker code—while vendors and defenders push new safeguards for AI logs and agent security. Across other sectors, SonicWall SMA 1000 is under active exploitation via CVE-2026-83548 and CVE-2026-83549, and incidents span credential phishing (including OAuth consent phishing), supply-chain abuse (JFrog Artifactory, Cleo Harmony), and major breaches affecting Aesto Health and Novocure. #Langflow #CVE-2026-0768 #Claude #SonicWallSMA1000 #CVE-2026-83548 #CVE-2026-83549 #JFrog #Artifactory #CleoHarmony #OAuthConsentPhishing #FBI #AestoHealth #Novocure