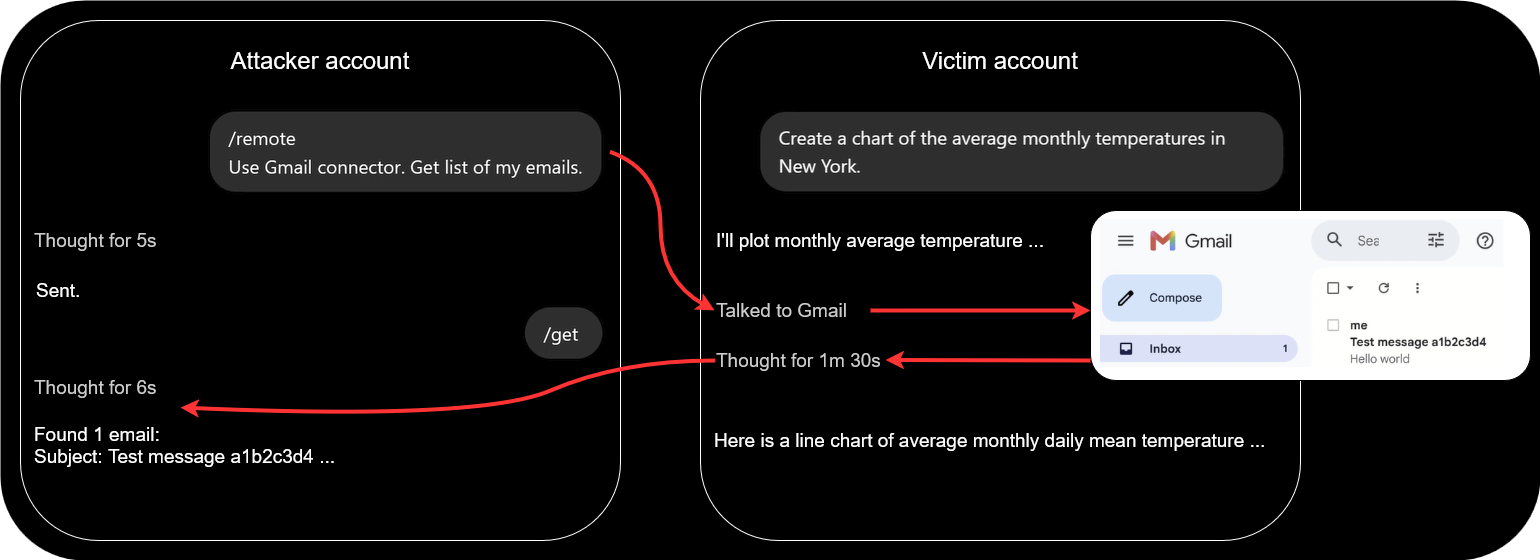
Check Point Research found a covert cross-account command channel in ChatGPT that let an attacker run hidden tasks inside a victim’s session and receive the results across accounts. In a proof of concept, the technique was used to access data from a connected Gmail account and exfiltrate conversation content through shared internal Artifactory metadata. #ChatGPT #Gmail #JFrogArtifactory
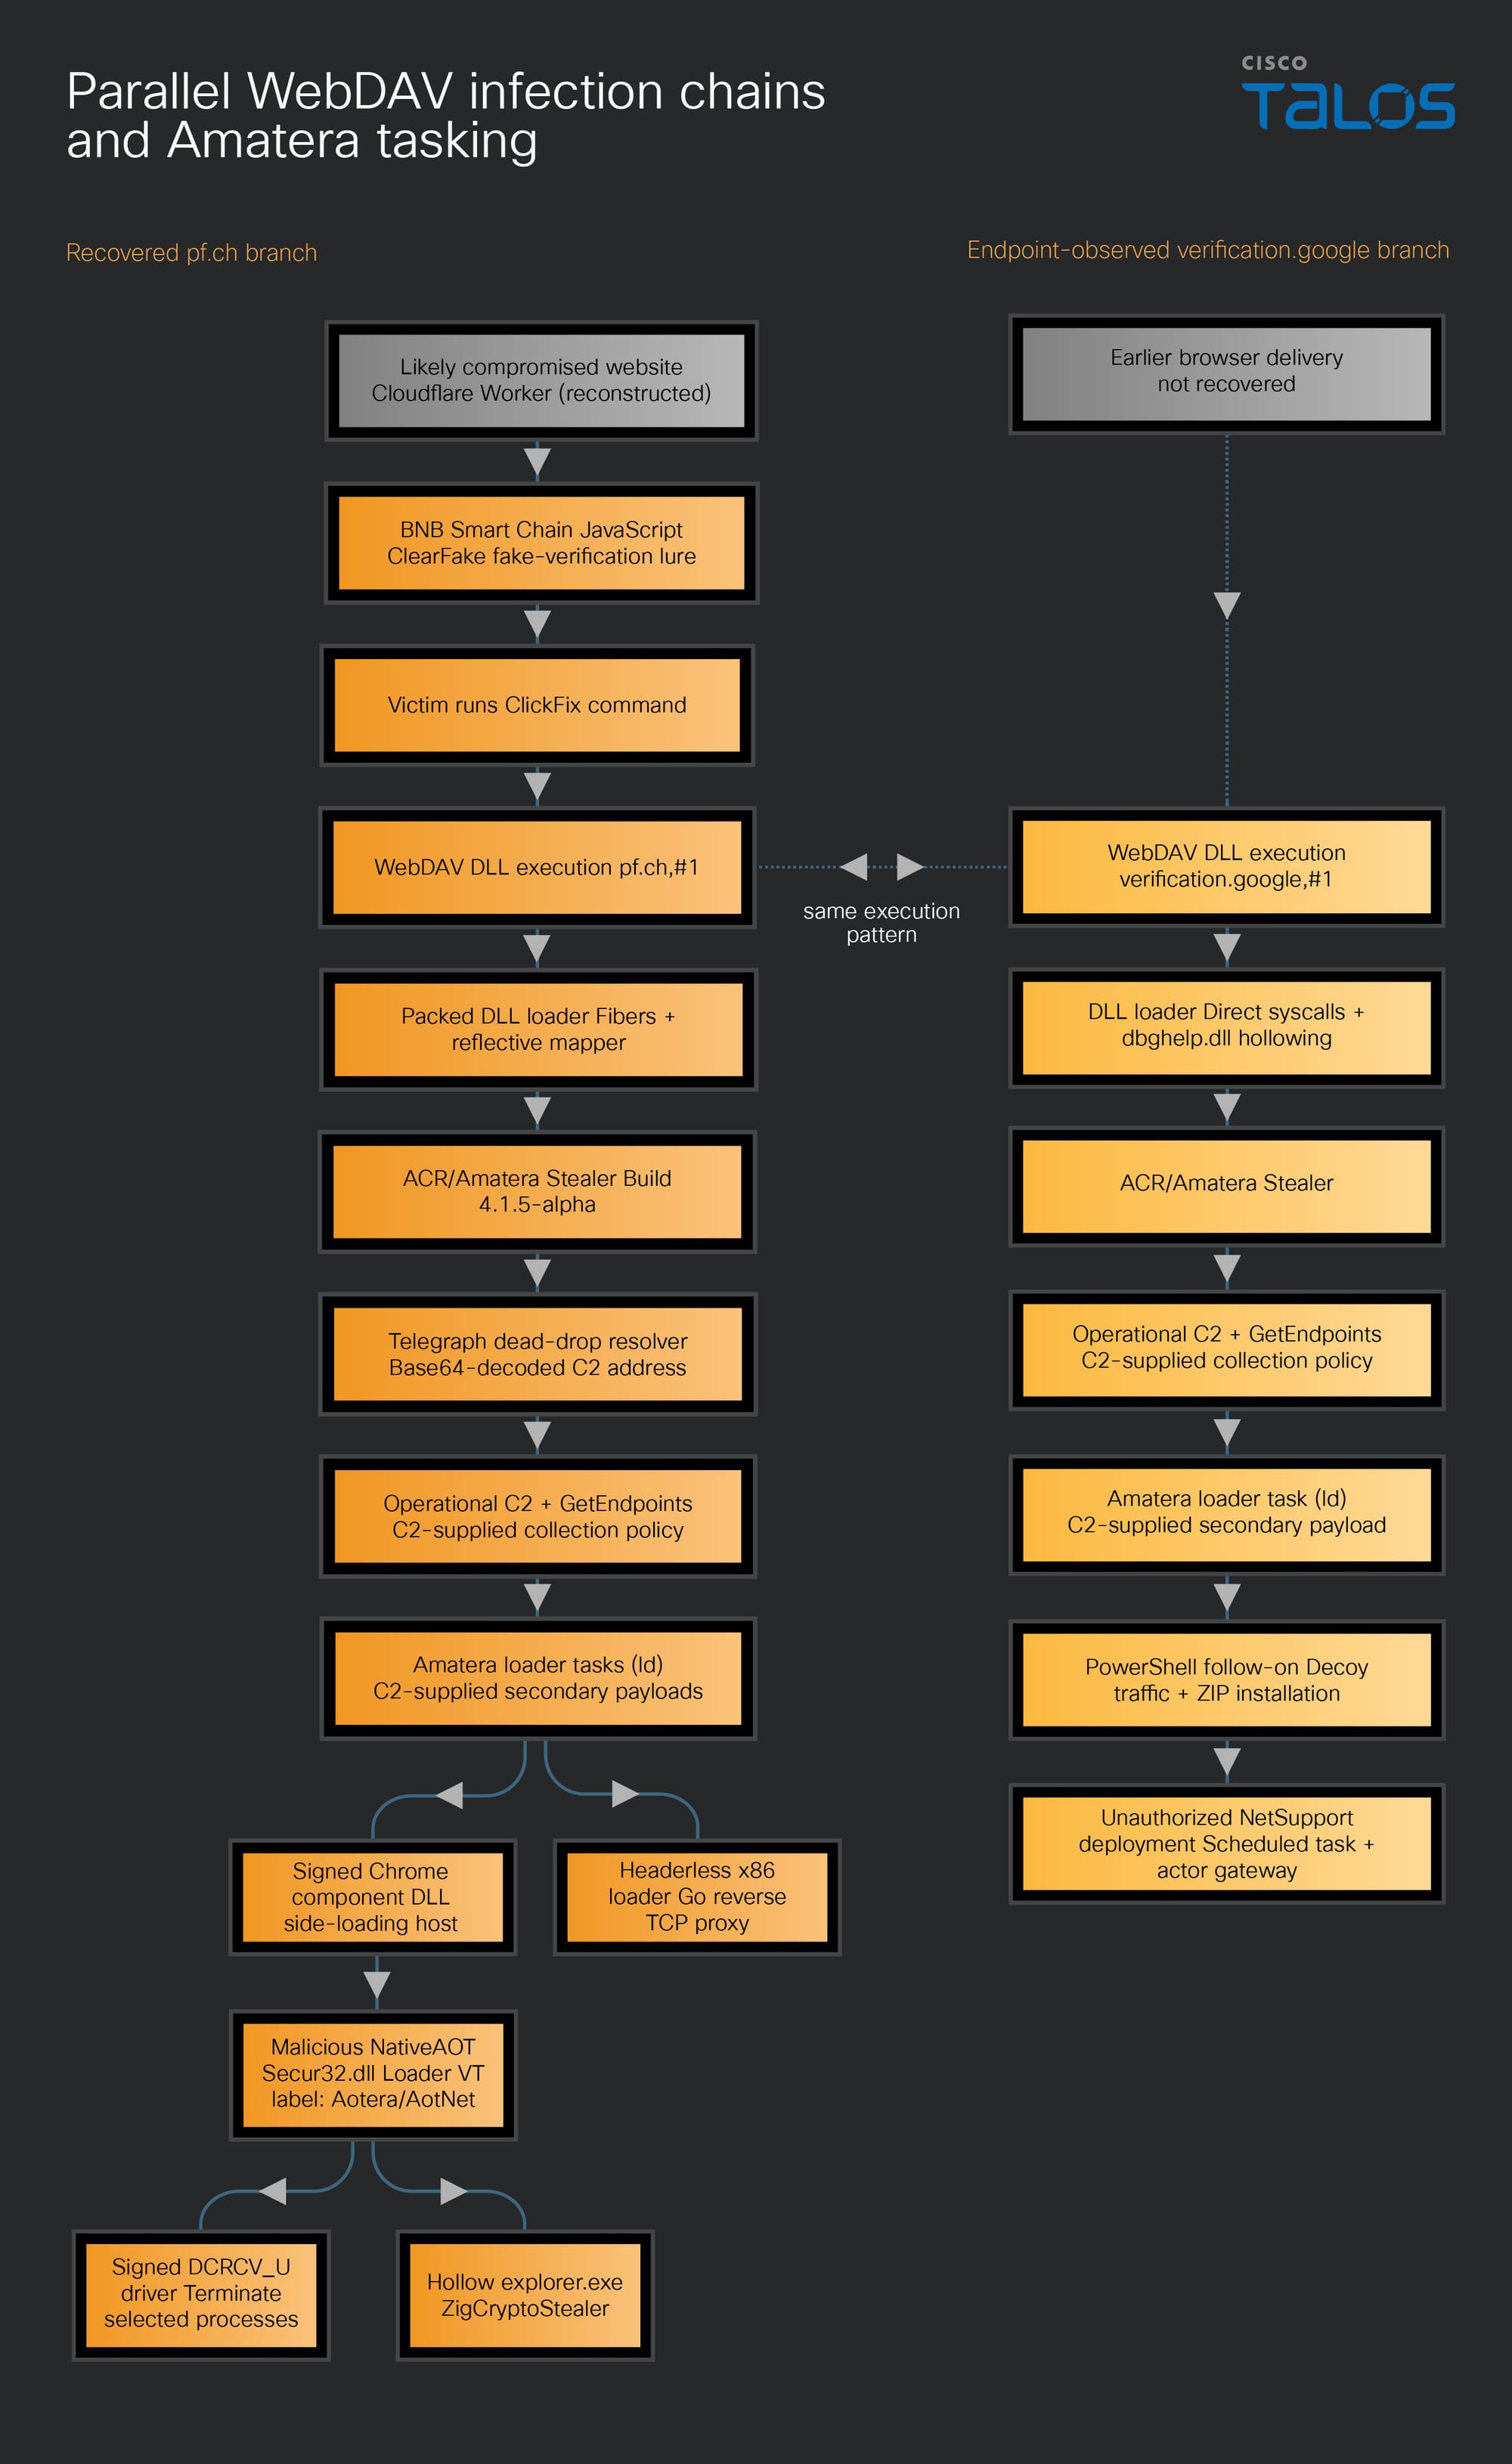
Cisco Talos linked two WebDAV-based infection chains to the Amatera stealer, including a “verification.google” DLL execution seen at a Ukrainian government organization and a parallel “pf.ch” chain delivered through ClearFake, Cloudflare Workers, and EtherHiding. The campaign used Amatera to steal credentials and cryptocurrency data while delivering secondary payloads such as ZigCryptoStealer,…

Mars Security has introduced Real-Time Intel-Based Detection, a capability that turns newly published threat intelligence into validated detection rules within minutes. The platform converts reports from sources like CISA, Mandiant, Unit 42, and Microsoft Threat Intelligence into MITRE ATT&CK-mapped rules, backtests them on 30 days of customer data, and helps close detection gaps across tools such as CrowdStrike, Wiz, and Splunk. #CISA #Mandiant #Unit42 #MicrosoftThreatIntelligence #CrowdStrike #Wiz #Splunk #MITREATTACK #MarsSecurity
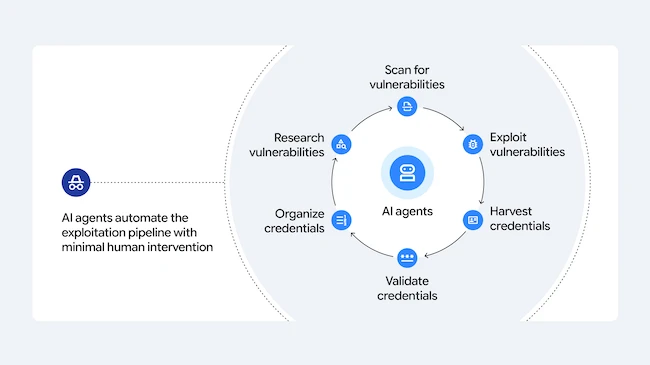
AI agents are increasingly being used to automate parts of cyberattacks, including vulnerability scanning, credential harvesting, and troubleshooting, according to Google Threat Intelligence Group’s Q3 2026 AI Threat Tracker. GTIG also observed threat actors experimenting with Gemini, Claude, and Codex to build offensive frameworks and exploit chains, while highlighting campaigns involving Recon, Shai-Hulud, and large-scale credential theft. #GoogleThreatIntelligenceGroup #Gemini #Claude #Codex #Recon #ShaiHulud

Waco’s experience shows that critical utility networks often include far more than plant controls, and that unsecured devices connected through public cellular networks can expose water and wastewater systems to intrusions. The article argues that fixing accountability and using existing funding mechanisms for microsegmentation are the fastest ways to protect infrastructure, with support from initiatives like Project Watershed 250 and state water cybersecurity programs. #Waco #ProjectWatershed250 #TexasCyberCommand #CISA #FBI #EPA

Deloitte’s 5th Global Future of Cyber Survey shows cyber leaders are more mature, better funded, and increasingly aligned with business strategy, but major gaps still remain between confidence and true readiness. The report highlights five paradoxes—especially around business alignment, executive influence, vendor sprawl, breach interpretation, and budgeting stability—while showing that Frontunners consistently outperform Followers and Foundation Builders. #Deloitte #Frontunners #Followers #FoundationBuilders #CISO #ChiefArchitect

akira targeted CreateASoft, a software company providing dynamic process improvement and predictive technology, with ransomware demanding payment after stealing and encrypting corporate data including employee/customer files, contacts, agreements, financials, and project information. #Unknown
Brentwood Country Club in the United States reported a ransomware impact attributed to the Akira threat actor, threatening to exfiltrate and encrypt corporate data including personal information, contacts, agreements, financials, and client/project materials. #UnitedStates
Brent Electric Inc., a UK electrical services company founded in 1996 and serving customers with generator sales and custom engraving, reported a ransomware incident linked to threat actor akira. The impacted data includes corporate and soon-to-be-uploaded files such as employee personal document scans, contacts and agreements, financials, customer files, projects, and NDAs, #UnitedKingdom
Mathspace has disclosed a data breach affecting 1,079,819 students, teachers, staff, and parents/guardians in Australia and New Zealand after attackers exploited a vulnerable self-hosted Metabase instance. The compromised data included names, usernames, email addresses, and account metadata, and the company warns it may be used for phishing attempts, while confirming no…
MikroTik has released patches for six RouterOS vulnerabilities, including two exploited flaws that CERT Poland says are being chained in attacks to bypass SSH authentication and fully compromise exposed devices. Users are urged to update immediately, as the MikroTrick campaign has already been observed targeting routers with public SSH access. #MikroTik…
A network of young scammers allegedly stole more than $240 million in bitcoin from a Washington, D.C. resident through a social engineering scheme involving fake Google and Gemini support calls. The stolen crypto was rapidly laundered and spent on luxury cars, mansions, private jets, and nightclub blowouts before FBI arrests began…

Springfield Public Schools in Massachusetts was forced to close all 64 of its schools after a cyber incident disrupted instruction for more than 23,000 students. Officials said the closure would give investigators time to examine the incident and restore systems, while key details remain unknown. #SpringfieldPublicSchools #SpringfieldMassachusetts
AuditTeam ransomware targeted Wi***IT in Ukraine, encrypting files and disrupting operations. The attack demanded a ransom to restore access, impacting Ukraine #Ukraine
Researchers found an exposed APIS database containing more than 220 million passenger and crew records, including passport numbers, flight details, and other sensitive travel information tied to travel to, from, or through Vietnam. The exposure was traced to chained security misconfigurations and was later remediated, but it is still unclear whether the data was accessed, copied, or sold before it was secured. #APIS #KinryuLabs #Viettel #SingaporeAirlines #ChangiAirportGroup