OpenSSL has released the first alpha of version 4.1.0, introducing DTLS 1.3 support and performance improvements for post-quantum cryptography. The build also brings several compatibility changes, new protocol features, and early support for additional architectures ahead of the final release. #OpenSSL #DTLS13 #MLDSA #MLKEM

Proofpoint found at least four China-aligned threat groups chaining three zero-day flaws in Chrome, Chromium-based browsers, and Windows to carry out espionage since late August. The BlueMoon exploit chain has been used against NGOs, mining and commodity firms, U.S. aerospace companies, and organizations in Vietnam, Indonesia, and Singapore. #TA412 #VioletTyphoon #APT31 #BlueMoon #CVE-2026-85046 #CVE-2026-87491 #CVE-2026-85880 #UNK_LateNight #UNK_DoubleCheck #UNK_QuietRacket

A forum actor using the alias 2019 is claiming to sell a database tied to Blossom Health, a U.S. virtual psychiatric care provider, containing records for more than 29,600 mental health patients. The alleged exposure includes highly sensitive personal, clinical, and insurance billing details, and the claim remains unverified. #BlossomHealth #2019…
A forum actor posting as DaOnlySpark claimed to have a database dump from AdvaCare, a Swiss healthcare consultancy, containing timesheet, task, expense, project, and staff-account data. The post is unverified, but it could expose internal financial details and support phishing or business email compromise. #AdvaCare #DaOnlySpark #Switzerland…

Panzer ransomware impacted Aqualogus, a private engineering consulting firm supporting smart hydraulic, water resources management, and environmental protection projects. The attack disrupted their operations and services for affected clients and stakeholders in #UNKNOWN
AmorSaúde, a rapidly growing network of popular clinics in Brazil, was targeted by the LockBit5 ransomware group, with the victim identified as amorsaude.com.br. The incident impacted medical and dental services across Brazil. #Brazil
AuditTeam allegedly targeted mo***al in Germany with ransomware, encrypting files and demanding payment for their release. The affected organization faced operational disruption as a result of the attack, Germany #Germany
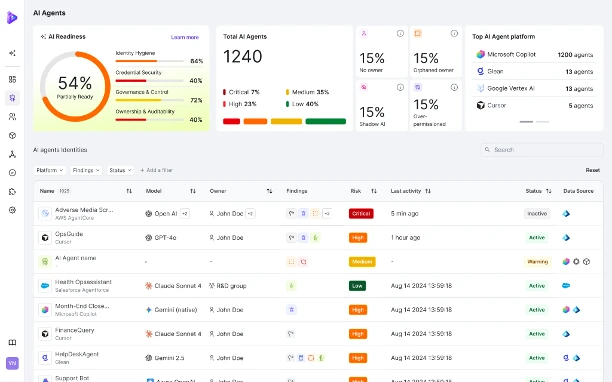
Orchid Security has introduced identity drift detection and application-level kill switches to help enterprises control AI agents that can exceed their intended scope by using hidden identity weaknesses. The company says AI adoption must be paired with continuous observation, governance, and auditability to prevent agents from exploiting orphaned accounts, excessive permissions, and other forms of identity debt. #OrchidSecurity #IdentityControlPlane #PaloAltoNetworksIdira #SplunkEnterpriseSecurity #NIST #DORA
A bipartisan group of U.S. lawmakers is urging the Treasury Department to sanction three India-based hack-for-hire firms, citing years of espionage against American citizens, companies, and lawyers. The firms—Sunkissed Organic Farms, BellTroX, and CyberRoot—have also been tied to global efforts to suppress reporting and, in some cases, alleged work on behalf of the Qatari government. #SunkissedOrganicFarms #BellTroX #CyberRoot #Qatar
The FTC has rescinded a Biden-era policy statement that expanded federal health data breach notification rules to cover health and fitness apps, citing minimal benefit and a shift toward deregulation. The move removes a rule that had aimed to hold apps and connected devices accountable for disclosing breaches involving sensitive health information and data sharing with third parties. #FTC #LinaKhan #HealthInsurancePortabilityAndAccountabilityAct
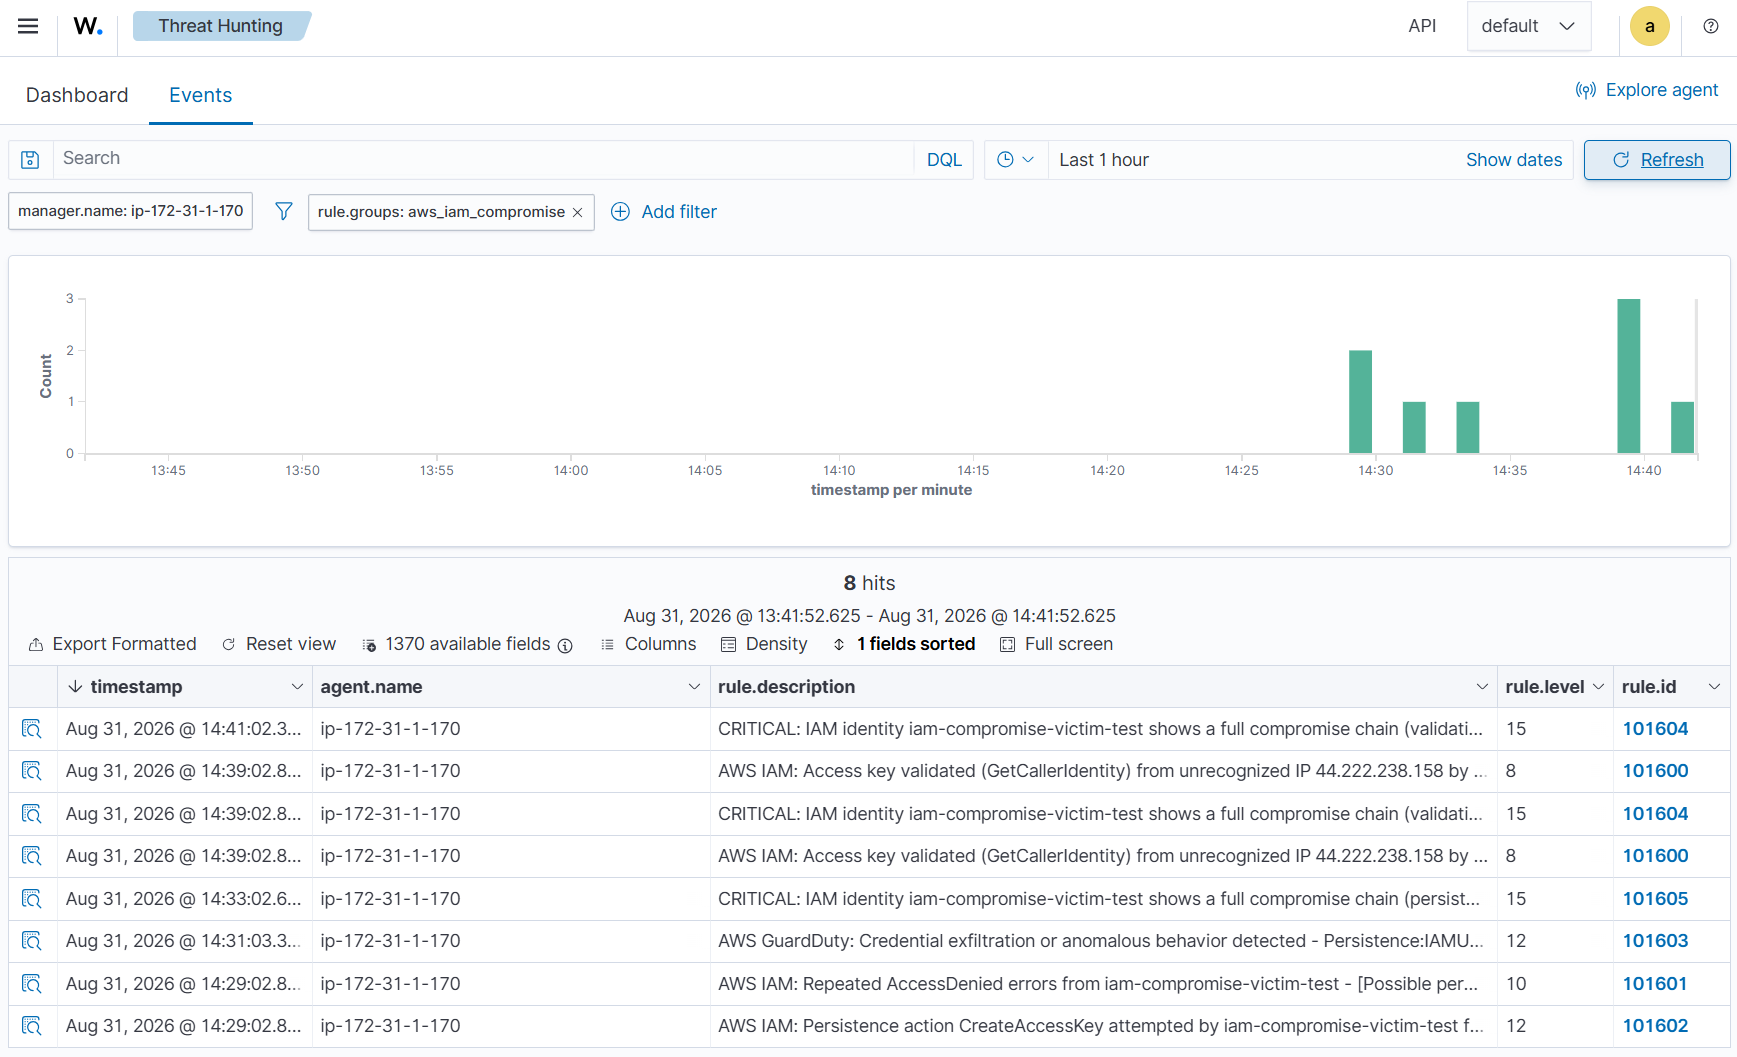
Wazuh detects AWS access key compromise by correlating CloudTrail and GuardDuty telemetry across validation, enumeration, persistence, and exfiltration stages. The article explains how attackers abuse exposed AWS access keys and how Wazuh rules can reconstruct the compromise chain to raise a high-confidence alert. #Wazuh #CloudTrail #GuardDuty #AWSCompromisedKeyQuarantineV2…
Veradigm disclosed a data breach after a third-party vendor compromise exposed patient personal data through a customer-service API, though the incident did not disrupt operations. The Gentlemen ransomware group claimed the attack and says it stole millions of patient records, including names, addresses, SSNs, and contact details, while Veradigm continues its investigation and notification efforts. #Veradigm #TheGentlemen #GentleKiller #SystemBC
U.S. cybersecurity and intelligence agencies say six Chinese AI companies conducted industrial-scale distillation attacks on frontier AI models from Anthropic, OpenAI, Google, and xAI since late 2024. The advisory says the campaigns used fraud, proxies, and API abuse to extract model knowledge at scale, with DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI named in the report. #DeepSeek #MoonshotAI #Alibaba #MiniMax #StepFun #ZAI #Anthropic #OpenAI #Google #xAI #CISA #NSA #FBI
The municipality of Le Tampon has been hit by a cyberattack since Wednesday morning, causing major disruptions and preventing the local authority from carrying out its duties normally. The incident has affected the operations of www.linfo.re and highlights the impact on the public services of Le Tampon in France. #LeTampon #wwwlinfore
Google released September 2026 Android security updates that patch 180 vulnerabilities across Android’s runtime, Framework, System, kernel, and multiple vendor components. The most severe issues include critical flaws in the System component and CVE-2026-28662, a Wi-Fi-related memory corruption bug that could enable remote code execution without user interaction. #Google #Android #CVE-2026-28662…