Grindr has agreed to pay £26 million to settle a UK lawsuit alleging it shared sensitive user data, including HIV status, with advertisers before early 2020. The company says the settlement includes no admission of liability and follows complaints from UK users over privacy practices during the period when Grindr was…

The U.S. government sanctioned Xinbi Guarantee, a Telegram-based illicit marketplace tied to billions in scam-related transactions, money laundering, and human trafficking. Authorities also seized $52.8 million in crypto and targeted related entities and infrastructure supporting the platform’s operations. #XinbiGuarantee #Tether #USDT #Telegram #Elliptic #DOJ #ScamCenterTaskForce…
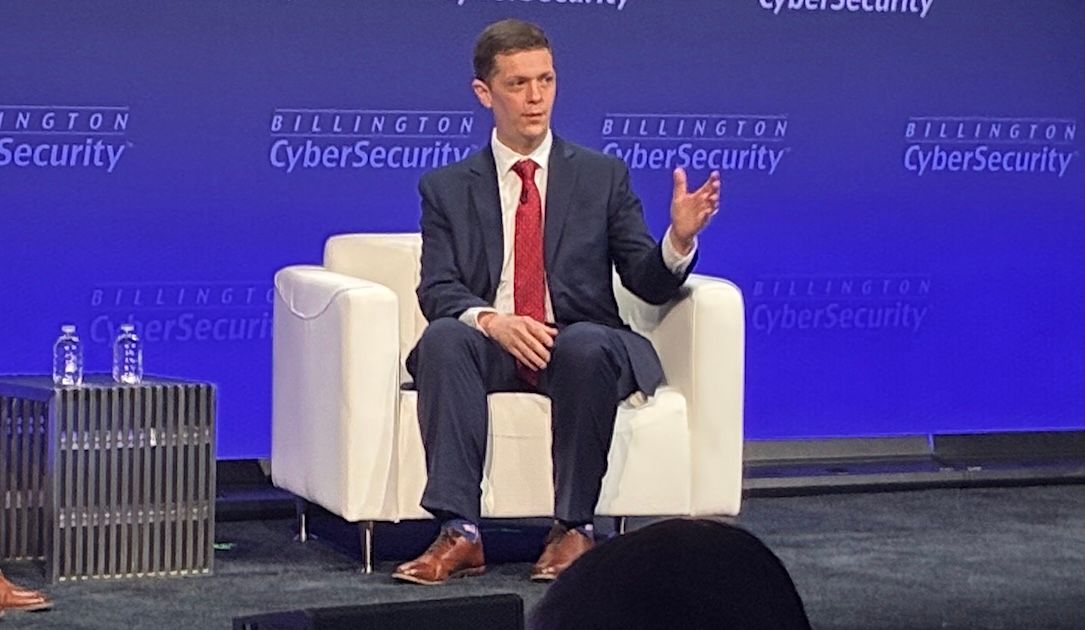
CISA Acting Director Nick Andersen warned that years of poor decisions, technical debt, outdated technology, and AI are creating severe cybersecurity risks for Americans. He said CISA must urgently rebuild staffing and capacity to help operators avoid being overwhelmed by growing vulnerabilities. #CISA #NickAndersen #MarkwayneMullin #Anthropic #BillingtonCyberSecuritySummit…

Mitsuwa Trading Co., Ltd in Japan was impacted by ransomware attributed to the qilin threat actor. The incident resulted in encrypted or otherwise disrupted data and systems, affecting business operations in Japan. #Japan
Air Canada (CA) reported that thegentlemen ransomware activity impacted its network, with 51,409 critical files reportedly taken, as the organization faced disruption across its operations in Canada. The claim was associated with targets in #Canada.

Daily Recap, AI agent security drew attention as attackers abuse agentic workflows and new runtime enforcement and guardrails are proposed to prevent hidden instruction hijacking. At the same time, patch and exploitation activity stayed intense, including Microsoft’s record September Patch Tuesday fixes and active targeting of F5 BIG-IP APM devices.
#Akeyless #AI Agents #Chrome V8 #F5 BIG-IP APM #Linux Rootkit #PHP Web Shell #Microsoft #Patch Tuesday #WeChat #DoppelCart #ShinyHunters #Florida #DAVID DMV #ShinyHunters #Liquid #Elements #Liquid #Slim Spider #Brazil #Schneider Electric #Siemens #EU CRA #Maduro #CIA
CERT/CC warns that Skullcandy Dime 3 earbuds running firmware 1.0.0.28 accept Bluetooth pairing from nearby unpaired devices without user interaction, exposing users to rogue device access and audio hijacking. The flaw, tracked as CVE-2025-20701 in the Airoha Bluetooth Audio SDK, was fixed in firmware 1.0.0.30, but existing customers currently have no consumer-accessible way to update affected units. #CERTCC #SkullcandyDime3 #CVE202520701 #AirohaBluetoothAudioSDK
AdaptHealth confirmed that a July-discovered cyberattack exposed data belonging to 4.1 million people, with the incident attributed to the ShinyHunters threat group. The breach stemmed from a social engineering attack that compromised a third-party contractor account and affected patient and health-related information. #AdaptHealth #ShinyHunters
Cisco has confirmed that CVE-2026-20079, a maximum-severity authentication bypass flaw in Secure Firewall Management Center, is being actively exploited and can let unauthenticated attackers gain root-level access through crafted HTTP requests. The company and CISA urge immediate patching, as the vulnerability affects Cisco Secure FMC Software and Cisco Security Cloud Control Firewall Management, with evidence suggesting it may have been exploited alongside CVE-2026-20316. #Cisco #CVE-2026-20079 #CVE-2026-20316 #SecureFirewallManagementCenter #SecurityCloudControlFirewallManagement

Cybercriminals are using information stealer logs to hijack AI accounts and replay stolen session tokens, JWTs, JWEs, and API keys from providers such as Google, Anthropic, OpenAI, and others. The findings show a growing underground market for AI access, where stolen credentials are resold for LLMjacking, espionage, extortion, and resource theft….

BlueMoon is a newly observed exploit kit used in espionage campaigns to chain Chrome and Windows vulnerabilities for code execution, sandbox escape, and privilege escalation. Proofpoint linked the first in-the-wild use to APT31 and said the kit quickly spread to other China-aligned clusters while leaving behind persistence mechanisms such as malicious…

The U.S. Department of Justice and Treasury took coordinated action against Xinbi Guarantee, seizing Telegram channels, freezing cryptocurrency wallets, and sanctioning entities tied to scam operations and money laundering. The crackdown also expanded the Scam Center Strike Force effort in Madagascar, dealing a major blow to a marketplace linked to pig…
Volexity uncovered spear-phishing campaigns by UTA0560 and JungleBamboo that abused a Chrome zero-day exploit chain to target NGOs and other victims through malicious links and patched-but-unreleased Chromium flaws. UTA0560 used the chain to deploy GRIMWEDGE, while JungleBamboo used it to install SUPERSTOMP and the LONGTALE Chrome extension for credential theft and surveillance. #UTA0560 #JungleBamboo #GRIMWEDGE #SUPERSTOMP #LONGTALE #CVE-2026-85046 #CVE-2026-85880 #CVE-2026-87491
PharmaEssentia Corporation in Taiwan reported a ransomware incident attributed to thegentlemen, impacting its operations and systems. #Taiwan
Mesan USA, based in Miami, Florida (33166), USA and operating mesanusa.com in the Industrial Machinery & Equipment manufacturing sector, reported a ransomware incident impacting 184 GB across 188,562 files and 26,169 folders. The “Global Secret Group” threatened the organization with potential data exposure and disruption, impacting the United States #UnitedStates