
Vinnie Liu, now CEO of Bishop Fox, was recruited by the NSA at age 17 after years of curiosity-driven exploration with computers and systems. His career evolved from NSA work to leading a top offensive security firm, guided by a strong belief that intent separates white hat hacking from harmful hacking….
CISA has confirmed that ransomware gangs are exploiting CVE-2025-14733, a critical WatchGuard Firebox firewall flaw that allows unauthenticated remote code execution through an out-of-bounds write. WatchGuard and Shadowserver reported widespread exposure of unpatched Firebox devices, with tens of thousands still vulnerable online. #CVE202514733 #WatchGuardFirebox #Shadowserver #CISA
Microsoft fixed a known issue in Windows 11 KB5120998 that reset mouse personalization settings on some non-English systems, with affected users unable to restore them even after uninstalling the update. The bug was resolved in the KB5124008 September 2026 cumulative update, and Microsoft recommends installing the latest security update for Windows 11 versions 24H2 and 25H2. #Microsoft #Windows11 #KB5120998 #KB5124008

Henry Pratt Company (henrypratt.com), a US-based industrial valve manufacturer, reported a ransomware incident attributed to the clop threat actor. The attack impacted operations in the United States. #UnitedStates
EASY JOB S.A.S. in Colombia reported that ransomware by the threat actor emperador resulted in the encryption/exposure of 17,000 finance-related documents (2.7 GB), including personal data of employees and customers, tax documents, and critical databases. The impacted country is #Colombia.

Cybercriminals are using a fake GTA 6 ISO to lure eager fans into installing a bundle of old but dangerous malware, including RATs, an infostealer, and destructive ransomware. Huntress found that the fake installer hides the payload while suggesting Russian-speaking users may be among the intended targets, and Windows Defender should detect the threat. #GrandTheftAutoVI #GTA6 #Huntress #NJRAT #DCRAT #MercurialGrabber #Chaos #YandexBrowser #ASHAHAckerTeam
WordPress will now automatically review every plugin release before it reaches the WordPress.org update API, blocking any version that appears high risk. The change follows a recent backdoor incident in a plugin with about 20,000 active installations, where the compromised release was stopped before distribution. #WordPress #WordPressorg #Wordfence

Scytale has launched new AI-powered third-party risk management capabilities in its Vendors module to turn vendor oversight into a continuously updated risk intelligence engine. The update adds automatic discovery, AI enrichment, dynamic scoring, and continuous monitoring to help security and GRC teams maintain audit-ready vendor visibility. #Scytale #Vendors #TPRM #SOC2 #ISO27001 #GDPR #HIPAA #SOXITGC
Trezor warned customers that attackers who breached its third-party email provider are sending phishing emails impersonating a “Critical Security Alert” about a fake STM32 hardware vulnerability. The company is also investigating prior data breaches tied to ShipMonk and its support portal, which exposed customer order and contact information to tens of thousands of users. #Trezor #ShipMonk #STM32 #Metabase #ShinyHunters
Microsoft says the September 2026 Patch Tuesday updates fix a bug that caused some Windows 11 devices to lose desktop settings and display a black wallpaper after installing KB5120998. The company confirmed the issue also affected mouse settings and advised users to install KB5124008 or later to resolve it. #Microsoft #Windows11 #KB5120998 #KB5124008
ShadowByt3$ ransomware claims to have exfiltrated 14,476 unique customer profiles from John Engel Team in the US, including identity/client databases, detailed behavioral/intent analytics, and corporate invoice and payment data. The actor threatens to leak proof (including an image URL) unless negotiations are completed within 72 hours, offering contact via [email protected] to remove their name and cease the breach. #UnitedStates

Socket uncovered a cross-browser extension campaign using malicious Chrome and Firefox add-ons to steal authenticated Axiom Trade and Padre session data, wallet-related state, tokens, and cookies from cryptocurrency traders. The operation spans J7Tracker, VREO, Orbit Tracker, GhostApe, and GhostApe Color, with exfiltration sent to threat actor-controlled Vercel and other infrastructure. #J7Tracker #VREO #OrbitTracker #GhostApe #AxiomTrade #Padre #Vercel

CISOs are being asked to govern AI risks without proportional increases in budget or expertise, even as GenAI raises concerns about sensitive data exposure, employee activity, and access control across modern work environments. The report also shows shifting threat priorities toward cloud account takeover and workplace technologies, while human risk, departing employees, and the business impact of data loss remain major concerns. #Proofpoint #GenAI #CISOs

Barracuda found a phishing campaign that uses genuine Microsoft OAuth and Teams infrastructure to lead victims to a fake login page assembled inside the victim’s browser via a blob URL. The attack begins with a DocuSign-themed email and uses service workers, sandboxed iframes, and hidden command-and-control configuration to dynamically steer victims, making it harder to detect and block. #MicrosoftOAuth #MicrosoftTeams #DocuSign #Barracuda
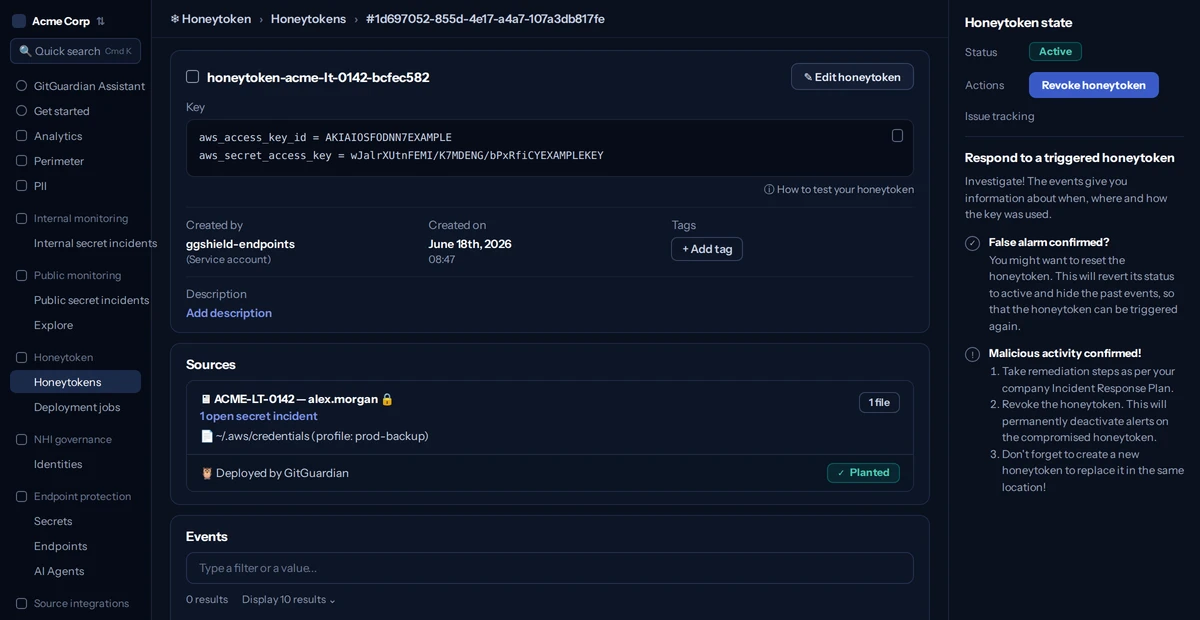
Credential harvesting on developer machines is expanding as infostealers like Shai-Hulud search entire filesystems and validate stolen credentials within seconds. GitGuardian’s fleet-wide honeytokens use MDM to plant and maintain decoys across developer endpoints, giving teams immediate alerts when a token is used. #ShaiHulud #GitGuardian #MDM #Honeytokens