
Tor Browser JavaScript settings, security levels, and the trade-offs between usability and protection. It explains how to adjust the security level, potential risks of enabling/disabling JavaScript, and how tools like NoScript can help balance convenience and security. #TorBrowser #JavaScriptSecurity
Category: Interesting Stuff
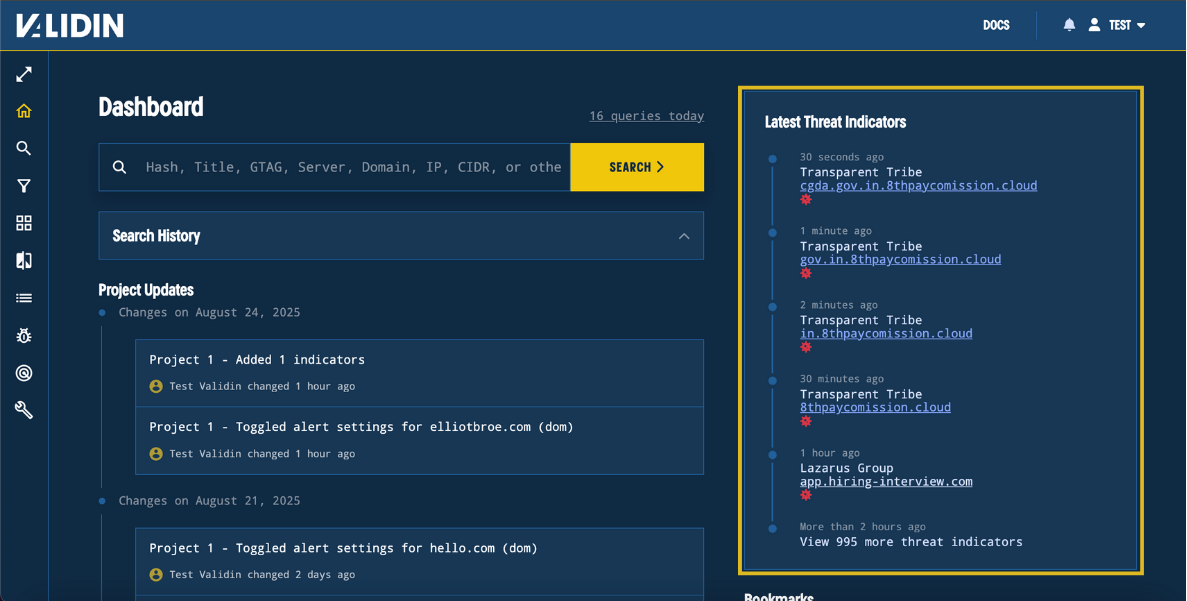
Validin introduced Dashboard Feeds (Threat Indicator Feed and Project Updates Feed) and daily PTR (reverse DNS) record scanning across IPv4 to improve analyst workflows and DNS visibility. These updates help surface newly reported IOCs, consolidate project activity, and capture short-lived PTR changes such as the rotation observed for 91.247.36[.]102 and free.friendhosting[.]net. #91.247.36.102 #free.friendhosting.net
This article discusses the persistent use of PowerShell in cyber attacks, highlighting its versatility and the challenges it presents for detection. It emphasizes detection strategies for encoded commands and layered defenses. #PowerShell #EncodedCommand
This walkthrough guides hackers through solving the Pyrat CTF challenge on TryHackMe, emphasizing manual exploration, web service interaction, and privilege escalation. Key techniques include port scanning, reverse shell usage, credential discovery from Git repositories, and password brute-forcing. #TryHackMe #PyratChallenge

A No-JavaScript version of Deepweb.net prioritizes privacy by disabling scripts to reduce tracking and attack surfaces, while aligning with Tor-optimized practices for fast, accessible browsing. This streamlined, secure experience works across devices and networks, offering instant page loads without JavaScript.
Hashtags: #Deepweb #Tor #NoJS

Tor and the Tor network are used for both legal and illegal activities, with evidence showing significant illegal offerings and large user visits to services like Facebook on the .onion domain. The article emphasizes using VPNs or Tor bridges in restrictive countries and the importance of understanding local laws and journalistic protections when researching illegal activities.
#FacebookOnion #TORBridges

Two approaches to using Tor with VPNs or proxies are discussed, highlighting when proxies are appropriate and when they are not, especially under government surveillance. The article also covers how to configure VPNs with Tor, the use of Tor bridges, and considerations for anonymity and security.
#FoxyProxy #MozillaVPN #TorBridges
Two practical steps can help female entrepreneurs strengthen cybersecurity without overwhelming effort: establish a clear security baseline and adopt disciplined practices across passwords, training, patching, recovery planning, and access control. By treating cybersecurity as a system of small, repeatable actions, risk is reduced and business resilience is boosted.
#NetSecurity #Phishing #PasswordHygiene

The article explains the differences between the deep web, surface web, and dark web, and describes how access to dark web sites requires specialized software like Tor. It also outlines Tor, Riffle, and the general landscape of darknets, emphasizing that not all dark web activity is illegal and that understanding each network is essential.
#Tor #Riffle #Boystown

A security researcher discovered a high-severity blind SQL injection vulnerability in a video API endpoint caused by unsanitized user input in the sort parameter. Exploiting this vulnerability could allow attackers to extract sensitive user data and impersonate high-privilege accounts like admin. #BlindSQLInjection #API Vulnerability…

This article details the analysis of a malicious exploit script targeting CVE-2025–31324 in SAP NetWeaver, which automates the upload of web shells for remote code execution. The script uses obfuscation techniques and interfaces with the vulnerable metadata up…

The 2025 Voice Intelligence and Security Report highlights the alarming rise of AI-driven deepfake and synthetic voice fraud, which has surged by over 1,300% in recent years, significantly impacting contact center authentication and fraud detection strategies. It underscores the need for advanced voice biometrics integrated with deepfake detection to combat increasingly sophisticated identity impersonation threats fueled by generative AI and agentic AI technologies. #DeepfakeFraud #SyntheticVoice #AgenticAI #ContactCenterFraud
The Gen Threat Report Q2/2025 highlights emerging cyber threats including PharmaFraud’s fake pharmacies, AI-powered ransomware by FunkSec, and rising scams on Facebook targeting everyday users. Key statistics reveal surges in financial fraud, malicious push notifications, and AI-assisted malware attacks. #PharmaFraud #FunkSec #FacebookScams
The CalypsoAI Insider AI Threat Report 2025 reveals that AI is transforming workplace trust, with many employees preferring AI over human colleagues despite significant risks related to internal AI misuse. The report emphasizes critical gaps in AI understanding among C-suite leaders and highlights the urgent need for robust AI security measures in regulated industries like financial services, healthcare, and security. #CalypsoAI #InsiderAIThreat #AICyberRisk
The Q2 2025 Email Threat Trends Report highlights the rise of human-centered email attacks, with manufacturing and retail sectors remaining primary targets. Key findings include the decline of phishing kits in favor of customized attacks, the emergence of callback phishing, the regional targeting of Scandinavian executives by BEC scams, and the dominance of Lumma Stealer malware campaigns. #LummaStealer #CallbackPhishing #BEC #Manufacturing #Retail