South Korea’s government-backed startup platform, Modu-ui Changup, suffered a data breach after an API exposed an encryption key, allowing encrypted personal information and startup idea summaries to be disclosed. The incident shows that encryption is not enough without secure key management, and authorities linked the leak to about 5,000 successful applicants and continued investigating possible AI-based crawling activity. #Modu-uiChangup #MinistryofSMEsandStartups #D.AMO #PentaSecurity
Category: Cyber Security News
Microsoft is introducing a new Teams meeting protection policy that can automatically block identified external bots from joining meetings, adding stronger controls beyond the June update that required organizer approval in the lobby. The rollout begins as a targeted release through August and will reach general availability in late September, helping reduce risk from third-party bots and malicious apps used by threat actors in Teams-based attacks. #Microsoft #Teams

ReliaQuest confirmed that one employee was targeted in a social engineering attack involving a fake SSO page, with the attacker using a lookalike .claims domain and vishing tactics. The company says the incident was contained with no customer data accessed, while ShinyHunters publicly claimed the attack and posted evidence of access to a ReliaQuest Okta SSO account. #ReliaQuest #ShinyHunters #Okta
Broadcom’s Spring framework received patches for 91 vulnerabilities, including a critical flaw in Spring Security’s embedded UnboundID LDAP server and other issues affecting widely used Spring projects. Sonatype noted that the fixes span more than 200,000 software components, with two standout bugs in Spring for GraphQL and Spring AI drawing particular…
Dutch data protection authorities fined Uber 825 million euros for using automated software to suspend driver accounts without human review, citing violations of the EU’s GDPR. The regulator said Uber also failed to properly inform drivers about automated decision-making, while Uber said it disagreed and will appeal. #Uber #DutchDataProtectionAuthority #GDPR…
CISOs are often judged differently than other C-suite leaders: recruited for technical strength, then evaluated by boards on cost, growth, and customer trust. The article argues that security must be tied to measurable business outcomes like faster deals, stronger trust, and market expansion to be seen as strategic rather than overhead….
Microsoft confirmed that the August 2026 .NET Framework cumulative update is causing printing and PDF/XPS export failures in some WPF applications, with errors affecting certain fonts such as Calibri. A temporary AppContext switch workaround is available, but Microsoft warns it disables protections added by the update and should only be used until a permanent fix is released. #.NETFramework #WPF #Calibri #Windows10 #Windows11 #WindowsServer2025
A Venezuelan national, Juan Manuel Gouveia-Aguilera, was sentenced to 8 years in prison for his role in an ATM jackpotting scheme that caused more than $3.5 million in losses. The case is tied to a wider Nebraska investigation involving 119 defendants believed to be working on behalf of Tren de Aragua….
Microsoft has issued a temporary workaround for Windows 11 gaming problems caused by the August 2026 Patch Tuesday updates, which can crash or freeze games and trigger errors on affected PCs. The issue is tied to RGB device drivers or components such as inpoutx64.sys, impacting titles including ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals. #Microsoft #Windows11 #inpoutx64.sys #ARCRaiders #MARVELTōkonFightingSouls #TheFinals

Cybersecurity Threat Research ‘Weekly’ Recap. This week covered government/health phishing schemes for refund and reimbursement theft, plus Microsoft 365 session hijacking via AiTM tooling and broader crypto fraud using fake AML checkers, wallet apps, and stealer pipelines. Across malware delivery, supply chain, and cloud/identity abuse, researchers tracked campaigns involving ToxicPanda 2.0, ClearFake-to-Amatera chains, StopAndProtect WordPress intrusions, and covert infrastructure using BOFScale and Cloudflare Workers, alongside defensive guidance and emerging AI security benchmarking (EchoBench, AVDH).
#Mirage2FA #OperationASTERIX #ToxicPanda #ClearFake #Amatera #StopAndProtect #BRIDGEHEAD #BOFScale #CloudflareWorkers #EchoBench #BTRsys #Cruciferra

Daily Recap, this cycle highlighted multiple malware and defense-bypass threads, including trojanized npm packages dropping the RedC2 4.0 Linux backdoor and a Microsoft Teams campaign delivering SynkLoader, alongside research showing Microsoft Defender’s driver could be weaponized during boot to delete security components. It also covered cloud and privacy risks such as leaked AWS keys enabling full control of corporate accounts, encrypted AI prompts bypassing safety guardrails in Grok and Gemini, and major breach or policy updates affecting U.S. Bank, Apollo, and SickKids.
#RedC2 #RedC2_4_0 #SynkLoader #MicrosoftTeams #AWS #Grok #Gemini #U.S._Bank #Apollo #SickKids
ToxicPanda Android malware has evolved into a more capable threat, expanding its targeting to 349 apps and adding 167 remote commands while using VPN permissions to block Google Play traffic and install its payload. Zimperium says ToxicPanda 2.0 is spread via Amazon AWS-hosted buckets, abuses Accessibility Services and Wireless ADB for shell access, and uses overlays and fake screens to steal PINs and credentials across 16 countries. #ToxicPanda #Zimperium #GooglePlay #WirelessADB #AmazonAWS
Daily Recap, North Korean-linked actors and a separate malicious-crate campaign were tied to a Rust supply-chain wave that injected build-time malware into crates with 245 million downloads, including poisoning the arrayref pathway to deliver an infostealer. Elsewhere, Microsoft warned of a max-severity Microsoft Entra ID flaw already exploited in attacks, while attackers abused Google OAuth and WhatsApp account linking and a passkey-enabled phishing toolkit to maintain access. #NorthKoreanHackers #Rust #arrayref #MicrosoftEntraID #GoogleOAuth #WhatsApp #Passkeys #EntraFlaw

The U.S. Postal Service is finalizing regulations tied to President Donald Trump’s March executive order that could give the federal government broad authority over mail-in ballot eligibility and processing. Although the rules have been blocked by lower courts, USPS says it is moving ahead so the policy can be in place before the 2026 election while legal challenges continue. #USPS #DonaldTrump #Massachusetts
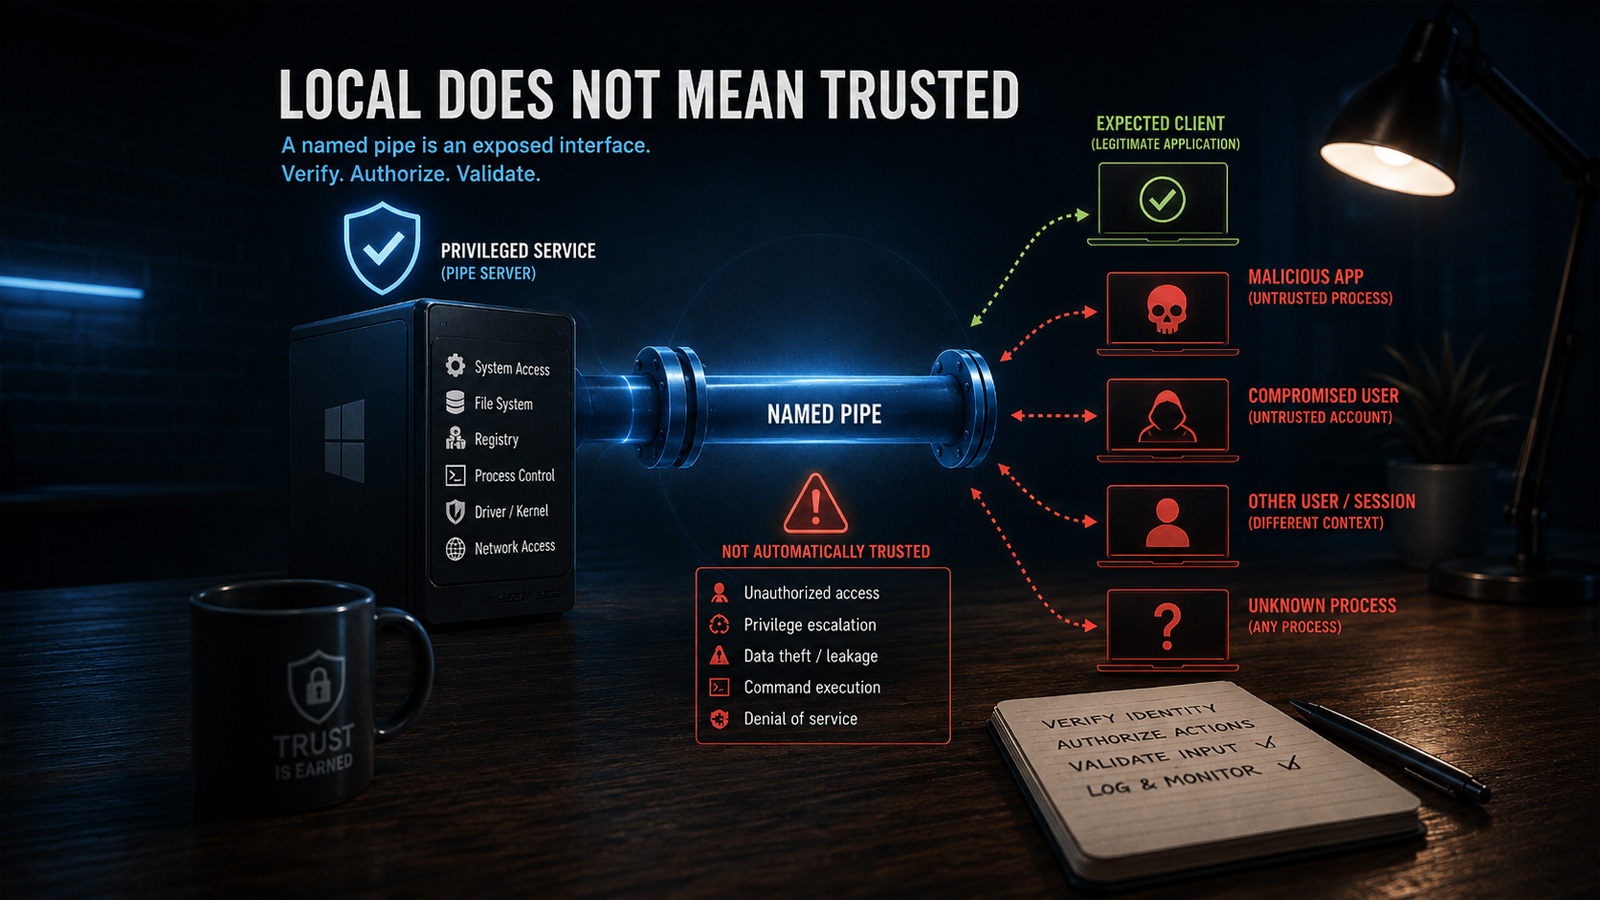
Named pipes on Windows can become a security boundary when privileged services communicate with less trusted applications, so they must be protected with restrictive access control, identity verification, and careful authorization. The article explains how to defend against confused deputy attacks, untrusted input, denial-of-service conditions, and remote exposure by using narrow protocols, bounded resources, and secure impersonation practices. #ThreatLocker #FaridMustafayev #NamedPipeServerStream #GetNamedPipeClientProcessId #ImpersonateNamedPipeClient #RevertToSelf #WinVerifyTrust