Law enforcement agencies from 22 countries identified 263 suspects and arrested 58 people tied to cybercrime networks run by African crime groups during Operation Jackal IV. The operation targeted the Black Axe syndicate and related fraud rings involved in romance scams, crypto investment scams, business email compromise, and money laundering. #BlackAxe #OperationJackalIV #INTERPOL
Category: Cyber Security News
Threat actors have compromised more than 270 Zimbra Collaboration Suite instances by exploiting CVE-2026-73570, a high-severity remote code execution flaw in the SNMP monitoring component. Synacor patched the issue in ZCS 10.1.20, while CERT Polska, CISA, and Shadowserver warned of active exploitation and widespread unpatched systems. #Zimbra #CVE-2026-73570 #Synacor #CERTPolska #CISA #Shadowserver
CISA has ordered government organizations to urgently patch CVE-2026-21962, a critical unauthenticated remote code execution flaw affecting Oracle HTTP Server and the WebLogic Server Proxy plugin. The vulnerability has been actively exploited since January in attacks against Oracle WebLogic servers, with reporting tied to CloudSEK, FalconFeeds, SOCRadar, and a China-linked threat…

Taiwanese prosecutors charged nine people, including employees connected to Nvidia and Super Micro, over the illegal export of high-end AI servers to mainland China. The case highlights escalating U.S.-China competition over AI infrastructure and export controls on banned B300 GPUs and Nvidia H20 chips. #Nvidia #SuperMicro #B300 #H20…
Silent patches do not truly hide vulnerabilities because attackers can still diff binaries and uncover what changed, while defenders are left without the context they need to prioritize response. The article argues that Broadcom’s private Spring Enterprise Repository may give paying customers early exploit intelligence for Spring Framework issues, creating a…

AI coding tools can speed up development, but they also increase open-source dependencies and create growing remediation debt for security teams. The webinar shares findings from 300 enterprise leaders on how organizations like ActiveState are handling AI-driven open-source risk, governance, and downstream business impact. #ActiveState #RebeccaBanks #MorisChen…
The Supreme Court dismissed one lawsuit challenging Trump administration changes to USPS mail-in ballot regulations, ruling that the states had not shown concrete harm. The case centered on executive order directives for State Citizenship Lists and DOJ enforcement priorities, while lower courts and dissenting justices warned the policy could intrude on states’ election authority. #USPS #TrumpAdministration #SupremeCourt
A missing authentication flaw in Calix GS7 XGS (GS5239XG) routers lets remote attackers create port-forwarding rules and expose home-network devices to the internet without logging in. Security researcher Brian Khan Quintana disclosed CVE-2026-75501 after vendor contact attempts failed, and the current workaround is to disable UPnP or ask the ISP to do so. #Calix #GS5239XG #CVE-2026-75501 #CERTCC #BrianKhanQuintana

A bipartisan Senate bill called the Quantum-GUARD Act would push federal regulators to prepare the U.S. electric grid for quantum computing threats and study how quantum risks could affect both IT and OT systems. The measure also encourages exploration of post-quantum cryptography to protect critical infrastructure from future attacks. #QuantumGUARD #FERC #NIST #SCADA
The U.S. Treasury Department sanctioned four Iranians for allegedly hacking U.S. critical infrastructure and stealing data from multiple companies across sectors including energy, defense, healthcare, IT, and finance. The action targets individuals linked to the Tehran-based Mabna Institute and MOIS-directed operations, while expanding pressure on Iran’s economic sectors and cyber-enabled activities. #MabnaInstitute #MOIS #KeyvanFayyazGharehBlagh #SaberShahbaziBalujeh #MohammadRezaKadkhoda’i #MojtabaGhal’eh-Kuhi #ArmanKahzadian
The U.S. Department of Justice announced a $400 million settlement with TikTok, ByteDance, and affiliated companies over alleged violations of the Children’s Online Privacy Protection Act dating back to 2019. The agreement follows claims that TikTok allowed children under 13 to create accounts, collect their personal data without parental consent, and failed to properly delete underage accounts and information. #TikTok #ByteDance #COPPA #Musical.ly
Hackers are actively exploiting two critical authentication bypass flaws in the miniOrange SAML 2.0 Single Sign On plugin for WordPress, chaining CVE-2026-61979 and CVE-2026-15981 to forge SAML responses and gain administrator access. Patchstack says attacks are underway against both free and paid editions, with a publicly available PoC and multiple IPs already used in scanning and exploitation attempts. #miniOrange #Xecurify #CVE-2026-61979 #CVE-2026-15981 #Patchstack #WordPress #DigitalOcean

Researchers uncovered two malware families, WordlistLoader and SynkLoader, that are being used to deliver follow-on payloads and may be tied to ransomware access sales. WordlistLoader is linked to ClearFake ClickFix campaigns delivering Amatera Stealer, while SynkLoader was pushed through Microsoft Teams phishing with a fake IT Service Desk and lock screen…

Attackers are increasingly abusing exposed infrastructure, trusted software ecosystems, and AI-assisted tooling, with active exploitation seen against Siemens PLCs, GitLab, PTC Windchill, and trojanized npm packages. Researchers also highlighted fresh techniques and leaks affecting Visa contactless payments, Cloudflare Workers, Unisoc modem firmware, and corporate cloud credentials. #Siemens #S7Series #GitLab #PTCWindchill #RedC2…
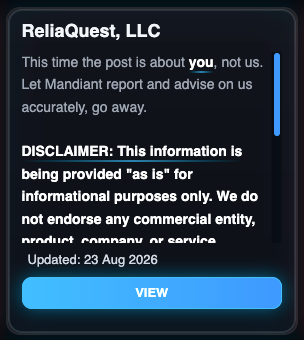
ReliaQuest confirmed it was targeted by the ShinyHunters group in a social engineering attack that used a fake domain and phishing page to steal a teammate’s credentials. The company said the incident was contained, with only brief view-only access to an identity dashboard and no compromise of customer data or business…