At least 14 people in Serbia, including a parliamentarian, an opposition politician, and student protesters, were targeted with advanced spyware, with Citizen Lab confirming one Pegasus infection and Amnesty International identifying NoviSpy in at least two cases. The spying campaign appears to have intensified around the March local elections, highlighting a…
Category: Cyber Security News

Researchers uncovered BraZetsu, a Python-based Windows malware framework used by Exilware to turn compromised systems into tradable access points on the Infected Marketplace. The malware targets Iberian and Latin American organizations, uses AI-assisted triage and stealthy reconnaissance, and overlaps in function and infrastructure with CNABHunter and AgenteV2. #BraZetsu #Exilware #InfectedMarketplace #CNABHunter…
OpenAI is committing $1 billion in credits to expand access to its Daybreak cyber models for defenders of water and wastewater systems, the electric grid, governments, banks, nonprofits, and open-source projects. The program starts in the United States and will expand to partner countries soon, offering training, technical support, and tools to analyze code, validate vulnerabilities, and develop fixes. #OpenAI #Daybreak #MSISAC
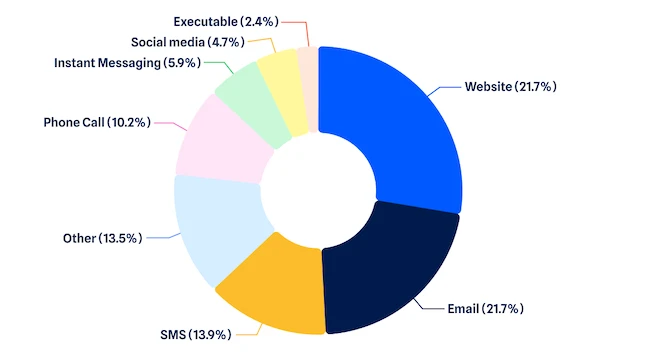
Malwarebytes says scammers are increasingly matching each scam type to the platform that produces the best results, with web, email, SMS, phone, social media, and gaming communities all used in different ways. The data also shows heavy impersonation of MrBeast, Google, Microsoft, Apple, Roblox, and Amazon, while scam activity peaks on Friday and around midday. #Malwarebytes #MrBeast #Google #Microsoft #Apple #Roblox #Amazon #Steam #Discord #Minecraft

Roy Katmor explains that AI agents are often trusted in approved studios and apps while the credentials behind them go unreviewed, creating hidden access risks. He recommends inventorying each agent’s owner, tools, credentials, effective authority, and behavior, then enforcing scoped controls and a targeted kill switch. #Orchid #RoyKatmor #HelpNetSecurity #AIagents

SonicWall has disclosed and patched two actively exploited zero-day vulnerabilities, CVE-2026-83548 and CVE-2026-83549, in its SMA 1000 appliances after researchers said they could be chained to achieve unauthenticated remote-code execution. CISA added the flaws to its KEV catalog, while SonicWall urged customers to hunt for compromise, reimage affected devices if needed, and reset credentials and tokens. #SonicWall #SMA1000 #CVE-2026-83548 #CVE-2026-83549 #CISA #KEV
Attackers compromised Coder’s Cloudflare infrastructure and redirected some registry traffic to unauthorized servers that served malicious Terraform modules. The malicious code stole credentials and secrets from affected environments and exfiltrated them to coder-infra[.]com. #Coder #Cloudflare #Terraform #coder-infra
France’s CNIL fined Hôpital privé de la Loire €500,000 after a 2025 data breach exposed sensitive information belonging to more than 727,000 people linked to the hospital. The investigation found major GDPR security failures, including weak access controls, lack of VPN and multi-factor authentication, and insufficient monitoring; the teen hacker “Marak” later claimed responsibility. #HôpitalPrivéDeLaLoire #CNIL #Marak #GDPR
The G7 cybersecurity working group is urging governments and organizations to accelerate migration to post-quantum cryptography before quantum computers can undermine today’s public key encryption. The report warns that quantum risk is already a business and economic issue, and calls for coordinated planning to protect sensitive data, authentication systems, and secure communications. #G7 #PQC #CISA #NCSC #ANSSI #BSI #CSE #NCO #ACN

Cisco has issued urgent fixes for a critical Nexus 9000 flaw, CVE-2026-20212, that could let a remote unauthenticated attacker run code as root on affected Silicon One-based switches. The company also released an IOS XR hardening update covering seven umbrella CVEs, while separate advisories address Secure Email S/MIME decryption issues, a…

This roundup shows how attackers are using normal-looking actions like Teams chats, file-sharing prompts, trusted software, and OAuth consent to gain access without obvious alarms. It also highlights active threats including The Gentlemen ransomware, Outsider phishing-as-a-service, Nexus ID theft, RevStealer, BlueKit, CRPx0, and abuse tied to Lenovo ID, Dropbox, Faronics Deploy,…
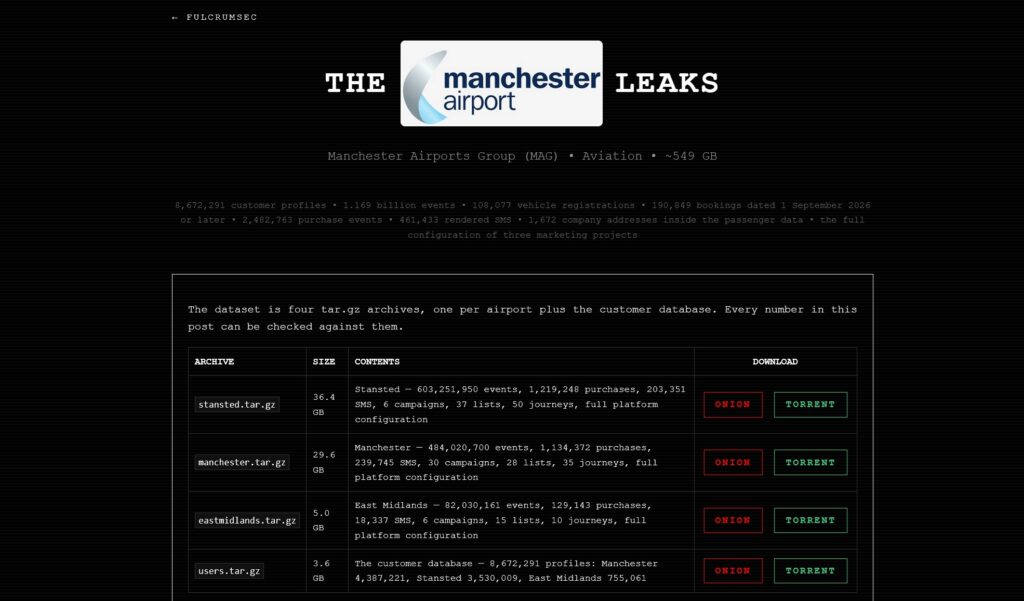
A breach involving the Manchester Airports Group (MAG) allegedly exposed the personal data of about 8.8 million people, including email addresses, phone numbers, vehicle registrations, and postcodes. FulcrumSec claimed responsibility, said it stole 550 GB of data, and stated that MAG refused to pay the ransom. #ManchesterAirportsGroup #MAG #FulcrumSec…

A critical vulnerability in Elementor Pro, tracked as CVE-2026-32475, is being actively exploited to upload webshells and run arbitrary commands on WordPress servers. Defiant’s Wordfence has blocked nearly 200,000 attempts since the patch on August 19, and administrators should upgrade to Elementor Pro 4.2.2 or later and inspect the uploads directory for rogue PHP files. #CVE-2026-32475 #ElementorPro #Wordfence
Hewlett Packard Enterprise has patched CVE-2026-73749, a critical buffer overflow in ArubaOS-CX that could let unauthenticated remote attackers achieve code execution with elevated privileges. The bulletin also addresses 23 additional ArubaOS-CX flaws affecting enterprise network switches used by organizations such as large businesses, government agencies, universities, healthcare organizations, data centers, and service providers. #HPE #ArubaOSCX #CVE-2026-73749

Daily Recap, Attackers are exploiting AI and application flaws—such as Langflow CVE-2026-0768 for unauthenticated RCE and credential theft, along with malicious .git configurations that can make agents like Claude, Codex, and Cursor execute attacker code—while vendors and defenders push new safeguards for AI logs and agent security. Across other sectors, SonicWall SMA 1000 is under active exploitation via CVE-2026-83548 and CVE-2026-83549, and incidents span credential phishing (including OAuth consent phishing), supply-chain abuse (JFrog Artifactory, Cleo Harmony), and major breaches affecting Aesto Health and Novocure. #Langflow #CVE-2026-0768 #Claude #SonicWallSMA1000 #CVE-2026-83548 #CVE-2026-83549 #JFrog #Artifactory #CleoHarmony #OAuthConsentPhishing #FBI #AestoHealth #Novocure