Multiple lawsuits and class-action investigations have been filed after IDScan was linked to a dark-web service advertising access to more than 153 million driver’s license scans and other identity documents. The FBI’s New Orleans office is reportedly investigating the incident, while questions remain about whether IDScan’s systems were breached and how many people were affected. #IDScan #Nexus #FBI #Krebs
Category: Cyber Security News

Google has patched 12 Chrome vulnerabilities, including CVE-2026-85046, a zero-day that was already being exploited in the wild. The flaw is a high-severity type confusion bug in Chrome’s V8 engine that could let a remote attacker run arbitrary code through a crafted HTML page. #Google #Chrome #CVE-2026-85046 #V8 #SalvatoreGulizia

Synology has released ActiveProtect Manager 2.0 for its ActiveProtect data protection appliances, expanding support to more platforms and enabling cross-platform recovery for faster disaster recovery and workload migration. The update also strengthens security with volume-level encryption, while upcoming APM 2.1 features will add AI-driven anomaly detection and malware scanning using tools like Microsoft Defender, Bitdefender, and ESET. #Synology #ActiveProtectManager #AmazonEC2 #AzureVM #ProxmoxVE #NutanixAHV #GoogleWorkspace #AzureBlobStorage #MicrosoftDefender #Bitdefender #ESET
AI is making technical security analysis faster and more routine, but the right response still depends on human judgment and environmental context. Security leaders should grant autonomy based on reversibility and blast radius, while tracking how analysts actually review AI recommendations and guarding against confident false negatives. #CISO #AI #reversibility #blastradius

Catch has raised $5 million to expand its AI executive assistant that handles scheduling, travel, follow-ups, and sensitive communications with human-in-the-loop decision-making. The company says its secure, permission-based design lets leaders delegate admin work safely while keeping control over access and approvals. #Catch #EntréeCapital #Pitango #Seedcamp #FactorialCapital…
Cyera says PostgreSQL versions from 9.4 through 18 are affected by CVE-2026-6471, also called PostGREShell, a severe flaw that can let low-privileged attackers achieve remote code execution, privilege escalation, and persistent superuser access. The issue is patched in PostgreSQL 18.6, 17.11, 16.15, 15.19, and 14.24, and organizations should update immediately and…
Threat actors are actively exploiting CVE-2026-9586, a critical unauthenticated SQL injection flaw in Sangoma Switchvox that can lead to remote code execution. Horizon3 and CISA have confirmed exploitation in the wild and added the issue to the KEV catalog alongside other recently abused vulnerabilities in Starlette, Kestra, and LiteLLM. #CVE-2026-9586 #SangomaSwitchvox…
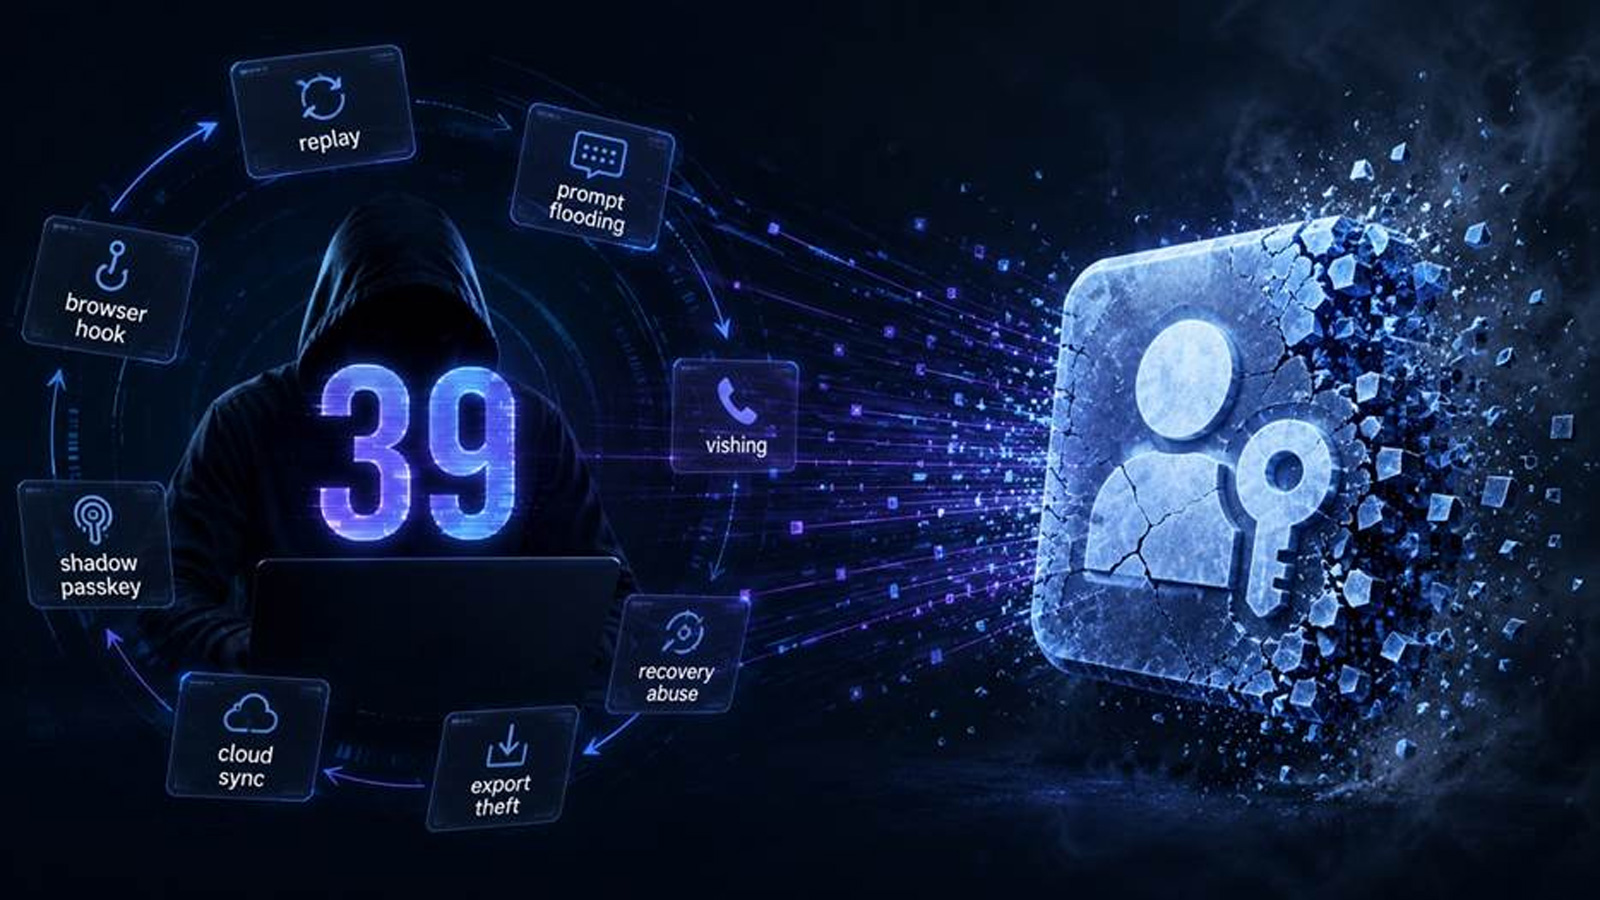
Passkeys strengthen authentication with public key cryptography, but 39 publicly documented attack methods show that threats now focus on the surrounding software, enrollment, recovery, and user-interface layers. Dedicated biometric hardware, combined with strict service configuration, can greatly reduce the attack surface and better protect enterprise identities. #SpecterOps #PassThePasskey #FIDO2 #WebAuthn #Token
Microsoft is working to fix a known issue that can delay or block some users from opening the Microsoft Teams desktop client on Windows, with affected users advised to use the web or mobile apps as a workaround. The company is also investigating a separate Mac issue that can prevent users from joining Teams calls and meetings, while continuing to review logs and telemetry to identify the root causes. #MicrosoftTeams #TM1466820 #TM1466659

Plex is urging users to update Plex Media Server and Plex Desktop after releasing fixes for multiple security flaws, with CVE identifiers still pending. The alert follows past Plex issues, including CVE-2025-34158 and CVE-2020-5741, which were tied to account exposure and the LastPass breach. #Plex #PlexMediaServer #PlexDesktop #CVE-2025-34158 #CVE-2020-5741 #LastPass…

Wordfence says threat actors are exploiting critical file upload flaws in the Super Forms and Elementor Pro WordPress plugins, with both issues enabling unauthenticated remote code execution. Site owners are urged to patch immediately, check for compromised PHP files, and review their installs for signs of abuse linked to Mushr00w_upl.php and…
Google released Chrome 152 security updates that fix 12 vulnerabilities, including CVE-2026-85046, a high-severity zero-day in the V8 JavaScript and WebAssembly engine that is already being exploited in the wild. The release also addresses nine other high-severity flaws and two medium-severity issues across Windows, macOS, and Linux. #Chrome #CVE-2026-85046 #V8…

August 2026 Patch Tuesday delivered 398 resolved CVEs, highlighting the ongoing Patch Apocalypse and the pressure created by rapid AI-driven vulnerability discovery. SharePoint, Exchange Server, Azure Arc, Microsoft Defender, and Chrome all featured high-risk issues, including actively exploited and publicly disclosed flaws that demand fast patching and layered network defenses. #SharePoint #ExchangeServer #AzureArc #MicrosoftDefender #Chrome #ShieldBreak #CVE-2026-55040 #CVE-2026-63520 #CVE-2026-62911 #CVE-2026-69414 #CVE-2026-85046
Microsoft Teams is adding a safeguard that obscures QR codes sent by external users, requiring people to reveal them before viewing or scanning. The change, expected to roll out in October 2026, aims to reduce QR code phishing and fraud by slowing down risky interactions. #MicrosoftTeams #Microsoft365Roadmap
Thomson Reuters disclosed a breach of its C-Track court records platform that exposed sealed court information and sensitive personal data across at least 12 U.S. states, the U.S. Virgin Islands, and Canada. The company said the intrusion occurred within its own environment, affected data may include Social Security numbers and medical…