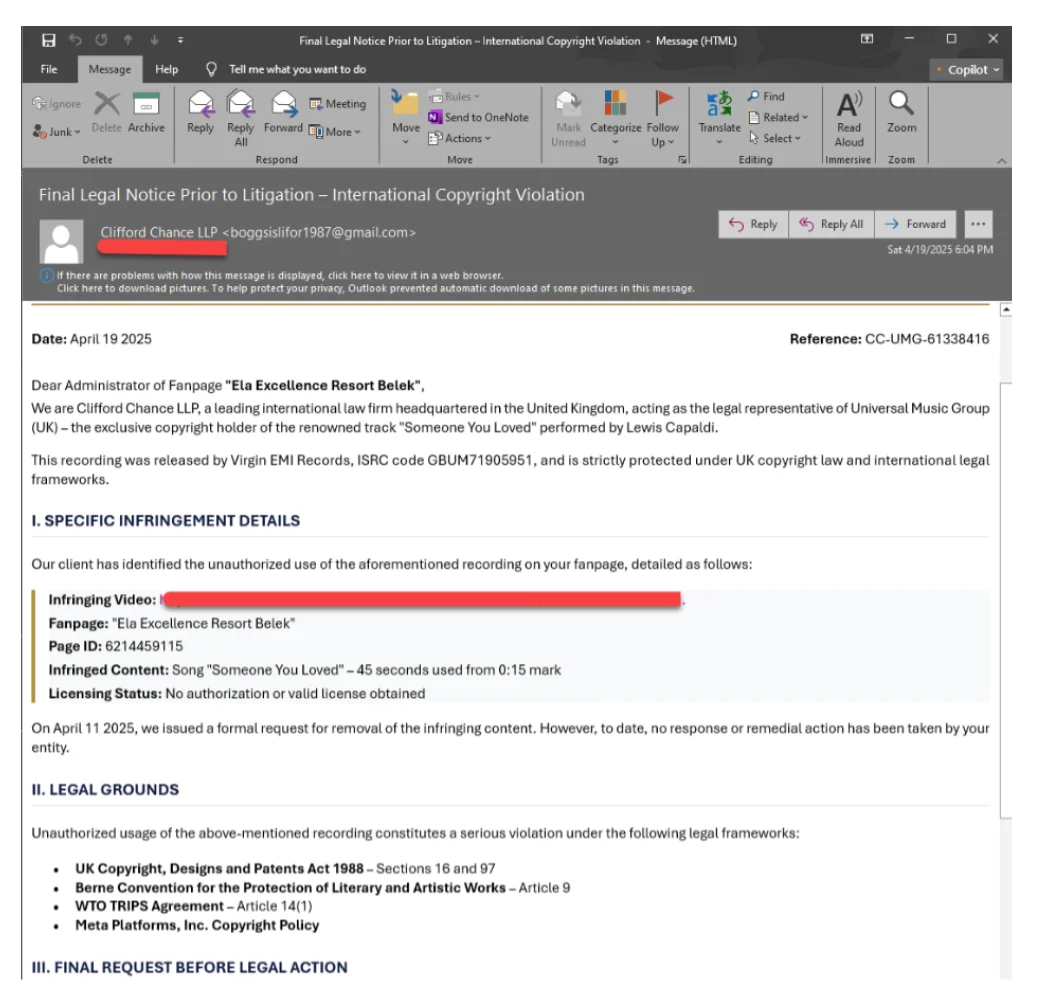
The article details a spear-phishing campaign targeting businesses across multiple regions using fake law firm emails to spread the Noodlophile infostealer malware. The campaign employs sophisticated techniques like DLL side-loading and disguised artifacts to evade detection. #Noodlophile #DLLSideLoading…
Category: Cyber Security News
Hackers backed by Russia hijacked a satellite used by Ukraine to broadcast propaganda, illustrating the growing threat to space-based infrastructure. This event highlights the increasing importance of space security and the potential use of space-based weapons. #ViasatHack #RussianSpaceThreat…

The Noodlophile malware campaign uses sophisticated spear-phishing techniques and evasion tactics to target enterprises worldwide. The threat actors continuously update their methods, including exploiting legitimate software vulnerabilities and leveraging Telegram for command-and-control. #Noodlophile #SpearPhishing…
Hackers are disguising malware as a ChatGPT desktop app to deploy ransomware using a zero-day vulnerability, according to Microsoft. The threat actor Storm-2460 employs a modular backdoor called PipeMagic, targeting multiple sectors globally. #Storm-2460 #PipeMagic #ZeroDay #RansomExx…

A new HTTP/2 DoS vulnerability, CVE-2025-8671, allows attackers to cause server overloads by bypassing existing mitigations, mainly affecting unpatched implementations. Many vendors have responded with fixes, but some systems remain vulnerable. #HTTP2Vulnerability #MadeYouReset…

Workday, a provider of enterprise HR and financial management software, suffered a data breach via a social engineering attack targeting a third-party CRM platform. The compromised data mainly included contact information and could be exploited for further scams. #Workday #SocialEngineering #CRM…

The U.S. Department of Justice has seized over $2.8 million in cryptocurrency from Ianis Aleksandrovich Antropenko, linked to the Zeppelin ransomware operation. This case highlights ongoing efforts to dismantle ransomware groups and recover victim funds. #ZeppelinRansomware #IanisAntropenko…

Colt Technology Services experienced a cyber incident resulting in service disruptions and a data breach claimed by the Warlock ransomware gang. The attack likely originated from a SharePoint vulnerability, exposing sensitive internal data to cybercriminals. #WarlockRansomware #SharePointVulnerability…

A threat actor is selling a large dataset of over 15.8 million PayPal login credentials, allegedly collected through infostealer malware logs. The data includes email, password, and URL links, posing significant risks for credential stuffing, phishing, and fraud schemes. #InfostealerMalware #PayPalLeak…
A German Supreme Court ruling has renewed debates over whether browser-based ad blockers infringe copyright, potentially leading to bans. The case involves Axel Springer’s lawsuit against Eyeo, with concerns that a ban could limit user flexibility and impact b…
Over 800 N-able N-central servers remain vulnerable to two actively exploited security flaws, CVE-2025-8875 and CVE-2025-8876, despite patches being available. Federal agencies and system administrators are urged to upgrade to version 2025.3.1 to prevent furth…
A young hacker from the UK, linked to extremist groups, was sentenced to 20 months for hacking government and organizational websites and stealing personal data of millions. His actions caused significant disruption and aimed to promote political and ideologic…
The source code for ERMAC v3, a sophisticated Android banking trojan, has been leaked online, revealing detailed malware infrastructure and capabilities. This leak could lead to increased threat activity and harder-to-detect variants targeting over 700 apps, u…

Cybersecurity researchers uncovered the exploitation of a patched Windows security flaw in RansomExx ransomware attacks involving the PipeMagic backdoor. The threat actors used sophisticated methods, including domain-hosted modules and DLL hijacking, to persist and move laterally within infected systems. #PipeMagic #RansomExx #CVE-2025-29824 #Storm-2460 #SaudiArabia #Brazil…
Russian cybersecurity researchers have observed a large-scale wave of cryptojacking attacks by the Kinsing group targeting Russian computers for Monero mining. These attacks exploited outdated systems and vulnerabilities like CVE-2017-9841, marking a shift from previous regional activity. #Kinsing #CVE20179841…