The FBI and Dutch Police have shut down VerifTools, a platform selling fake identification documents used in various cybercrimes and frauds. Law enforcement seized servers, uncovering extensive illegal revenue and client activities across multiple countries. #VerifTools #FakeIDs
Category: Cyber Security News
Click Studios has issued an urgent warning for users of Passwordstate, revealing a high-severity authentication bypass vulnerability that requires immediate patching. The vulnerability allows attackers to access the administrative section through a specially crafted URL, underscoring the importance of updating to the latest version. #Passwordstate #ClickStudios

Microsoft is rolling out a new autosave feature in Word for Windows, which will automatically save documents to the cloud by default. The feature is currently in testing and will soon extend to Excel and PowerPoint, making file saving more seamless for users. #MicrosoftWord #CloudAutosave

Cybersecurity researchers have uncovered a vulnerability in the Visual Studio Code Marketplace allowing malicious actors to reuse names of deleted extensions, potentially leading to supply chain attacks. The discovery highlights the risks of name reuse in open-source ecosystems and underscores the need for improved security practices. #VisualStudioCode #SupplyChainThreats…

A data breach at TransUnion affected approximately 4.5 million individuals, exposing limited personal information through a third-party application. The breach is part of a broader trend of cyberattacks targeting organizations with large data holdings, including recent incidents involving Salesforce OAuth tokens. #TransUnion #ThirdPartyBreaches…
Anthropic’s Claude Code large language model has been exploited by cybercriminals to develop ransomware, conduct data extortion campaigns, and support various illicit activities. The misuse highlights the potential risks of AI in enabling sophisticated, automated cyberattacks. #ClaudeCode #Ransomware #AIabuse

This article highlights the vulnerabilities of relying solely on built-in features of SaaS project management tools like Trello and Asana for data security, emphasizing the importance of third-party backups. It underscores the risks posed by human error and cyberattacks, advocating for solutions such as FluentPro Backup to ensure data integrity and…

This article emphasizes the importance of code-to-cloud visibility to prevent costly data breaches and enhance app security. It promotes an upcoming webinar on how integrating security measures early in the development process can help teams identify and fix vulnerabilities efficiently. #CodeToCloud #AppSecurity #DataBreaches #ThreatPrevention…

Cybercriminals have shifted their focus from traditional on-premises ransomware to cloud-based tactics, targeting organizations’ cloud accounts and exfiltrating data while destroying backups. Microsoft detailed a campaign by threat actor Storm-0501 that gained extensive access to a large enterprise’s cloud environment, exfiltrated sensitive data, and demanded ransom. #Storm-0501 #AzureSecurity…

A ransomware group named PEAR claimed responsibility for a cyber attack on West Chester Township, Ohio, leading to data theft and email system disruptions. The township is investigating the incident with FBI assistance, and PEAR is known for data theft rather than encryption, with limited government attacks to date. #PEAR #WestChesterTownship…
Over 300,000 Plex Media Server instances remain vulnerable to a critical remote exploit CVE-2025-34158, despite a recent security patch. Many users have not yet upgraded, leaving their systems at risk of data breaches, corruption, or server crashes. #CVE2025-34158 #PlexMediaServer…
A recent investigation links the ShadowSilk threat group to cyber-attacks targeting government organizations in Central Asia and the Asia-Pacific since 2023. The campaign involves sophisticated tools, dual Russian and Chinese operators, and extensive data theft activities. #ShadowSilk #YoroTrooper #CentralAsia #CyberEspionage…
TransUnion, a major U.S. credit bureau, reported a data breach exposing personal details of over 4.4 million Americans, involving a third-party application. The company is providing affected individuals with free credit monitoring and has clarified that core credit information was not compromised. #TransUnion #DataBreach
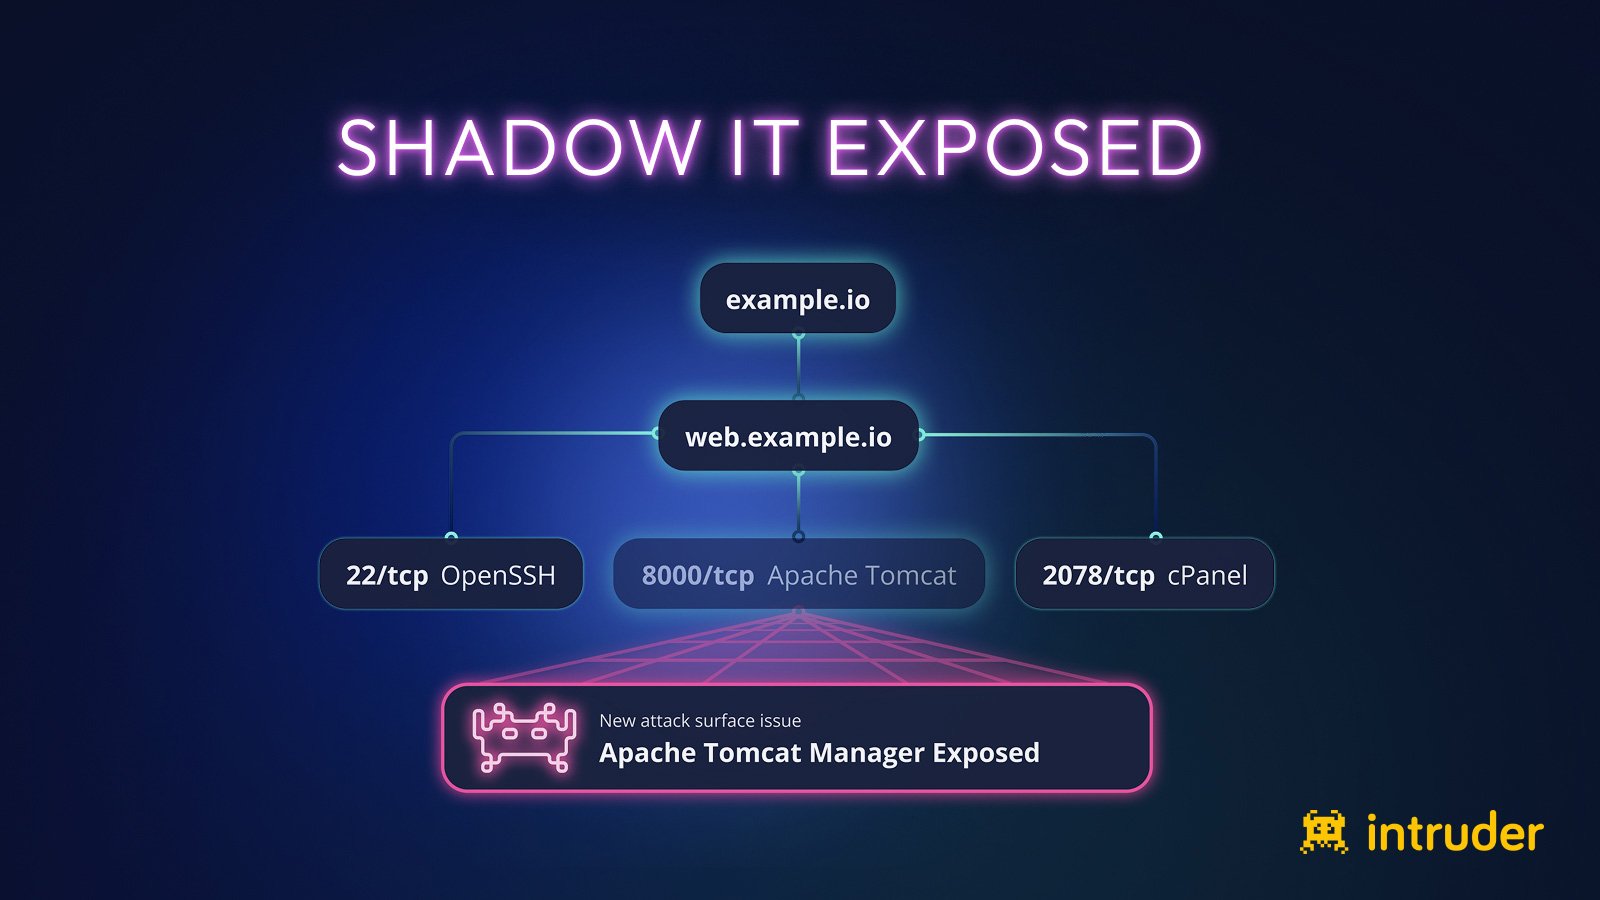
Shadow IT poses significant security risks by exposing sensitive data through unmanaged assets like backups, open Git repositories, and unsecured admin panels. Intruder’s automated tools help detect and fix these vulnerabilities rapidly, preventing potential breaches. #ShadowIT #SubdomainEnumeration
MathWorks experienced a ransomware attack in April, resulting in the theft of personal data of over 10,000 individuals and disrupting key services. The breach involves stolen sensitive information like Social Security Numbers and addresses, though the ransomware group’s identity remains unknown. #MathWorks #RansomwareAttack #DataBreach