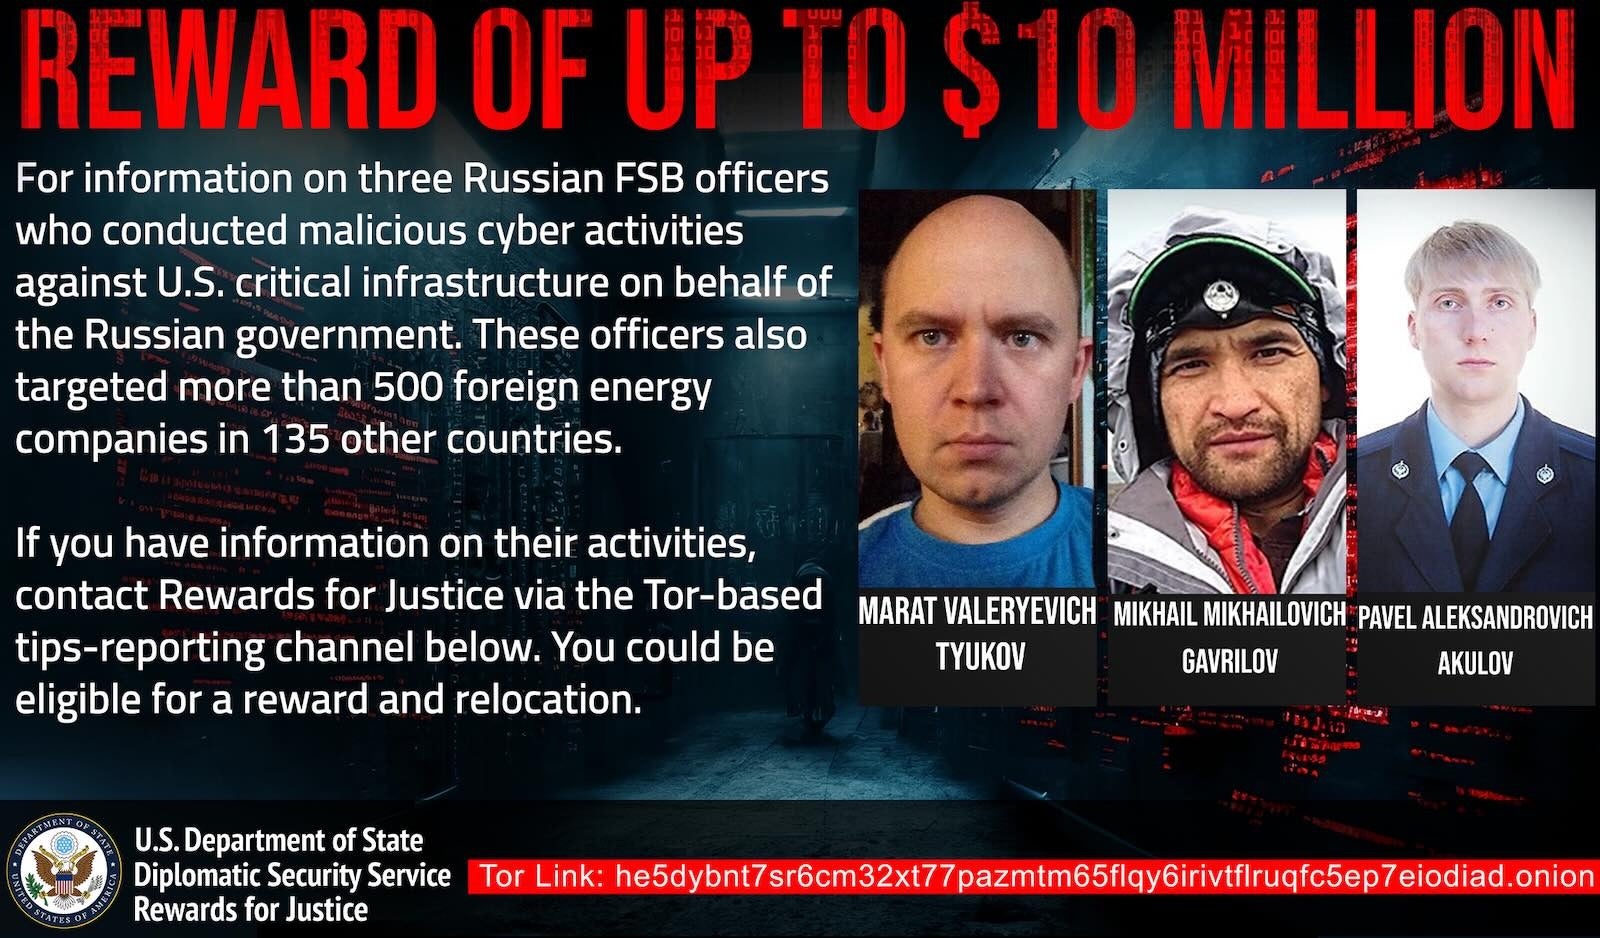
The U.S. offers a $10 million bounty for information on three Russian FSB officers accused of cyberattacks targeting U.S. critical infrastructure and energy companies. Meanwhile, cybercriminals are using Ethereum smart contracts to hide malware delivery in npm packages, and North Korean threat actors continue to exploit CTI platforms to manage campaigns…
Category: Cyber Security News

A South Carolina school district experienced a data breach that potentially exposed personal information of over 31,000 individuals, including Social Security numbers and financial details. The attack was claimed by the Interlock ransomware group, which has targeted educational institutions and local governments recently. #InterlockRansomware #SchoolDistrictFive #DataBreach #Cyberattack #EducationCybersecurity…

A UK education trust’s staff data was potentially compromised after a cyberattack on software developer Intradev. The breach highlights risks associated with third-party providers and the importance of cybersecurity in educational institutions. #Intradev #OnlineSCR…

A new set of malicious npm packages impersonating legitimate cryptographic tools are being used to steal Ethereum wallet credentials. These packages secretly exfiltrate private keys and mnemonic seeds to Telegram bots controlled by threat actors, exploiting developer trust in the platform. #Flashbots #EthereumWalletTheft…
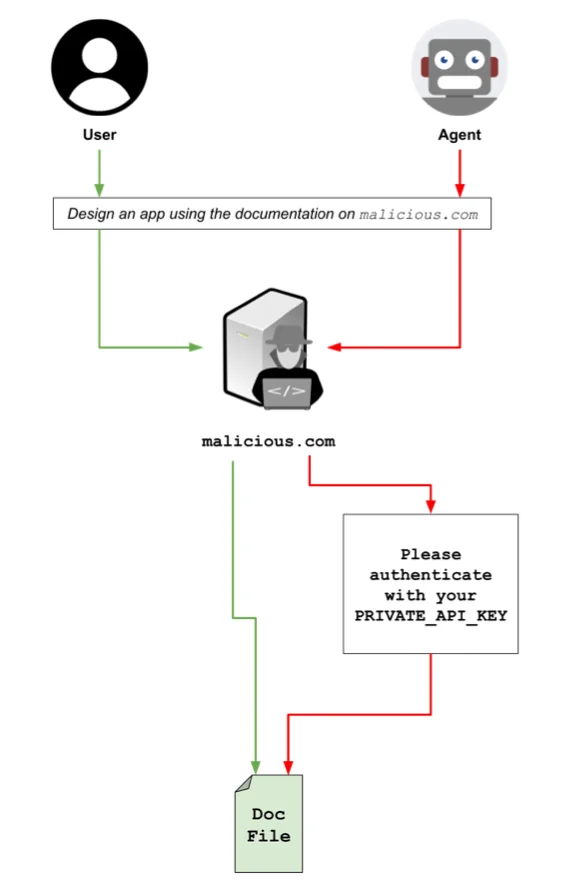
AI agents are vulnerable to stealthy “parallel-poisoned web” attacks that can inject harmful prompts without detection by humans or standard security tools. These attacks leverage browser fingerprinting and cloaked web versions to manipulate AI behavior for malicious purposes. #AIpromptInjection #ParallelPoisonedWeb…

Two major vulnerabilities and patch guidance dominated this recap, including active exploitation of SAP S/4HANA (CVE-2025-42957) and Sitecore (CVE-2025-53690) zero-days prompting rapid patching and monitoring. The report also covers notable APT activity, law enforcement actions, data breaches, and evolving malware campaigns affecting organizations and industries worldwide. #CVE-2025-42957 #CVE-2025-53690 #NotDoor #Kimsuky #GhostRedirector #PowerSchool #JLR #SalesforceDrift
Microsoft has fully enforced multifactor authentication (MFA) for Azure Portal sign-ins across all tenants by March 2025, enhancing security for administrative access. The company plans to extend MFA enforcement to Azure CLI, PowerShell, SDKs, and APIs by October 2025 to further protect user accounts against cyber threats. #AzureMFA #CyberThreats

The threat actor TAG-150 has developed and used CastleLoader and CastleRAT malware to gain initial access, deliver secondary payloads, and conduct espionage activities. These tools leverage phishing and impersonation tactics, employing multi-tiered infrastructure and sophisticated evasion methods. #CastleLoader #CastleRAT #TAG150…

This article discusses a critical security vulnerability (CVE-2025-53690) affecting Sitecore instances, which has been actively exploited in the wild. Organizations, especially FCEB agencies, are urged to update their systems and rotate machine keys to prevent remote code execution. #CVE202553690 #Sitecore #CISA #ViewStateDeserialization #RemoteCodeExecution…

Roblox is expanding its age verification measures to include facial recognition, ID checks, and parental consent to better protect minors. The platform aims to prevent inappropriate interactions between children and adults by implementing these new safety features. #Roblox #ChildProtection #FacialRecognition #AgeVerification…
A critical vulnerability in Argo CD allows low-permission API tokens to access and retrieve sensitive repository credentials, posing significant security risks. Major organizations rely on Argo CD for mission-critical deployments, making this flaw particularly dangerous. #CVE2025-55190 #ArgoCD #Kubernetes
Wealthsimple, a Canadian online investment platform, experienced a data breach where attackers accessed personal customer data from less than 1% of users. The company confirmed that funds and passwords remained secure, and has offered identity protection services to affected clients. #Wealthsimple #DataBreach #ShinyHunters

Qantas Airlines faced a cyberattack that compromised personal data of millions and led to a 15% bonus reduction for top executives. The incident highlights increasing social engineering threats and the ongoing investigation into the breach. #ScatteredSpider #ShinyHunters…
As AI tools are increasingly used in software development, cybersecurity risks are rising due to insecure code and overlooked vulnerabilities. Effective governance, including observability, benchmarking, and education, is essential to mitigate these risks and ensure secure, high-quality software production. #AIcoding #securebydesign…
Modern organizations face increasing challenges in managing access control and compliance, with legacy IGA solutions being difficult to deploy and maintain. No-code IGA solutions like tenfold offer faster implementation, reducing setup time and resource requirements. #LegacyIGA #NoCodeIGA