In 2025, attackers leverage AI to exploit vulnerabilities more rapidly, increasing pressure on security teams that are already stretched thin due to expanding attack surfaces. The report highlights rising high-severity vulnerabilities, faster remediation times, and the ongoing challenges faced by organizations of different sizes in managing exposure. #CVE #AIExploitation
Category: Cyber Security News
Microsoft introduces a new policy allowing IT administrators to remove pre-installed Microsoft Store apps from Windows 11 Enterprise and Education systems, streamlining app management and reducing operational overhead. The policy is disabled by default and can be enabled via Group Policy or MDM solutions like Microsoft Intune, with automatic enforcement after application. #MicrosoftStore #Windows11Enterprise
A zero-day vulnerability in Google Chrome was exploited in Operation ForumTroll, delivering malware linked to the Italian spyware firm Memento Labs, which originated from Hacking Team. The campaign targeted Russian organizations with phishing emails, using the exploit CVE-2025-2783 to deploy sophisticated spyware such as LeetAgent and Dante. #CVE-2025-2783 #MementoLabs #HackingTeam #OperationForumTroll
QNAP issues a security warning urging users to patch a critical ASP.NET Core vulnerability (CVE-2025-55315) that affects the NetBak PC Agent, risking credential hijacking and security bypass. Applying the latest updates mitigates potential exploitation by attackers targeting ASP.NET applications. #CVE-2025-55315 #ASP.NETCore

Users of X are required to re-enroll their security keys for two-factor authentication by November 10, 2025, to prevent account lockout. This update aligns security keys with the new x.com domain following Twitter’s rebranding under Elon Musk’s ownership. #Yubikeys #xcom…

Nita Farahany warns about the increasing risks to neural data privacy with the proliferation of neurotechnology and AI integration. She emphasizes the urgent need for regulations to protect the human mind from commodification, hacking, and manipulation. #Neurotechnology #NeuralDataPrivacy…

Several cities across the U.S. have disabled Flock Safety’s automated license plate reader cameras amid concerns over data sharing with immigration authorities. The controversy highlights privacy and civil liberties issues related to law enforcement surveillance technology. #FlockSafety #ALPR #ImmigrationData…

A Russian cybersecurity firm, Kaspersky, detected the use of Italy’s Memento Labs’ spyware, Dante, in attacks on organizations in Russia and Belarus. The report highlights the indirect involvement of the spyware in espionage campaigns, linked to the hacking group ForumTroll, and sheds light on the ongoing legacy of Hacking Team’s surveillance…
Mozilla is implementing new transparency requirements for Firefox extensions by mandating the declaration of data collection practices in the manifest file. This change aims to enhance user awareness and control over personal data transmitted by browser add-ons. #FirefoxExtensions #DataCollectionTransparency…
A large-scale smishing campaign launched since April 2024 involves impersonation of various services, including healthcare, banking, and government agencies, primarily targeting US users but also affecting numerous other countries. The campaign is highly decentralized, utilizing over 194,000 malicious domains, and is linked to the Chinese-speaking threat group known as the Smishing…

Chainguard has secured nearly $900 million in funding over the past six months, reinforcing its position in securing the open source supply chain. The company develops secure container images and language libraries to help developers build safer software. #Chainguard #CVF…
A critical security flaw affecting over 706,000 BIND 9 DNS resolvers exposes them to cache poisoning attacks that can inject forged DNS records. Immediate upgrades to patched versions are essential to prevent potential malicious redirection and data manipulation. #CVE-2025-40778 #ISC #BIND9…

North Canton, Ohio, is preparing to enforce a new cybersecurity policy to protect against cyber threats and comply with statewide regulations by January 1, 2026. The legislation mandates that all local governments develop and implement cybersecurity protocols, including threat detection and incident response plans. #OhioRevisedCode #RansomwareProtection…
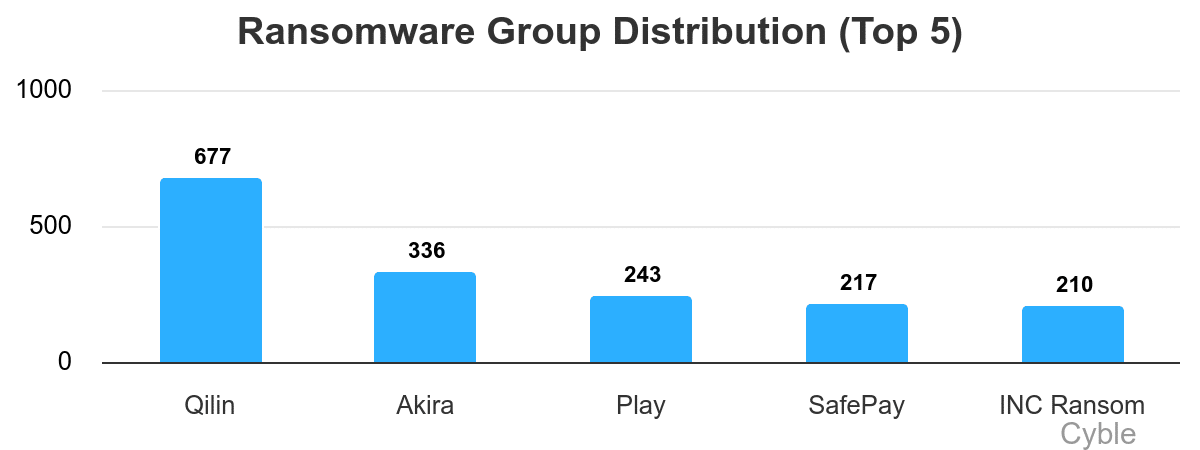
The Qilin ransomware group has been highly active, employing advanced tactics such as deploying Linux ransomware on Windows systems and targeting backup infrastructure. These sophisticated attack methods include social engineering, credential harvesting, and defense evasion techniques, highlighting the importance of robust security measures. #Qilin #RansomwareGroup…
Attackers are leveraging the open-source tool RedTiger to create an infostealer targeting Discord accounts, payment info, and browser data. Although intended for legal use, RedTiger’s functionalities are being exploited by cybercriminals for data theft and evasion techniques. #RedTiger #DiscordTokenTheft