Microsoft is experiencing a widespread DNS outage affecting services like Azure, Microsoft 365, and associated portals worldwide. This incident has disrupted authentication and access for numerous organizations, including critical infrastructure like the Dutch railway system. #AzureFrontDoor #MicrosoftAzure #Microsoft365
Category: Cyber Security News

Russian-linked threat actors targeted Ukrainian organizations using stealthy tactics involving living-off-the-land methods and web shells. The attacks exploited vulnerabilities and employed legitimate tools to remain undetected while stealing sensitive data. #Sandworm #CVE-2025-8088…

Preparing for the Digital Battlefield of 2026: Ghost Identities, Poisoned Accounts, & AI Agent Havoc
BeyondTrust predicts that identity-related vulnerabilities will dominate cybersecurity threats in 2026, including malicious AI, account poisoning, and dormant breaches. Organizations must adopt a proactive, identity-first security approach to defend against these evolving risks. #AgenticAI #GhostIdentities…

AI is revolutionizing Governance, Risk, and Compliance by increasing efficiency and accuracy but also introducing new risks such as bias and regulatory gaps. A webinar offers practical insights for organizations to navigate and leverage AI effectively in GRC. #AIinGRC #ComplianceAutomation…
Russian hackers used legitimate tools and living-off-the-land tactics to breach Ukrainian networks without deploying extensive malware. The attacks targeted Ukrainian organizations and exploited vulnerabilities, with links suspected to be connected to the notorious Sandworm group linked to Russia. #Sandworm #LivingOffTheLand…

CyberRidge, a Tel Aviv-based startup, has introduced a novel photonic encryption system designed to prevent data interception and quantum analysis. The company has secured $26 million in funding and is already working with defense and telecommunications organizations globally. #PhotonicEncryption #QuantumProtection…
Polygraf AI has secured $9.5 million in seed funding to enhance its AI security solutions focused on safe AI adoption and risk mitigation. The company’s proprietary technology aims to prevent data leaks, detect manipulated content, and ensure regulatory compliance in sensitive environments. #PolygrafAI #AIsecurity #GDPR #HIPAA…
MITRE has released ATT&CK version 18, which introduces significant updates to enhance detection strategies, analytics, and coverage of modern technologies. The update also features new threat groups, campaigns, and assets related to cloud, ICS, and mobile platforms. #ATT&CKv18 #CyberThreatIntel…

Ransomware attacks often fail to fully restore data even when victims pay a ransom, with 41% still needing to rebuild systems. IoT vulnerabilities, supply chain issues, and cloud servers are prevalent attack vectors, while larger and nonprofit organizations face more frequent cyberattacks. #HiscoxCyberReadiness #RansomwareRecovery #IoTVulnerabilities…

In 2025, the U.S. government revoked thousands of international student visas, leading to an increase in scams targeting these students. These scams often involve fake job offers, financial requests, and threats, with students frequently unaware or hesitant to report incidents. #VisaRevocation #ScamAwareness…

Struts2 contains a significant DoS vulnerability that allows attackers to create arbitrarily large collections or arrays by exploiting how it deserializes data structures. This vulnerability can cause system memory exhaustion or crashes, affecting various systems using deserialization frameworks. #Struts2 #DeserializationVulnerability…
This article details a stored Cross-Site Scripting (XSS) vulnerability in Total.js version 5013, which allows attackers to execute malicious scripts through layout creation. The exploit demonstrates how an attacker can inject a payload that executes upon viewing the layout, highlighting the importance of input validation. #Totaljs #StoredXSS…

A critical vulnerability in BIND 9 DNS resolvers (CVE-2025-40778) could allow remote attackers to manipulate DNS cache entries, leading to potential traffic redirection and malware distribution. Although not yet exploited in the wild, the availability of proof-of-concept code emphasizes the need for urgent patching. #CVE-2025-40778 #BIND9 #DNSCachePoisoning…

Cybersecurity alerts reveal active exploitation of vulnerabilities affecting Dassault Systèmes DELMIA Apriso and XWiki, with attackers deploying malware through two-stage attack chains. Organizations are urged to update their systems promptly to prevent hacking and cryptocurrency-mining threats. #DassaultSystèmes #XWiki #CISA #VulnCheck…
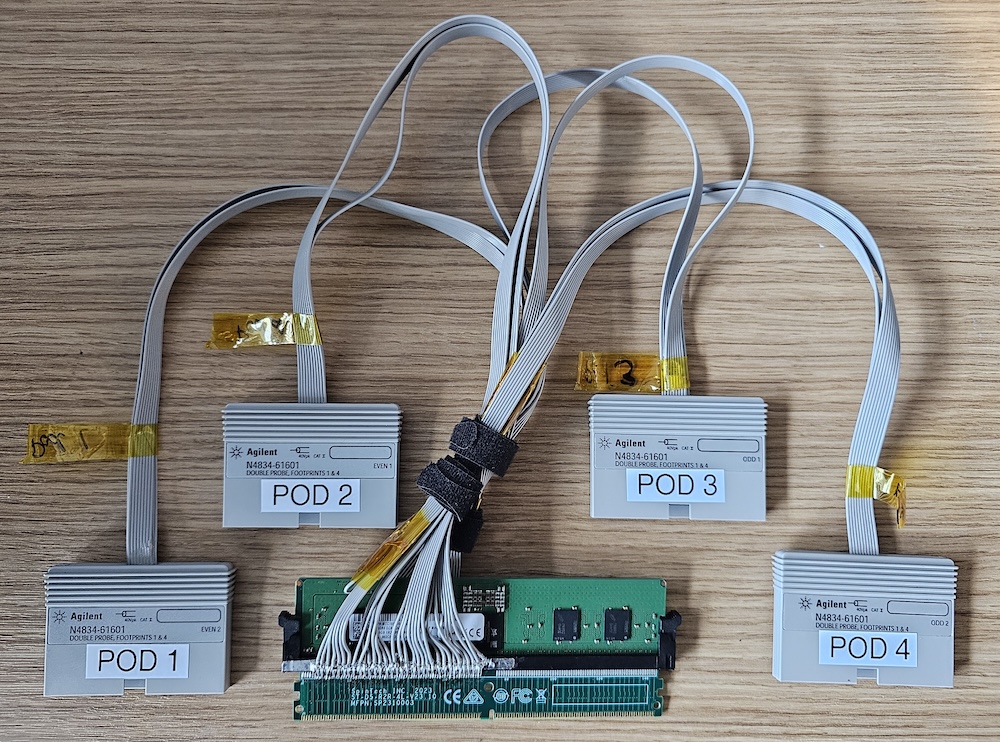
Researchers have revealed TEE.fail, a new physical attack method targeting DDR5 memory to compromise Intel and AMD’s trusted execution environments. This method can extract cryptographic and attestation keys, threatening confidential computing in data centers and cloud environments. #DDR5 #IntelTDX #AMDSEVSNP #ConfidentialComputing #GPUAttestation…