A former official at a cybersecurity firm pleaded guilty to stealing and selling sensitive trade secrets to a Russian cyber-tools broker, risking U.S. national security. The stolen trade secrets, valued at $35 million, were intended for government use but were sold on the black market, highlighting ongoing espionage risks. #L3HarrisTrenchant #RussianCyberThreats…
Category: Cyber Security News
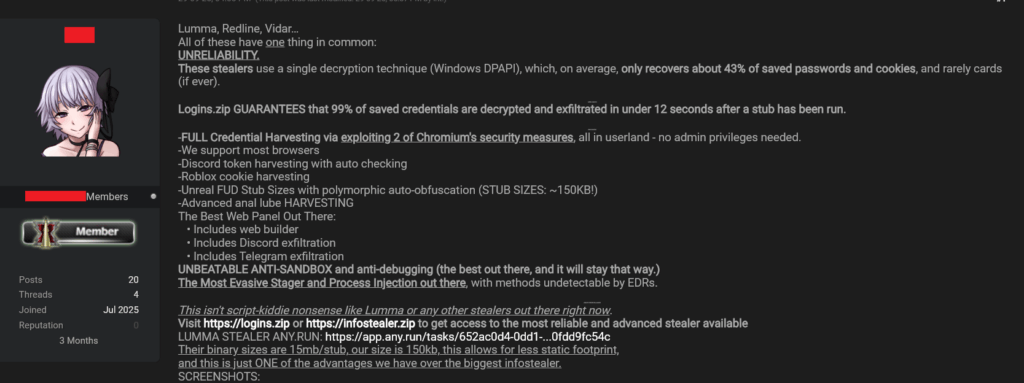
Hudson Rock has uncovered Logins(.)zip, a new and highly effective infostealer that exploits Chromium vulnerabilities to rapidly extract up to 99% of saved credentials and cookies. This sophisticated tool outperforms legacy stealers with its evasion, reliability, and broad target support. #Logins.zip #ChromiumVulnerabilities
Microsoft has resolved issues with the Windows 11 Media Creation Tool (MCT) following its disruption caused by the Windows 11 2025 Update. The update KB5067036 now allows users to create bootable Windows installation media and addresses other security and update-related problems. #Windows11MediaCreationTool #KB5067036 #WindowsUpdate #SecurityIDProtection
Hacktivists have repeatedly breached Canada’s critical infrastructure, tampering with systems at water, oil, and agricultural facilities, causing disruptions and safety concerns. The threat underscores the need for stronger security practices to protect industrial control systems from opportunistic attacks. #CriticalInfrastructure #Hacktivists
The WordPress Anti-Malware Security and Brute-Force Firewall plugin has a vulnerability (CVE-2025-11705) that could allow low-privileged users to read sensitive files and access private data. Although not critical, it affects over 50,000 sites, and a recent update has addressed the issue. #Wordfence #CVE-2025-11705

This report highlights a security vulnerability in totaljsv5013 where users can change their password without authenticating the current one. Exploiting this flaw could allow unauthorized password changes, compromising system security. #totaljsv5013 #passwordvulnerability…
Authentic businesses like Sarah’s face increasing threats from malicious SEO tactics powered by AI, which manipulate search rankings through fake content and manipulative link strategies. Next-generation defenses involve AI detection, network analysis, and proactive ecosystem monitoring to protect the integrity of search results. #MaliciousSEO #AIThreats…

Threat Fabric has discovered Herodotus, a new Android malware that uses human-like typing delays to evade detection during device takedowns and credential theft. The malware campaign targets financial institutions in Italy and Brazil, illustrating the evolving sophistication of banking malware-as-a-service tools. #Herodotus #K1R0 #AndroidBankingTrojan…

Cyber sanctions are an important tool in countering cyber threats, but they are most effective when combined with other strategies. The US leads in impactful cyber sanctions, while the EU faces operational challenges in implementation. #US #EU #CyberSanctions #CyberThreats…

Britain’s data watchdog has fined Bharat Singh Chand £200,000 for sending nearly a million spam texts related to debt and energy savings without consent. This case highlights the risks of unregulated marketing and targeted scams, especially toward vulnerable populations. #ICOFines #SpamTexts #DebtScams…
Security researchers uncovered a campaign involving typosquatted npm packages that execute malicious payloads on installation to steal credentials. This campaign used obfuscated multi-platform binaries, social engineering techniques, and IP fingerprinting to compromise systems before exfiltrating sensitive data. #npmTyposquatting #CredentialStealer…
Recent reports claiming a Gmail data breach affecting millions were based on a misunderstanding of infostealer data, not an actual attack. Google reassures users that their defenses remain strong, emphasizing the importance of 2FA and strong passwords. #Infostealer #HaveIBeenPwned…
Effective patch management is crucial for minimizing vulnerabilities in complex IT environments and requires centralized visibility and control to ensure timely updates and compliance. Action1 offers a cloud-native platform that automates, streamlines, and enhances vulnerability detection and remediation, transforming patching into a proactive, data-driven process. #VulnerabilityManagement #PatchAutomation
Microsoft has addressed a known issue causing Windows update failures on Windows 11 24H2 systems, which was linked to missing language packs and component payloads. The fix was implemented through the KB5067036 October 2025 preview update, offering temporary workarounds like In-Place Upgrade options. #WindowsUpdate #KB5050094
The PhantomRaven campaign targets developers through malicious npm packages that steal credentials and secrets, using sophisticated techniques like remote dynamic dependencies. This campaign highlights the dangers of supply chain attacks and the importance of verifying package authenticity. #PhantomRaven #npm #supplychainattack