A malicious extension disguised as a Solidity tool was uploaded to Open VSX, employing SleepyDuck malware that uses Ethereum smart contracts for command-and-control. Despite platform warnings, over 53,000 downloads highlight the extent of its spread and persistence, leveraging blockchain for resilience. #SleepyDuck #EthereumSmartContract
Category: Cyber Security News
The Balancer Protocol experienced a significant security breach targeting its V2 pools, resulting in over $128 million in losses. The incident involved a precision rounding error and possibly improper authorization, raising concerns within the DeFi community. #Balancer #Ethereum #DeFiHack

A new malicious extension in the Open VSX registry, SleepyDuck, is exploiting Visual Studio Code to steal blockchain data and take control of affected systems. It uses Ethereum contract updates and fallback control mechanisms to maintain persistence and evade detection. #SleepyDuck #OpenVSX #Ethereum…

A major cyberattack on SK Telecom resulted in a significant data breach affecting 27 million customers, leading to a 90% drop in operating profit and hefty fines. The incident involved long-term undetected malware and prompted widespread cybersecurity overhauls and customer compensation efforts. #SKTelecom #Malware #Cyberattack…

Cybercriminals are exploiting remote monitoring tools to hijack cargo shipments, targeting trucking and logistics companies. Organized crime groups are using digital infiltration and fraudulent load boards to steal goods, contributing to a significant rise in cargo theft with a substantial financial impact. #Proofpoint #CargoTheft #RemoteMonitoringTools…

Congressional Democrats are calling for the FTC to investigate Flock Safety due to poor cybersecurity practices, including the lack of mandatory multi-factor authentication. Reports indicate that at least 35 accounts have been hacked, exposing sensitive data of millions of Americans. #FlockSafety #FTC #cybersecurity #multifactorauthentication…

AI and large language models are transforming software development, but human oversight remains crucial for security, ethics, and legal compliance. Overreliance on AI can lead to vulnerable code and legal risks, emphasizing the need for best practices and continuous education. #AIcodeQuality #LegalLiability…
A Ukrainian national linked to the Jabber Zeus cybercrime group has been extradited from Italy to the US, highlighting ongoing international efforts against cybercriminals. The group, known for using Zeus banking trojan and Jabber messaging, stole millions from various banks through fraudulent transfers and social engineering attacks. #JabberZeus #ZeusBankingTrojan…
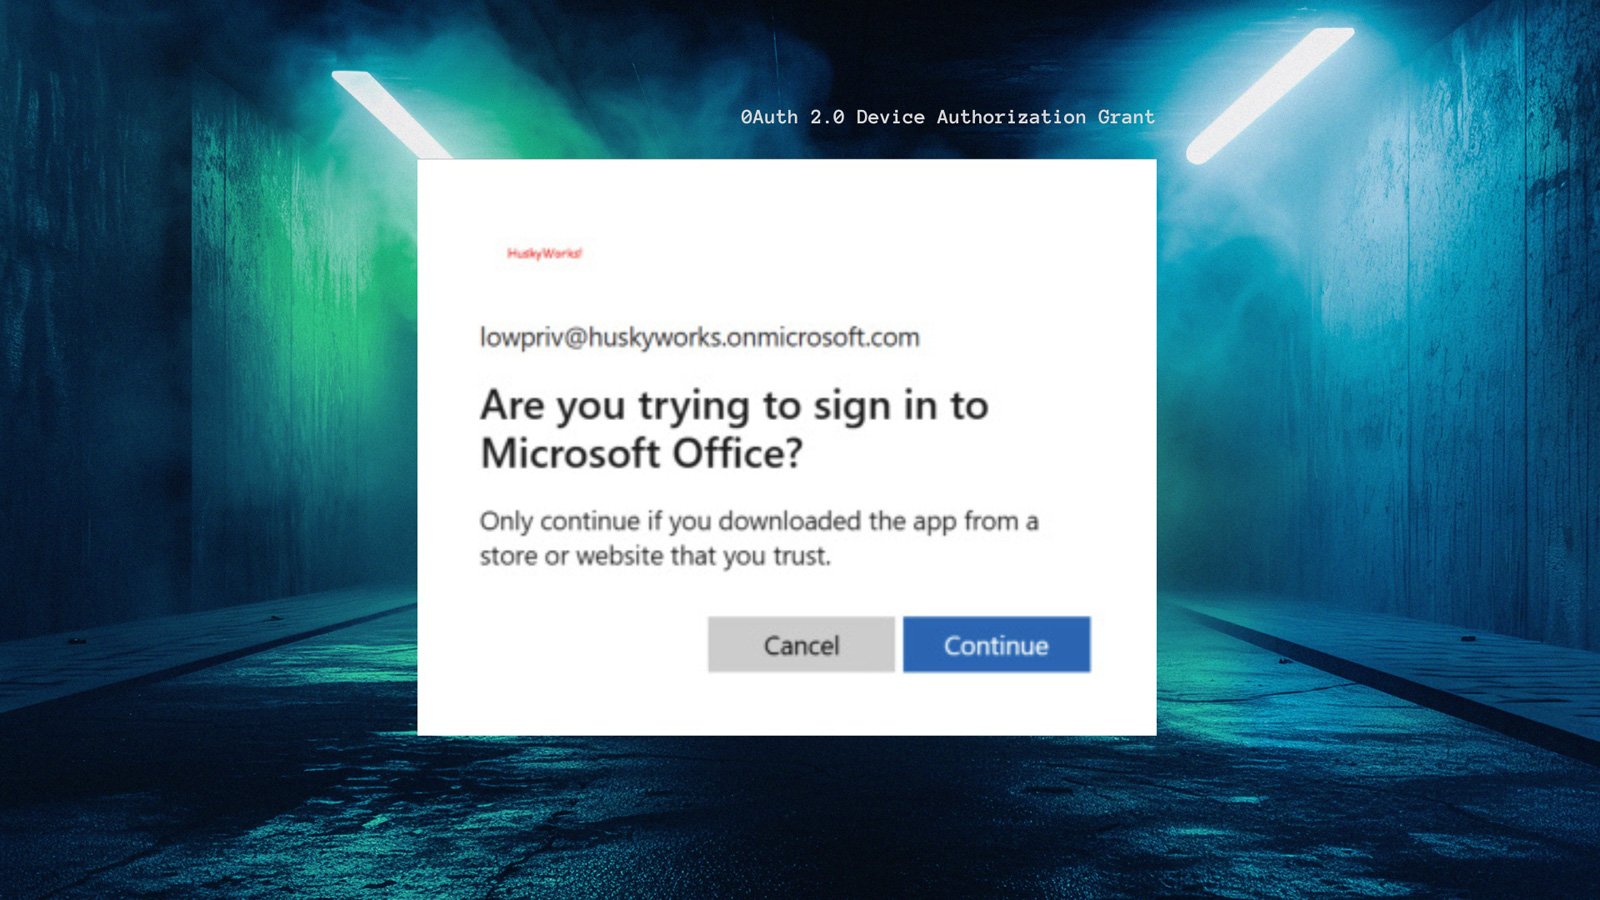
This article explores the differences in OAuth 2.0 device code flow implementations between Microsoft and Google, emphasizing their impact on attack surfaces. It demonstrates how device code phishing can be powerful in Azure due to fewer restrictions, while Google’s limited scopes mitigate similar risks. #Microsoft #Azure #Google #OAuth2Flow
An emergency out-of-band update for Windows Server 2025 aimed at fixing a critical CVE-2025-59287 vulnerability has unintentionally disrupted hotpatching for some systems. This issue has led to security concerns, with agencies and cybersecurity groups tracking vulnerable instances and Microsoft releasing a subsequent update to restore functionality. #CVE-2025-59287 #WindowsServer2025
Cybercriminals are targeting freight brokers and trucking carriers with malicious emails and links to install remote monitoring tools, enabling cargo hijacking and theft. These attacks are increasing globally, often exploiting trusted industry relationships and sophisticated social engineering tactics. #NetSupport #ScreenConnect
Three former cybersecurity incident responders have been indicted for their alleged involvement in BlackCat (ALPHV) ransomware attacks on multiple U.S. organizations. The case highlights ongoing threats from ransomware affiliates targeting critical sectors, with significant ransom demands and data theft. #BlackCat #ALPHV #DigitalMint #Sygnia #RansomwareThreats

Security Operations Centers face challenges including alert fatigue and lack of context, which hinder effective threat detection and response. Integrating continuous exposure management enhances SOC workflows by providing real-time attack surface visibility and contextual threat intelligence. #MITREATTACK #ExposureManagement…

Cybercriminals are targeting trucking and logistics companies by deploying remote monitoring and management (RMM) software to steal cargo, especially food and beverage products. These campaigns involve sophisticated tactics such as spear-phishing, fraudulent load listings, and hijacking legitimate business conversations. #RMMsoftware #LogisticsCyberattack…
British water suppliers in Britain have experienced five cyberattacks targeting their organizations since last year, underscoring increasing threats to critical infrastructure. While these attacks did not affect the water supply directly, they highlight the importance of improved cybersecurity measures amid evolving threats. #VoltTyphoon #BritishWater #CriticalInfrastructure…