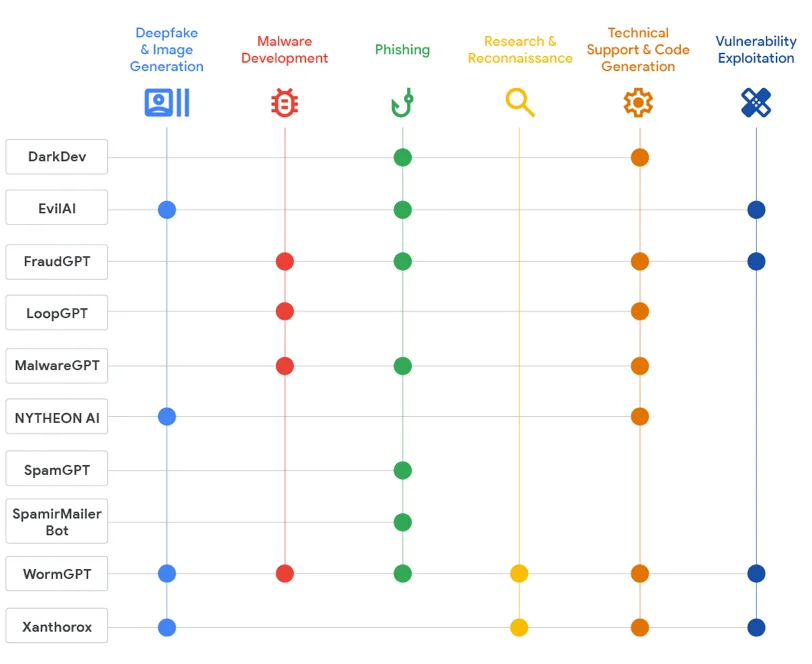
Recent reports highlight how AI-powered malware like PromptLock, QuietVault, and PromptSteal are being actively used by threat actors to evade detection and enhance their attack capabilities. Cybercriminals are increasingly leveraging large language models (LLMs) to develop more autonomous, adaptable, and sophisticated malware, marking a new era in cyber threats. #PromptLock #LLMs…
Category: Cyber Security News

SonicWall experienced a security breach involving cloud backup files, attributed to state-sponsored hackers, which prompted a company response including credential resets and system strengthening. The breach did not impact core products or customer networks, and investigations confirmed the activity was isolated to cloud backup files. #SonicWall #MySonicWall #StateSponsoredHackers…

A critical Out-of-Bounds Write vulnerability (CVE-2025-9242) affects WatchGuard Fireware OS, allowing remote attackers to execute arbitrary code. Active exploitation and available proof-of-concept increase the urgency to apply patches and rotate secrets. #CVE20259242 #WatchGuardFireware…

The European Parliament’s Council has approved a proposal to expand data sharing and biometric data collection by Europol to combat human trafficking and migrant smuggling. Privacy advocates warn that this move could lead to mass surveillance and privacy violations across Europe. #Europol #BiometricData #HumanTrafficking #MassSurveillance…

The Nevada government successfully recovered from a ransomware attack without paying the ransom, relying instead on backups and coordinated efforts. The attack traced back to an SEO poisoning campaign, with hackers gaining access through malicious code embedded in trusted online resources. #NevadaCyberAttack #SEOPhishing…
Three state attorneys general have fined Illuminate Education $5.1 million and mandated security improvements after a 2021 data breach exposed sensitive student information. The breach was attributed to poor security practices, including failure to delete former employees’ credentials and inadequate system monitoring. #IlluminateEducation #DataBreach #StudentDataProtection…
The U.S. Congressional Budget Office (CBO) experienced a cybersecurity breach attributed to the Chinese state-sponsored group Silk Typhoon, potentially exposing sensitive government data. The agency responded swiftly to contain the incident, highlighting ongoing threats to government networks. #SilkTyphoon #CBO #governmentbreach

Daily Recap, Google releases an emergency Chrome 142 update to fix high-risk vulnerabilities including RCE flaws, while Cisco patches critical firewall and UCCX vulnerabilities under active attack. Sandworm deploys data wipers targeting Ukraine’s grain sector, and various APTs use RMM, VM techniques, and covert Hyper-V VMs to evade EDR; notable incidents include SonicWall cloud backup theft, Nikkei breach, Hyundai AutoEver data exposure, and Penn/Israeli contractor compromises. #Chrome142 #CVE-2025-20333 #CVE-2025-20362 #Sandworm #UNK_SmudgedSerpent #APT-C-60 #SpyGlace #CovertHyper-V #SonicWallTheft #Nikkei #HyundaiAutoEver #UPenn
Nevada’s detailed report highlights how hackers used a trojanized administration tool to breach government systems and deploy ransomware, impacting over 60 agencies. The state’s proactive response without paying ransom, combined with increased security measures, showcases effective cyber resilience. #TrojanizedTools #NevadaCyberattack
A malicious VS Code extension called susvsex, created with AI, has been found to possess ransomware capabilities and was available on Microsoft’s official marketplace. Despite its clear malicious activities, Microsoft has not removed the extension, raising concerns about the effectiveness of their vetting process. #susvsex #MicrosoftVSCodeMarketplace
Cisco issued security advisories on November 5, 2025, addressing vulnerabilities in multiple products including Cisco Identity Services Engine and several versions of Cisco Unified Contact Center Express and Unified Intelligence Center. Users are urged to review the advisories, implement mitigations, and apply updates to ensure security. #CiscoVulnerabilities #ContactCenterSecurity…

Google has issued an urgent security update for Chrome, fixing five critical and medium-severity vulnerabilities related to WebGPU, Views, and V8 engine. The update aims to safeguard users from remote code execution threats, with wide rollout across all platforms starting November 5, 2025. #WebGPU #ChromeVulnerabilities…

The analysis reveals a vast and diverse landscape of connected devices within enterprise networks, many of which remain unmanaged and vulnerable. Top risks stem from xIoT devices like IP cameras, VoIP phones, and medical equipment, highlighting the challenges of device diversity and aging firmware. #xIoT #IPcamera #Vulnerabilities #HealthcareDevices #RetailSystems…
ClickFix attacks have become more sophisticated by incorporating videos, timers, and OS detection to deceive victims into executing malicious commands. These tactics aim to steal information by tricking users into pasting harmful code, often through fake CAPTCHA verifications. #ClickFix #CloudflareCaptcha #Malvertising
Purple teaming promotes collaboration between red and blue teams, shifting from rivalry to continuous validation and improvement in cybersecurity defenses. Breach and Attack Simulation (BAS) automates real-time testing, enabling organizations to close security gaps effectively. #PurpleTeam #BreachAndAttackSimulation