This week’s cybersecurity news highlights governmental efforts to remove Chinese Huawei technology from critical networks and ongoing law enforcement operations targeting criminal organizations through covert messaging apps. The stories also cover new vulnerabilities, industry-specific threats, and incident responses that shape the current cybersecurity landscape. #Huawei #AN0M…
Category: Cyber Security News

A recent cyberattack on the University of Pennsylvania resulted in the theft of sensitive personal data and disrupted university systems. The breach was carried out through social engineering, with hackers gaining access via a compromised PennKey account. #PennKey #FBI…

Cisco has issued a security advisory warning about two critical vulnerabilities in its Unified Contact Center Express platform that could allow remote attackers to execute arbitrary code and gain root access. The flaws, CVE-2025-20354 and CVE-2025-20358, require urgent software updates as no workarounds are available, emphasizing the importance of timely patching….
AI malware is emerging with several samples detected in the wild, showcasing evolving threats using AI capabilities. Despite their early development stage, these threats demonstrate potential future risks and sophistication. #PROMPTFLUX #AP28…

The increasing enforcement of ID laws is forcing organizations to store sensitive government-issued IDs, raising serious security concerns highlighted by the Discord data breach. The breach demonstrates the risks associated with storing large volumes of personally identifiable information and underscores the need for integrated cybersecurity solutions. #Discord #IDlaws
Cisco has issued security updates addressing two vulnerabilities exploited in zero-day attacks that cause ASA and FTD firewalls to reboot. These vulnerabilities, when chained, can allow attackers complete control over affected systems. #CVE202520362 #CVE202520333
A zero-day vulnerability in Samsung’s Android image processing library was exploited to deploy the ‘LandFall’ spyware via malicious WhatsApp images. The attack targeted Samsung Galaxy devices in the Middle East and involved sophisticated techniques for persistence, evasion, and device fingerprinting. #CVE-2025-21042 #LandFall #SamsungGalaxy
QNAP recently addressed seven zero-day vulnerabilities that were exploited during the Pwn2Own Ireland 2025 competition, affecting their NAS devices and software products. Users are advised to update their systems and passwords to secure against potential threats. #QNAP #Pwn2OwnIreland

A sophisticated cyberattack by the group Cavalry Werewolf targeted a Russian government organization, using phishing emails and multiple malware variants to steal data and perform network reconnaissance. The campaign highlights the threat posed by advanced persistent threat actors employing open-source tools and covert tactics. #CavalryWerewolf #BackDoorShellNET #TrojanFileSpyNET #ReverseSocks5…
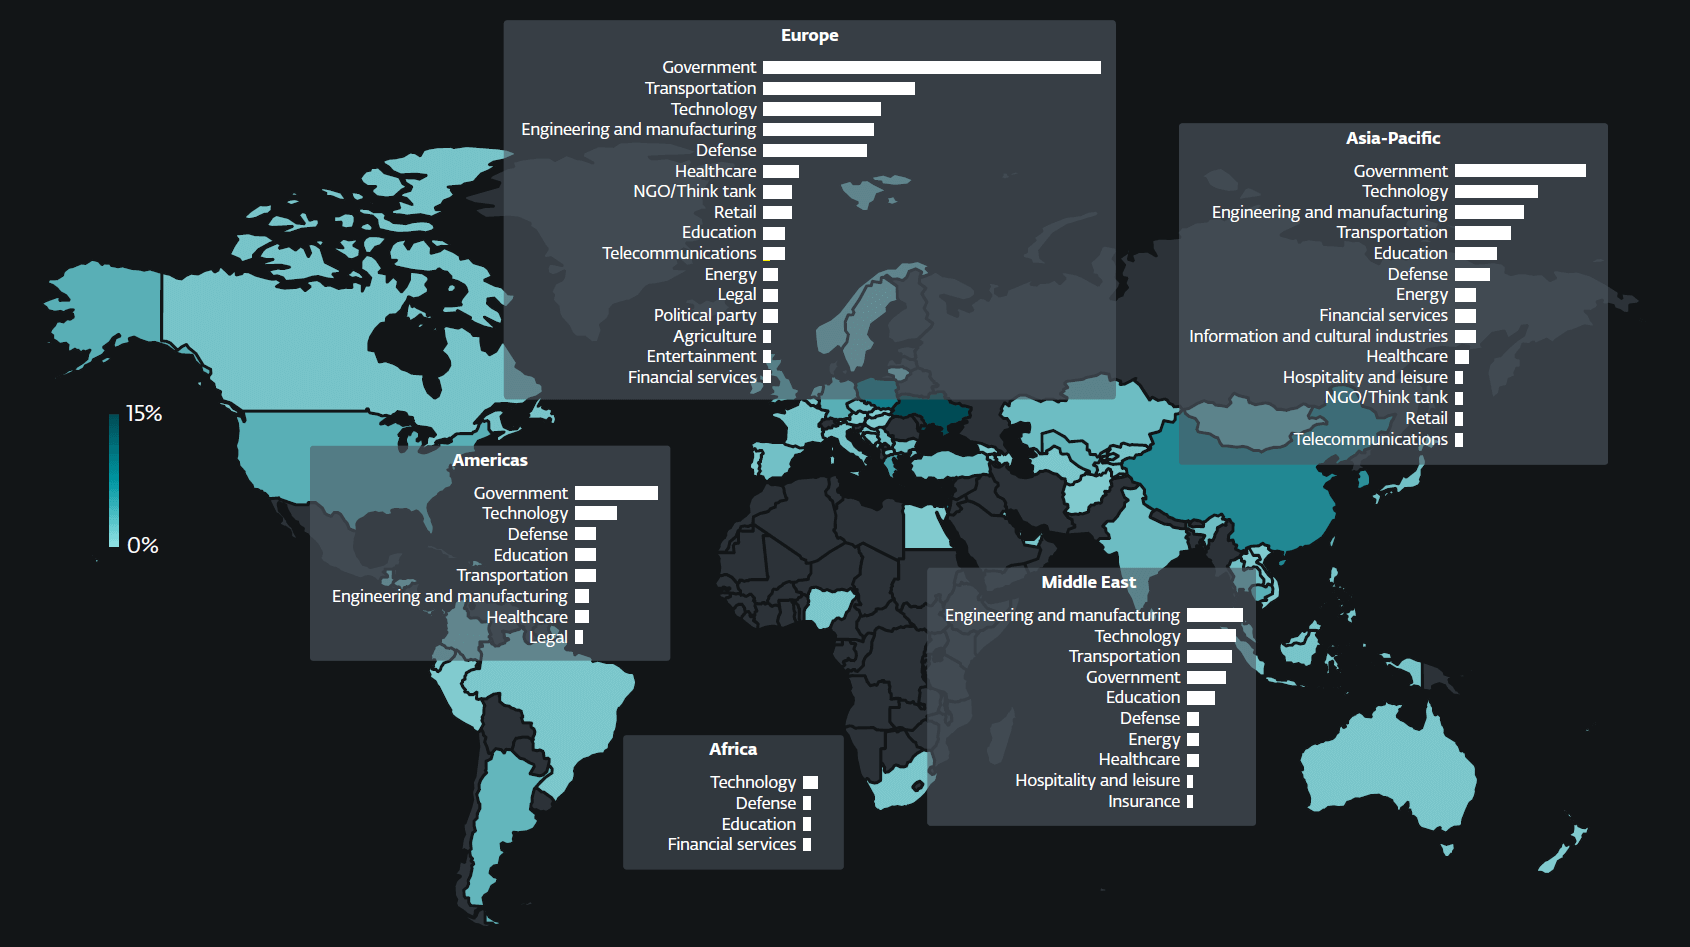
Russia-aligned threat actor Sandworm has intensified its destructive cyber operations targeting Ukrainian infrastructure using sophisticated data wipers like ZEROLOT and Sting. These attacks aim to cause maximum disruption to Ukraine’s economy and critical sectors, including government, energy, and agriculture. #Sandworm #ZEROLOT #Sting #UkrainianInfrastructure…

Chinese cyber-espionage groups such as APT41, Kelp, and Space Pirates continue to target U.S. and international policy organizations with advanced intrusion techniques. Their persistent campaigns involve exploiting vulnerabilities, establishing stealthy network presence, and using legitimate tools for automation and persistence. #APT41 #Kelp #SpacePirates #ChineseEspionage #CyberThreats…

Businesses of all sizes face increasing legal risks related to online user data collection, driven by outdated privacy laws and widespread use of tracking tools. Small and midsize enterprises, especially in retail, healthcare, and hospitality, are frequently targeted in lawsuits citing violations of old statutes like the California Invasion of Privacy…
Google has released a Chrome update to fix five vulnerabilities, including three high-severity flaws related to memory safety and UI security. These fixes come at a time when browser vulnerabilities are increasingly exploited by threat actors targeting user systems and organizations. #ChromeVulnerabilities #WebGPU #V8JavaScript…

The Congressional Budget Office confirmed it was hacked, potentially exposing sensitive government data to malicious actors. The incident is under investigation, with suspected foreign involvement, prompting enhanced security measures. #CBOhack #ForeignActor…
Google’s $32 billion acquisition of Wiz has cleared U.S. antitrust review and is expected to close in 2026, marking the largest cybersecurity deal ever. The integration of Wiz will enhance Google Cloud’s enterprise security capabilities, offering solutions across multiple cloud platforms. #Wiz #GoogleCloud #CybersecurityMergers…