Microsoft’s recent Patch Tuesday updates have addressed over 60 vulnerabilities, including a critical Windows kernel zero-day (CVE-2025-62215) that has been exploited in attacks. These fixes improve security across Windows, Office, Visual Studio, and other Microsoft products, highlighting ongoing threats and patch efforts. #CVE202562215 #WindowsKernelZeroDay…
Category: Cyber Security News
Adobe’s latest Patch Tuesday updates fix 29 vulnerabilities across multiple products, addressing critical security flaws including arbitrary code execution and bypass issues. Although there are no current reports of exploitation, the vulnerabilities remain a concern for future attacks. #InDesign #Pass…
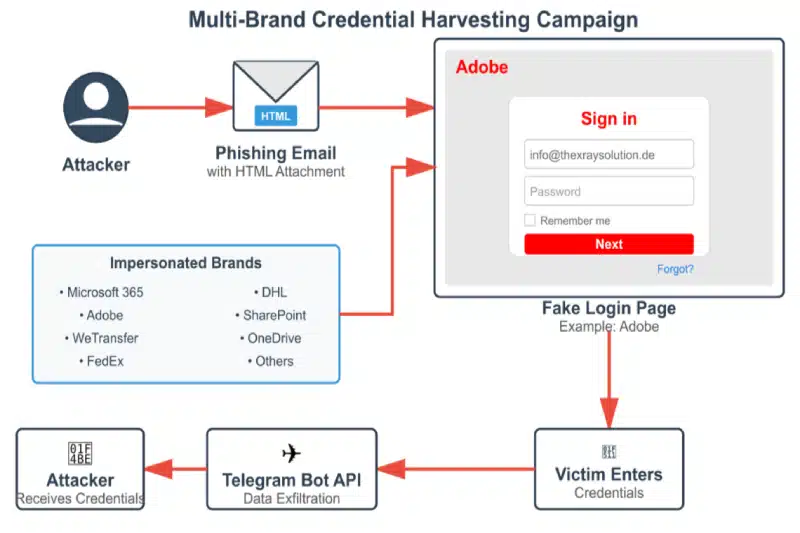
Cybersecurity researchers at Cyble have uncovered a sophisticated phishing campaign in Central and Eastern Europe that uses malicious HTML attachments to steal credentials without relying on external hosting servers. The attack employs convincing fake login pages and embeds JavaScript to exfiltrate data via Telegram bots, bypassing traditional security measures. #PhishingCampaign #CredentialTheft…
Microsoft has issued an emergency out-of-band update to fix a critical issue preventing Windows 10 users from enrolling in the Extended Security Updates (ESU) program. Once installed, users can successfully enroll and receive essential security updates, ensuring continued protection after Windows 10’s end of support. #KB5071959 #Windows10ESU
Microsoft has released cumulative updates KB5068861 and KB5068865 for Windows 11, which include security patches, bug fixes, and new features. The updates introduce a new Start menu UI, enhanced battery indicators, and improved security protections, marking the last update for Windows 11 23H2. #Windows11 #PatchTuesday
Microsoft’s November 2025 Patch Tuesday releases security updates addressing 63 flaws, including a zero-day actively exploited in the Windows Kernel. Key vulnerabilities include Critical remote code execution and privilege escalation flaws, with a focus on critical systems like Windows and Microsoft Office. #WindowsKernel #CVE202562215
Microsoft has released the KB5068781 update to extend security support for Windows 10 devices, including bug fixes and security patches. This update addresses a bug affecting ESU enrollment and incorporates critical security fixes for vulnerabilities, ensuring continued protection for users. #Windows10 #KB5068781 #ESU #PatchTuesday #MicrosoftUpdate

Microsoft announced that Windows 11 23H2 Home and Pro editions have reached end of support, stopping security updates. Users are advised to upgrade to Windows 11 25H2 to continue receiving critical security patches. #Windows11 #SupportEnd #Windows11Upgrade
SAP has released 18 new security notes in its November 2025 patches, addressing critical vulnerabilities across multiple products. The most severe issues include insecure key management in SQL Anywhere Monitor and code injection in Solution Manager, emphasizing the importance of timely patch application. #CVE202542890 #CVE202542887…
Mozilla has enhanced its Firefox browser’s fingerprinting protections to reduce user tracking by limiting the collection of hardware and system details. These improvements almost halve the number of users identifiable as unique, strengthening privacy without disrupting web functionality. #Firefox #BrowserFingerprinting…

A threat actor exploited a critical vulnerability in Triofox to gain remote access and create a new administrator account, enabling malicious activities. Organizations are urged to update to version 16.7.10368.56560 or later and audit their accounts to prevent further exploitation. #CVE-2025-12480 #UNC6485…

Google’s Mandiant uncovered threat actors exploiting a patched Triofox vulnerability (CVE-2025-12480) to gain unauthorized access, upload malicious scripts, and establish remote control via installed remote access tools. Immediate patching, account auditing, and monitoring are crucial to prevent further attacks. #CVE-2025-12480 #Triofox #UNC6485 #ZohoUEMS #RemoteAccessTools…
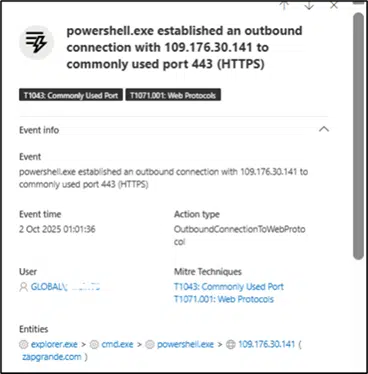
CyberProof researchers have uncovered a connection between the banking trojans Maverick and Coyote, both targeting Brazilian users via WhatsApp downloads. These malware families share code, infection methods, and attack patterns, highlighting a sophisticated and coordinated threat against financial institutions in Brazil. #MaverickTrojan #CoyoteTrojan #BrazilianBanks #WhatsAppMalware…

A sophisticated espionage campaign targeting aerospace and defense organizations is active, using a new Comebacker backdoor variant by the Lazarus Group. The campaign involves targeted spear phishing with malicious documents impersonating key industry organizations, with advanced encrypted command-and-control communications. #LazarusGroup #ComebackerBackdoor…

Recent vulnerabilities in runC, a critical container runtime, could allow attackers to escape containers and compromise host systems. Upgrading to the latest versions and applying recommended security measures are essential to mitigate these risks. #runC #Docker #Kubernetes #containerescape #securitypatches…